diff --git "a/collect/lowRISC/lowRISC__ibex_s01_03_issues.jsonl" "b/collect/lowRISC/lowRISC__ibex_s01_03_issues.jsonl"
new file mode 100644--- /dev/null
+++ "b/collect/lowRISC/lowRISC__ibex_s01_03_issues.jsonl"
@@ -0,0 +1,702 @@
+{"org": "lowRISC", "repo": "ibex", "number": 2447, "state": "closed", "title": "Fix ifdef VERILATOR breaking sv-tests ibex", "body": "## Observed Behavior\n\nThe Ibex test that runs on Verilator as part of sv-tests at https://chipsalliance.github.io/sv-tests-results/?v=verilator+ibex+ibex\n\nfails with:\n\n```\n%Error-CONTASSINIT: build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/../src/lowrisc_ibex_ibex_simple_system_core_0/rtl/ibex_simple_system.sv:68:19: Continuous assignment to variable with initial value: 'clk_sys'\n : ... note: In instance 'ibex_simple_system'\n : ... Location of variable initialization\n build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/../src/lowrisc_ibex_ibex_simple_system_core_0/rtl/ibex_simple_system.sv:132:12: ... Location of continuous assignment\n ... For error description see https://verilator.org/warn/CONTASSINIT?v=5.049\n```\n\n## Expected Behavior\n\nDoes not fail.\n\n## Steps to reproduce the issue\n\nSee sv-tests for their command line.\n\n## Notes\n\nI believe this is because Verilator recently added/updated the continuous assignment error, previously this was (incorrectly) not an error. I believe that the error is correct, and is due to the `ifdef VERILATOR code around here:\n\nhttps://github.com/lowRISC/ibex/blob/2cf450db5133f6215c32d8463e65f8733e7323a3/examples/simple_system/rtl/ibex_simple_system.sv#L131\n\nit should be updated to be an always or otherwise not create IEEE-illegal code when VERILATOR is defined. Thanks.\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2397, "state": "closed", "title": "[rtl] Move prim_generic dependency to ibex_top", "body": "The `prim_generic` fileset dependency was declared in `ibex_top_tracing.core` rather than `ibex_top.core`, causing fusesoc to fail when targeting `ibex_top` directly. This PR fixes this by moving the `prim_generic` dependency to `ibex_top.core`.\r\n\r\nFixes #2396."}
+{"org": "lowRISC", "repo": "ibex", "number": 2396, "state": "closed", "title": "Trouble with using Ibex without FuseSoC", "body": "Hi,\n\nI'm not sure if this is the correct approach but I was planning to gather all RTL files and run simulations/tests on QuestaSim so I found the following in your documentation:\n\n\"\nIbex flows use [FuseSoC](https://github.com/olofk/fusesoc) to gather needed RTL files and run builds. If you want to use Ibex without FuseSoC the following FuseSoC command will copy all the needed files into a build directory.\n\nfusesoc --cores-root . run --target=lint --setup --build-root ./build/ibex_out lowrisc:ibex:ibex_top\n\"\n\nI have used the command above and it did generate a bunch of files and what seems to be a makefile for verilator simulation so I thought I'd run it first to make sure I'm not missing any files.\n\nI ran make binary as well as make lint-only and they produce the same error:\n\n$ make binary\nverilator --binary -f lowrisc_ibex_ibex_top_0.1.vc -Wall --unroll-count 72\n%Error: src/lowrisc_prim_xilinx_clock_gating_0/rtl/prim_clock_gating.sv:23:7: Cannot find file containing module: 'BUFGCE'\n 23 | BUFGCE #(\n | ^~~~~~\n ... Looked in:\n src/lowrisc_dv_dv_fcov_macros_0/BUFGCE\n src/lowrisc_dv_dv_fcov_macros_0/BUFGCE.v\n src/lowrisc_dv_dv_fcov_macros_0/BUFGCE.sv\n src/lowrisc_prim_util_get_scramble_params_0/rtl/BUFGCE\n src/lowrisc_prim_util_get_scramble_params_0/rtl/BUFGCE.v\n src/lowrisc_prim_util_get_scramble_params_0/rtl/BUFGCE.sv\n src/lowrisc_prim_util_memload_0/rtl/BUFGCE\n src/lowrisc_prim_util_memload_0/rtl/BUFGCE.v\n src/lowrisc_prim_util_memload_0/rtl/BUFGCE.sv\n src/lowrisc_prim_assert_0.1/rtl/BUFGCE\n src/lowrisc_prim_assert_0.1/rtl/BUFGCE.v\n src/lowrisc_prim_assert_0.1/rtl/BUFGCE.sv\n src/lowrisc_prim_secded_0.1/rtl/BUFGCE\n src/lowrisc_prim_secded_0.1/rtl/BUFGCE.v\n src/lowrisc_prim_secded_0.1/rtl/BUFGCE.sv\n BUFGCE\n BUFGCE.v\n BUFGCE.sv\n%Error: Exiting due to 1 error(s)\nmake: *** [Makefile:19: binary] Error 1\n\nCan you please let me know what I'm doing wrong? Thanks!"}
+{"org": "lowRISC", "repo": "ibex", "number": 2350, "state": "closed", "title": "[doc] PMP instruction fetch check clarified", "body": "Clarify that instruction fetch bus should not contain devices that experience side-effects due to reads."}
+{"org": "lowRISC", "repo": "ibex", "number": 2345, "state": "closed", "title": "Problem building the simple system", "body": "Hi,\nI have installed all prerequisites according to the simple system instructions. However, the fusesoc command fails as shown below:\n```\n$ fusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system $(util/ibex_config.py small fusesoc_opts)\nINFO: Preparing lowrisc:dv:crypto_prince_ref:0.1\nINFO: Preparing lowrisc:dv:dv_fcov_macros:0\nINFO: Preparing lowrisc:dv:secded_enc:0\nINFO: Preparing lowrisc:dv_verilator:ibex_pcounts:0\nINFO: Preparing lowrisc:dv_verilator:simutil_verilator:0\nINFO: Preparing lowrisc:ibex:ibex_pkg:0.1\nINFO: Preparing lowrisc:prim:primgen:0.1\nINFO: Preparing lowrisc:prim:ram_1p_pkg:0\nINFO: Preparing lowrisc:prim:ram_2p_pkg:0\nINFO: Preparing lowrisc:prim:util_get_scramble_params:0\nINFO: Preparing lowrisc:tool:check_tool_requirements:0.1\nINFO: Preparing lowrisc:dv:scramble_model:0\nINFO: Preparing lowrisc:dv_verilator:memutil_dpi:0\nINFO: Preparing lowrisc:lint:common:0.1\nINFO: Preparing lowrisc:prim:prim_pkg:0.1\nINFO: Preparing lowrisc:dv_verilator:memutil_dpi_scrambled:0\nINFO: Preparing lowrisc:dv_verilator:memutil_verilator:0\nINFO: Preparing lowrisc:prim:assert:0.1\nINFO: Preparing lowrisc:prim:cipher_pkg:0.1\nINFO: Preparing lowrisc:prim:clock_gating:0\nINFO: Preparing lowrisc:prim:clock_mux2:0\nINFO: Preparing lowrisc:prim:ram_1p:0\nINFO: Preparing lowrisc:prim:ram_2p:0\nINFO: Preparing lowrisc:prim:secded:0.1\nINFO: Preparing lowrisc:ibex:ibex_icache:0.1\nINFO: Preparing lowrisc:ibex:ibex_tracer:0.1\nINFO: Preparing lowrisc:ibex:sim_shared:0\nINFO: Preparing lowrisc:prim:and2:0\nINFO: Preparing lowrisc:prim:buf:0\nINFO: Preparing lowrisc:prim:cipher:0\nINFO: Preparing lowrisc:prim:count:0\nINFO: Preparing lowrisc:prim:flop:0\nINFO: Preparing lowrisc:prim:lfsr:0.1\nINFO: Preparing lowrisc:prim:util:0.1\nINFO: Preparing lowrisc:prim:mubi:0.1\nINFO: Preparing lowrisc:prim:onehot:0\nINFO: Preparing lowrisc:prim:onehot_check:0\nINFO: Preparing lowrisc:prim:ram_1p_adv:0.1\nINFO: Preparing lowrisc:ibex:ibex_core:0.1\nINFO: Preparing lowrisc:prim:ram_1p_scr:0.1\nINFO: Preparing lowrisc:ibex:ibex_top:0.1\nINFO: Preparing lowrisc:ibex:ibex_top_tracing:0.1\nINFO: Preparing lowrisc:ibex:ibex_simple_system_core:0\nINFO: Preparing lowrisc:ibex:ibex_simple_system:0\nINFO: Generating lowrisc:prim:prim_pkg-impl:0.1\nCreating prim_pkg.sv\nCore file written to prim_pkg.core.\nINFO: Generating lowrisc:prim:clock_gating-impl:0\nImplementations for primitive clock_gating: xilinx, generic\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_clock_gating.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.sv\nCreating core file for primitive clock_gating.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.core\nINFO: Generating lowrisc:prim:clock_mux2-impl:0\nImplementations for primitive clock_mux2: generic, xilinx\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_clock_mux2.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_mux2-impl_0/prim_clock_mux2.sv\nCreating core file for primitive clock_mux2.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_mux2-impl_0/prim_clock_mux2.core\nINFO: Generating lowrisc:prim:ram_1p-impl:0\nImplementations for primitive ram_1p: generic, badbit\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_1p.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.sv\nCreating core file for primitive ram_1p.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.core\nINFO: Generating lowrisc:prim:ram_2p-impl:0\nImplementations for primitive ram_2p: generic\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_2p.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.sv\nCreating core file for primitive ram_2p.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.core\nINFO: Generating lowrisc:prim:and2-impl:0\nImplementations for primitive and2: generic, xilinx\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_and2.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_and2-impl_0/prim_and2.sv\nCreating core file for primitive and2.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_and2-impl_0/prim_and2.core\nINFO: Generating lowrisc:prim:buf-impl:0\nImplementations for primitive buf: xilinx, generic\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_buf.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_buf-impl_0/prim_buf.sv\nCreating core file for primitive buf.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_buf-impl_0/prim_buf.core\nINFO: Generating lowrisc:prim:flop-impl:0\nImplementations for primitive flop: xilinx, generic\nInspecting generic module /home/mn/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_flop.sv\n[Errno 2] No such file or directory: 'verible-verilog-syntax'\nVerible parser failed, using regex fallback instead.\nCreating SystemVerilog module for abstract primitive\nAbstract primitive written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_flop-impl_0/prim_flop.sv\nCreating core file for primitive flop.\nCore file written to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_flop-impl_0/prim_flop.core\nINFO: Wrote dependency graph to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/lowrisc_ibex_ibex_simple_system_0.deps-after-generators.dot\nINFO: Wrote Makefile fragment to /home/mn/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/core-deps.mk\nINFO: Setting up project\n\nINFO: Running pre_build script check_tool_requirements\nINFO: Building simulation model\nINFO: verilator -f lowrisc_ibex_ibex_simple_system_0.vc --trace --trace-fst --trace-structs --trace-params --trace-max-array 1024 -CFLAGS \"-std=c++17 -Wall -DVM_TRACE_FMT_FST -DTOPLEVEL_NAME=ibex_simple_system -g\" -LDFLAGS \"-pthread -lutil -lelf\" -Wall --unroll-count 72\n\nERROR: %Warning-UNOPTFLAT: ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_id_stage.sv:220:16: Signal unoptimizable: Circular combinational logic: 'ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.instr_executing_spec'\n : ... note: In instance 'ibex_simple_system'\n 220 | logic instr_executing_spec;\n | ^~~~~~~~~~~~~~~~~~~~\n ... For warning description see https://verilator.org/warn/UNOPTFLAT?v=5.043\n ... Use \"/* verilator lint_off UNOPTFLAT */\" and lint_on around source to disable this message.\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_id_stage.sv:220:16: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.instr_executing_spec\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_id_stage.sv:781:3: Example path: ALWAYS\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_id_stage.sv:269:16: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.stall_alu\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:103:33: Example path: ASSIGNW\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:103:33: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.stall_id_i\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:453:3: Example path: ALWAYS\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:136:9: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.halt_if\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ASSIGNW\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.id_in_ready_o\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:453:3: Example path: ALWAYS\n%Warning-UNOPTFLAT: ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:140:9: Signal unoptimizable: Circular combinational logic: 'ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.special_req'\n : ... note: In instance 'ibex_simple_system'\n 140 | logic special_req;\n | ^~~~~~~~~~~\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:140:9: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.special_req\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:453:3: Example path: ALWAYS\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:136:9: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.halt_if\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ASSIGNW\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.id_in_ready_o\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:453:3: Example path: ALWAYS\n%Warning-UNOPTFLAT: ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Signal unoptimizable: Circular combinational logic: 'ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.id_in_ready_o'\n : ... note: In instance 'ibex_simple_system'\n 44 | output logic id_in_ready_o,\n | ^~~~~~~~~~~~~\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.id_in_ready_o\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:453:3: Example path: ALWAYS\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:136:9: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.halt_if\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ASSIGNW\n ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:44:33: Example path: ibex_simple_system.u_top.u_ibex_top.u_ibex_core.id_stage_i.controller_i.id_in_ready_o\n%Error: Exiting due to 3 warning(s)\nmake: *** [Makefile:16: Vibex_simple_system.mk] Error 1\n\nERROR: Failed to build lowrisc:ibex:ibex_simple_system:0 : '['make', '-j', '12']' exited with an error: 2\n```\nI have installed Verilator from the source. See below that the command exists:\n```\n$ which verilator\n/usr/local/bin/verilator\n$ find /usr/local/bin/ -name \"verilator*\"\n/usr/local/bin/verilator_gantt\n/usr/local/bin/verilator_profcfunc\n/usr/local/bin/verilator_coverage_bin_dbg\n/usr/local/bin/verilator_bin\n/usr/local/bin/verilator_coverage\n/usr/local/bin/verilator_bin_dbg\n/usr/local/bin/verilator\n```\nI don't understand errors like `No such file or directory: 'verible-verilog-syntax'`. Any idea about that?"}
+{"org": "lowRISC", "repo": "ibex", "number": 2324, "state": "open", "title": "Add Zcb and Zcmp extensions DV", "body": "This PR adds support for the **Zcb** and **Zcmp** code-saving extensions. This support is implemented in a parameterizable way via the `RV32ZC` parameter, which allows choosing none, either, or both extensions. By default, both extensions are enabled because their combined hardware overhead is small, approximately 800 gate equivalents.\r\n\r\nThe Zcb extension introduces new compressed encodings for common instructions already supported in Ibex. The Zcmp extension introduces single compressed instructions that expand into multiple existing instructions within Ibex. For example, a stack push expands into multiple store instructions and a stack pointer update. Therefore, both extensions are implemented in the IF stage.\r\n\r\nAdding these new instructions requires updates to the following components:\r\n- [x] Ibex RTL: Implemented in: https://github.com/lowRISC/ibex/pull/2347\r\n- [x] Documentation: Updated in: https://github.com/lowRISC/ibex/pull/2347\r\n- [x] Verification: Implemented in this PR as well. Some missing parts still (see at the bottom)\r\n + [x] `riscv-isa-sim` (Spike): Updated Spike to support those new extensions https://github.com/lowRISC/riscv-isa-sim/pull/27\r\n + [x] `riscv-dv`: Add both extensions to [riscv-dv](https://github.com/SamuelRiedel/riscv-dv/tree/zcbzcmp). We can either try to upstream those or create a fork.\r\n * [x] Small fix to simplify Zcb/Zcmp extension: https://github.com/chipsalliance/riscv-dv/pull/1024\r\n * [x] Support for Zcb extension: https://github.com/chipsalliance/riscv-dv/pull/1025\r\n * [x] Support for the Zcmp's CMMV instructions: https://github.com/chipsalliance/riscv-dv/pull/1026\r\n + [x] Ibex co-simulation: Updated in this PR.\r\n * [x] Support for Zcb extension\r\n * [x] Support for the Zcmp's CMMV instructions\r\n * [x] Support for Zcmp's CMPP instructions\r\n- [ ] Compiler Support: We need to update the compiler to a version that supports the Zcb and Zcmp instructions. Currently, we are still on an [rather old](https://github.com/lowRISC/ibex/blob/master/ci/vars.env#L10) version. The latest RISC-V GCC and Clang support those instructions already.\r\n\r\nMissing Components and Known Issues:\r\n- ~~The verification for the Zcmp's CMPP instructions (cm.push, cm.pop(ret(z))) is not fully working yet. The primary issue lies in the cosimulation interface with Spike. Checking multiple memory accesses that occur within a single step causes riscv-isa-sim to throw an error.~~ Fixed.\r\n- ~~This PR depends on https://github.com/lowRISC/ibex/pull/2338 to fix a DV error that is triggered with the new tests, but unrelated to the new changes.~~ Merged\r\n- This PR depends on https://github.com/lowRISC/ibex/pull/2346 to fix a DV error that is triggered in the CI here, but unrelated to the new changes.\r\n- This PR currently disables the new Zcb/Zcmp checks with the latest few WIP commits. This is done to make the current regression tests work with the current compiler. The Zcb/Zcmp regressions will require the updated compiler."}
+{"org": "lowRISC", "repo": "ibex", "number": 2316, "state": "closed", "title": "Makefile error: Directory examples/sw/led no longer present", "body": "## Observed Behavior\nI am not sure the provenance of the Makefile in this project, maybe it is deprecated. However I am trying to build a design arty the arty100 and it bombs out when that target calls the other target sw-led.\n\n```\ncd examples/sw/led && make\n/bin/sh: 1: cd: can't cd to examples/sw/led\nmake: *** [Makefile:65: examples/sw/led/led.vmem] Error 2\n```\nChecking the contents of the base directory there is no `examples/sw/led` present, i checked back in time and it was in the past.\n\n## My Environment\n\nUbuntu and python 3.12 under venv, but this is a basic Makefile error\n\nFor clarity the Makefile should be fixed or removed. Is it supposed to be possible to build a working arty7 system from this repo any more or is this only maintained in [ibex-demo-system](https://github.com/lowRISC/ibex-demo-system) now?"}
+{"org": "lowRISC", "repo": "ibex", "number": 2312, "state": "closed", "title": "[Bug,TestFW] Zicntr in CoSim not compliant with the standard", "body": "\n\n## Observed Behavior\n\nI encountered some cosim mismatches around operations on CSR `instret` (user mode delegate of `minstret`), which is not (planned to be) implemented (according to #1973 ).\n```\nFAILURE: Co-simulation mismatch at time 36\nPC mismatch, DUT retired : 100000 , but the ISS retired: 100008\n[36] %Error: ibex_simple_system_cosim_checker.sv:74: Assertion failed in TOP.ibex_simple_system.u_ibex_simple_system_cosim_checker_bind: Co-simulation mismatch seen\nReceived stop request, shutting down simulation.\n```\ntrace_core_00000000.log:\n```\nTime Cycle PC Insn Decoded instruction Register and memory contents\n 30 11 00100004 c0206073 csrrsi x0,instret,0 x0=0x00000000\n=> trap IllegalInsn here\n 36 14 00100000 0670 c.addi4spn x12,x2,780 x12=0x0000030c\n```\n\n \n\n## Expected Behavior\n\nAs the project has not yet planned to impl Zicntr, spike used as reference model should be aligned.\nCurrently the fork lowrisc/riscv-isa-sim is far behind the upstream. While the upstream has made Zicntr optional regarding the ISA string, there exists a fragment in the fork that always enable Zicntr:\n```c\nriscv/isa_parser.cc:L37\n// enable zicntr and zihpm unconditionally for backward compatibility\n extension_table[EXT_ZICNTR] = true;\n```\n\n## Steps to reproduce the issue\n\n1. Build lowrisc:ibex:ibex_simple_system_cosim\n2. Run Cosim with the provided testcase binary (which may need conversion? bin is not officially supported, I run with my modified simulating c++ code) build/lowrisc_ibex_ibex_simple_system_cosim_0/sim-verilator/Vibex_simple_system -c 10000 --meminit=ram,errors/ba8335cdf5815390859b835ec904d458\n3. Mismatch reported\n\n[ibex_zicntr_unimpl.zip](https://github.com/user-attachments/files/21960935/ibex_zicntr_unimpl.zip)\n\n## My Environment\n\n\n**EDA tool and version:**\n\nVerilator 5.006 2023-01-22 rev (Debian 5.006-3)\n\n**Operating system:**\n\n\n**Version of the Ibex source code:**\n\nmaster (commit 587e9fe47ddf54a387b7976f6f720455f5a0b95d)\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2310, "state": "open", "title": "Add CITATION.cff for Standardized Ibex Citations", "body": "\n\n\n\nHi Ibex-team,\n\nI’d like to propose adding a [CITATION.cff](https://docs.github.com/en/repositories/managing-your-repositorys-settings-and-features/customizing-your-repository/about-citation-files) file to the Ibex repository. This would help researchers and users cite Ibex consistently in academic (and professional) work. \nI’ve generated a draft using [cffinit](https://citation-file-format.github.io/cff-initializer-javascript/#/finish) as a starting point:\n```\n# This CITATION.cff file was generated with cffinit.\n# Visit https://bit.ly/cffinit to generate yours today!\n\ncff-version: 1.2.0\ntitle: Ibex\nmessage: >-\n If you use this software, please cite it using the\n metadata from this file.\ntype: software\nauthors:\n - name: lowRISC CIC\n address: 7 Hills Road\n city: Cambridge\n post-code: CB2 1GE\n country: GB\n website: 'https://lowrisc.org/'\nabstract: >-\n Ibex is a production-quality open source 32-bit RISC-V CPU\n core written in SystemVerilog. The CPU core is heavily\n parametrizable and well suited for embedded control\n applications. Ibex is being extensively verified and has\n seen multiple tape-outs. Ibex supports the Integer (I) or\n Embedded (E), Integer Multiplication and Division (M),\n Compressed (C), and B (Bit Manipulation) extensions.\n```\n\n**Open Questions**:\n\n1. **Authorship:** Should lowRISC CIC be the sole author, or would it be more appropriate to include the [PULP Platform](https://www.pulp-platform.org/) as a co-author (or primary author)?\n\n2. **Additional Metadata:** Would you like to add a DOI, ORCID, version, or specific contributors (e.g., key maintainers) to the file?\n\n3. **Preferred Citation Format:** Do you have existing guidelines for how Ibex should be cited (e.g., in papers or documentation, which I have missed)?\n\nI’m happy to refine this further or submit a PR. Thanks for considering this!\n\nBest,\nFelix Uhle"}
+{"org": "lowRISC", "repo": "ibex", "number": 2309, "state": "closed", "title": "Introduce an OSS Formal Flow", "body": "This PR introduces a formal flow for Ibex that does not depend on Jasper, instead using yosys and our fork of the yosys-slang frontend to produce an aiger file, which the rIC3 model checker, under the instruction of conductor.py, can then verify. Just one aiger file is created, and is subsequently reconfigured by the Rust aig-manip tool.\r\n\r\nThis commit also introduces a new ci job which invokes the OS formal flow. It uses the nix flake, which contains all the necessary dependencies.\r\n\r\nSee dv/formal/README.md for more details, but in general:\r\n\r\n1. We generate the specification module and psgen RTL in roughly the same way as the Jasper flow, with small changes to the psgen output in particular.\r\n2. We use a fork of yosys-slang as the frontend for yosys. It has comprehensive SystemVerilog support, and handles both the specification and Ibex easily. It lacks SVA support by default, hence the need for the fork, though hopefully this will be upstreamed soon. The RTL source list is constructed by fusesoc in the same way as for Jasper.\r\n3. The yosys build script is then specified in build_all.ys. It makes use of three custom passes, which may be found in yosys_formal. See their source files for more explanation of what they do. Yosys takes ~10 minutes to build an aiger file. See aig-manip/src/main.rs for more description of aiger files.\r\n4. In order to prove a property, the rIC3 model checker can be used. However, the aiger file produced by yosys in step 3 contains all properties as assertions. To focus on just one, and to take all prior steps as assumptions the aig-manip tool is used. After this invocation of rIC3 is straightforward for IC3, k-induction or BMC. If a CEX is discovered it may be analysed by the aig-manip tool, which can lift the AIW (aiger witness) into a VCD file, for use in gtkwave etc.\r\n5. When considering the proof as a whole, the conductor.py script is used to discover proof strategies, and then run proofs while maximising memory usage. It caches proofs for each step under strategies/step*.json.\r\n\r\nAdditonal notes:\r\n1. The actual proof is relatively unchanged, with just a couple of new properties.\r\n2. The proof is fast (it takes 40 minutes or so in CI)\r\n3. smt2 based proofs are also available, e.g. for k-induction, since the build script (build_all.ys) will produce an smt2 file, which can be manipulated by smt2manip.py in the same that aig-manip does for an aiger file.\r\n4. The transformation made to a global clock will confuse clock gating. It *should* be fine, since the clock signal it generates is essentially ignored anyway."}
+{"org": "lowRISC", "repo": "ibex", "number": 2302, "state": "closed", "title": "Verilator flags indentation warning that looks like a testbench bug", "body": "I was trying to run Verilator lint on the full Ibex source code, including the testbench. I found that there was a lint warning about indentation. It actually looks like it's flagging a real bug:\n\n```\n%Warning-MISINDENT: ibex/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_request_driver.sv:87:17: Misleading indentation\n 87 | tr.intg = vif.request_driver_cb.rintg;\n | ^\n ibex/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_agent_pkg.sv:24:1: ... note: In file included from 'ibex_mem_intf_agent_pkg.sv'\n ibex/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_request_driver.sv:85:7: ... Expected indentation matching this earlier statement's line:\n 85 | if(tr.read_write == READ)\n | ^~\n ... For warning description see https://verilator.org/warn/MISINDENT?v=5.037\n ... Use \"/* verilator lint_off MISINDENT */\" and lint_on around source to disable this message.\n```\n\n## Observed Source Code Issue\n\nIn `ibex/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_request_driver.sv:87:17`:\n\n```\n if(tr.read_write == READ)\n tr.data = vif.request_driver_cb.rdata;\n tr.intg = vif.request_driver_cb.rintg;\n seq_item_port.put_response(tr);\n```\n\nThe two lines starting with `tr.` should probably both be under the if clause.\n\n## Expected Source Code\n\nThe driver should probably be fixed to have a `begin` and `end` to encapsulate these.\n\nIn `ibex/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_request_driver.sv:87:17`:\n\n```\n if(tr.read_write == READ) begin\n tr.data = vif.request_driver_cb.rdata;\n tr.intg = vif.request_driver_cb.rintg;\n end\n seq_item_port.put_response(tr);\n```\n\n## My Environment\n\n**EDA tool and version:** Verilator 5.037 devel\n\n**Operating system:** macOS 15.5 arm64\n\n**Version of the Ibex source code:** 479750353fdf2a74d507ec436028349ded1b951a\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2299, "state": "closed", "title": "Support testbench elaboration with Verific", "body": "This PR adds support for testbench elaboration using [Verific](https://www.verific.com/), which is the backbone of many EDA tools that do static analysis on SystemVerilog.\r\n\r\nVerific is a bit more strict than other parsers about DV includes. It also does not support functional coverage binding. I've added the necessary includes and protection around functional coverage binding assigns.\r\n\r\nLet me know if any changes are needed!"}
+{"org": "lowRISC", "repo": "ibex", "number": 2268, "state": "closed", "title": "[bug][ibex_decoder] Report a bug in Ibex", "body": "Hi all!\n\nI am using a static analysis to found a various bugs in open source RTL designs.\n\nIt was founded that in `ibex_decoder.sv` RTL file dead code is exists [here](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_decoder.sv#L439).\n\nThis assignment under `else` statement is never executed due to [this](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_decoder.sv#L406) external `else` branch with `!instr[26]` condition."}
+{"org": "lowRISC", "repo": "ibex", "number": 2267, "state": "closed", "title": "[ibex] Pass mvendorid and mimpid as top-level params", "body": "Instead of using default values from a package, create a top-level parameter to define these and pass them down. This allows integrators to specify them on a per-instance basis."}
+{"org": "lowRISC", "repo": "ibex", "number": 2259, "state": "closed", "title": "Verification should be done with ibex_cosim branch", "body": "This resolves comment: https://github.com/lowRISC/riscv-isa-sim/pull/25#issuecomment-2655147799"}
+{"org": "lowRISC", "repo": "ibex", "number": 2249, "state": "closed", "title": "Ibex core assertion NoExecWhenFetchEnableNotOn not gated correctly.", "body": "## Observed Behavior\nI'm seeing the NoExecWhenFetchEnableNotOn assertion fire inside of ibex_core.sv in a case where I'm not using the lockstep mode. I have a single instance of Ibex with the default parameters including `parameter bit SecureIbex = 1'b0,`\n\nThe assertion in question is part of the following code block:\n\n```\n // Keep track of the PC last seen in the ID stage when fetch is disabled\n logic [31:0] pc_at_fetch_disable;\n ibex_mubi_t last_fetch_enable;\n\n always_ff @(posedge clk_i or negedge rst_ni) begin\n if (!rst_ni) begin\n pc_at_fetch_disable <= '0;\n last_fetch_enable <= '0;\n end else begin\n last_fetch_enable <= fetch_enable_i;\n\n if ((fetch_enable_i != IbexMuBiOn) && (last_fetch_enable == IbexMuBiOn)) begin\n pc_at_fetch_disable <= pc_id;\n end\n end\n end\n\n // When fetch is disabled no instructions should be executed. Once fetch is disabled either the\n // ID/EX stage is not valid or the PC of the ID/EX stage must remain as it was at disable. The\n // ID/EX valid should not ressert once it has been cleared.\n `ASSERT(\n NoExecWhenFetchEnableNotOn,\n fetch_enable_i != IbexMuBiOn |=> (~instr_valid_id || (pc_id == pc_at_fetch_disable)) && ~$rose\n (instr_valid_id))\n```\n\nMy understanding from reading the documentation about `fetch_enable_i` was that I just needed to tie the LSB to 1. So I'm driving the input port to `4'b0001`. If that is correct, then it looks like this assertion shouldn't be firing. It should probably only be used when `SecureIbex == 1`?\n\nThe assertion fires for the first valid instruction fetched after reset.\n\n## Expected Behavior\nNo assertion should fire - unless I'm missing the fact that I'm doing something stupid.\n\n## Steps to reproduce the issue\nMy instantiation looks like:\n```\n ibex_top #(\n .RV32M (ibex_pkg::RV32MSlow),\n .RV32B (ibex_pkg::RV32BNone),\n .RegFile(ibex_pkg::RegFileFPGA)\n ) u_top (\n // Clock and reset\n .clk_i (clk),\n .rst_ni (!rst),\n .test_en_i ('0),\n .scan_rst_ni('0),\n .ram_cfg_i ('0),\n\n // Configuration\n .hart_id_i ('0),\n .boot_addr_i('0),\n\n // Instruction memory interface\n .instr_req_o (instr_req),\n .instr_gnt_i (instr_gnt),\n .instr_rvalid_i (instr_rvalid),\n .instr_addr_o (instr_addr),\n .instr_rdata_i (instr_rdata),\n .instr_rdata_intg_i('0),\n .instr_err_i (instr_err),\n\n // Data memory interface\n .data_req_o (data_req),\n .data_gnt_i (data_gnt),\n .data_rvalid_i (data_rvalid),\n .data_we_o (data_we),\n .data_be_o (data_be),\n .data_addr_o (data_addr),\n .data_wdata_o (data_wdata),\n .data_wdata_intg_o(),\n .data_rdata_i (data_rdata),\n .data_rdata_intg_i('0),\n .data_err_i (data_err),\n\n // Interrupt inputs\n .irq_software_i('0),\n .irq_timer_i (timer_irq),\n .irq_external_i('0),\n .irq_fast_i ('0),\n .irq_nm_i ('0),\n\n // Scrambling Interface\n .scramble_key_valid_i('0),\n .scramble_key_i ('0),\n .scramble_nonce_i ('0),\n .scramble_req_o (),\n\n // Debug interface\n .debug_req_i ('0),\n .crash_dump_o (),\n .double_fault_seen_o(),\n\n // Special control signals\n .fetch_enable_i (4'b0001),\n .alert_minor_o (),\n .alert_major_internal_o(),\n .alert_major_bus_o (),\n .core_sleep_o ()\n );\n```\n\n## My Environment\n\n**EDA tool and version:**\nCadence Xcelium 24.03\n\n**Operating system:**\nRHEL 9.5\n\n**Version of the Ibex source code:**\n8f4c75c5e43e61b994248307c814e01860303056\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2239, "state": "closed", "title": "Undriven signal in ibex_register_file_fpga.sv", "body": "## Observed Behavior\n\n\nOn the following line, `oh_raddr_a_err` is undriven if `RdataMuxCheck` is zero.\n\nhttps://github.com/lowRISC/ibex/blob/master/rtl/ibex_register_file_fpga.sv#L54\n\nThis was seen in Verilator linting when trying to integrate Ibex into my design. I've searched the VLT files for any relevant waivers but can't see any relating to this level of hierarchy.\n\n```\nERROR: %Warning-UNDRIVEN: src/lowrisc_export_ibex_top_0/rtl/ibex_register_file_fpga.sv:54:9: Signal is not driven: 'oh_raddr_a_err'\n : ... note: In instance 'ibex_wb.u_top..gen_regfile_fpga.register_file_i'\n 54 | logic oh_raddr_a_err, oh_raddr_b_err, oh_we_err;\n | ^~~~~~~~~~~~~~\n ... For warning description see https://verilator.org/warn/UNDRIVEN?v=5.024\n ... Use \"/* verilator lint_off UNDRIVEN */\" and lint_on around source to disable this message.\n%Warning-UNDRIVEN: src/lowrisc_export_ibex_top_0/rtl/ibex_register_file_fpga.sv:54:25: Signal is not driven: 'oh_raddr_b_err'\n : ... note: In instance 'ibex_wb.u_top..gen_regfile_fpga.register_file_i'\n 54 | logic oh_raddr_a_err, oh_raddr_b_err, oh_we_err;\n | ^~~~~~~~~~~~~~\n%Error: Exiting due to 2 warning(s)\nmake: *** [Makefile:23: lint-only] Error 1\n\nERROR: Failed to build nq:ip:ibex_wb:0 : '['make', 'lint-only']' exited with an error: 2\n```\n\n## Expected Behavior\n\nTis lint clean please.\n\n## Steps to reproduce the issue\n\n\nI'm trying to export the Ibex RTL source code to get around the fact that you are using a custom version of Fusesoc. I'm instantiating Ibex with the following parameters:\n\n```\n ibex_top #(\n .RV32M (ibex_pkg::RV32MSlow),\n .RV32B (ibex_pkg::RV32BNone),\n .RegFile(ibex_pkg::RegFileFPGA)\n ) u_top (\n\n```\n\nand then running a Verilator lint using the standard Fusesoc/Edalize flow.\n\n## My Environment\n\n\n\n**EDA tool and version:**\nVerilator 5.024 2024-04-05 rev v5.024\n\n\n**Operating system:**\nRocky 9.4\n\n\n**Version of the Ibex source code:**\n8f4c75c5e43e61b994248307c814e01860303056\n\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2236, "state": "closed", "title": "simulator report error", "body": "\n\n## Observed Behavior\nTest ibex in verilator with cosim, simulator report error illegal instruction.\n```\n001003e8 :\n 1003e8:\t1141 \taddi\tsp,sp,-16\n 1003ea:\tc606 \tsw\tra,12(sp)\n 1003ec:\t0000 \tunimp # <--- This is the illegal instruction!\n 1003ee:\t0000 \tunimp\n 1003f0:\t37b9 \tjal\t10033e \n 1003f2:\t00000517 \tauipc\ta0,0x0\n 1003f6:\t05650513 \taddi\ta0,a0,86 # 100448 \n 1003fa:\t3959 \tjal\t100090 \n 1003fc:\t40b2 \tlw\tra,12(sp)\n 1003fe:\t4501 \tli\ta0,0\n 100400:\t0141 \taddi\tsp,sp,16\n 100402:\t8082 \tret\n```\n```\nDASM(0x00010413)\nmv s0, sp\n```\n\n\n\nMTVAL in `ibex_simple_system.log` file is 0x00000000\n\n\n## Expected Behavior\nThe terminal should print right mtval value.\n\n\n## Steps to reproduce the issue\nRun `build/lowrisc_ibex_ibex_simple_system_cosim_0/sim-verilator/Vibex_simple_system --meminit=ram,ibex/examples/sw/simple_system/input/test.elf`\n```\n#include \"simple_system_common.h\"\nint main(void){\n // puts(\"Starting test\");\n __asm__ volatile(\".word 0x000000\");\n puts(\"Test complete\");\n return 0;\n}\n```\n\n\n## My Environment\nBuild verilator to run ibex by [co-sim](https://ibex-core.readthedocs.io/en/latest/03_reference/cosim.html#quick-build-and-run-instructions).\n\n\n**EDA tool and version:**\nNone\n\n\n**Operating system:**\nUbuntu Linux 18.04\n\n\n**Version of the Ibex source code:**\n8f4c75c5e43e61b994248307c814e01860303056\n\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2233, "state": "open", "title": "[dv] Verify access to Debug Module in debug mode even if disallowed by PMP", "body": "Verify the feature implemented in #2232; specific tasks are:\n- [ ] (P1) Minimal smoke test that verifies the feature works (i.e., read, write, and fetch a couple of addresses in the Debug Module address space while debug mode is enabled but the PMP doesn't allow the accesses).\n- [ ] (P2) Extensive testing that verifies the feature cannot be used for accesses outside the Debug Module address space that are disallowed by the PMP.\n- [ ] (P3) Extensive testing that verifies the feature works (close coverage over all addressing cases cross access types cross relevant states)."}
+{"org": "lowRISC", "repo": "ibex", "number": 2230, "state": "closed", "title": "[regfile_fpga] oh_raddr_*_err signals unassigned if RdataMuxCheck=0", "body": "\n\n## Observed Behavior\nThe onehot-error signals in relation to the read addresses (`oh_raddr_a_err`, `oh_raddr_b_err`) in [rtl/ibex_register_file_fpga.sv](../blob/master/rtl/ibex_register_file_fpga.sv) are unassigned for non-secure Ibex configurations (which is for example used for opentitan FPGA top-levels IIRC):\nhttps://github.com/lowRISC/ibex/blob/667fd20d2ede51caececccbcbda3652074424ce2/rtl/ibex_register_file_fpga.sv#L152-L158\n\nThis leads to the regfile `err_o` signal becoming `x`\nhttps://github.com/lowRISC/ibex/blob/667fd20d2ede51caececccbcbda3652074424ce2/rtl/ibex_register_file_fpga.sv#L55\nwhich triggers assertions (at least for us) when simulating with the FPGA regfile. It however seems to not cause issues during synthesis, at least with Vivado.\n\nI am also unsure about the comments that refer to `rdata_*_o` as asynchronous:\nhttps://github.com/lowRISC/ibex/blob/667fd20d2ede51caececccbcbda3652074424ce2/rtl/ibex_register_file_fpga.sv#L153-L154\n\n## Expected Behavior\nSame as for the other regfile variants; signals in question being tied to `1'b0` for `RdataMuxCheck = 0`.\n\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2229, "state": "closed", "title": "Revert \"[rtl] Fix counter reset value on FPGA\"", "body": "Reverts lowRISC/ibex#2226 because the scope for counter_q is incorrect resulting in synthesis failure for Xilinx targets."}
+{"org": "lowRISC", "repo": "ibex", "number": 2226, "state": "closed", "title": "[rtl] Fix counter reset value on FPGA", "body": "If the counter width is >= 49, we do not use a DSP on the FPGA. Then, we should use an asynchronous reset to initialize the counter.\r\n\r\nThis bug was detected when enabling the lockstep for the CW340. A lockstep mismatch happend as the mcycle counters of the main and shadow core did not match due to this bug."}
+{"org": "lowRISC", "repo": "ibex", "number": 2205, "state": "closed", "title": "Compile_tb.py generate options not recogised by xrun", "body": "\r\n\r\n## Observed Behavior\r\n\r\n[compile_tb_stdstreams.log](https://github.com/user-attachments/files/16634707/compile_tb_stdstreams.log)\r\n\r\n## Expected Behavior\r\n\r\n\r\n## Steps to reproduce the issue\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n Xcelium 23.09-s001\r\n\r\n**Operating system:**\r\n Centos 7.9\r\n\r\n**Version of the Ibex source code:**\r\n 668233699df9ec2a40413e69e0de0a5b10185980\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2193, "state": "closed", "title": "Pipeline not being flushed on PMP register clears", "body": "In [this commit](https://github.com/lowRISC/ibex/commit/46404cf86f60f72fb84a2bc693d2ab08011bdb37) the pipeline was made to flush on changes to PMP registers, changes made via `CSR_OP_CLEAR` however are missed.\r\n\r\nThis is likely because prior to this commit only mstatus and mie were listed, and clearing is safe for those.\r\n\r\nThis meant that instructions being fetched were passing PMP checks which they should not have been."}
+{"org": "lowRISC", "repo": "ibex", "number": 2188, "state": "closed", "title": "A bit-flip in the ECC-protected register file can go unnoticed when writeback forwarding is enabled", "body": "# Summary\r\n\r\nThe register file can be protected through ECC. In case this ECC detects an error, an alert signal is raised, and execution is aborted. However, the ECC signal is masked (ignored) in case writeback forwarding is enabled, see [ibex\\_core.sv:919](https://github.com/lowRISC/ibex/blob/668233699df9ec2a40413e69e0de0a5b10185980/rtl/ibex_core.sv#L919):\r\n\r\n```\r\n // Calculate errors - qualify with WB forwarding to avoid xprop into the alert signal\r\n assign rf_ecc_err_a_id = |rf_ecc_err_a & rf_ren_a & ~rf_rd_a_wb_match;\r\n```\r\n\r\nThis masking ignores the fact that sometimes, the core uses the value from the register file, even when writeback forwarding is enabled -- namely when encountering data hazards.\r\n\r\nAs a result, a bit-flip in the register file can propagate to the rest of the core, even with ECC in the register file being enabled.\r\n\r\nThis issue was found by [Konrad Jansen](https://github.com/kjnsen), [Niklas Kühnapfel](https://github.com/niclasku), [Peter William Deutsch](https://github.com/peterdeutsch), and [Vincent Ulitzsch](https://github.com/viniul).\r\n\r\n# Issue Details\r\n\r\nConsider [this waveform](https://file.io/d7aRruYHYKXS), in particular the signals listed in this screenshot:\r\n\r\n\r\nConsider these two instructions which are about to be executed in the attached screenshot of the waveform.\r\n\r\n```\r\n168: fec42703 lw a4,-20(s0)\r\n16c: fcf740e3 blt a4,a5,12c \r\n```\r\n\r\nThe branch instruction needs to wait for the load instruction to finish -- therefore the core is encountering a data hazard. A fault injected in the register file (in register a4), will propagate and disrupt execution, but remains undetected by the ECC. In the attached waveform, the fault is injected at 553 ps. To see why the fault does not trigger an alert, let us look at the waveform:\r\n\r\nConsider the signals debug\\_pc\\_id (pc decode) and debug\\_pc\\_wb. At 550, the load instruction is in the writeback stage and the branch instruction is in the decode + execute stage. The load instruction will cause a stall in the pipeline, see [ibex\\_decoder, line 1003](https://github.com/lowRISC/ibex/blob/668233699df9ec2a40413e69e0de0a5b10185980/rtl/ibex_id_stage.sv#L1003)\r\n\r\n```\r\n // If instruction is reading register that load will be writing stall in\r\n // ID until load is complete. No need to stall when reading zero register.\r\n assign rf_rd_a_hz = rf_rd_a_wb_match & rf_ren_a;\r\n assign stall_ld_hz = outstanding_load_wb_i & (rf_rd_a_hz | rf_rd_b_hz);\r\n```\r\n\r\nWe therefore stall for one cycle to get the load.\r\n\r\nThis load happens one cycle later (552 ps). The `rf_write_wb` signal is set to low, therefore setting\r\n\r\n```\r\nassign rf_rdata_a_fwd = rf_rd_a_wb_match & rf_write_wb_i ? rf_wdata_fwd_wb_i : rf_rdata_a_i;\r\n```\r\n\r\nto not use the value from the writeback stage, but from the `rf_rdata_a_i` value, see [ibex\\_id\\_stage, line 1006](https://github.com/lowRISC/ibex/blob/668233699df9ec2a40413e69e0de0a5b10185980/rtl/ibex_id_stage.sv#L1006). However, the `rf_rd_a_wb_match` signal is not set to low, thereby disabling the ECC signal:\r\n\r\n```\r\nassign rf_ecc_err_a_id = |rf_ecc_err_a & rf_ren_a & ~rf_rd_a_wb_match;\r\n```\r\n\r\nThe branch instruction from the decode stage therefore receives the value from the register file, although the `rf_rd_a_wb_match` signal is still set to high. Because the ECC signal is set to low, our fault goes unnoticed. In the example waveform, the injected fault at 553 ps (in the register file holding register a4) disrupts the value of alu\\_operand\\_a\\_ex, thereby changing the result of branch (debug\\_branch\\_decision), but because rf\\_rd\\_a\\_wb\\_match is still enabled, the ECC does not trigger.\r\n\r\n# Fix\r\n\r\nOnly mask the ECC signal in case writeback forwarding is enabled:\r\n\r\n```\r\n // Calculate errors - qualify with WB forwarding to avoid xprop into the alert signal\r\n assign rf_ecc_err_a_id = |rf_ecc_err_a & rf_ren_a & (~rf_rd_a_wb_match | ~rf_write_wb);\r\n assign rf_ecc_err_b_id = |rf_ecc_err_b & rf_ren_b & (~rf_rd_b_wb_match | ~rf_write_wb);\r\n\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 2182, "state": "closed", "title": "[dv] Add riscv_rf_ctrl_intg_test", "body": "This tests new hardening added to the register file around read and write control signals."}
+{"org": "lowRISC", "repo": "ibex", "number": 2173, "state": "closed", "title": "[dv] Implement fault injection tests for `prim_ram_1p_scr` MUBI values", "body": "Implement new test which inject faults into various MUBI values used in the `prim_ram_1p_scr` module. Proposed test should:\r\n\r\n- Run a random program using the same RISC-DV test and config as `riscv_rand_instr_test`\r\n- After a random interval choose a random `prim_ram_1p_scr` instance from the following (within `ibex_top`).\r\n - `gen_rams.gen_rams_inner.gen_scramble_rams.tag_bank`\r\n - `gen_rams.gen_rams_inner.gen_scramble_rams.data_bank`\r\n- Chose a random MUBI rather within that instance from the following:\r\n - `read_en`\r\n - `write_en_d`/`write_en_q`\r\n - `addr_match`\r\n - `rvalid_q`\r\n - `req_d`/`req_q`- Within `prim_ram_1p_adv`\r\n - `write_d`/`write_q` - Within `prim_ram_1p_adv`\r\n - `rvalid_d`/`rvalid_q` - Within `prim_ram_1p_adv`\r\n - `rvalid_sram_d`/`rvalid_sram_q` - Within `prim_ram_1p_adv`\r\n - Check an alert has occurred within a bounded number of cycles (bound TBD)"}
+{"org": "lowRISC", "repo": "ibex", "number": 2156, "state": "open", "title": "Proof-of-concept Nix environments for Ibex development", "body": "> This PR is just a PoC, and will likely never be merged. It contains some unrelated changes that I didn't bother completely tidying up, and some short-term fixes to make things work. Hopefully it is obvious which parts are unrelated.\r\n\r\nAdd a Nix flake to provide development environments for Ibex simulation and synthesis.\r\nThe goal of this is to try and utilize the principled properties of Nix (the tool, the language, etc) to easily bootstrap reproducible development environments. This should work on any x86_64-linux system where nix is installable (macOS support is also possible), as there is no dependency on system libraries at all. \r\n\r\n\r\n### Precursors\r\n1. Install Nix (I suggest to use this guide: https://zero-to-nix.com/start/install). If you use another installer, you will need to ensure the flakes and nix-command experimental features are enabled.\r\n2. Clone/checkout this branch\r\n```\r\ngit clone git@github.com:hcallahan-lowrisc/ibex.git --branch nix_env_init_poc\r\ncd ibex/\r\n```\r\n\r\nN.B. The first time running `nix develop` may take a little while to fetch and build dependencies. This is normal (no system library deps etc.), and the second time everything will be cached.\r\n\r\n### Demo 1 (verilator sims)\r\n1. Enter a development shell\r\n```\r\nnix develop # This drops you into a subshell with all the deps on your path\r\n# When you are done with the devshell...\r\nexit\r\n```\r\n2. Run some verilator sims (My makefile changes are incomplete, so ensure you clean with `make reset` when switching between sims)\r\n```\r\n# Run the simple_system under verilator\r\nmake run-simple-system-hello\r\n# Run coremark under verilator\r\nmake run-coremark\r\n# Run a pmp smoketest\r\nmake run-pmp-smoke-test\r\n```\r\n### Demo 2 (synthesis)\r\n1. Enter a different development shell, which contains the synthesis deps\r\n```\r\nnix develop .#syn_shell\r\n```\r\n2. Run a yosys synthesis using the Nangate45 open cell library\r\n```\r\nmake run_syn_yosys_nangate45\r\n``` \r\n\r\n### Demo 3 (HDL simulations including bootstrapping internal lowrisc tools)\r\nN.B. this will only evaluate for lowrisc internal environments with appropriate credentials. See the commit message (https://github.com/lowRISC/ibex/pull/2156/commits/350969abe123cd2d5a70816dd8132e2d0b12e1a8) for more details\r\n1. Enter a development shell\r\n```\r\nnix develop .#eda_shell_lowrisc\r\n```\r\n2. Run a simulation using the core_ibex UVM environment\r\n```\r\nmake -C dv/uvm/core_ibex SIMULATOR=xlm ITERATIONS=4 TEST=riscv_rand_instr_test\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 2153, "state": "closed", "title": "Installation Issue: FuseSoC build doesn't work", "body": "Ubuntu 22.04\r\nVerilator version: 5.022 2024-02-24 rev v5.020-157-g2b4852048\r\ngcc version: 12.3.0\r\ng++ version: 12.3.0\r\nclang version: 14.0.0\r\n\r\nAfter the installation of all the prerequisites, I'm stuck.\r\nIdk how to solve this, why does it seems that I haven't a C++14 compiler?\r\n\r\n\r\n\r\n\r\nERROR: Failed to build lowrisc:ibex:ibex_simple_system:0 : '['make', '-j', '3']'"}
+{"org": "lowRISC", "repo": "ibex", "number": 2144, "state": "closed", "title": "Security vulnerability: Ibex leaks data when multiplication is aborted", "body": "\r\n\r\n## Observed Behavior\r\n\r\n\r\nA MULH instruction that is aborted by an unsolicited memory error response leaks information about its input values to a subsequent MUL instruction. The subsequent MUL instruction stores a value dependent on MULH's operands into its result register, thus produces a wrong result and leaking information.\r\n\r\nI believe that the reason is that the multiplication's module's internal state machine is not reset in case of an abort. \r\n\r\n## Expected Behavior\r\n\r\nIbex should not leak data in case of external interface errors.\r\n\r\n## Steps to reproduce the issue\r\n\r\nThe testbench in https://github.com/KatCe/ibex/tree/bug_mulh_reg_leakage/dv/bug_mulh_reg_leakage demonstrates the problem.\r\nThis testbench uses the default configuration. We have also observed the bug in secure configuration with the parameters commented in the testbench.\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nQuesta Sim-64, Version 2022.3_1 linux_x86_64 Aug 12 2022\r\n\r\n**Operating system:**\r\n\r\nUbuntu 20.04.6 LTS\r\n**Version of the Ibex source code:**\r\n\r\n5a8a1a99930afbb9efe107ff2c80d482239d7a5f\r\nThe exact list of files run by the test bench can be found in https://github.com/KatCe/ibex/blob/bug_mulh_reg_leakage/dv/bug_mulh_reg_leakage/flist.f"}
+{"org": "lowRISC", "repo": "ibex", "number": 2132, "state": "closed", "title": "docs/readthedocs.org:ibex-core CI step keeps failing", "body": "The docs/readthedocs.org:ibex-core CI steps rebuilding the documentation seems to keep failing. I've seen it for multiple PRs now. The error message we get is always:\r\n```\r\n python -m sphinx -T -E -b html -d _build/doctrees -D language=en . $READTHEDOCS_OUTPUT/html\r\nRunning Sphinx v4.5.0\r\n/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/setuptools_scm/git.py:163: UserWarning: \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/checkouts/2130\" is shallow and may cause errors\r\n warnings.warn(f'\"{wd.path}\" is shallow and may cause errors')\r\nloading translations [en]... done\r\n\r\nTraceback (most recent call last):\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/registry.py\", line 438, in load_extension\r\n metadata = setup(app)\r\n ^^^^^^^^^^\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinxcontrib/applehelp/__init__.py\", line 230, in setup\r\n app.require_sphinx('5.0')\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/application.py\", line 393, in require_sphinx\r\n raise VersionRequirementError(version)\r\nsphinx.errors.VersionRequirementError: 5.0\r\n\r\nThe above exception was the direct cause of the following exception:\r\n\r\nTraceback (most recent call last):\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/cmd/build.py\", line 272, in build_main\r\n app = Sphinx(args.sourcedir, args.confdir, args.outputdir,\r\n ^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^^\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/application.py\", line 219, in __init__\r\n self.setup_extension(extension)\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/application.py\", line 380, in setup_extension\r\n self.registry.load_extension(self, extname)\r\n File \"/home/docs/checkouts/readthedocs.org/user_builds/ibex-core/envs/2130/lib/python3.11/site-packages/sphinx/registry.py\", line 441, in load_extension\r\n raise VersionRequirementError(\r\nsphinx.errors.VersionRequirementError: The sphinxcontrib.applehelp extension used by this project needs at least Sphinx v5.0; it therefore cannot be built with this version.\r\n\r\nSphinx version error:\r\nThe sphinxcontrib.applehelp extension used by this project needs at least Sphinx v5.0; it therefore cannot be built with this version.\r\n```\r\nI don't know if we can just update the Sphinx version but someone should definitely look into this."}
+{"org": "lowRISC", "repo": "ibex", "number": 2131, "state": "closed", "title": "Upgrade Verilator dependency", "body": "As discussed with @rswarbrick in PR #2129, it might be worth to upgrade the Verilator dependency. That reason is that we got some linting errors, i.e., `IMPERFECTSCH`, that were removed in more recent Verilator versions.\r\n\r\nWhen upgrading Verilator, it might also be worth to get rid of the following hack to get rid of the linting error:\r\nhttps://github.com/lowRISC/ibex/blob/2f040eb901155ea694b20ba280f33f333baf90ed/rtl/ibex_lockstep.sv#L139\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2129, "state": "closed", "title": "[rtl] Harden lockstep enable against FI", "body": "Currently, the dual-core lockstep FI mitigation is enabled/disabled using a single bit. For transient bit-flips, this is not problematic, as one bit-flip into this signal and one bit into the Ibex is required to threaten the security of the system.\r\n\r\nHowever, a permanent stuck-at-0 fault could disable the lockstep completely by targeting this signal. Then, only a single, additional fault (transient or permanent) is required.\r\n\r\nThis PR enhances the FI resilience of the Ibex lockstep by encoding this single bit into a `ibex_mubi_t` signal, i.e., a 4-bit multi-bit signal. Note that the MUXes:\r\nhttps://github.com/lowRISC/ibex/blob/2fbf04636b329bdb643501ab0ef3ee7d6b3303a9/rtl/ibex_lockstep.sv#L138\r\nand\r\nhttps://github.com/lowRISC/ibex/blob/2fbf04636b329bdb643501ab0ef3ee7d6b3303a9/rtl/ibex_lockstep.sv#L468\r\nare not redundant. However, as the goal is to protect the previously 1-bit select signal against stuck-at-0 faults, increasing the bit-width to 4-bit significantly increases security against this threat.\r\n\r\nI opted for going with a `ibex_mubi_t` instead of a `mubi4/8` as it seems that only `ibex_mubi_t` is frequently used in the core.\r\n\r\nTracked in #[20779](https://github.com/lowRISC/opentitan/issues/20779).\r\n\r\nFull DV regression looks good."}
+{"org": "lowRISC", "repo": "ibex", "number": 2101, "state": "closed", "title": "Strange performance counters after following Simple System guide", "body": "\r\n\r\n\r\n\r\nHi, I closely followed the guide in https://github.com/lowRISC/ibex/blob/master/examples/simple_system/README.md to try and simulate Ibex to run some tests, but I get strange results from the performance counters no matter the test used (everything but cycles and instructions retired is 0). I've attached the results of hello_test and dit_test respectively, can someone point me to where the simulation is going wrong?\r\n\r\n\r\n\r\n## My Environment\r\n\r\n\r\nI'm running Ibex in Visual Studio Code using an Ubuntu wsl terminal. All the pre-requisites in the simple_system guide were installed (along with RISC-V toolchain from https://github.com/lowRISC/lowrisc-toolchains/releases/tag/20230811-1), and the commands to build the simulation + software and run them are straight from the guide.\r\n\r\n**EDA tool and version:**\r\n\r\nN/A\r\n\r\n**Operating system:**\r\n\r\nUbuntu 22.04.2 LTS\r\n\r\n**Version of the Ibex source code:**\r\n\r\n7aec1404f1d406ff9d3e68f9844387fc9f44c9ac"}
+{"org": "lowRISC", "repo": "ibex", "number": 2099, "state": "open", "title": "[dv] Improve instruction trace around faulting instructions", "body": "When an executed instruction generates a fault we suppress its destination register write. On the RVFI interface this mean setting the write register index to 0. On the instruction trace this results in seeing `x0` as the destination register, rather than the actual destination register. This can be confusing. We should improve our trace output to include the actual destination register in the printed instruction along with a note the write is suppressed due to a trap.\r\n\r\nSee https://github.com/lowRISC/opentitan/issues/13134 for an example of this issue."}
+{"org": "lowRISC", "repo": "ibex", "number": 2091, "state": "closed", "title": "Building Simulation error", "body": "Building Simulation error:\r\nfusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system --RV32E=0 --RV32M=ibex_pkg::RV32MFast \r\nINFO: Preparing lowrisc:dv:crypto_prince_ref:0.1\r\nINFO: Preparing lowrisc:dv:dv_fcov_macros:0\r\nINFO: Preparing lowrisc:dv:secded_enc:0\r\nINFO: Preparing lowrisc:dv_verilator:ibex_pcounts:0\r\nINFO: Preparing lowrisc:dv_verilator:simutil_verilator:0\r\nINFO: Preparing lowrisc:ibex:ibex_pkg:0.1\r\nINFO: Preparing lowrisc:prim:primgen:0.1\r\nINFO: Preparing lowrisc:prim:ram_1p_pkg:0\r\nINFO: Preparing lowrisc:prim:ram_2p_pkg:0\r\nINFO: Preparing lowrisc:prim:util_get_scramble_params:0\r\nINFO: Preparing lowrisc:tool:check_tool_requirements:0.1\r\nINFO: Preparing lowrisc:dv:scramble_model:0\r\nINFO: Preparing lowrisc:dv_verilator:memutil_dpi:0\r\nINFO: Preparing lowrisc:lint:common:0.1\r\nINFO: Preparing lowrisc:prim:prim_pkg:0.1\r\nINFO: Preparing lowrisc:dv_verilator:memutil_dpi_scrambled:0\r\nINFO: Preparing lowrisc:dv_verilator:memutil_verilator:0\r\nINFO: Preparing lowrisc:prim:assert:0.1\r\nINFO: Preparing lowrisc:prim:cipher_pkg:0.1\r\nINFO: Preparing lowrisc:prim:clock_gating:0\r\nINFO: Preparing lowrisc:prim:clock_mux2:0\r\nINFO: Preparing lowrisc:prim:ram_1p:0\r\nINFO: Preparing lowrisc:prim:ram_2p:0\r\nINFO: Preparing lowrisc:prim:secded:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_icache:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_tracer:0.1\r\nINFO: Preparing lowrisc:ibex:sim_shared:0\r\nINFO: Preparing lowrisc:prim:buf:0\r\nINFO: Preparing lowrisc:prim:cipher:0\r\nINFO: Preparing lowrisc:prim:flop:0\r\nINFO: Preparing lowrisc:prim:lfsr:0.1\r\nINFO: Preparing lowrisc:prim:util:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_core:0.1\r\nINFO: Preparing lowrisc:prim:onehot_check:0\r\nINFO: Preparing lowrisc:prim:ram_1p_adv:0.1\r\nINFO: Preparing lowrisc:prim:ram_1p_scr:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_top:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_top_tracing:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_simple_system_core:0\r\nINFO: Preparing lowrisc:ibex:ibex_simple_system:0\r\nINFO: Generating lowrisc:prim:prim_pkg-impl:0.1\r\nCreating prim_pkg.sv\r\nCore file written to prim_pkg.core.\r\nINFO: Generating lowrisc:prim:clock_gating-impl:0\r\nImplementations for primitive clock_gating: xilinx, generic\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_clock_gating.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.sv\r\nCreating core file for primitive clock_gating.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.core\r\nINFO: Generating lowrisc:prim:clock_mux2-impl:0\r\nImplementations for primitive clock_mux2: generic, xilinx\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_clock_mux2.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_mux2-impl_0/prim_clock_mux2.sv\r\nCreating core file for primitive clock_mux2.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_mux2-impl_0/prim_clock_mux2.core\r\nINFO: Generating lowrisc:prim:ram_1p-impl:0\r\nImplementations for primitive ram_1p: generic, badbit\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_1p.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.sv\r\nCreating core file for primitive ram_1p.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.core\r\nINFO: Generating lowrisc:prim:ram_2p-impl:0\r\nImplementations for primitive ram_2p: generic\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_2p.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.sv\r\nCreating core file for primitive ram_2p.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.core\r\nINFO: Generating lowrisc:prim:buf-impl:0\r\nImplementations for primitive buf: xilinx, generic\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_buf.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_buf-impl_0/prim_buf.sv\r\nCreating core file for primitive buf.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_buf-impl_0/prim_buf.core\r\nINFO: Generating lowrisc:prim:flop-impl:0\r\nImplementations for primitive flop: xilinx, generic\r\nInspecting generic module /home/lipengfei2/disk/tmp/Ibex/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_flop.sv\r\nNo module named 'anytree'\r\nVerible parser failed, using regex fallback instead.\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_flop-impl_0/prim_flop.sv\r\nCreating core file for primitive flop.\r\nCore file written to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_flop-impl_0/prim_flop.core\r\nINFO: Wrote dependency graph to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/lowrisc_ibex_ibex_simple_system_0.deps-after-generators.dot\r\nINFO: Wrote Makefile fragment to /home/lipengfei2/disk/tmp/Ibex/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/core-deps.mk\r\nINFO: Setting up project\r\n\r\nINFO: Running pre_build script check_tool_requirements\r\nINFO: Building simulation model\r\nINFO: verilator -f lowrisc_ibex_ibex_simple_system_0.vc --trace --trace-fst --trace-structs --trace-params --trace-max-array 1024 -CFLAGS \"-std=c++11 -Wall -DVM_TRACE_FMT_FST -DTOPLEVEL_NAME=ibex_simple_system -g\" -LDFLAGS \"-pthread -lutil -lelf\" -Wall -Wwarn-IMPERFECTSCH --unroll-count 72\r\nMakefile:16: recipe for target 'Vibex_simple_system.mk' failed\r\n\r\nERROR: %Warning-MULTIDRIVEN: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:762:5: Variable written to in always_comb also written by other process (IEEE 1800-2017 9.2.2.2): 'decoded_str'\r\n : ... In instance ibex_simple_system.u_top.u_ibex_tracer\r\n ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:762:5: \r\n 762 | decoded_str = \"\";\r\n | ^~~~~~~~~~~\r\n ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:735:5: ... Location of other write\r\n 735 | decoded_str = $sformatf(\"fence\\t%s,%s\", predecessor, successor);\r\n | ^~~~~~~~~~~\r\n ... For warning description see https://verilator.org/warn/MULTIDRIVEN?v=5.016\r\n ... Use \"/* verilator lint_off MULTIDRIVEN */\" and lint_on around source to disable this message.\r\n%Warning-MULTIDRIVEN: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:763:5: Variable written to in always_comb also written by other process (IEEE 1800-2017 9.2.2.2): 'data_accessed'\r\n : ... In instance ibex_simple_system.u_top.u_ibex_tracer\r\n ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:763:5: \r\n 763 | data_accessed = 5'h0;\r\n | ^~~~~~~~~~~~~\r\n ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:702:7: ... Location of other write\r\n 702 | data_accessed = RS1 | RS2 | MEM;\r\n | ^~~~~~~~~~~~~\r\n%Warning-BLKSEQ: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer.sv:119:19: Blocking assignment '=' in sequential logic process\r\n : ... In instance ibex_simple_system\r\n : ... Suggest using delayed assignment '<='\r\n 119 | file_handle = $fopen(file_name, \"w\");\r\n | ^\r\n%Error: Exiting due to 3 warning(s)\r\nmake: *** [Vibex_simple_system.mk] Error 1\r\n\r\nERROR: Failed to build lowrisc:ibex:ibex_simple_system:0 : '['make', '-j', '16']' exited with an error: 2\r\n\r\n\r\n\r\nMY OS:\r\nNAME=\"Ubuntu\"\r\nVERSION=\"18.04.4 LTS (Bionic Beaver)\"\r\n\r\nVerilator 5.016 2023-09-16 rev v5.014-149-g57c816f90\r\n\r\nibex's git log\r\ndccad9e6a39b196261e1ba4586eb8a1711783fed\r\n\r\nThanks for your help\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2080, "state": "closed", "title": "Error installing prerequisites in Examples", "body": "Good evening, I am an undergraduate student doing research. I was trying to simulate the ibex core by following the instructions in the \"Examples\" directory and i encountered 2 issues. 1) While i was trying to install Vivado 2023.1 in Ubuntu 20.04, but the installation got stuck while \"generating device list\" 2) After cloning the ibex repo and running the command \" pip3 install -U -r python-requirements.txt\", i got an error while installing the list of prerequisites in the file (in the picture). May i know why this happened, and how to fix this ?\r\n\r\n**EDA tool and version:**\r\nXilinx Vivado 2023.1 \r\n\r\n\r\n**Operating system:**\r\nUBuntu 20.04\r\n\r\n**Version of the Ibex source code:**\r\n1eb0beafa5ed23fc0403386bf83367f7c84af669\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2077, "state": "closed", "title": "directed_test_schema.py pydantic error", "body": "When I run dv with makefile in core_ibex, pydantic gives error. I think it should be updated.\r\n\r\nThe message is like:\r\n @pydantic.root_validator()\r\n File \"/home/tutel/.local/lib/python3.8/site-packages/pydantic/deprecated/class_validators.py\", line 228, in root_validator\r\n raise PydanticUserError(\r\npydantic.errors.PydanticUserError: If you use `@root_validator` with pre=False (the default) you MUST specify `skip_on_failure=True`. Note that `@root_validator` is deprecated and should be replaced with `@model_validator`.\r\n\r\nI changed somewhere in the python script according to error message but i didn't succeed."}
+{"org": "lowRISC", "repo": "ibex", "number": 2071, "state": "open", "title": "make[1]: *** [out/metadata/tb.compile.stamp] Error 2", "body": "I am a beginner in ibex, and when I followed the github steps to test something wrong, can you tell me what I missed or did wrong?\r\nThe error message is as follows:\r\n\r\nautumn@localhost ~/ibex/dv/uvm/core_ibex$ make --keep-going IBEX_CONFIG=opentitan SIMULATOR=vcs ISS=spike ITERATIONS=1 SEED=1 TEST=riscv_arithmetic_basic_test WAVES=0 COV=0\r\nBuilding RTL testbench\r\n23:54:56 (snpslmd) OUT: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823296] \r\n23:55:19 (snpslmd) IN: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823296] \r\n23:55:19 (snpslmd) OUT: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823319] \r\n23:55:21 (snpslmd) IN: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823319] \r\nmake[1]: *** [out/metadata/tb.compile.stamp] Error 2\r\nGenerating core configuration file\r\nBuilding randomized test generator\r\n23:55:24 (snpslmd) OUT: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823324] \r\n23:55:41 (snpslmd) IN: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823324] \r\n23:55:41 (snpslmd) OUT: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823341] \r\n23:55:43 (snpslmd) IN: \"VCSCompiler_Net\" autumn@localhost.localdomain [snps_checkout_1691823341] \r\nRunning randomized test generator to create assembly file /home/autumn/ibex/dv/uvm/core_ibex/out/run/tests/riscv_arithmetic_basic_test.1/test.S\r\n23:55:44 (snpslmd) OUT: \"VCSRuntime_Net\" autumn@localhost.localdomain [snps_checkout_1691823344] \r\n23:55:51 (snpslmd) IN: \"VCSRuntime_Net\" autumn@localhost.localdomain [snps_checkout_1691823344] \r\nCompiling riscvdv test assembly to create binary at /home/autumn/ibex/dv/uvm/core_ibex/out/run/tests/riscv_arithmetic_basic_test.1/test.bin\r\nmake[1]: Target `all' not remade because of errors.\r\nmake: *** [run] Error 2\r\n\r\nHere are the details of how I use the tools:\r\n\r\nVMware:16Pro\r\nLinux:CentOS7.9\r\nVCS:2020.03-SP2-7\r\nPython:3.10.5\r\nPip:23.2.1\r\nGcc/G++:4.8.5\r\nSpike:riscv-isa-sim-ibex-cosim-v0.3\r\nPre-built toolchain:lowrisc-toolchain-gcc-rv32imcb-20230519-1\r\n\r\nFinally, some of my path information in bashrc:\r\n#riscv-gcc\r\nexport RISCV=/home/autumn/lowrisc-gcc\r\nexport RISCV_TOOLCHAIN=$RISCV\r\nexport RISCV_GCC=$RISCV/bin/riscv32-unknown-elf-gcc\r\nexport RISCV_OBJCOPY=$RISCV/bin/riscv32-unknown-elf-objcopy\r\nexport SPIKE_PATH=$RISCV/bin\r\nexport PKG_CONFIG_PATH=$RISCV/lib/pkgconfig\r\nexport PATH=$PATH:/root/.local/bin #.txt\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 2058, "state": "closed", "title": "[util,ci,dv] Update python to work with pydantic 2.0", "body": "Pydantic 2.0 was released and promptly broke our CI, the pydantic version we use has been pinned to < 2.0 to fix it again. We should fix the errors seen with 2.0 and update the version pin."}
+{"org": "lowRISC", "repo": "ibex", "number": 2054, "state": "closed", "title": "Unexpected PoR value of mstatus", "body": "\r\n### Bug Description\r\n\r\nThe [documented](https://ibex-core.readthedocs.io/en/latest/03_reference/cs_registers.html#machine-status-mstatus) power-on-reset value of the `mstatus` CSR (0x300) is 0x0000_1800. The actual PoR value is 0x0000_0080.\r\n\r\nI believe that the documented PoR value is the proper one, but the coded PoR has been in the Ibex code for three years so this is as much a question as it is a bug report.\r\n\r\n## Observed Behavior\r\n\r\nIn simulations of our fork of Ibex, coming out of reset, the read value of `mstatus` is 0x0000_0080. This is matches the coded PoR in the [RTL](https://github.com/lowRISC/ibex/blob/a7845832a2895ac3be8e28f41b87992207daee30/rtl/ibex_cs_registers.sv#L859):\r\n```\r\nlocalparam status_t MSTATUS_RST_VAL = '{mie: 1'b0,\r\n mpie: 1'b1,\r\n mpp: PRIV_LVL_U,\r\n mprv: 1'b0,\r\n tw: 1'b0};\r\n```\r\nGiven that [PRIV_LVL_U](https://github.com/lowRISC/ibex/blob/a7845832a2895ac3be8e28f41b87992207daee30/rtl/ibex_pkg.sv#L208) is 2'b00, this yields a PoR of 0x0000_0080.\r\n\r\n## Expected Behavior\r\n\r\nComing out of reset, the read value of `mstatus` should be 0x0000_1800. The RTL definition should look like this:\r\n```\r\nlocalparam status_t MSTATUS_RST_VAL = '{mie: 1'b0,\r\n mpie: 1'b0,\r\n mpp: PRIV_LVL_M,\r\n mprv: 1'b0,\r\n tw: 1'b0};\r\n```\r\n\r\n## Steps to reproduce the issue\r\n\r\nI have a test-program in CORE-V-VERIF for the CVE2, but do not have an Ibex test for this. Having said that, visual inspection easily supports what we are seeing in simulation.\r\n\r\n## My Environment\r\n\r\n\r\nThe OpenHW Group has created a fork of the Ibex which we are branding as the [CVE2](https://github.com/openhwgroup/cve2/tree/main). The first release of this project will be the CV32E20.\r\n\r\n**EDA tool and version:**\r\n\r\nQuestasim 2021.4_4\r\n\r\n**Operating system:**\r\n\r\nCentOS 7.9.2009\r\n\r\n**Version of the Ibex source code:**\r\n\r\nThe current head as of 2023-06-22 @ 10:35 EDT: `a784583`."}
+{"org": "lowRISC", "repo": "ibex", "number": 1973, "state": "closed", "title": "[rtl] Implement cycle/instret/time/hmpcountern CSRs", "body": "The cycle/instret/time/hmpcountern CSRs are optionally accessible from U-mode. In Ibex we hardwire `mcounteren` to 0 meaning these counters cannot be accessed from U-mode. However they are still accessible from M-mode. Ibex currently doesn't implement them at all which isn't standards compliant. They should be implemented."}
+{"org": "lowRISC", "repo": "ibex", "number": 1893, "state": "closed", "title": "[doc] No register file write enable glitching in documentation", "body": "It looks like we do not mention write enable glitch checking as a security countermeasure neither in register file page or in security page. It might be good to have it at least somewhere."}
+{"org": "lowRISC", "repo": "ibex", "number": 1890, "state": "closed", "title": "Cov merge fixes", "body": "This PR contains fixes that allow us to merge coverage for large numbers of iterations. Our current infrastructure will run all simulations then die without merging, due to the length of shell arguments becoming too long.\r\n\r\nThis PR contains the necessary fixes to the Ibex build system, as well as applying two patches to 'riscv-dv' and 'lowrisc_ip' from OT. These patches are necessary, but not currently in a state to be upstreamed. Applying them in this way is a short-term solution before submitting upstream, at which point the changes can be vendored in as normal, and these commits reverted.\r\n\r\nFixes #1859 "}
+{"org": "lowRISC", "repo": "ibex", "number": 1886, "state": "closed", "title": "[pmp] Add directed instr streams to increase PMP coverage", "body": "The main idea is to see some writes to `mseccfg` CSR while operating on the `pmp_full_random test` to enhance our stimulus generation and see coverage increases around sticky bit features + some no region match crosses.\r\n\r\nAlso now we enable randomising `mstatus.mprv` bit in `pmp_full_random_test` with second commit which should improve the coverage on `mprv_effect_cross`\r\n\r\nThird commit is about increasing coverage in pmpcfg0 region, enables us to see NA4 region getting configured for instruction channel with randomised execute access.\r\n\r\nNote that these changes reduces the pass rate while increasing the coverage."}
+{"org": "lowRISC", "repo": "ibex", "number": 1880, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@be9c75f", "body": "This includes the code-changes initially proposed in #1875 \r\n\r\n\r\nUpdate code from upstream repository https://github.com/google/riscv- dv to revision be9c75fe6911504c0e6e9b89dc2a7766e367c500\r\n\r\n* Reserve one extra word when pushing GPRs to kernel stack (Harry Callahan)\r\n* Store user-stack-pointer on kernel stack when pushing/popping GPRs (Harry Callahan)\r\n\r\nSigned-off-by: Harry Callahan \r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1879, "state": "closed", "title": "[dv] Add test glitching data/tag of icache", "body": "This PR addresses the integrity part of https://github.com/lowRISC/ibex/issues/1759 by verifying that a glitch on the data or tag response from the instruction cache raises a minor alert by the core (if the data/tag returned from the cache is used by the core).\r\n\r\nThe **last** commit implements the actual test. The commits before that are prerequisites as follows:\r\n1. ~~[dv] Add assert control for `NoAlertsTriggered`: duplicate from #1873, will be dropped once that PR is merged.~~\r\n2. ~~[wip] Extend vendored-in `clk_rst_if`: adds two functions to that IF -- if we agree that this is appropriate and necessary, these functions should be upstreamed.~~\r\n3. ~~[wip] Locally import `DV_CREATE_SIGNAL_PROBE_FUNCTION`: adds a macro recently added in OpenTitan (I wanted to properly vendor it in, but the update failed). If we agree that this macro should be used here, we need to fix the vendor-update problems.~~\r\n4. [dv] Add icache signals to `core_ibex_dut_probe_if`: should be fairly uncontroversial.\r\n5. [dv] Create signal probe functions in `core_ibex_dut_probe_if`: these functions have benefits over `uvm_hdl_read()`; see the commit message.\r\n\r\nPass rate is currently 100% (I tried 20 seeds) -- that is, alerts are produced and checked as expected. Every test corrupts a used data/tag of the icache, but not in every test the data/tag is valid (even when not corrupted). The test takes this into account when checking for an alert.\r\n\r\n~~Note: This test currently only works correctly if waves are being logged. Otherwise, the simulator complains that it does not have access to the icache data/tag to glitch it.~~"}
+{"org": "lowRISC", "repo": "ibex", "number": 1875, "state": "closed", "title": "Nested interrupt test fixes", "body": "> After [removing the integrity-errors generated](https://github.com/lowRISC/ibex/pull/1874/files) from uninit memory accesses, the nested_interrupt test was still failing reliably.\r\n> I think I found the reason why this test was accessing uninit memory in the first place, and propose a solution in this PR.\r\n> \r\n> Note that I am making this PR with changes directly to the vendored RISCV-DV code, with a view to upstream shortly.\r\n\r\nUpstream PR merged [here](https://github.com/google/riscv-dv/pull/906), now vendored into Ibex [here](https://github.com/lowRISC/ibex/pull/1880).\r\n\r\n> \r\n> The problem with this test currently is that riscv-dv has routines to push and pop the GPR's to the kernel-stack upon entering and exiting an interrupt handler, storing the pointer to this effective stack-frame in MSCRATCH. However, the code that allows for nested interrupts by setting xSTATUS.xIE inside the ISR also makes use of MSCRATCH to hold a temporary value that stops the program from entering more than one level of nesting. By overwriting our original pointer to the GPR's, we could not restore them when going back to our original program, hence the program state was corrupted and we would access uninit memory.\r\n> \r\n> These changes fix the problem by storing the pointer to the saved state also on the kernel mode stack, and not in the MSCRATCH csr.\r\n> This PR also raises the value of `vseq.irq_raise_seq_h.max_delay = 5000;`, which allows more instructions to be executed between our applied IRQ stimulus. Locally I see 100% of the riscv_nested_interrupt_test iterations pass within approximately 60s.\r\n\r\nDropped the RISCV-DV changes from this PR, and rebased onto master with those same changes now vendored-in.\r\nOnly remaining change in this PR is the change to `vseq.irq_raise_seq_h.max_delay`."}
+{"org": "lowRISC", "repo": "ibex", "number": 1874, "state": "closed", "title": "[dv] Disable bad integrity on uninitialised memory for selected tests", "body": "From an initial triage and test regression run these tests benefit from this."}
+{"org": "lowRISC", "repo": "ibex", "number": 1873, "state": "closed", "title": "[dv] Add test glitching PC of Ibex", "body": "This PR addresses #1755 by verifying that a glitch on the PC of Ibex raises an internal major alert in the core."}
+{"org": "lowRISC", "repo": "ibex", "number": 1872, "state": "closed", "title": "Misc fixes", "body": "This fixes https://github.com/lowRISC/ibex/issues/1863"}
+{"org": "lowRISC", "repo": "ibex", "number": 1863, "state": "closed", "title": "insn_trigger_exception coverpoint does not work", "body": "The test riscv_debug_triggers_test added in #1801 generates stimulus to hit [this coverpoint](https://github.com/lowRISC/ibex/blob/ce536ae47677e952de02b7421e1b78efb5761ab2/dv/uvm/core_ibex/fcov/core_ibex_fcov_if.sv#L502), but it does not trigger.\r\n\r\n```verilog\r\n// > core_ibex_fcov_if.sv\r\n// L502\r\n DV_FCOV_EXPR_SEEN(insn_trigger_exception, instr_id_matches_trigger_q &&\r\n id_stage_i.controller_i.fcov_pipe_flush)\r\n```\r\n\r\nREPRO\r\n```\r\n// Checkout https://github.com/lowRISC/ibex/pull/1801\r\nmake TEST=riscv_debug_triggers_test ITERATIONS=1 SEED=14664 COV=1 -j12 -ik\r\n// The instruction/event that should trigger this coverpoint can be seen retiring at t = 1010124 ns\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1861, "state": "closed", "title": "[uvm] Timed out tests do not create coverage", "body": "When a tests times out with the new UVM mechanism added in this PR: https://github.com/lowRISC/ibex/pull/1833/files\r\n\r\nTo reproduce this you can use the following version of Ibex:\r\nhttps://github.com/lowRISC/ibex/commit/e317666d4805bed58b17fdf3e663cb4ecfcd21ed\r\nAnd then run the following command in `out/uvm/core_ibex`:\r\n```\r\nmake -j7 --keep-going IBEX_CONFIG=opentitan ITERATIONS=100 TEST=riscv_pmp_full_random_test WAVES=0 COV=1\r\n```\r\nThen look in `out/run/regr.log` to find the test cases labelled as `Failed {T}` and in those test folders the `coverage` sub-directory will be empty."}
+{"org": "lowRISC", "repo": "ibex", "number": 1859, "state": "closed", "title": "[riscv-dv] Cannot merge coverage for thousands of tests", "body": "When running the following command:\r\n```\r\n make -j7 --keep-going IBEX_CONFIG=opentitan ITERATIONS=1000 TEST=riscv_pmp_full_random_test WAVES=0 COV=1\r\n```\r\n\r\nThe Makefile in `dv/uvm/core_ibex` fails when in the `riscv-dv-fcov` rule. When running that script separately, I see the following issue:\r\n```\r\nTraceback (most recent call last):\r\n File \"ibex/vendor/google_riscv-dv/cov.py\", line 344, in \r\n main()\r\n File \"ibex/vendor/google_riscv-dv/cov.py\", line 335, in main\r\n collect_cov(output_dir, cfg, cwd)\r\n File \"ibex/vendor/google_riscv-dv/cov.py\", line 207, in collect_cov\r\n sim_cov(out, cfg, cwd, opts_vec, opts_cov, csv_list)\r\n File \"ibex/vendor/google_riscv-dv/cov.py\", line 125, in sim_cov\r\n run_cmd(sim_cmd, debug_cmd=argv.debug)\r\n File \"ibex/vendor/google_riscv-dv/scripts/lib.py\", line 107, in run_cmd\r\n ps = subprocess.Popen(\"exec \" + cmd,\r\n File \"/usr/lib/python3.8/subprocess.py\", line 858, in __init__\r\n self._execute_child(args, executable, preexec_fn, close_fds,\r\n File \"/usr/lib/python3.8/subprocess.py\", line 1704, in _execute_child\r\n raise child_exception_type(errno_num, err_msg, err_filename)\r\nOSError: [Errno 7] Argument list too long: '/bin/bash'\r\n```\r\n\r\nThis error is due to the bash command being too long in terms of characters. To fix this, we could rewrite the script in RISCV-DV to use xargs.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1855, "state": "closed", "title": "Change ibex_mem_intf_response_seq to handle uninit memory differently", "body": "Reading uninit DMEM returns a random value.\r\nReading uninit IMEM returns returns `{2{C.unimp}}`.\r\n\r\n[~Integrity errors are no-longer generated.~](https://github.com/lowRISC/ibex/pull/1855#discussion_r995967300)\r\nIntegrity errors are now generated by default, but this behaviour can be disabled by settings the plusarg `+enable_bad_intg_on_uninit_access=0`\r\n\r\n\r\n\r\nGoes towards #1846 "}
+{"org": "lowRISC", "repo": "ibex", "number": 1846, "state": "closed", "title": "[dv] Tests failing when accessing uninitialized memory", "body": "When doing a load to uninitialized memory, I get the following error:\r\n```\r\nUVM_ERROR ~/ibex/vendor/lowrisc_ip/dv/sv/mem_model/mem_model.sv(35) @ 16688864: reporter [mem] read from uninitialized addr 0x7\r\n```\r\n\r\nWhen doing a fetch to unitialized memory, I get the following error:\r\n```\r\nUVM_ERROR ~/ibex/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv(162) @ 25601766: reporter [ASSERT FAILED] NoAlertsTriggered\r\n```\r\n\r\nNow for most tests this is fine, but for tests like random PMP tests you would like to be able to catch these errors. @hcallahan-lowrisc has seen similar issues when testing debug mode. My proposal would be to have a flag that says to pass when it sees these errors, but am happy to discuss alternative approaches.\r\n\r\n> Estimate 2\r\n> remaining 2022-10-14 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1837, "state": "closed", "title": "[pmp] Instruction straddling two TOR regions cosim mismatch", "body": "When running the following test:\r\n`make -j1 --keep-going IBEX_CONFIG=opentitan ITERATIONS=1 TEST=riscv_epmp_mml_test WAVES=0 COV=0 SEED=30325`\r\n\r\nIbex and Spike have different behavior. Spike throws an instruction access fault exception for the address `0x80005cc4`. The TOR region ends at `0x80005cc4`, which is the expected behavior.\r\n\r\nI think Ibex somehow does not perform the check for fetched instructions properly. In this test case there is a branch instruction that straddles two PMP entries, so Ibex must do two requests.\r\n\r\nIbex commit: 0e396d594435c0acca9df785ac40309c76576cc3\r\nSpike commit: 0dc2de5d76add7b218b31053792a676973034b9e\r\n\r\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 1831, "state": "closed", "title": "[riscv-formal] Yosys parsing fails", "body": "When running `make -C formal/riscv-formal` the Yosys toolchain emits the following error:\r\n```\r\n12. Executing Verilog-2005 frontend: build/ibex_if_stage.v\r\nParsing Verilog input from `build/ibex_if_stage.v' to AST representation.\r\nbuild/ibex_if_stage.v:333: ERROR: syntax error, unexpected TOK_STRING, expecting TOK_ID or '#'\r\nmake: *** [Makefile:76: ibex.v] Error 1\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1827, "state": "closed", "title": "`core_busy_o` not protected by lockstep", "body": "## Observed Behavior\r\nThe `core_busy_o` output signal of the non-lockstep core is used to gate the core clock, which is used by the regular Ibex core and its lockstep counterpart.\r\nhttps://github.com/lowRISC/ibex/blob/3943a4eca3917d0a00406abb36f4951304c0b394/rtl/ibex_top.sv#L211-L219\r\nhttps://github.com/lowRISC/ibex/blob/3943a4eca3917d0a00406abb36f4951304c0b394/rtl/ibex_top.sv#L286-L287\r\nhttps://github.com/lowRISC/ibex/blob/3943a4eca3917d0a00406abb36f4951304c0b394/rtl/ibex_top.sv#L927-L928\r\n\r\nThis means that the lockstep core gets gated in the same clock cycle as the regular core, even though the lockstep core is a few cycles delayed. **A low-glitch in the `core_busy_o` output of the non-lockstep core thus does not lead to a comparison mismatch and a major alert because the lockstep core is already clock-gated when it would produce the value of `core_busy_o` that is used in the comparison.**\r\nhttps://github.com/lowRISC/ibex/blob/3943a4eca3917d0a00406abb36f4951304c0b394/rtl/ibex_lockstep.sv#L453-L454\r\n\r\n\r\n\r\n## Expected Behavior\r\n\r\nA low-glitch/mismatch in the `core_busy_o` output signal of the non-lockstep core should lead to a major alert by the lockstep core.\r\n\r\n## Steps to reproduce the issue\r\nRun the `chip_sw_ibex_lockstep_glitch` test in OpenTitan (currently in https://github.com/lowRISC/opentitan/pull/15221) and override `port_idx` to the index of `core_busy_o` in `output_ports`.\r\n\r\n> estimate 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1826, "state": "closed", "title": "python flow error: `rtl_log` not substituted in dv/uvm/core_ibex/scripts/riscvdv_interface.py", "body": "\r\n\r\n\r\nThanks for help.\r\nI am just setup my new study environment.\r\nAfter I use command `make TEST=riscv_machine_mode_rand_test ITERATIONS=1 SIMULATOR=vcs`, terminal just report this:\r\n```\r\nBuild metadata already exists, not recreating from scratch.\r\nBuilding RTL testbench\r\nParameters in riscvdv command not substituted!\r\nParameters : ['']\r\nCommand : vcs\r\n -full64\r\n -f /home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/ibex_dv.f\r\n -l /home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/out/build/tb/\r\n -sverilog\r\n -ntb_opts uvm-1.2\r\n +define+UVM\r\n +define+UVM_REGEX_NO_DPI\r\n -timescale=1ns/10ps\r\n -licqueue\r\n -LDFLAGS '-Wl,--no-as-needed'\r\n -CFLAGS '--std=c99 -fno-extended-identifiers'\r\n -Mdir=/home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/out/build/tb/vcs_simv.csrc\r\n -o /home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/out/build/tb/vcs_simv\r\n -debug_access+pp\r\n -xlrm uniq_prior_final\r\n -CFLAGS '--std=c99 -fno-extended-identifiers'\r\n -lca -kdb\r\n -pvalue+core_ibex_tb_top.RV32E=0 +define+IBEX_CFG_RV32M=ibex_pkg::RV32MSingleCycle +define+IBEX_CFG_RV32B=ibex_pkg::RV32BOTEarlGrey +define+IBEX_CFG_RegFile=ibex_pkg::RegFileFF -pvalue+core_ibex_tb_top.BranchTargetALU=1 -pvalue+core_ibex_tb_top.WritebackStage=1 -pvalue+core_ibex_tb_top.ICache=1 -pvalue+core_ibex_tb_top.ICacheECC=1 -pvalue+core_ibex_tb_top.ICacheScramble=1 -pvalue+core_ibex_tb_top.BranchPredictor=0 -pvalue+core_ibex_tb_top.DbgTriggerEn=1 -pvalue+core_ibex_tb_top.SecureIbex=1 -pvalue+core_ibex_tb_top.PMPEnable=1 -pvalue+core_ibex_tb_top.PMPGranularity=0 -pvalue+core_ibex_tb_top.PMPNumRegions=16 -pvalue+core_ibex_tb_top.MHPMCounterNum=10 -pvalue+core_ibex_tb_top.MHPMCounterWidth=32 -f /home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/ibex_dv_cosim_dpi.f -LDFLAGS '-Wl,-rpath,/opt/riscv/ibex_toolchain/lib' -CFLAGS '-I/opt/riscv/ibex_toolchain/include -I/opt/riscv/ibex_toolchain/include/softfloat -I/opt/riscv/ibex_toolchain/include' -CFLAGS '-I/home/ser_lip/Projects/ibex/ibex/dv/cosim' -L/opt/riscv/ibex_toolchain/lib -lriscv -lsoftfloat -ldl -ldisasm -lfdt -lstdc++\r\n\r\nTraceback (most recent call last):\r\n File \"/home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/scripts/compile_tb.py\", line 108, in \r\n sys.exit(_main())\r\n File \"/home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/scripts/compile_tb.py\", line 85, in _main\r\n md.tb_build_cmds = riscvdv_interface.get_tool_cmds(\r\n File \"/home/ser_lip/.local/lib/python3.10/site-packages/typeguard/__init__.py\", line 1033, in wrapper\r\n retval = func(*args, **kwargs)\r\n File \"/home/ser_lip/Projects/ibex/ibex/dv/uvm/core_ibex/scripts/riscvdv_interface.py\", line 165, in get_tool_cmds\r\n raise RuntimeError\r\nRuntimeError\r\n```\r\nI find that the `` is not substituted by the real file name. \r\n\r\nThanks a lot.\r\n\r\n## My Environment\r\n\r\n\r\nJust setup the latest environment.\r\nlatest ibex master branch with no edit. `3943a4eca3917d0a00406abb36f4951304c0b394`\r\nSpike. ibex-cosim-v0.3\r\nToolchain. lowrisc-toolchain-rv32imcb-20220524-1 release.\r\n\r\n**EDA tool and version:**\r\n\r\nSynopsys VCS 2018.09\r\n\r\n**Operating system:**\r\n\r\nUbuntu Linux Desktop 22.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\nlatest ibex master branch with no edit. \r\n```\r\n3943a4eca3917d0a00406abb36f4951304c0b394\r\nAuthor: Marno van der Maas \r\nDate: Tue Sep 27 11:36:50 2022 +0100\r\n\r\n [pmp] Remove off mode from pmp_*_mode_cross coverpoints\r\n```\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1825, "state": "closed", "title": "[dv] Implement testing and coverage for various mstatus states", "body": "I recently discovered Ibex enabled/disabled interrupts in U mode based on the mstatus.mie bit which is a violation of the spec (mie applies only to M-mode in U mode it is ignored, only the per interrupt MIE CSR bits should be considered. This is fixed in https://github.com/lowRISC/ibex/pull/1824\r\n\r\nI found this when adding interrupts to the debug single step test, which does execute code in U mode with mstatus.mie set to 0, but clearly other testing (in particular the interrupt tests) don't do this otherwise we would have found this bug earlier.\r\n\r\nThis indicates a gap in our testing. We should add some coverage over different mstatus states that checks we see various states across U-mode/M-mode and with interrupts/debugs/exceptions occurring.\r\n\r\nCoverpoints:\r\n\r\n- [x] cross - priv_modes, interrupts, mstatus.MIE (excluding mstatus.MIE == 1 && priv_mode == MACHINE as interrupt will not be taken in that case)\r\n- [x] cross - priv_modes, exceptions\r\n\r\nExisting tests will require expanding to meet the new coverage\r\n\r\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 1823, "state": "closed", "title": "[dv] Implement double fault loop detector", "body": "Add a double fault loop detector to the testbench. It should determine when Ibex has entered a loop of double faults and terminate the simulation after some configurable number of iterations (with a default e.g. 100).\r\n\r\nBy default is should exit with a fail but a configuration option should be supplied to enable exit with a pass (for tests where a double fault loop is the intended behaviour).\r\n\r\n> estimate 4\r\n> remaining 2022-10-12 1\r\n> remaining 2022-10-17 0\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1820, "state": "closed", "title": "Ibex DV environment does not configure spike to have a matching number of performance counters", "body": "@ctopal \r\n\r\n## Observed Behavior\r\nCosimulation mismatch when reading from mhpmevent15 register in a randomly-generated program.\r\n```\r\n[E] 463: UVM_FATAL /home/harry/projects/ibex/dv/uvm/core_ibex/common/ibex_cosim_agent/ibex_cosim_scoreboard.sv(142) @ 50550: uvm_test_top.env.cosim_agent.scoreboard [uvm_test_top.env.cosim_agent.scoreboard]\r\n 464: Cosim mismatch : 0) Register write data mismatch to x27 DUT: 0 expected: 1000\r\n```\r\n\r\nThe `opentitan` ibex_config specifies 10 performance counters. Spike defaults to having all 29 possible counters. Hence, due to the one-hot style in which [our spike fork](https://github.com/lowRISC/riscv-isa-sim/blob/68edd1799d812a12ec181830cb21681e48ee1093/riscv/processor.cc#L220) initializes the event registers to match those in the Ibex (see PR [here](https://github.com/lowRISC/riscv-isa-sim/pull/5)), we initialize registers in spike that don't exist in Ibex. Hence when an instruction reads those registers, which read 0 for unimplemented performance counters in Ibex, we get a cosimulation mismatch.\r\n\r\n> estimate 4\r\n> remaining 2022-10-06 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1814, "state": "closed", "title": "[rtl] Ibex services interrupts when single stepping", "body": "Ibex hard-codes `dcsr.stepie` to 0, meaning when single-stepping is enabled all interrupts should be masked. From trials with debugging on https://github.com/GregAC/ibex_super_system this is not the observed behaviour, a single step can enter an instruction handler.\r\n\r\nIn addition to fixing this we should look at our existing DV to determine if this bug could have been caught by it (single step tests are failing in the nightly regression so potentially have already found the bug, we just haven't had the time to look at the failures yet)\r\n\r\nIncreased estimate as I've spent time on testing this and not yet finished. Fix is available as a PR.\r\nold estimate 4\r\n> estimate 6\r\n> remaining 2022-09-23 4\r\n> remaining 2022-09-30 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1799, "state": "closed", "title": "[dv] Out of bounds access in dside access tracking logic", "body": "This line: https://github.com/lowRISC/ibex/blob/056cb44ff75f797898709546ea1b0fd08d862e1a/rtl/ibex_top.sv#L1092\r\n\r\nUses `i - 1` and it's possible to evaluate this condition when `i == 0` giving an out of bounds access. This logic needs refactoring to more explicitly split out the `i == 0` case from the others to ensure this does not occur.\r\n\r\n> estimate 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1795, "state": "open", "title": "[dv] CSR Coverage Waiver", "body": "### Coverpoints/bins affected\n - `cp_csr_read_only`/`cp_csr_write`\n - `CSR_SCONTEXT`\n - `CSR_MCONTEXT`\n - `CSR_MSECCFGH`\n - `CSR_TDATA3`\n - `CSR_MCOUNTINHIBIT`\n - `CSR_MENVCFGH`\n - `cp_ignored_csrs` / `cp_ignored_csrs_w`\n - `CSR_SCONTEXT`, `CSR_MCONTEXT`, `CSR_TDATA3` are also the ignored CSRs, remove this coverpoint?\n\n### Justification\nNone of these is particularly complex but it's all small changes to spike that add up.\n\n`CSR_SCONTEXT` / `CSR_MCONTEXT` are optional CSRs only accessible in debug mode, Ibex implements them as read as 0, write ignore. They do not need to implemented and aren't used by our debug setup. As they're not accessible via debug mode this is a low priority item to test\n\n`CSR_MSECCFGH`/`CSR_MENVCFGH` - These CSRs have no implemented bits and are only accessible in M mode. They're in the M mode only CSR space so the generic check that accesses from U mode cause illegal instruction exceptions is sufficiently testing by other illegal CSR accesses from U mode.\n\n`CSR_TDATA3` - This is accessible in M mode and is an optional CSR for debug trigger points, Ibex implements it as read as 0 write ignore.\n\n`CSR_MCOUNTINHIBIT` - The controls the performance counters and is not a high priority item.\n\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 1787, "state": "closed", "title": "[dv] More flexible riscv_core_setting.sv generation", "body": "Currently the DV flow patches the `riscv_core_setting.sv` file if certain configs are used to remove CSRs those configs do not have and adjust PMP settings.\r\n\r\nWe need something more flexible that can look directly at the Ibex config and generate the file based upon settings in there.\r\n\r\nIn particular we need this to enable https://github.com/lowRISC/ibex/pull/1776. With better CSR coverage we're seeing failures in different configs due to different CSR setups.\r\n\r\nI would suggest we an existing python templating library (e.g. Jinja2). We'll need a small python script that can read in the ibex config and pass it through to jinja2 to produce the final `riscv_core_setting.sv`.\r\n\r\n@marnovandermaas @ctopal @hcallahan-lowrisc any thoughts?\r\n\r\n(Estimate based on us following my idea above)\r\n\r\n> estimate 4\r\n> remaining 2022-08-23 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1777, "state": "closed", "title": "[dv] Randomize code and stack regions for PMP tests", "body": "When running the `riscv_pmp_full_random_test`, we want it to choose a random entry to give execution privilege to instructions and read/write privilege to the stack. This issue was initially a part of subtask 2 of this issue: https://github.com/lowRISC/ibex/issues/1702\r\n\r\nOld estimate 2022-08-19: 16\r\n> estimate 10\r\n> remaining 2022-08-16 12\r\n> remaining 2022-08-18 10\r\n> remaining 2022-08-19 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1775, "state": "closed", "title": "Bug in reset behaviour for cosimulation", "body": "## Observed Behavior\r\nNightly regression failures for the test `riscv_reset_test` commonly have the following error : \r\n```\r\nUVM_FATAL /home/harry/projects/ibex/dv/uvm/core_ibex/common/ibex_cosim_agent/ibex_cosim_scoreboard.sv(138) @ 746774: uvm_test_top.env.cosim_agent.scoreboard [uvm_test_top.env.cosim_agent.scoreboard] Cosim mismatch Synchronous trap was expected at ISS PC: 80000000 but the DUT didn't report one at PC 80000080\r\n```\r\nThis appears to be something to do with the way the reset stimulus is passed onto the cosimulated ISS. The ISS appears to read 0x0 from it's memory model from the first address out of reset. Maybe the memory model needs to be reinitialized? I haven't looked too closely at it.\r\nThe ISS trace will contain the following...\r\n```\r\ncore 0: 0x80000080 (0x00000000) c.unimp\r\ncore 0: exception trap_illegal_instruction, epc 0x80000080\r\ncore 0: tval 0x00000000\r\n```\r\n(The trace/log is overwritten upon each reset, this could be improved to just append to an existing file. [See here](https://github.com/lowRISC/ibex/blob/2f8dfa9dfe2d938228118ed8ab6a543804d0c9ae/dv/uvm/core_ibex/common/ibex_cosim_agent/ibex_cosim_scoreboard.sv#L63).)\r\n\r\n## Expected Behavior\r\n\r\n## Steps to reproduce the issue\r\n```\r\ncd dv/uvm/core_ibex/\r\nmake TEST=riscv_reset_test ITERATIONS=1 -j12 -ik SEED=9894\r\n```\r\n> estimate 8"}
+{"org": "lowRISC", "repo": "ibex", "number": 1772, "state": "closed", "title": "Cosim mismatch when reading DCSR.cause", "body": "## Observed Behavior\r\nTest failures with the following error : \r\n```\r\nUVM_FATAL ibex_cosim_scoreboard.sv(138) @ 4049807: Cosim mismatch Register write data mismatch to x22 DUT: 40000100 expected: 400000c0\r\n```\r\n\r\nThis fails upon reading from `DCSR.cause`\r\nIn this case : \r\n\r\n\r\n(IBEX)\r\n\r\n\r\n(SPIKE)\r\n\r\nObserving the waveform below, we can see that `debug_req_i` is de-asserted shortly after `debug_mode_i` goes low due to leaving debug mode from a dret. We do re-enter debug mode, but the cause can be seen to be recorded as `DBG_CAUSE_STEP`. In spike, we read back `DBG_CAUSE_HALTREQ` at the same instruction, hence the mismatch.\r\n\r\n## Expected Behavior\r\n\r\nIbex should record `DCSR.cause` as DBG_CAUSE_HALTREQ.\r\n\r\nI think this might be due to the [ibex_controller.sv ](https://github.com/lowRISC/ibex/blob/2f8dfa9dfe2d938228118ed8ab6a543804d0c9ae/rtl/ibex_controller.sv#L662)state machine sampling the `debug_req_i` signal to determine the correct `cause` one cycle later than the decision to enter debug_mode.\r\n\r\n## Steps to reproduce the issue\r\n```\r\ncd dv/uvm/core_ibex/\r\nmake TEST=riscv_debug_basic_test ITERATIONS=1 WAVES=1 SEED=9892 -j12 -ik\r\n```\r\n\r\n\r\n> estimate 8\r\n> remaining 2022-09-27 4\r\n> remaining 2022-10-12 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1765, "state": "closed", "title": "[dv] Investigate issues in mixed interrupts/traps/debug tests", "body": "> estimate 16\r\n> remaining 2022-09-28 8"}
+{"org": "lowRISC", "repo": "ibex", "number": 1762, "state": "closed", "title": "[dv] Security Feature Coverage", "body": "Document and add coverage points then ensure they're getting hit for:\r\n\r\n- [x] Data independent timing enabled whilst executing all instruction categories - Estimate 2\r\n- [x] Random instruction generation\r\n - [x] enabled whilst executing all instruction categories - Estimate 2\r\n - [x] Random instruction generated, for all possible kinds of random instruction - Estimate 2\r\n - [x] Cross of different generator configurations - Estimate 2\r\n- [x] Various faults seen - Estimate 2\r\n - [x] Register File ECC fault seen\r\n - [x] Register File write enable glitch fault seen \r\n - [x] Lockstep glitch fault seen\r\n - [x] Icache ECC Fault seen\r\n\r\noriginal estimate: 10\r\n> estimate 4\r\n> remaining 2022-11-01 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1761, "state": "closed", "title": "[dv] Add instructions to enable/disable random instruction generation to existing tests", "body": "Ensure CSR writes that will enable and disable the random instruction generator are emitted for some tests. This is mostly dealt with via on-going CSR work. The task here is just to use the new functionality to stimulate the random instruction generator. Some extra work may be required to ensure the randomly generated instructions don't get fed into co-sim checking (but we do ensure they have no effect on architectural state).\r\n\r\n> estimate 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1760, "state": "closed", "title": "[dv] Verify double fault behaviour", "body": "Ibex has a double fault detector. A checker should be created to ensure this functions correctly and double faults should be stimulated in some tests.\r\n\r\nVarious work has been happening in this area, as a result this issue is less effort than originally estimated.\r\nold estimate: 4\r\n> estimate 2\r\n> remaining 2022-11-8 1\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1759, "state": "closed", "title": "[dv] Verify ICache Integrity and Scrambling", "body": "Verify the ICache integrity and scrambling features\r\n\r\nFor integrity create a testbench component to corrupt icache data and icache tags. Ensure corruptions triggered the required alert. This will require targeting to corrupt data and tags that relate to instructions that are going to get execute. Understanding of scrambling will need to be employed to determine the appropriate memory locations to corrupt.\r\n\r\nFor scrambling I'm uncertain if we need to do anything further as we're using a existing OT primitive component. @ctopal any thoughts from your OTBN experience? \r\n\r\nold estimate 16, new estimate based upon more detailed analysis by @andreaskurth \r\n> estimate 4\r\n> remaining 2022-10-28 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1756, "state": "closed", "title": "[dv] Verify register file integrity checking and write enable glitch detection", "body": "Create a testbench component that can corrupt bits and glitch the one hot write enable in the register file.\r\n\r\nWrite a test that uses this and checks the appropriate alert is signaled.\r\n\r\noriginal estimate 8\r\n> estimate 4\r\n> remaining 2022-10-28 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1755, "state": "closed", "title": "[dv] Verify PC integrity check", "body": "Verify the PC Integrity checking countermeasure. This will involve corrupting the PC and checking the appropriate alert occurs. Ideally we will not disable the co-simulation checking around this which should be feasible as we shouldn't be retiring any instructions that involve the corrupted PC.\r\n\r\nWrite a testbench component to corrupt the PC and employ it within a suitable test.\r\n\r\n> estimate 8\r\n> remaining 2022-10-14 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1743, "state": "closed", "title": "Ibex DCSR.cause priority encoding does not match debug-spec 0.13.2 or 1.0.0-STABLE", "body": "\r\n\r\n## Observed Behavior\r\n\r\nWhile testing single-step behaviour, a cosimulation-mismatch was encountered when reading DCSR.cause. It was tracked down to a simultaneous assertion of DCSR.step and debug_req_i when entering debug_mode, and I believe that the spike behaviour is correct in this case.\r\nAccording to both debug specifications [0.13.2](https://riscv.org/wp-content/uploads/2019/03/riscv-debug-release.pdf) and [1.0.0-STABLE](https://raw.githubusercontent.com/riscv/riscv-debug-spec/master/riscv-debug-stable.pdf), the priority among reporting DCSR.cause has **step** (0) as a lower priority than **haltreq** (1). Ibex [currently reports](https://ibex-core.readthedocs.io/en/latest/03_reference/debug.html#debug-support) debug support in compliance with the RISCV Debug Specification Version 0.13.\r\nCurrent ibex behaviour is a priority-encoder [which places **step** above **haltreq**](https://github.com/lowRISC/ibex/blob/c4a97e05f5853b25e40fa1ea5b4edcfafba9a370/rtl/ibex_controller.sv#L662).\r\n\r\n\r\n## Expected Behavior\r\n\r\nIbex should prioritize reporting DCSR.cause as **haltreq** above **step** when entering debug_mode with both stimulus present.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1740, "state": "closed", "title": "[rtl,epmp] Prevent addition of executable regions as required by the specification", "body": "The Smepmp specification states:\r\n\r\n> Adding a rule with executable privileges that either is M-mode-only or a locked Shared-Region is not possible and such pmpcfg writes are ignored, leaving pmpcfg unchanged. This restriction can be temporarily lifted e.g. during the boot process, by setting mseccfg.RLB.****\r\n\r\nThis was overlooked during the original epmp implementation and must be added.\r\n\r\n> estimate 2\r\n> remaining 2022-18-08 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1736, "state": "closed", "title": "[rtl,bug] Ibex allows execution in no-match case while MML=1", "body": "Header explains the issue. According to Smepmp v1.0 in a no-match case we should block execution in machine mode. However, we are not currently doing that. It's a tricky thing to recreate it in our master branch for now but if you add #1695 and #1735 to master and run: `make ITERATIONS=1 TEST=riscv_pmp_full_random_test SEED=14910` you should be able to re-create the error.\r\n\r\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 1728, "state": "closed", "title": "[dv,core_ibex] Instantiate Scrambling Key Interface in core_ibex DV", "body": "If we are starting to issue `FENCE.I` instructions, we definitely need to drive scrambling key ports so that ICache would have a valid key. Currently we don't have a valid key, so we are stuck at an invalidating state.\r\n\r\n>estimate 4\r\n>remaining 2022-07-27 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1727, "state": "closed", "title": "[dv] Drive Xs on interfaces where appropriate", "body": "https://github.com/lowRISC/ibex/issues/1645 has highlighted in some circumstances we're not driving Xs on the data memory response where we should (for non read responses rdata_i and rdata_intg_i should be X). Fix this specific case and check for any other cases where we're not driving X where we should be.\r\n\r\nEstimate updated as actual work was smaller than anticipated\r\nOld estimate: 4\r\n> estimate 2\r\n> remaining 2022-08-26 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1720, "state": "closed", "title": "[dv] Exception divergence using MML PMP mode", "body": "\r\nI'm seeing a divergence between Spike and Ibex when in MML mode and setting region 0 to read only. Spike throws a trap and Ibex zeroes out a destination register. I'm not sure if this is an issue with Spike, Ibex or with the UVM comparison.\r\n\r\n## Observed Behavior\r\n\r\nCosimulation result:\r\n```\r\nname: riscv_epmp_mml_read_only_test\r\nseed: 14822\r\nbinary: out/run/riscv_epmp_mml_read_only_test.14822/test.o\r\nuvm_log: out/run/riscv_epmp_mml_read_only_test.14822/rtl.log\r\nrtl_trace: out/run/riscv_epmp_mml_read_only_test.14822/trace_core_00000000.log\r\nrtl_trace_csv: out/run/riscv_epmp_mml_read_only_test.14822/trace_core_00000000.log.csv\r\niss_trace: \r\niss_trace_csv: \r\nen_cosim: True\r\ncosim_trace: \r\ncosim_trace_csv: \r\ncomparison_log: \r\npassed: False\r\nfailure_message: |-\r\n UVM_FATAL /home/mvdmaas/ibex/dv/uvm/core_ibex/common/ibex_cosim_agent/ibex_cosim_scoreboard.sv(131) @ 7304: uvm_test_top.env.cosim_agent.scoreboard [ibex_cosim_agent_pkg::ibex_cosim_scoreboard.run_cosim_rvfi] Cosim mismatch Synchronous trap was expected at ISS PC: 80001900 but DUT didn't report one at PC 80000118\r\n [FAILED]: sim error seen\r\n```\r\n\r\nIbex RVFI trace:\r\n```\r\nTime\tCycle\tPC\tInsn\tDecoded instruction\tRegister and memory contents\r\n 2524\t 24\t80000080\t400015b7\tlui\tx11,0x40001\t x11=0x40001000\r\n 2864\t 41\t80000084\t10658593\taddi\tx11,x11,262\t x11:0x40001000 x11=0x40001106\r\n 3004\t 48\t80000088\t30159073\tcsrrw\tx0,misa,x11\t x11:0x40001106 x0=0x00000000\r\n 3024\t 49\t8000008c\t0002c397\tauipc\tx7,0x2c\t x7=0x8002c08c\r\n 3444\t 70\t80000090\tc5838393\taddi\tx7,x7,-936\t x7:0x8002c08c x7=0x8002bce4\r\n 3724\t 84\t80000094\t00002597\tauipc\tx11,0x2\t x11=0x80002094\r\n 3744\t 85\t80000098\t86c58593\taddi\tx11,x11,-1940\t x11:0x80002094 x11=0x80001900\r\n 3944\t 95\t8000009c\t0015e593\tori\tx11,x11,1\t x11:0x80001900 x11=0x80001901\r\n 4364\t 116\t800000a0\t30559073\tcsrrw\tx0,mtvec,x11\t x11:0x80001901 x0=0x00000000\r\n 4384\t 117\t800000a4\t00002b17\tauipc\tx22,0x2\t x22=0x800020a4\r\n 4404\t 118\t800000a8\t2f0b0b13\taddi\tx22,x22,752\t x22:0x800020a4 x22=0x80002394\r\n 4424\t 119\t800000ac\t002b5b13\tsrli\tx22,x22,0x2\t x22:0x80002394 x22=0x200008e5\r\n 4584\t 127\t800000b0\t3b0b1073\tcsrrw\tx0,pmpaddr0,x22\t x22:0x200008e5 x0=0x00000000\r\n 4604\t 128\t800000b4\t74725073\tcsrrwi\tx0,0x747,4\t x0=0x00000000\r\n 4924\t 144\t800000b8\t08c00b13\taddi\tx22,x0,140\t x0:0x00000000 x22=0x0000008c\r\n 4944\t 145\t800000bc\t3a0b1073\tcsrrw\tx0,pmpcfg0,x22\t x22:0x0000008c x0=0x00000000\r\n 4964\t 146\t800000c0\t7472d073\tcsrrwi\tx0,0x747,5\t x0=0x00000000\r\n 4984\t 147\t800000c4\t00002b17\tauipc\tx22,0x2\t x22=0x800020c4\r\n 5024\t 149\t800000c8\t2d0b0b13\taddi\tx22,x22,720\t x22:0x800020c4 x22=0x80002394\r\n 5124\t 154\t800000cc\t6589\tc.lui\tx11,0x2\t x11=0x00002000\r\n 5544\t 175\t800000ce\t66658593\taddi\tx11,x11,1638\t x11:0x00002000 x11=0x00002666\r\n 5564\t 176\t800000d2\t9b2e\tc.add\tx22,x11\t x22:0x80002394 x11:0x00002666 x22=0x800049fa\r\n 5584\t 177\t800000d4\t002b5b13\tsrli\tx22,x22,0x2\t x22:0x800049fa x22=0x2000127e\r\n 5604\t 178\t800000d8\t3b1b1073\tcsrrw\tx0,pmpaddr1,x22\t x22:0x2000127e x0=0x00000000\r\n 5664\t 181\t800000dc\t00002b17\tauipc\tx22,0x2\t x22=0x800020dc\r\n 5804\t 188\t800000e0\t2b8b0b13\taddi\tx22,x22,696\t x22:0x800020dc x22=0x80002394\r\n 5824\t 189\t800000e4\t6595\tc.lui\tx11,0x5\t x11=0x00005000\r\n 5944\t 195\t800000e6\tccc58593\taddi\tx11,x11,-820\t x11:0x00005000 x11=0x00004ccc\r\n 5964\t 196\t800000ea\t9b2e\tc.add\tx22,x11\t x22:0x80002394 x11:0x00004ccc x22=0x80007060\r\n 6364\t 216\t800000ec\t002b5b13\tsrli\tx22,x22,0x2\t x22:0x80007060 x22=0x20001c18\r\n 6384\t 217\t800000f0\t3b2b1073\tcsrrw\tx0,pmpaddr2,x22\t x22:0x20001c18 x0=0x00000000\r\n 6644\t 230\t800000f4\t00002b17\tauipc\tx22,0x2\t x22=0x800020f4\r\n 6704\t 233\t800000f8\t2a0b0b13\taddi\tx22,x22,672\t x22:0x800020f4 x22=0x80002394\r\n 6724\t 234\t800000fc\t659d\tc.lui\tx11,0x7\t x11=0x00007000\r\n 6744\t 235\t800000fe\t33258593\taddi\tx11,x11,818\t x11:0x00007000 x11=0x00007332\r\n 6764\t 236\t80000102\t9b2e\tc.add\tx22,x11\t x22:0x80002394 x11:0x00007332 x22=0x800096c6\r\n 6784\t 237\t80000104\t002b5b13\tsrli\tx22,x22,0x2\t x22:0x800096c6 x22=0x200025b1\r\n 6924\t 244\t80000108\t3b3b1073\tcsrrw\tx0,pmpaddr3,x22\t x22:0x200025b1 x0=0x00000000\r\n 7104\t 253\t8000010c\t8f8f9b37\tlui\tx22,0x8f8f9\t x22=0x8f8f9000\r\n 7124\t 254\t80000110\tf8fb0b13\taddi\tx22,x22,-113\t x22:0x8f8f9000 x22=0x8f8f8f8f\r\n 7264\t 261\t80000114\t3a0b1073\tcsrrw\tx0,pmpcfg0,x22\t x22:0x8f8f8f8f x0=0x00000000\r\n 7284\t 262\t80000118\t00002b17\tauipc\tx22,0x2\t x22=0x80002118\r\n 7304\t 263\t8000011c\t27cb0b13\taddi\tx0,x0,636\t x0:0x00000000 x0=0x00000000\r\n```\r\n\r\nSpike RVFI trace:\r\n```\r\ncore 0: 0x80000080 (0x400015b7) lui a1, 0x40001\r\ncore 0: 3 0x80000080 (0x400015b7) x11 0x40001000\r\ncore 0: 0x80000084 (0x10658593) addi a1, a1, 262\r\ncore 0: 3 0x80000084 (0x10658593) x11 0x40001106\r\ncore 0: 0x80000088 (0x30159073) csrw misa, a1\r\ncore 0: 3 0x80000088 (0x30159073) c769_misa 0x40901104\r\ncore 0: 0x8000008c (0x0002c397) auipc t2, 0x2c\r\ncore 0: 3 0x8000008c (0x0002c397) x7 0x8002c08c\r\ncore 0: 0x80000090 (0xc5838393) addi t2, t2, -936\r\ncore 0: 3 0x80000090 (0xc5838393) x7 0x8002bce4\r\ncore 0: 0x80000094 (0x00002597) auipc a1, 0x2\r\ncore 0: 3 0x80000094 (0x00002597) x11 0x80002094\r\ncore 0: 0x80000098 (0x86c58593) addi a1, a1, -1940\r\ncore 0: 3 0x80000098 (0x86c58593) x11 0x80001900\r\ncore 0: 0x8000009c (0x0015e593) ori a1, a1, 1\r\ncore 0: 3 0x8000009c (0x0015e593) x11 0x80001901\r\ncore 0: 0x800000a0 (0x30559073) csrw mtvec, a1\r\ncore 0: 3 0x800000a0 (0x30559073) c773_mtvec 0x80001901\r\ncore 0: 0x800000a4 (0x00002b17) auipc s6, 0x2\r\ncore 0: 3 0x800000a4 (0x00002b17) x22 0x800020a4\r\ncore 0: 0x800000a8 (0x2f0b0b13) addi s6, s6, 752\r\ncore 0: 3 0x800000a8 (0x2f0b0b13) x22 0x80002394\r\ncore 0: 0x800000ac (0x002b5b13) srli s6, s6, 2\r\ncore 0: 3 0x800000ac (0x002b5b13) x22 0x200008e5\r\ncore 0: 0x800000b0 (0x3b0b1073) csrw pmpaddr0, s6\r\ncore 0: 3 0x800000b0 (0x3b0b1073) c944_pmpaddr0 0x200008e5\r\ncore 0: 0x800000b4 (0x74725073) csrwi mseccfg, 4\r\ncore 0: 3 0x800000b4 (0x74725073) c1863_mseccfg 0x00000004\r\ncore 0: 0x800000b8 (0x08c00b13) li s6, 140\r\ncore 0: 3 0x800000b8 (0x08c00b13) x22 0x0000008c\r\ncore 0: 0x800000bc (0x3a0b1073) csrw pmpcfg0, s6\r\ncore 0: 3 0x800000bc (0x3a0b1073) c928_pmpcfg0 0x0000008c\r\ncore 0: 0x800000c0 (0x7472d073) csrwi mseccfg, 5\r\ncore 0: 3 0x800000c0 (0x7472d073) c1863_mseccfg 0x00000005\r\ncore 0: 0x800000c4 (0x00002b17) auipc s6, 0x2\r\ncore 0: 3 0x800000c4 (0x00002b17) x22 0x800020c4\r\ncore 0: 0x800000c8 (0x2d0b0b13) addi s6, s6, 720\r\ncore 0: 3 0x800000c8 (0x2d0b0b13) x22 0x80002394\r\ncore 0: 0x800000cc (0x00006589) c.lui a1, 0x2\r\ncore 0: 3 0x800000cc (0x6589) x11 0x00002000\r\ncore 0: 0x800000ce (0x66658593) addi a1, a1, 1638\r\ncore 0: 3 0x800000ce (0x66658593) x11 0x00002666\r\ncore 0: 0x800000d2 (0x00009b2e) c.add s6, a1\r\ncore 0: 3 0x800000d2 (0x9b2e) x22 0x800049fa\r\ncore 0: 0x800000d4 (0x002b5b13) srli s6, s6, 2\r\ncore 0: 3 0x800000d4 (0x002b5b13) x22 0x2000127e\r\ncore 0: 0x800000d8 (0x3b1b1073) csrw pmpaddr1, s6\r\ncore 0: 3 0x800000d8 (0x3b1b1073) c945_pmpaddr1 0x2000127e\r\ncore 0: 0x800000dc (0x00002b17) auipc s6, 0x2\r\ncore 0: 3 0x800000dc (0x00002b17) x22 0x800020dc\r\ncore 0: 0x800000e0 (0x2b8b0b13) addi s6, s6, 696\r\ncore 0: 3 0x800000e0 (0x2b8b0b13) x22 0x80002394\r\ncore 0: 0x800000e4 (0x00006595) c.lui a1, 0x5\r\ncore 0: 3 0x800000e4 (0x6595) x11 0x00005000\r\ncore 0: 0x800000e6 (0xccc58593) addi a1, a1, -820\r\ncore 0: 3 0x800000e6 (0xccc58593) x11 0x00004ccc\r\ncore 0: 0x800000ea (0x00009b2e) c.add s6, a1\r\ncore 0: 3 0x800000ea (0x9b2e) x22 0x80007060\r\ncore 0: 0x800000ec (0x002b5b13) srli s6, s6, 2\r\ncore 0: 3 0x800000ec (0x002b5b13) x22 0x20001c18\r\ncore 0: 0x800000f0 (0x3b2b1073) csrw pmpaddr2, s6\r\ncore 0: 3 0x800000f0 (0x3b2b1073) c946_pmpaddr2 0x20001c18\r\ncore 0: 0x800000f4 (0x00002b17) auipc s6, 0x2\r\ncore 0: 3 0x800000f4 (0x00002b17) x22 0x800020f4\r\ncore 0: 0x800000f8 (0x2a0b0b13) addi s6, s6, 672\r\ncore 0: 3 0x800000f8 (0x2a0b0b13) x22 0x80002394\r\ncore 0: 0x800000fc (0x0000659d) c.lui a1, 0x7\r\ncore 0: 3 0x800000fc (0x659d) x11 0x00007000\r\ncore 0: 0x800000fe (0x33258593) addi a1, a1, 818\r\ncore 0: 3 0x800000fe (0x33258593) x11 0x00007332\r\ncore 0: 0x80000102 (0x00009b2e) c.add s6, a1\r\ncore 0: 3 0x80000102 (0x9b2e) x22 0x800096c6\r\ncore 0: 0x80000104 (0x002b5b13) srli s6, s6, 2\r\ncore 0: 3 0x80000104 (0x002b5b13) x22 0x200025b1\r\ncore 0: 0x80000108 (0x3b3b1073) csrw pmpaddr3, s6\r\ncore 0: 3 0x80000108 (0x3b3b1073) c947_pmpaddr3 0x200025b1\r\ncore 0: 0x8000010c (0x8f8f9b37) lui s6, 0x8f8f9\r\ncore 0: 3 0x8000010c (0x8f8f9b37) x22 0x8f8f9000\r\ncore 0: 0x80000110 (0xf8fb0b13) addi s6, s6, -113\r\ncore 0: 3 0x80000110 (0xf8fb0b13) x22 0x8f8f8f8f\r\ncore 0: 0x80000114 (0x3a0b1073) csrw pmpcfg0, s6\r\ncore 0: 3 0x80000114 (0x3a0b1073) c928_pmpcfg0 0x8f8f8f8f\r\ncore 0: exception trap_instruction_access_fault, epc 0x80000118\r\ncore 0: tval 0x80000118\r\n```\r\n\r\n## Expected Behavior\r\n\r\nNot sure if it's a bug in Spike, Ibex or the cosimulation environment\r\n\r\n## Steps to reproduce the issue\r\n\r\nUsing the following commands from the root of the ibex repo:\r\n```console\r\ncd dv/uvm/core_ibex\r\nmake -j7 --keep-going IBEX_CONFIG=opentitan ITERATIONS=1 SEED=14822 TEST=riscv_epmp_mml_read_only_test WAVES=0 COV=0\r\n```\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nUsing Spike version ibex_cosim on commit: 9af9730baf7b956c3072c1b436d867aca5ef8f4c\r\n\r\n**Operating system:**\r\n\r\nUbuntu Linux 20.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\nCurrently running inside this PR: https://github.com/lowRISC/ibex/pull/1695\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1718, "state": "closed", "title": "[dv] Allow generic use of ecall", "body": "As I understand it RISC-V DV uses `ecall` to the signal the end of a test. The issue with this is we can't have arbitrary `ecall` executions within a generated test.\r\n\r\nWe should use another mechanism to trigger test end (maybe a write to a specific memory location?) allowing use of `ecall` within the test program body.\r\n\r\nI've added this to the V2 milestone as I think we'll need to to close some of the coverage holes (specifically single stepping over an `ecall`).\r\n\r\nDepending on how complex it ends up being we could consider waiving the need for this for V2 or do some limited fix that allows us to close the coverage without altering the end of test signalling too radically.\r\n\r\n> estimate 8\r\n> remaining 2022-08-08 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1701, "state": "closed", "title": "[dv, fcov] Debug related coverage holes", "body": "@hcallahan-lowrisc assigned to all of these \r\n\r\nThe following debug related coverpoints are not yet being hit:\r\n\r\n- [ ] Some categories for single stepping over each instruction category - `cp_single_step_instr` - #1763 Orig Estimate 4. Remain 2022-07-28 2. Remain 4 2022-08-01. Remain 4 2022-08-03. Remain 1 2022-08-10. Remain 0 2022-10-06.\r\n - [x] `CSRAccess`\r\n - [ ] `EBreakDbg`\r\n - [x] `EBreakExc`\r\n - [x] `ECall`\r\n - [x] `MRet`\r\n - [x] `DRet` - Illegal bin?\r\n - [x] `WFI`\r\n - [x] `Fence`\r\n - [x] `FenceI`\r\n - [x] `FetchError`\r\n - [x] `CompressedIllegal`\r\n - [x] `UncompressedIllegal`\r\n - [x] `CSRIllegal`\r\n - [x] `PrivIllegal`\r\n- [ ] Hardware breakpoint triggered - `cp_insn_trigger_enter_debug` - #1801 Orig Estimate 8. Remain 2022-08-16 4. Remain 2022-08-26 1.\r\n- [ ] Hardware breakpoint on instruction that causes an exception `cp_insn_trigger_exception` - #1801 Orig Estimate 8. Remain 2022-08-16 4. Remain 2022-08-26 1.\r\n\r\nNote for some of the single step instruction categories it's possible we simply cannot trigger the coverpoint for those. However from an initial look I think it should be possible for all of them (other than `None`) \r\n\r\nOriginal HW/PM estimate 20\r\n> estimate 30\r\n> remaining 2022-07-27 16\r\n> remaining 2022-08-01 18\r\n> remaining 2022-08-03 18\r\n> remaining 2022-08-10 15\r\n> remaining 2022-08-16 9\r\n> remaining 2022-08-23 5\r\n> remaining 2022-08-26 3\r\n> remaining 2022-10-06 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1697, "state": "closed", "title": "[dv,fcov] Implement \"Memory Fetch Error\" coverage point", "body": "I believe this ( [unaligned memory access](https://github.com/lowRISC/ibex/blob/master/doc/03_reference/coverage_plan.rst#exceptionsinterruptsdebug) ) is the sole remaining coverpoint to implement, rather similar to `misaligned_lsu_access_cross` but instead of PMP errors we're looking at memory fetch errors.\r\n\r\n_Originally posted by @GregAC in https://github.com/lowRISC/ibex/pull/1696#discussion_r916957719_"}
+{"org": "lowRISC", "repo": "ibex", "number": 1692, "state": "closed", "title": "[dv,cosim] Scoreboard expects 0 for some register writes", "body": "\r\n\r\n## Observed Behavior\r\n\r\n`risv_perf_counter_test` fails with every seed. For one example see below:\r\n```\r\n @ 124850: uvm_test_top.env.cosim_agent.scoreboard [ibex_cosim_agent_pkg::ibex_cosim_scoreboard.run_cosim_rvfi] Cosim mismatch Register write data mismatch to x14 DUT: 3b1 expected: 0\r\n```\r\n\r\nFor `riscv_debug_branch_jump_test` we see this error in some of the seeds, please see the error message below:\r\n```\r\n@ 9203330: uvm_test_top.env.cosim_agent.scoreboard [ibex_cosim_agent_pkg::ibex_cosim_scoreboard.run_cosim_rvfi] Cosim mismatch Register write data mismatch to x24 DUT: 17f35 expected: 0\r\n```\r\n## Expected Behavior\r\n\r\nI think either cosim misses the `wdata` for some reason or our writes to the registers happen in the hardware level (rather than in the software level so cosim couldn't model it. This is a completely wild guess, might make no sense at all! Definitely needs more investigating.\r\n## Steps to reproduce the issue\r\n\r\nPlease run this command to see both of the failing tests in one go.\r\n`make -C dv/uvm/core_ibex TEST=riscv_perf_counter_test,riscv_debug_branch_jump_test ITERATIONS=1 SIMULATOR=xlm -j2 SEED=22630`\r\n\r\n> estimate 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1691, "state": "closed", "title": "[dv] riscv_dret_test fails privilege mode check", "body": "\r\n\r\n## Observed Behavior\r\n\r\nUVM fail with the error message below: \r\n\r\n`Check failed dut_vif.dut_cb.priv_mode == mode (0 [0x0] vs 3 [0x3]) Incorrect privilege mode`\r\n\r\n## Expected Behavior\r\n\r\nI think this happened because `dret` actually changes our privilege level and if our privilege level is `U` before entering debug, we'll set the privilege as so after receiving `dret`. So I believe the problem comes from us using `check_illegal_insn` task after we have a `dret`.\r\n## Steps to reproduce the issue\r\n\r\nRun this command while at the repository top.\r\n``` make -C dv/uvm/core_ibex TEST=riscv_dret_test ITERATIONS=1 SIMULATOR=xlm -j2 SEED=22633 ```\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1688, "state": "closed", "title": "Commenting UVM testbench code, tidy formatting, minor refactoring", "body": "- Adds comments for explanations of test and library functionality\r\n- Refactor types and naming of control knob signals for clarity\r\n- Move constraints from MEMBER to CLASS for more flexibility\r\n- Add missing license header"}
+{"org": "lowRISC", "repo": "ibex", "number": 1687, "state": "closed", "title": "[dv, cosim] Add support for exceptions on first instruction of interrupt", "body": "When an interrupt occurs that causes an exception on it's first instruction co-sim break. This is a missing feature that needs implementing, see the TODO here\r\n\r\nhttps://github.com/lowRISC/ibex/blob/5c49fad9a236351a884f55d44248e4f9a0f7c7e5/dv/cosim/spike_cosim.cc#L145\r\n\r\n> estimate 8\r\n> remaining 2022-07-26 0"}
+{"org": "lowRISC", "repo": "ibex", "number": 1663, "state": "closed", "title": "riscv_csr_test fails because we don't model MCAUSE properly", "body": "*Copying from https://github.com/lowRISC/ibex/issues/1658#issuecomment-1129412757 (a silly place for me to have put this text in the first place)*\r\n\r\nRunning the `riscv_csr_test` with\r\n```\r\nmake -j4 ITERATIONS=1 SEED=1 TEST=riscv_csr_test VERBOSE=1 SIMULATOR=xlm WAVES=1\r\n```\r\nfails. It turns out that this is in the self-checking part, where we're writing and then reading back the MCAUSE register. The problem is that we describe the `mcause` CSR to riscv-dv with the following hunk of YAML:\r\n```\r\n# MCAUSE\r\n- csr: mcause\r\n description: >\r\n Indicates trap cause\r\n address: 0x342\r\n privilege_mode: M\r\n rv32:\r\n - field_name: Interrupt\r\n description: >\r\n Indicates if trap caused by interrupt\r\n type: WARL\r\n reset_val: 0\r\n msb: 31\r\n lsb: 31\r\n - field_name: Exception Code\r\n type: WLRL\r\n reset_val: 0\r\n msb: 4\r\n lsb: 0\r\n```\r\n\r\nThis might have been right once, but is no longer correct since Greg implemented internal interrupts. I don't think that `gen_csr_test.py` supports the behaviour that we've got for our MCAUSE field, which boils down to this code in `ibex_cs_registers.sv`:\r\n```systemverilog\r\n // mcause: exception cause\r\n CSR_MCAUSE: csr_rdata_int = {mcause_q.irq_ext | mcause_q.irq_int,\r\n mcause_q.irq_int ? {26{1'b1}} : 26'b0,\r\n mcause_q.lower_cause[4:0]};\r\n```\r\n\r\nHere, we ostensibly have a 31-bit exception code field, but the top bits are all constrained to be equal.\r\n\r\n@GregAC: What do you think we should do? A lame response might be to just use 6 bits and represent internal interrupts starting at 32, without the bit extension. Or we could split the field and just set the top bit? Or we could do some work to generalise the DV code to understand this sort of thing: for example, we could say that the field is 6 bits but the other 25 bits are some sort of mirror. But that means some DV work and (eek) getting a patch into riscv-dv.\r\n\r\nMy preference is probably to just set the top bit, so it ends up looking like this:\r\n```systemverilog\r\n // mcause: exception cause\r\n CSR_MCAUSE: csr_rdata_int = {mcause_q.irq_ext | mcause_q.irq_int,\r\n mcause_q.irq_int,\r\n 25'b0,\r\n mcause_q.lower_cause[4:0]};\r\n```\r\n\r\n> estimate 4\r\n> remaining 2022-07-22 3\r\n> remaining 2022-07-27 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1654, "state": "closed", "title": "[dv] Add instructions to enable/disable data independent timing to RISC-V DV generated code", "body": "Our DV environment never enables data independent timing or random instruction generation. These are controlled the CPUCTRL CSR, We should emit some instructions that toggle it.\r\n\r\nWhilst strictly security related features they impacts the basic functionality of the pipeline so we should have some basic testing of them in V2. Consideration on any specific scenarios and coverpoints for this feature can be dealt with in V2S.\r\n\r\n> estimate 4\r\n> remaining 2022-09-09 2\r\n> remaining 2022-10-25 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1649, "state": "closed", "title": "[dv] Add functional coverage points for icache", "body": "old estimate: 16 (Now I've done some work I can see it's a simpler task)\r\n> estimate 8\r\n> remaining 2022-10-21 4\r\n> remaining 2022-11-11 1"}
+{"org": "lowRISC", "repo": "ibex", "number": 1645, "state": "closed", "title": "Simple system VCS simulation fails with multiple errors", "body": "\r\n\r\n\r\nI want to simulate the simple system example using VCS, the build passes without any issue, but when I run the simulation, I get multiple errors caused by failed assertion\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nVCS S-2021.09-SP1_Full64\r\n**Operating system:**\r\nRed Hat Enterprise Linux release 8.5 \r\n\r\n**Version of the Ibex source code:**\r\n master branch hash : 668856441a73ebd067c09fdd2432241a32b8f03d\r\n\r\n**first part of the long errors list**\r\n\r\nChronologic VCS simulator copyright 1991-2021\r\nContains Synopsys proprietary information.\r\nCompiler version S-2021.09-SP1_Full64; Runtime version S-2021.09-SP1_Full64; May 2 13:47 2022\r\nInitializing memory ibex_simple_system.u_ram.u_ram.gen_generic.u_impl_generic.unnamed$$_2.gen_meminit from file './examples/sw/simple_system/hello_test/hello_test.vmem'.\r\n\"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 982: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX: started at 18s failed at 18s\r\n\tOffending '(!$isunknown(instr_req_o))'\r\nError: \"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 982: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX: at time 18\r\n18: (../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv:982) [ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX] [ASSERT FAILED] IbexInstrReqX\r\n\"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 983: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqPayloadXKnownEnable: started at 18s failed at 18s\r\n\tOffending '(!$isunknown(instr_req_o))'\r\nError: \"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 983: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqPayloadXKnownEnable: at time 18\r\n18: (../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv:983) [ibex_simple_system.u_top.u_ibex_top.IbexInstrReqPayloadXKnownEnable] [ASSERT FAILED] IbexInstrReqPayloadXKnownEnable\r\n\"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 1002: ibex_simple_system.u_top.u_ibex_top.IbexInstrGntX: started at 18s failed at 18s\r\n\tOffending '(!$isunknown(instr_gnt_i))'\r\nError: \"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 1002: ibex_simple_system.u_top.u_ibex_top.IbexInstrGntX: at time 18\r\n18: (../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv:1002) [ibex_simple_system.u_top.u_ibex_top.IbexInstrGntX] [ASSERT FAILED] IbexInstrGntX\r\n\"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 982: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX: started at 20s failed at 20s\r\n\tOffending '(!$isunknown(instr_req_o))'\r\nError: \"../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv\", 982: ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX: at time 20\r\n20: (../src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_top.sv:982) [ibex_simple_system.u_top.u_ibex_top.IbexInstrReqX] [ASSERT FAILED] IbexInstrReqX\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1613, "state": "closed", "title": "Xcelium cosim support", "body": "This builds on the earlier work in #1575 to get closer to running a cosimulation workflow for core-ibex dv by default.\r\n\r\nThis PR enables both VCS and Xcelium to run with the cosimualation workflow using COSIM=1 and SIMULATOR=xlm/vcs.\r\nHowever, the ISS is still setup to run standalone and the output test success critera is based upon the existing comparison mechanisms. Switching over to the cosim workflow by default is left for a later task.\r\n\r\nThis depends upon using a recent version of spike where pkg-config is supported. "}
+{"org": "lowRISC", "repo": "ibex", "number": 1587, "state": "closed", "title": "changing MEM_SIZE does not affect BRAM utilization ", "body": "I wanted to check if 2 KB memory works with IBEX ARTY A7 example. The default is 64 KB with FPGAPowerAnalysis option set to '0' and 256 KB otherwise.\r\n\r\nI changed top_artya7.sv file such as:\r\n// parameter int MEM_SIZE = FPGAPowerAnalysis == 0 ? 64 * 1024 : 256 * 1024;\r\n parameter int MEM_SIZE = 2 * 1024; // use 2 KB RAM for instr & data\r\n\r\nI checked both synthesis results for 64 KB and 2 KB, somehow BRAM utilization numbers are the same: 16\r\n\r\nI checked synth reports (top_artya7.vds) and synth utilization reports (top_artya7_utilization_synth.rpt) and be sure that the parameters related to memory are really consistent according to my changes: \r\n\r\nThe log for 2 KB synth from top_artya7.vds\r\n\r\nINFO: [Synth 8-6157] synthesizing module 'top_artya7' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_ibex_top_artya7_0.1/rtl/top_artya7.sv:5]\r\n Parameter FPGAPowerAnalysis bound to: 32'sb00000000000000000000000000000000\r\n Parameter MEM_SIZE bound to: 32'sb00000000000000000000100000000000\r\n Parameter MEM_START bound to: 0 - type: integer\r\n Parameter MEM_MASK bound to: 32'b00000000000000000000011111111111\r\n Parameter SRAMInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n\r\nINFO: [Synth 8-6157] synthesizing module 'ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_ibex_fpga_xilinx_shared_0/rtl/ram_2p.sv:11]\r\n Parameter Depth bound to: 32'sb00000000000000000000001000000000\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001001\r\nINFO: [Synth 8-6157] synthesizing module 'prim_ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_abstract_ram_2p_0/prim_ram_2p.sv:14]\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000000001000000000\r\n Parameter DataBitsPerMask bound to: 32'sb00000000000000000000000000000001\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001001\r\nINFO: [Synth 8-6157] synthesizing module 'prim_generic_ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_generic_ram_2p_0/rtl/prim_generic_ram_2p.sv:9]\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000000001000000000\r\n Parameter DataBitsPerMask bound to: 32'sb00000000000000000000000000000001\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001001\r\n Parameter MaskWidth bound to: 32'sb00000000000000000000000000100000\r\n\r\nThe log for 64 KB synth:\r\n\r\nINFO: [Synth 8-6157] synthesizing module 'top_artya7' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_ibex_top_artya7_0.1/rtl/top_artya7.sv:5]\r\n Parameter FPGAPowerAnalysis bound to: 32'sb00000000000000000000000000000000\r\n Parameter MEM_SIZE bound to: 32'sb00000000000000010000000000000000\r\n Parameter MEM_START bound to: 0 - type: integer\r\n Parameter MEM_MASK bound to: 32'b00000000000000001111111111111111\r\n Parameter SRAMInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n\r\nINFO: [Synth 8-6157] synthesizing module 'ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_ibex_fpga_xilinx_shared_0/rtl/ram_2p.sv:11]\r\n Parameter Depth bound to: 32'sb00000000000000000100000000000000\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001110\r\nINFO: [Synth 8-6157] synthesizing module 'prim_ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_abstract_ram_2p_0/prim_ram_2p.sv:14]\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000100000000000000\r\n Parameter DataBitsPerMask bound to: 32'sb00000000000000000000000000000001\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001110\r\nINFO: [Synth 8-6157] synthesizing module 'prim_generic_ram_2p' [/home/mbaykenar/ibex_mba/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_generic_ram_2p_0/rtl/prim_generic_ram_2p.sv:9]\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000100000000000000\r\n Parameter DataBitsPerMask bound to: 32'sb00000000000000000000000000000001\r\n Parameter MemInitFile bound to: ../../../../../examples/sw/led/led.vmem - type: string\r\n Parameter Aw bound to: 32'sb00000000000000000000000000001110\r\n Parameter MaskWidth bound to: 32'sb00000000000000000000000000100000\r\n\r\n\r\nI see that the parameters on prim_generic_ram_2p.sv are elaborated correctly:\r\n\r\n2 KB (32-bit * 512 = 2 KB)\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000000001000000000\r\n64 KB (32-bit * 16384 = 64 KB)\r\n Parameter Width bound to: 32'sb00000000000000000000000000100000\r\n Parameter Depth bound to: 32'sb00000000000000000100000000000000\r\n\r\nI also checked detailed module level utilization and found out that all the BRAM instances are utilized for ram_2p. The register file utilizes LUT RAMs.\r\n\r\nDo I miss a detail on synthesizing for 2 KB RAM or what can cause inferring same amount of BRAM for 64 KB and 2 KB ?\r\n\r\nRegards,\r\n\r\n## My Environment\r\n\r\n**EDA tool and version:**\r\nVIVADO 2020.2\r\n\r\n**Operating system:**\r\nUBUNTU 20.04\r\n\r\n**Version of the Ibex source code:**\r\n6bb67e20f8a7c670e4baf5fe8f130a5ef360f411\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1579, "state": "closed", "title": "[dv] Implement ePMP tests", "body": "RISC-DV only generates code to test normal PMP, this needs to be extended to stimulate ePMP functionality.\r\n\r\nOriginal estimate 8.\r\n2022-07-28 based on @marnovandermaas comment increasing estimate to accommodate time spent on issue\r\n> estimate 9\r\n> remaining 2022-07-22 8\r\n> remaining 2022-08-01 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1575, "state": "closed", "title": "Unconditionally enable cosim in simulations", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 1571, "state": "closed", "title": "Get core_ibex UVM tests working with Xcelium", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 1570, "state": "open", "title": "Teach auto-generated interrupt handlers to clear interrupts again", "body": "It would be nice if we could customise our (new) sequences that drive interrupts to drop the interrupts again only when they were acknowledged. (Ibex has level-, rather than edge-triggered interrupts)\r\n\r\nAt the moment, the ISRs that come out of riscv-dv write to a magic \"signature address\". We could either use that for this purpose or could use something else. But the latter case would mean a modification of the (moribund?) riscv-dv project.\r\n\r\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 1568, "state": "closed", "title": "[test] Add tests to mix up exceptions/interrupts/debug", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 1566, "state": "closed", "title": "Rip out all the non-cosim stuff from dv/uvm/core-ibex scripts", "body": "Depends on #1565 but, once we've got working \"cosim tooling\", we should get rid of the old way of doing things.\r\n\r\nThis doesn't include the work to rip out the old sequences for e.g. exceptions: we'll track that separately.\r\n\r\n> estimate 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1558, "state": "closed", "title": "[icache, dv] Added scrambling agent to verify scrambling in RAMs", "body": "This commit adds a new scrambling agent to drive scrambling key and valid to the data and tag memory interfaces."}
+{"org": "lowRISC", "repo": "ibex", "number": 1557, "state": "closed", "title": "yosys synthesis flow - Module `\\prim_buf' is not part of the design.", "body": "\r\n\r\n\r\nHi,\r\n\r\nI am trying to run the experimental Yosys/OpenSTA Ibex Synthesis flow according to the README instructions, but I get the following error during synthesis:\r\n\r\n```\r\n31.2.3. Executing AST frontend in derive mode using pre-parsed AST for module `\\ibex_core'.\r\nERROR: Module `\\prim_buf' referenced in module `\\ibex_top' in cell `\\u_rf_rdata_b_ecc_buf' is not part of the design.\r\n```\r\nWhen I look into the generated code in `syn_out`, I see that `ibex_top.v` does reference `prim_buf` multiple times, which is not defined in the generated verilog files.\r\n\r\nI am not sure how to solve this, maybe it's necessary to include the `prim_buf`rtl definition in the `sv2v` [call from line 47](https://github.com/lowRISC/ibex/blob/094451a9489d631895101a5de19a26cd4cf4fd7d/syn/syn_yosys.sh#L47) of `syn_yosys.sh`.\r\n\r\n## My Environment\r\n\r\n\r\n\r\nI am following the instruction from [syn/README.md](https://github.com/lowRISC/ibex/blob/master/syn/README.md).\r\n\r\n- Yosys 0.9 (git sha1 1979e0b) installed from apt\r\n- sv2v v0.0.9-0-gc822d2e binary from GitHub\r\n- OpenSTA installed from GitHub latest source code (git hash 3c3f8f61fde2dd28afec9eca81f5b361f22f0cc4)\r\n- OpenRoad-flow-scripts from latest GitHub version (git hash fbcfb64bc92d6543e5c6c5c7e4c485a7b7709198)\r\n\r\n**EDA tool and version:**\r\n\r\n\r\n**Operating system:**\r\n\r\n\r\n- Ubuntu 20.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\n- Ibex from `master` (git hash 094451a9489d631895101a5de19a26cd4cf4fd7d)\r\n\r\nI haven't made any changes to the source code."}
+{"org": "lowRISC", "repo": "ibex", "number": 1553, "state": "closed", "title": "alert_major_o output port must be removed from ibex_top.sv module in top_artya7.sv ", "body": "\r\n\r\n## Observed Behavior\r\n\r\n\r\n## Expected Behavior\r\n\r\n\r\n## Steps to reproduce the issue\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\n\r\n**Operating system:**\r\n\r\n\r\n**Version of the Ibex source code:**\r\n\r\nalert_major_o output port of ibex_top.sv module has to be removed as Vivado throws error when synthesizing top_artya7.sv module. This port is not defined in ibex_top.sv module used in FPGA example"}
+{"org": "lowRISC", "repo": "ibex", "number": 1526, "state": "closed", "title": "Consider adding srecord as an optional pre-requisite in examples/simple_system", "body": "\r\n\r\n## Observed Behavior\r\n\r\n\r\nI followed the instructions to build the software in `examples/symple_system` but I noticed that the `vmem` file wasn't generated.\r\n\r\nLooking into the logs of the `make -C <...>` command, I found the following error message:\r\n\r\n```\r\nsrec_cat hello_test.bin -binary -offset 0x0000 -byte-swap 4 -o hello_test.vmem -vmem \r\nmake: srec_cat: Command not found \r\n```\r\nI searched online and found that I needed to install `srecord`, after which the `vmem` file was successfully generated.\r\n\r\nI noticed that `srecord` is not listed in the [Prerequisites](https://github.com/lowRISC/ibex/tree/master/examples/simple_system#prerequisites) section of the README.md, where other needed libraries and software tools are specified.\r\n\r\n## Expected Behavior\r\n\r\n\r\nI would expect an extra line in the [Prerequisites](https://github.com/lowRISC/ibex/tree/master/examples/simple_system#prerequisites) section stating the following:\r\n\r\n> \\# Prerequisites\r\n> - <...>\r\n> - srecord. On Debian/Ubuntu, install it by running `apt-get install srecord`.\r\n\r\nOptionally, it could state is optional by saying something like this:\r\n\r\n> - srecord. On Debian/Ubuntu, install it by running `apt-get install srecord`. (Optional, needed for vmem generation)\r\n\r\n## Steps to reproduce the issue\r\n\r\n\r\nFollow the instructions for building a simple system in: https://github.com/lowRISC/ibex/tree/master/examples/simple_system\r\n\r\n## My Environment\r\n\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nlowrisc-toolchain-gcc-rv32imc-20210412-1\r\n\r\n**Operating system:**\r\n\r\nUbuntu 20.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\n69dfa6f8daf294c766a042c640a5830169e5b914"}
+{"org": "lowRISC", "repo": "ibex", "number": 1524, "state": "closed", "title": "[simple_system, sw] Add PMP example tests", "body": "# Introduction\r\n\r\nThese tests and support libraries have been ported from the OpenTitan repository.\r\n\r\nI have stripped some of the less relevant dependencies, with the exception of:\r\n- Bit manipulation API: makes the `pmp.{h,c}` a bit tidier, but also factoring it out would take some effort\r\n- CSR access helpers: same as above, however, can be factored out more easily (if required)\r\n\r\nThis PR is split into smaller logical commits, so should be relatively easy to review."}
+{"org": "lowRISC", "repo": "ibex", "number": 1517, "state": "closed", "title": "user manual - minor error in the rv32b description", "body": "\r\n\r\n## Observed Behavior\r\n\r\n\r\nIn the [User Manual, section Core Integration, subsection Parameters](https://ibex-core.readthedocs.io/en/latest/02_user/integration.html#parameters), the description for the RV32B parameter says the following:\r\n\r\n> “ibex_pkg::RV32Full”: All sub-extensions\r\n\r\nBut `RV32Full` is not defined in `ibex_pkg.sv`.\r\n\r\n```systemverilog\r\n typedef enum integer {\r\n RV32BNone = 0,\r\n RV32BBalanced = 1,\r\n RV32BOTEarlGrey = 2,\r\n RV32BFull = 3\r\n } rv32b_e;\r\n```\r\n\r\n## Expected Behavior\r\n\r\n\r\nThe table should say:\r\n\r\n> “ibex_pkg::RV32BFull”: All sub-extensions\r\n\r\n## Steps to reproduce the issue\r\n\r\n\r\nRead the manual in: https://ibex-core.readthedocs.io/en/latest/02_user/integration.html#parameters\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\n\r\n**Operating system:**\r\n\r\n\r\n**Version of the Ibex source code:**\r\n\r\n\r\nlatest"}
+{"org": "lowRISC", "repo": "ibex", "number": 1514, "state": "closed", "title": "Use plain memory primitives when ICache scrambling is disabled", "body": "The recent PR to add scrambling support to the ICache lacks an option to allow the use of non-scrambled RAMs. Scrambling is only of interest to applications requiring security hardening, other applications may simply want an ICache without scrambled memories."}
+{"org": "lowRISC", "repo": "ibex", "number": 1500, "state": "closed", "title": "Building Arty A7 A35-T example", "body": "\r\n\r\n\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\nXilinx Vivado 2019.2 (64-bit)\r\n\r\n\r\n**Operating system:**\r\nArch linux\r\n\r\n\r\n**Version of the Ibex source code:**\r\n410ffd349da1d4c13f77b208bb3b93adb154fac0 - no changes to the code\r\n\r\n\r\nI've tried to build Arty A7 example for A35-T using current master, but it looks like there aren't enough resources available on the board. Run command:\r\n```\r\nfusesoc --cores-root=. run --build --tool vivado --target=synth lowrisc:ibex:top_artya7 --part xc7a35ticsg324-1L --SRAMInitFile=`pwd`/../led.vmem\r\n```\r\nVivado error message:\r\n```\r\nERROR: [DRC UTLZ-1] Resource utilization: RAMB18 and RAMB36/FIFO over-utilized in Top Level Design (This design requires more RAMB18 and RAMB36/FIFO cells than are available in the target device. This design requires 128 of such cell types but only 100 compatible sites are availabl\r\ne in the target device. Please analyze your synthesis results and constraints to ensure the design is mapped to Xilinx primitives as expected. If so, please consider targeting a larger device.)\r\nERROR: [DRC UTLZ-1] Resource utilization: RAMB36/FIFO over-utilized in Top Level Design (This design requires more RAMB36/FIFO cells than are available in the target device. This design requires 64 of such cell types but only 50 compatible sites are available in the target device. \r\nPlease analyze your synthesis results and constraints to ensure the design is mapped to Xilinx primitives as expected. If so, please consider targeting a larger device.)\r\nERROR: [DRC UTLZ-1] Resource utilization: RAMB36E1 over-utilized in Top Level Design (This design requires more RAMB36E1 cells than are available in the target device. This design requires 64 of such cell types but only 50 compatible sites are available in the target device. Please\r\n analyze your synthesis results and constraints to ensure the design is mapped to Xilinx primitives as expected. If so, please consider targeting a larger device.)\r\n``` \r\nTargeting A100-T generates bitstream, but description of the ``top_artya7.core`` file suggests it should also support A35-T: https://github.com/lowRISC/ibex/blob/master/examples/fpga/artya7/top_artya7.core#L6.\r\n\r\nDoes A35-T is still supported?\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1485, "state": "closed", "title": "Wrong SV code - compilation error occurs", "body": "\r\n\r\n## Observed Behavior\r\n\r\nAfter https://github.com/lowRISC/ibex/commit/169785d0711335c94561a93146e069766eec138c commit the \"ibex_simple_system\" and UVM tests cannot be compiled because of the error:\r\n\r\n`ALOG: Error: VCP2675 /ibex/build/lowrisc_ibex_ibex_simple_system_0/src/lowrisc_ibex_ibex_top_0.1/rtl/ibex_register_file_fpga.sv : (63, 1): Cannot write to a variable 'mem[k]' that is also driven by an always_comb/always_latch/always_ff procedural block. `\r\n\r\n\r\nThe problem is caused by wrong SV code:\r\nhttps://github.com/lowRISC/ibex/blob/c78acac8cc381293900f3648e365ddd136784789/rtl/ibex_register_file_fpga.sv#L54-L65\r\n\r\nIn this case the mem[] variable is written in always_ff and initial block what is prohibited by SV LRM:\r\n\r\n> \"The always_ff procedure imposes the restriction that it contains one and only one event control and no\r\n> blocking timing controls. Variables on the left-hand side of assignments within an always_ff procedure,\r\n> including variables from the contents of a called function, shall not be written to by any other process.\"\r\n\r\n## Expected Behavior\r\n\r\n\r\nThe code should compile without errors.\r\n\r\n## Steps to reproduce the issue\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nAldec Riviera-PRO\r\n\r\n**Operating system:**\r\n\r\nLinux, Ubuntu 20.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1478, "state": "closed", "title": "[icache,dv] Inserting Memory Bit Flips Inside Scrambled Memory Causes ECC Test Failures", "body": "The way we test ECC inside ICache causes faulty bits (one or two) inside the scrambled RAMs. However, scrambled RAMs get unscrambled and then sent inside ICache to do the ECC checking. When we unscramble, it might propagate the faulty bits in a way that we might end up inserting 4+ faulty bits to the original memory. Thus, cause ECC to not catch the faulty situation and generate a false negative.\r\n\r\nA proper DV work should include fixing this bit insertion scheme so that we would not see 4+ bits change between original memory content and unscrambled memory when trying to insert bad bits.\r\n\r\nIn OTBN, we are also using scrambled memories and in there we are first unscrambling the memory, changing the content and scrambling it back to put inside the memory. In order to do that, we need to use the functions from sram_scrambling_pkg and change the cache memory so that it will be suitable to read/write using the keys."}
+{"org": "lowRISC", "repo": "ibex", "number": 1476, "state": "closed", "title": "[bitmanip] Re-align bitmanip implementation with v.1.0.0 and v.0.93 of the specs - Part 1", "body": "This PR contains the first chunk of work to re-align the bitmanip implementation inside Ibex with the ratified v.1.0.0 spec (covering Zba, Zbb, Zbc, and Zbs only) and draft version v.0.93 (covering also Zbe, Zbf, Zbp, Zbr). In particular, this PR takes care of aligning the ratified sub-extensions Zba, Zbb, Zbc and Zbs. The changes were successfully tested using RISCV-DV. However, to keep verifying this in CI and hence before merging this PR a couple of other things need to happen. For details, see #1470."}
+{"org": "lowRISC", "repo": "ibex", "number": 1472, "state": "closed", "title": "[bug, dbg] Don't cache instruction whilst in debug mode", "body": "The debug module used in conjunction with Ibex implements its functionality by having Ibex execute code that dynamically changes depending upon the commands issued to it. When the icache is present caching the memory region used for this will break the debug module.\r\n\r\nA simple fix is to disable instruction caching whilst Ibex is in debug mode.\r\n\r\n> estimate 2"}
+{"org": "lowRISC", "repo": "ibex", "number": 1471, "state": "closed", "title": "[bug] PMP checking incorrect with icache", "body": "Since the PMP checking in Ibex is performed on external requests, any changes to PMP registers or changes between U and M mode will render the icache contents out of date. The checking cannot easily be moved after the icache as the address can be misaligned at that point due to compressed instructions.\r\nThe following solutions are proposed:\r\n1. Flush the icache (and all buffered instructions) any time a PMP register is written (which should be rare).\r\n2. Store the associated U/M mode status with each cache line so that the icache does not need to be flushed on every mode change (which happens on interrupts and so is more frequent)"}
+{"org": "lowRISC", "repo": "ibex", "number": 1470, "state": "closed", "title": "[tracking] Align bitmanip implementation with latest version of the spec", "body": "Currently, Ibex optionally implements draft version 0.92 of the RISC-V Bitmanip spec. We want to re-align the implementation with the updated specification v.1.0.0 (Zba, Zbb, Zbc, Zbs sub extensions) and draft version 0.93 (Zbf, Zbt, Zbe, Zbp, Zbr sub extensions). To this end, the following tasks need to be done:\r\n\r\n- [x] Zba: implementation, see #1422\r\n- [x] Zbb: see #1476 \r\n - [x] Move slo[i] and sro[i] instructions to Zbp (0.93).\r\n - [x] Remove rev. This instruction isn’t part of Zbb anymore. It’s part of grev[i] which is included in Zbp (Ibex “Full” only). The rev8 instruction remains part of Zbb.\r\n - [x] Rename pcnt to cpop.\r\n - [x] Move sext.[bh] from Zb_temp to Zbb (classification was ambiguous in 0.92)\r\n- [x] Zbs: Rename sb* instructions (sbset[i], sbclr[i], sbinv[i], sbext[i]) to b*, see #1476\r\n- [x] Zbe: Rename bext/bdep to bcompress/bdecompress (technically only 0.94, but needed as in 0.93 there exist two different instructions named bext otherwise), see #1476 \r\n- [x] Zbp: Implement xperm.[nbh], see #1483\r\n- [x] Add a new config to enable everything except for Zbe, see #1493 \r\n\r\n- [x] Verification/RISCV-DV:\r\n - [x] Merge PR adding support for v.1.0.0, see google/riscv-dv#832\r\n - [x] Enable support for both v.1.0.0 and v.0.93 at the same time, currently exclusive (only sub-extensions not part of v.1.0.0), see see google/riscv-dv#834\r\n - [x] Update Spike version, the [one modified by Greg for the cosim framework](https://github.com/lowRISC/riscv-isa-sim/tree/ibex_cosim) is working (at least for v.1.0.0), #1530\r\n - [x] Re-enable bitmanip tests #1532\r\n- [x] GCC/LLVM compiler toolchains: #1529\r\n - [x] [GCC 10.2.0 with RVB support](https://github.com/riscv-collab/riscv-gcc/tree/riscv-gcc-10.2.0-rvb) works for v.1.0.0, not sure about v.0.93 in that GCC version\r\n - [x] [Latest RISC-V binutils](https://github.com/riscv-collab/riscv-binutils-gdb/commit/b69c9d41e89498442cb5af5287f378b3583dd445) works for v.1.0.0, not sure about v.0.93 with that version of binutils\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1462, "state": "closed", "title": "[Bug] Branch prediction on predicted branches causes bad behaviour", "body": "\r\n\r\n## Steps to reproduce the issue\r\n\r\nConsider the following code:\r\n```\r\nint main(int argc, char **argv) {\r\n static int x = 25;\r\n int* x_addr = (int*)&x;\r\n __asm__ (\r\n \"j skip\\n\\t\"\r\n\r\n \"predict_to_here:\\n\\t\" // we shouldn't branch here but even if we do, just finish\r\n \"j finish\\n\\t\"\r\n \"wfi\\n\\t\" // this will kill things if hit\r\n\r\n \"skip:\\n\\t\"\r\n \"lw t0, 0(%0)\\n\\t\"\r\n \"beqz t0, predict_to_here\\n\\t\" // clearly this branch is not meant to be taken but is predicted taken\r\n \"j finish\\n\\t\"\r\n\r\n \"finish:\\n\\t\"\r\n \"nop\\n\\t\"\r\n :\r\n :\"r\" (x_addr)\r\n : \"t0\"\r\n );\r\n return 0;\r\n\r\n}\r\n```\r\nWe would expect the following branch pattern in general: `-> skip -> finish`\r\nBuilding ibex_simple_system with the following parameters works correctly:\r\n`fusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system --RV32E=0 --RV32M=ibex_pkg::RV32MFast --BranchTargetALU=1 --WritebackStage=1 --BranchPredictor=0`\r\n\r\nBuilding with these parameters causes the core to seemingly \"lock up\":\r\n`fusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system --RV32E=0 --RV32M=ibex_pkg::RV32MFast --BranchTargetALU=1 --WritebackStage=1 --BranchPredictor=1`\r\n\r\n## Observed Behavior\r\n\r\nIbex overrides `branch_mispredict_addr` by predicting on a predicted branch. This means when a mispredict fires on `beqz t0, predict_to_here` the PC fetched next is at `wfi`.\r\n\r\n[waves.zip](https://github.com/lowRISC/ibex/files/7384667/waves.zip)\r\n\r\n## Expected Behavior\r\n\r\nI honestly don't know. In the prefetch buffer configuration, there is only one `branch_mispredict_addr_q` present so there is no practical way to nest branch predictions as far as I can tell. It seems like branches should just be predicted not taken when we are already on a predicted path.\r\n\r\n## My Environment\r\n\r\n\r\n**Compiler:**\r\nriscv64-unknown-elf-gcc (GCC) 8.2.0\r\n\r\n**EDA tool and version:**\r\n\r\nVerilator 4.210 2021-07-07 rev v4.210\r\n\r\n**Operating system:**\r\n\r\nUbuntu 21.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\ncfeef7e864926cf4d30e271a3e2aa5d95e0c141f"}
+{"org": "lowRISC", "repo": "ibex", "number": 1457, "state": "closed", "title": "Use of blocking assignment within `always_ff` block.", "body": "Here, inside an `always_ff` block, there is some blocking assignment `f_addr_valid = 1'b1;` that looks like it should be non-blocking\r\n\r\nhttps://github.com/lowRISC/ibex/blob/master/formal/icache/formal_tb.sv#L112-L117\r\n\r\nFound by the verible [`always-ff-non-blocking`]( https://chipsalliance.github.io/verible/lint.html#always-ff-non-blocking) rule:\r\n```\r\nverible-verilog-lint formal/icache/formal_tb.sv\r\nformal/icache/formal_tb.sv:114:9: Use blocking assignments, at most, for locals inside 'always_ff' sequential blocks. [Style: sequential-logic] [always-ff-non-blocking]\r\nformal/icache/formal_tb.sv:116:9: Use blocking assignments, at most, for locals inside 'always_ff' sequential blocks. [Style: sequential-logic] [always-ff-non-blocking]\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1448, "state": "closed", "title": "Update lowrisc_ip to lowRISC/opentitan@ad629e3e6", "body": "(This pulls in a fix for the annoying \"unknown item: Formal\" messages: see https://github.com/lowRISC/ibex/issues/1445)\r\n\r\nUpdate code from upstream repository\r\nhttps://github.com/lowRISC/opentitan to revision\r\nad629e3e6e70c5eaa3c2dd68457b0a020448b35f\r\n\r\n* [dvsim] Introduce {self_dir} as variable (Philipp Wagner)\r\n* [dvsim] Small cleanups (Philipp Wagner)\r\n* [prim_lfsr] Minor lint fix (Michael Schaffner)\r\n* [dv] Update sec_cm testplan (Weicai Yang)\r\n* [prim/lint] Move waiver to correct waiver file (Michael Schaffner)\r\n* [prim_assert] Relocate waivers to dedicated prim_assert.waiver file\r\n (Michael Schaffner)\r\n* [alert_handler] Lint fixes and waiver updates (Michael Schaffner)\r\n* [prim_lc_receiver] Add parameter to select reset value (Michael\r\n Schaffner)\r\n* [lint] Add lint waiver for IP regfiles with shadow resets (Michael\r\n Schaffner)\r\n* [fpv] Fix Verible lint errors (Philipp Wagner)\r\n* [prim_lfsr] Minor lint fixes (Timothy Chen)\r\n* [clkmgr] Fix measurement control CDC (Timothy Chen)\r\n* [fpv/prim_counter] Pad one bit to include overflow case (Cindy Chen)\r\n* [fpv] Fix issue lowRISC#8371 (Zeeshan Rafique)\r\n* [flash_ctrl] Flash ctrl security hardening (Timothy Chen)\r\n* [dv] Fix CI error (Cindy Chen)\r\n* [prim_alert_*] Extend SVAs for FPV (Michael Schaffner)\r\n* [prim_alert_*] Update DV TB to respect initialization timing\r\n (Michael Schaffner)\r\n* [prim_alert_rxtx_fpv] Update FPV environment and fix SVAs (Michael\r\n Schaffner)\r\n* [prim_alert_sender] Update sender to support in-band reset mechanism\r\n (Michael Schaffner)\r\n* [prim_alert_sender] Simplify sender and clear ping req upon sigint\r\n (Michael Schaffner)\r\n* [prim_lc_sender] Add option to select reset value (Michael\r\n Schaffner)\r\n* [prim] Correct assertion valid term (Timothy Chen)\r\n* [prim_lc_combine] Align behavior of lc combine with mubi functions\r\n (Michael Schaffner)\r\n* [fpv/tool] Support GUI mode on dvsim (Cindy Chen)\r\n* [prim_lfsr] Further permutation refinements for SBox layer (Michael\r\n Schaffner)\r\n* [dv/shadow_reg] Shadow register write by field (Cindy Chen)\r\n* [prim] Fix the edge type (Eunchan Kim)\r\n* [checklist] Updates to checklist for D2 status (Tom Roberts)\r\n* [prim_mubi_pkg] Add a generic multibit type and associated functions\r\n (Michael Schaffner)\r\n* [prim] Minor fix and clarification to prim_count (Timothy Chen)\r\n* [keymgr/dv] Update testplan and covergroup plan (Weicai Yang)\r\n* [prim_lc_combine] Fix parameterization error (Michael Schaffner)\r\n* [fpv/prim_count] Small update on prim_count assertions (Cindy Chen)\r\n* [dv] Add ip_name in reg_block (Weicai Yang)\r\n* [keymgr] Finalize keymgr hardening (Timothy Chen)\r\n* [prim_lc_combine] Add a prim to compute logical AND/OR for LC\r\n signals (Michael Schaffner)\r\n* [dv] Remove common_cov_excl.el from unr.cfg (Weicai Yang)\r\n* [dv/top_level] Loop through the SW test multiple times (Cindy Chen)\r\n* [flash_ctrl] Various clean-up and updates (Timothy Chen)\r\n* [prim] Change prim_reg_cdc assertions (Timothy Chen)\r\n* [prim, keymgr] Migrate keymgr_cnt to prim_count (Timothy Chen)\r\n* [sw dv] Multi-site support for Verilator (Martin Lueker-Boden)\r\n* [dv/csr] Update write exclusion wdata value (Cindy Chen)\r\n* [dv/dv_base_reg] remove debug display (Cindy Chen)\r\n* [dv/shadow_reg] Fix alert shadow_reg regression error (Cindy Chen)\r\n* [top] Integrate ast into fpga (Timothy Chen)\r\n* [prim_lfsr] Improve statistics of non-linear output (Michael\r\n Schaffner)\r\n* [prim_esc_receiver] Fix response toggling corner case (Michael\r\n Schaffner)\r\n* option to use partner ast_pkg (Sharon Topaz)\r\n* [dv/prim_esc] Double the ping timeout cycles (Cindy Chen)\r\n* [dv] Use sed to add -elfile for each excl file (Weicai Yang)\r\n* [dv] Fix coverage report error (Weicai Yang)\r\n* [dv] Update common exclusion file (Weicai Yang)\r\n* [dv/prim_esc] Improve FSM coverage (Cindy Chen)\r\n* [reggen] Add a check to limit the swaccess type for shadow regs\r\n (Michael Schaffner)\r\n* [prim_subreg_shadow] Fix for W1S/W0C corner case (Michael Schaffner)\r\n* [prim_subreg_shadow] Disallow phase updates when storage err is\r\n present (Michael Schaffner)\r\n* [dvsim] Add passing count by milestone in reports (Srikrishna Iyer)\r\n* [dv/tool] Include toggle coverage for prim_alert_sender in\r\n cover_reg_top (Cindy Chen)\r\n* [clkmgr] Harden clock manager through frequency measurements\r\n (Timothy Chen)\r\n* [dv] Only enable VCS -kdb when dumping waves (Weicai Yang)\r\n* [dv] Fix shadow reg (Weicai Yang)\r\n* [dvsim] Allow non-integral values of --reseed-multiplier (Rupert\r\n Swarbrick)\r\n* [ast] Fixes for various ast issues (Timothy Chen)\r\n* [prim_esc_receiver] Assert escalation in case of sigint error\r\n (Michael Schaffner)\r\n* [prim_esc_receiver] Minor signal renaming for consistency (Michael\r\n Schaffner)\r\n* [dv/alert_handler] Support shadow register sequence (Cindy Chen)\r\n* [verilator] Use FileSz rather than MemSz when flattening ELF files\r\n (Michael Munday)\r\n* [prim_subreg_shadow] Only assert QE when committed_reg is written\r\n (Michael Schaffner)\r\n* [dv,verilator] Round up SV_MEM_WIDTH_BYTES to a multiple of 4\r\n (Rupert Swarbrick)\r\n* [prim] Add missing include (Pirmin Vogel)\r\n* [dv/cover_cfg] Exclude prim_alert/esc from xcelium (Cindy Chen)\r\n* [dv/cover_cfg] Exclude prim_alert/esc pairs (Cindy Chen)\r\n* [clkmgr] Use local BUFHCE clock gates on FPGA (Pirmin Vogel)\r\n* [prim_prince] Mark \"leaf\" functions in prince_ref.h as static inline\r\n (Rupert Swarbrick)\r\n* [dv/shadow_reg] Check status after shadow_reg write (Cindy Chen)\r\n* [dv/shadwo_reg] Shadow reg common sequence update (Cindy Chen)\r\n* [otp_ctrl/lc_ctrl] Add 32bit OTP vendor test ctrl/status regs to LC\r\n TAP (Michael Schaffner)\r\n* [otp_ctrl] Add VENDOR_TEST partition (Michael Schaffner)\r\n* [prim] Edge Detector (Eunchan Kim)\r\n* [prim_diff_decode] Fix asynchronous assertions (Michael Schaffner)\r\n* [spi_device] Instantiate Upload module (Eunchan Kim)\r\n* [dv] Add sv_flist_gen_flags HJson var for FuseSoc (Srikrishna Iyer)\r\n* [dv, xcelium] Properly pass excl files to IMC (Srikrishna Iyer)\r\n* [reg] Fix shadow reg update during storage error (Timothy Chen)\r\n* [regfile] Refactor cdc handling to the reg level (Timothy Chen)\r\n* [dv/prim_esc] Add a testplan and increase coverage (Cindy Chen)\r\n* [dv] Update TLUL and EDN frequency (Weicai Yang)\r\n* [rstmgr, top] Add support for shadow resets (Timothy Chen)\r\n* [dv] Update Xcelium cover ccf (Srikrishna Iyer)\r\n* [dv] reduce seeds for CSR tests (Weicai Yang)\r\n* [usb/top] Remove AND gates on non-AON domain and rename 3.3V signal\r\n (Michael Schaffner)\r\n* [dv/prim_alert] Improvement on prim_alert tb (Cindy Chen)\r\n* [prim] FIFO SRAM Adapter fix (Eunchan Kim)\r\n* [prim] Add Write Mask port (Eunchan Kim)\r\n* [dv] Fix timescale issue with Xcelium (Weicai Yang)\r\n* [dv/prim_esc] Fix prim_esc regression error (Cindy Chen)\r\n* [dv/dv_base_reg] change from uvm_low to uvm_high (Cindy Chen)\r\n* [sram_ctrl] Harden initialization counter (Michael Schaffner)\r\n* [tools/uvmdvgen] Fix path in testplan inclusion (Guillermo Maturana)\r\n* [dv] Change stress_all_with_rand_reset to V3 (Weicai Yang)\r\n* [dv] fix tl error coverage (Weicai Yang)\r\n* [dv] Add macro DV_GET_ENUM_PLUSARG (Weicai Yang)\r\n* [prim] SRAM Async FIFO (Eunchan Kim)\r\n* [dv, xcelium] Fix statement coverage extraction (Srikrishna Iyer)\r\n* [dvsim] Minor fixes to coverage extraction (Srikrishna Iyer)\r\n* [prim_lfsr] Do not shadow |state| variable (Philipp Wagner)\r\n* [prim] Add non-linear out option to prim_lfsr (Timothy Chen)\r\n* [dv] Constrain TLUL to 24Mhz or higher (Weicai Yang)\r\n* [primgen] Instantiate tech libs in stable order (Philipp Wagner)\r\n* [primgen] Actually find the Verible Python wrapper (Philipp Wagner)\r\n* [dv/prim_esc] fix regression error (Cindy Chen)\r\n* [dv] Fix shadow reg predict (Weicai Yang)\r\n* [dv/common] Exclude assertion coverage from IP level testbench\r\n (Cindy Chen)\r\n* [dv/prince] hit additional toggle coverpoints (Udi Jonnalagadda)\r\n* [sram_ctrl] Update docs (Michael Schaffner)\r\n* [sram_ctrl] Absorb prim_ram_1p_scr (Michael Schaffner)\r\n* [dv/prim_alert/esc] Improvements for prim_alert/esc_tb (Cindy Chen)\r\n* [dv/dvsim] Add \"testfile\" grading option (Guillermo Maturana)\r\n* [dv/prim_esc] Direct test for prim_rx/tx (Cindy Chen)\r\n* [dv/utils] added 6MHz to clk_freq_mhz_e (Dror Kabely)\r\n* [prim_xor2/lint] Add waiver for .* use in generated prim (Michael\r\n Schaffner)\r\n* [dv, doc] Replace all 'dv.plan' with testplan (Srikrishna Iyer)\r\n* Fix the testplan link in dvsim code (Srikrishna Iyer)\r\n* [dv/dsim] Add dsim workaround for issue 242 (Guillermo Maturana)\r\n* [util, reggen] Support standardized cdc handling for regfile\r\n (Timothy Chen)\r\n* [dv/shadow_reg] Align shadow_reg field update behavior (Cindy Chen)\r\n* [dvsim] Fix publish report summary typo (Cindy Chen)\r\n* [rtl/prim_alert_sender] Allow ping_req to stay high without error\r\n (Cindy Chen)\r\n* [dvsim] Separate publish report from dvsim flow [PART3] (Cindy Chen)\r\n* [dv/prim_alert] Add a testbench for prim_alert (Cindy Chen)\r\n* [otp_ctrl] Connect test-related GPIO signal (Michael Schaffner)\r\n* [prim_subreg_shadow] Make local parameter a localparam (Philipp\r\n Wagner)\r\n* [prim_subreg] Make software access type an enum (Philipp Wagner)\r\n* [rtl/prim_diff_decode] Add prim_flop_2sync dependency (Cindy Chen)\r\n* [otp_ctrl] Update AscentLint waiver file (Michael Schaffner)\r\n* [edn] Add MaxLatency assertion (Eunchan Kim)\r\n* [prim_subreg_shadow] Correct write data signal usage (Michael\r\n Schaffner)\r\n* [script/dvsim] Separate publish report from dvsim flow [PART2]\r\n (Cindy Chen)\r\n* [prim_lfsr] Fix assertion issue occuring right after reset (Michael\r\n Schaffner)\r\n* [dv/shadow_reg] Handle CSR automated sequence write abort (Cindy\r\n Chen)\r\n* [dv/dv_lib] Add post_apply_reset for extra delay (Guillermo\r\n Maturana)\r\n* [dv] Add function coverage plan for tl_errors, tl_intg_err (Weicai\r\n Yang)\r\n* [dv] Remove tl_intg_err in top-level and increase seeds for\r\n tl_intg_err (Weicai Yang)\r\n* [dv/shadow_reg] Fix alert shadow reg regression error (Cindy Chen)\r\n\r\nSigned-off-by: Rupert Swarbrick "}
+{"org": "lowRISC", "repo": "ibex", "number": 1445, "state": "closed", "title": "Showing warnings related to core file while running simulation", "body": "\r\n\r\n## Observed Behavior\r\nThe warning messages can be seen in Yellow color. \r\n\r\n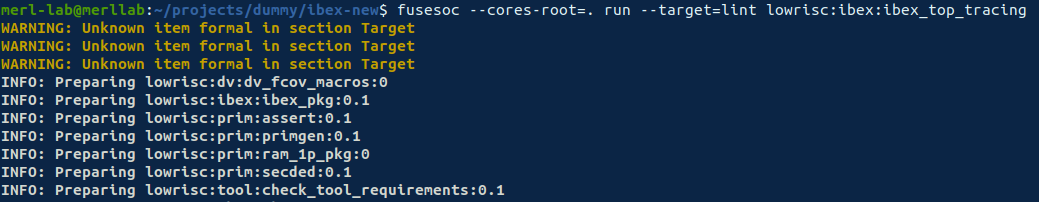\r\n\r\n## Expected Behavior\r\nTADA! Now they are gone. \r\n\r\n\r\n\r\n## Steps to reproduce the issue\r\nI didn't make any modifications to the source code, before running the command. But to resolve the issue I did.\r\n\r\n**EDA tool and version:**\r\nTool verilator present: Sufficiently recent version (found 4.212; needed 4.028)\r\nTool edalize present: Sufficiently recent version (found 0.2.2; needed 0.2.0)\r\nFusesoc 1.11\r\n\r\n**Operating system:**\r\nUbuntu 20.04\r\n\r\n**Version of the Ibex source code:**\r\n\r\n45f727dfc6e59119347aca62e38e69175f680bf6\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1444, "state": "closed", "title": "Building dependency in Fusesoc step fails on Ubuntu 20.04", "body": "\r\n\r\n\r\n\r\nHii, I am trying to run the ibex core on my Ubuntu 20.04 system as suggested in https://github.com/lowRISC/ibex/tree/master/examples/simple_system. \r\n\r\nThe dependencies are correctly installed, but the fusesoc building simulation step fails inspite of that:\r\nfusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system --RV32E=0 --RV32M=ibex_pkg::RV32MFast\r\n\r\nThe error is as follows:\r\n\r\nINFO: Running pre_build script check_tool_requirements\r\nINFO: Tool verilator present: Sufficiently recent version (found 4.213; needed 4.028)\r\nINFO: Tool edalize present: Sufficiently recent version (found 0.2.2; needed 0.2.0)\r\nINFO: Building simulation model\r\nverilator -f lowrisc_ibex_ibex_simple_system_0.vc --trace --trace-fst --trace-structs --trace-params --trace-max-array 1024 -CFLAGS \"-std=c++11 -Wall -DVM_TRACE_FMT_FST -DTOPLEVEL_NAME=ibex_simple_system -g\" -LDFLAGS \"-pthread -lutil -lelf\" -Wall -Wwarn-IMPERFECTSCH --unroll-count 72\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_top_tracing_0.1/rtl/ibex_top_tracing.sv:27:26: Parameter is not used: 'RndCnstLfsrSeed'\r\n : ... In instance ibex_simple_system.u_top\r\n 27 | parameter lfsr_seed_t RndCnstLfsrSeed = RndCnstLfsrSeedDefault,\r\n | ^~~~~~~~~~~~~~~\r\n ... For warning description see https://verilator.org/warn/UNUSED?v=4.213\r\n ... Use \"/* verilator lint_off UNUSED */\" and lint_on around source to disable this message.\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_top_tracing_0.1/rtl/ibex_top_tracing.sv:28:26: Parameter is not used: 'RndCnstLfsrPerm'\r\n : ... In instance ibex_simple_system.u_top\r\n 28 | parameter lfsr_perm_t RndCnstLfsrPerm = RndCnstLfsrPermDefault,\r\n | ^~~~~~~~~~~~~~~\r\n%Error: Exiting due to 2 warning(s)\r\nMakefile:16: recipe for target 'Vibex_simple_system.mk' failed\r\nmake: *** [Vibex_simple_system.mk] Error 1\r\nERROR: Failed to build lowrisc:ibex:ibex_simple_system:0 : 'make' exited with an error code\r\n\r\n\r\nI am new to ibex, can anyone be kind to help me with the resolution of the error. \r\nThanks in advance.\r\n\r\n\r\n\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\n\r\n**Operating system:**\r\n\r\n\r\n**Version of the Ibex source code:**\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1441, "state": "closed", "title": "Use of RD in B type.", "body": "https://github.com/lowRISC/ibex/blob/ac8934459b028220ce9fd20683bb018244b59756/rtl/ibex_tracer.sv#L493\r\n\r\nI am wondering why there is a use of RD in B-type instructions? Is this an issue or I am missing something."}
+{"org": "lowRISC", "repo": "ibex", "number": 1440, "state": "closed", "title": "Error when running ./syn_yosys.sh", "body": "\r\n\r\n## Observed Behavior\r\n\r\nHello,\r\nI am new to Ibex and try to experiment with it.\r\nI have an issue when running the ./syn_yosys.sh script. \r\nMore precisely, I have such error: \r\n`Executing Verilog-2005 frontend: syn_out/ibex_22_09_2021_14_37_02/generated/ibex_top_tracing.v\r\nsyn_out/ibex_22_09_2021_14_37_02/generated/ibex_top_tracing.v:99: ERROR: FATAL: Fatal error: RVFI needs to be defined globally..\r\nFailed to synthesize RTL with Yosys`\r\n\r\n\r\nI did define the syn_setup.sh script with the Nangate45 lib.\r\n\r\nDo you have an idea of why I get such error ?\r\n\r\nThanks for your help.\r\n\r\n## My Environment\r\n\r\n\r\n**Operating system:**\r\n\r\nI am working on Ubuntu 20.04.3 amd64.\r\n**Version of the Ibex source code:**\r\n\r\nI am using the ibex source code version ac8934459b028220ce9fd20683bb018244b59756.\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1435, "state": "closed", "title": "Co-simulation framework", "body": "You can also look at the spike changes here: https://github.com/lowRISC/riscv-isa-sim/commit/d3cd47117e47bef6864d8e5c84f38a9cde0b42ae (it's in a branch in our Spike fork) you can comment directly on that commit.\r\n\r\nThis doesn't include the simple system integration by previous PR did as I've just been working on the UVM environment recently. I do intend to add a simple system integration once we've got this PR merged.\r\n\r\nI've run a full regression with a good pass rate (over 90%) though I've been fiddling with it since so may have broken a few more things. In particular it seems turning on the icache causes issues with instruction errors and a recent RTL change I did seems to be hitting an assertion in ibex_controller.\r\n\r\nI'll be looking at these issues in parallel (and doing another full regression) but wanted to get this PR out finally!"}
+{"org": "lowRISC", "repo": "ibex", "number": 1434, "state": "closed", "title": "[TEST] Fail the linter", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 1427, "state": "closed", "title": "[ci] Add GHA workflows to review PRs using Verible", "body": "This PR adds CI scripts that use [Verible Lint Action](https://github.com/chipsalliance/verible-linter-action)\r\nto automatically review the changes in `.v` and `.sv` files.\r\n\r\nYou can see an example of how this works here:\r\nhttps://github.com/antmicro/gha-playground/pull/20\r\n\r\nIn order to post comments, the action needs a proper token.\r\nDue to restrictions described [in the docs](https://docs.github.com/en/actions/reference/authentication-in-a-workflow#permissions-for-the-github_token) It's not possible to create comments\r\nin the context of `pull_request` from an external repository.\r\nTo tackle this problem we create two workflows:\r\nThe first workflow triggered by `pull_request` stores information\r\nabout the PR in artifact and triggers the main workflow.\r\nThe main workflow runs the Action using a token that allows creating review comments in any PR.\r\n\r\nWe can also add a configuration file for Verible using the `config_file` input.\r\nCurrently the default rule set is used.\r\nThese topics are also described in the Readme of the Action."}
+{"org": "lowRISC", "repo": "ibex", "number": 1425, "state": "closed", "title": "Vivado 2018.3 doesn't recognize SIM_DEVICE param on BUFGCE", "body": "\r\n[Synth 8-3438] module 'BUFGCE' declared at '/tools/Xilinx/Vivado/2018.3/scripts/rt/data/unisim_comp.v:619' does not have any parameter 'SIM_DEVICE' used as named parameter override [\"/home/nioclast0604/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_xilinx_clock_gating_0/rtl/prim_xilinx_clock_gating.sv\":18]\r\n[Synth 8-6156] failed synthesizing module 'prim_xilinx_clock_gating' [\"/home/nioclast0604/ibex/build/lowrisc_ibex_top_artya7_0.1/src/lowrisc_prim_xilinx_clock_gating_0/rtl/prim_xilinx_clock_gating.sv\":5]\r\n[Vivado_Tcl 4-5] Elaboration failed - please see the console for details\r\n\r\n\r\n\r\n## Observed Behavior\r\n\r\nVivado synthesis & implementation for Arty A7 FPGA board\r\n## Expected Behavior\r\n\r\nbitstream finished\r\n## Steps to reproduce the issue\r\nmake build-arty-35 program-arty\r\n\r\n\r\n## My Environment\r\n\r\n\r\n\r\n**EDA tool and version:**\r\nVivado 2018.3\r\n\r\n\r\n**Operating system:**\r\n\r\nUbuntu 18.04.5\r\n**Version of the Ibex source code:**\r\n\r\nmaster fork 246"}
+{"org": "lowRISC", "repo": "ibex", "number": 1423, "state": "closed", "title": "Implenting implementer specified reset value for ePMP", "body": "OpenTitan will want a PMP region configured on reset, along with a non-zero reset value of `mseccfg`: https://github.com/lowRISC/opentitan/issues/7834\r\n\r\nHow do we want to support this in Ibex? I don't think we should use top-level parameters as it'll be a rarely used feature and would require many parameters. We could use `define`. Perhaps if a single `IBEX_CUSTOM_PMP_RESET_VAL` is defined it then uses a whole set of `IBEX_CUSTOM_PMPCFG0_RESET_VAL` `IBEX_CUSTOM_PMPADDR0_RESET_VAL` etc then specify all of the reset values.\r\n\r\nAnother possibility is an `ibex_pmp_reset.svh` include. It'd have a bunch of `localparam` giving all of the reset values. We'd supply a default one with Ibex (that just resets to 0) and implementers, such as OpenTitan, would supply a different include. This may mean a patch against Ibex when we vendor into OT, or perhaps we could use a `define` to specify the name of the include file? Maybe there's something we can do with fusesoc to override the include file used in the build (@imphil any cunning ideas)?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1414, "state": "open", "title": "Violation of the Data Independent Timing property for misaligned Load and Store Instructions", "body": "\r\n\r\n## Observed Behavior\r\nIbex handles misaligned load and store Instructions by splitting them into two separate, aligned memory accesses.\r\nThis creates a data dependent execution time for these Instructions.\r\nAccording to the specification, the **data_ind_timing** control bit should ensure that _execution times and power consumption of all instructions shall be independent of input data_.\r\nHowever, this does not hold for load and store instructions and creates a possible timing side channel.\r\n\r\n\r\n## Expected Behavior\r\nI would expect Ibex to do either one of the following things:\r\n1. Disable the \"misaligned address feature\" whenever the data_ind_timing bit is set to ensure all loads and stores require a single memory access. If a misaligned access is scheduled, Ibex should perform an aligned access and return bogus data. Further, the specification should tell the SW developer to ensure no misaligned access occurs.\r\n2. In a different fix, Ibex could perform an additional dummy memory access (e.g. to an adjacent address), whenever an aligned load/store is issued while the data_ind_timing bit is set.\r\n\r\n\r\n## Steps to reproduce the issue\r\nEnable the data_ind_timing bit and set up a \"secret\" register value.\r\nIssue a LW or LH with the secret register value as source and measure the time.\r\nIf value+offset result in an aligned access, the instruction will only trigger a single memory access.\r\nIf value+offset result in a misaligned access, the instruction will trigger two memory accesses.\r\n\r\nIn the trace, you can see an example with two processor instances.\r\nThe data independent timing bit gets set in both processors (via CSRRW) and the same LH instruction is executed.\r\nHowever, r20 contains different values in the different instances (0 and 3) which causes a misaligned access only in instance 2.\r\nAs a consequence, instance 1 finishes earlier and is ready for the next instruction (id_in_ready_o) whereas instance 2 is requesting a second memory access (data_req_o).\r\n\r\n\r\n\r\n## My Environment\r\nI set up a set of formal SVA properties inside OneSpin to prove data independent execution of different instructions, both with and without the data_ind_timing bit.\r\nFor the proofs, I only consider the ibex_core, i.e., without cache or register file, in a 2-safety approach.\r\nIf you are interested in the details of the methodology, feel free to message me.\r\n\r\n\r\n## My Results\r\nI was able to prove that branches, division and (slow) multiplication have data dependent timing in the non-secure Ibex setting.\r\nAs described in the specification, when the data_ind_timing bit set, all of these issues get resolved.\r\nHowever, I also got counterexamples for both load and store instructions, showing that the same instruction can cause different timing behavior based on register values.\r\nThis behavior does not change with an enabled data_ind_timing bit set.\r\n\r\n**EDA tool and version:** OneSpin 360 DV - Version 2021.1.1\r\n\r\n\r\n**Operating system:** Ubuntu Linux 18.04\r\n\r\n\r\n**Version of the Ibex source code:** 90ff7ca6c3367da721dba13e91dfc98f782a5745\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1390, "state": "closed", "title": "[dv] Azure CI runs missing log output", "body": "The `sim.log` file output during Azure CI runs is missing characters. This can result in false failures as the 'RISC-V UVM TEST PASSED' line isn't seen.\r\n\r\nThe artifacts from this run: https://dev.azure.com/lowrisc/lowrisc-private/_build/results?buildId=45477&view=results contain many examples. I've attached one to this issue, it's missing a `RISC-V UVM TEST PASSED' line (though also reports 0 error/fatal messages) but there's also examples of other missing bits e.g.\r\n\r\n```\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_seq_lib.sv(39) @ 29240000: uvm_test_top.env.irq_agent.sequencer@@irq_drop_seq_h [uvm_test_top.env.irq_agent.sequencer.irq_drop_seq_h] Starting sequence...\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_seq_lib.sv(51) @ 29241000: uvm_test_top.env.irq_agent.sequencer@@irq_drop_seq_h [uvm_test_top.env.irq_agent.sequencer.irq_drop_seq_h] Exiting sequence\r\nUVM_INFO /azp/agentUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_test_lib.sv(206) @ 30966000: uvm_test_top [uvm_test_top] irq_id: 0x1d\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_test_lib.sv(330) @ 31850000: uvm_test_top [uvm_test_top] mcause: 0x8000001d\r\n```\r\n\r\n[sim.log](https://github.com/lowRISC/ibex/files/6732895/sim.log)\r\n\r\n\r\nCould be a tricky one to debug, might be a VCS issue, might be an azure issue. Any thoughts?\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1379, "state": "closed", "title": "DbgTriggerEn impacts mcounteren", "body": "Why does DbgTriggerEn impact mcounteren? That does not look correct to me.\r\n\r\n> // mcounteren: machine counter enable\r\n> CSR_MCOUNTEREN: begin\r\n> csr_rdata_int = '0;\r\n> illegal_csr = ~DbgTriggerEn;\r\n> end\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1372, "state": "closed", "title": "Teach core_ibex testbench to run the comparison step in parallel", "body": "The interesting commit is the second last. Here's its message:\r\n\r\nThis patch teaches Make which tests we're actually running (via the\r\n`list_tests.py` script), which means that we can compare the ISS and RTL\r\nresults in parallel rather than serially.\r\n\r\nThere's a bit of duplicated code (both `list_tests.py` and `sim.py`\r\ncurrently contain the code to get a list of tests and then filter by\r\nIbex configuration), but this should go away with a later patch that\r\nruns the RTL simulations in parallel in a similar way.\r\n\r\nNote: This might seem a little silly: trace comparison takes way less\r\ntime than the RTL simulation! The point is that it's probably easier\r\nto work \"from the bottom\" than to start by parallelising the\r\nsimulations themselves.\r\n\r\n@GregAC: This is in draft because it probably clashes quite badly with the stuff you're thinking about as well. I'm very happy to rebase onto your changes (it's my fault for stepping on your toes!). However, it would be helpful if the comparison stuff could work \"per-file\", passing the pass/fail info to the code that gathers things up through the filesystem, rather than relying on passing a tuple around in the Python. Does that make sense? *(EDIT: We've chatted about it and agreed that it makes sense to merge this first)*"}
+{"org": "lowRISC", "repo": "ibex", "number": 1369, "state": "closed", "title": "[dv] Spike mismatch in riscv_illegal_instr_test", "body": "* Config: opentitan\r\n* Seed: 26328\r\n* Version: 93a76b390081b6b3b6cea2671c469f9293b998f2\r\n\r\n```\r\nriscv_illegal_instr_test.0\r\n--------------------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_illegal_instr_test_0.o\r\nsim log: out/seed-26328/rtl_sim/riscv_illegal_instr_test.0/sim.log\r\nibex : out/seed-26328/rtl_sim/riscv_illegal_instr_test.0/trace_core_00000000.csv\r\nspike : out/seed-26328/instr_gen/spike_sim/riscv_illegal_instr_test.0.csv\r\nMismatch[1]:\r\nibex[16697] : pc[80001680] addi x22,x22,-124: s6:80027db4 \r\nspike[16697] : pc[ffffffff8000c8f4] sbinviw (args unknown): t2:00000010 \r\nMismatch[2]:\r\nibex[16698] : pc[80001700] csrrs x19,mepc,x0: s3:8000c8f4 \r\nspike[16698] : pc[ffffffff80001680] addi s6, s6, -124: s6:80027db4 \r\nMismatch[3]:\r\nibex[16699] : pc[80001704] csrrs x19,mcause,x0: s3:00000002 \r\nspike[16699] : pc[ffffffff80001700] csrr s3, mepc: s3:8000c8f8 \r\nMismatch[4]:\r\nibex[16700] : pc[80001708] c.li x21,3: s5:00000003 \r\nspike[16700] : pc[ffffffff80001704] csrr s3, mcause: s3:00000002 \r\nMismatch[5]:\r\nibex[16701] : pc[80001712] c.li x21,8: s5:00000008 \r\nspike[16701] : pc[ffffffff80001708] c.li s5, 3: s5:00000003 \r\n529 instructions left in trace spike\r\n[FAILED]: 9355 matched, 1833 mismatch\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1368, "state": "closed", "title": "[dv] [ASSERT FAILED] NoMemResponseWithoutPendingAccess in test riscv_reset_test", "body": "* Config: opentitan\r\n* Seed: 26328\r\n* Version: 93a76b390081b6b3b6cea2671c469f9293b998f2\r\n\r\n```\r\nriscv_reset_test.0\r\n------------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_reset_test_0.o\r\nsim log: out/seed-26328/rtl_sim/riscv_reset_test.0/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_core.sv(893) @ 740185700: reporter [ASSERT FAILED] NoMemResponseWithoutPendingAccess\r\n[FAILED]: sim error seen\r\n```\r\n\r\nDoesn't fail for all iterations, but for most of them."}
+{"org": "lowRISC", "repo": "ibex", "number": 1367, "state": "closed", "title": "[dv] [ASSERT FAILED] IbexImmBMuxSelValid in test riscv_csr_test", "body": "* Config: opentitan\r\n* Seed: 26328\r\n* Version: 93a76b390081b6b3b6cea2671c469f9293b998f2\r\n\r\n```\r\nriscv_csr_test.0\r\n----------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_csr_test_0.o\r\nsim log: out/seed-26328/rtl_sim/riscv_csr_test.0/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_id_stage.sv(346) @ 7861700: reporter [ASSERT FAILED] IbexImmBMuxSelValid\r\n[FAILED]: sim error seen\r\n\r\nriscv_csr_test.1\r\n----------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_csr_test_1.o\r\nsim log: out/seed-26328/rtl_sim/riscv_csr_test.1/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_id_stage.sv(346) @ 7977600: reporter [ASSERT FAILED] IbexImmBMuxSelValid\r\n[FAILED]: sim error seen\r\n\r\nriscv_csr_test.2\r\n----------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_csr_test_2.o\r\nsim log: out/seed-26328/rtl_sim/riscv_csr_test.2/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_id_stage.sv(346) @ 7950600: reporter [ASSERT FAILED] IbexImmBMuxSelValid\r\n[FAILED]: sim error seen\r\n\r\nriscv_csr_test.3\r\n----------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_csr_test_3.o\r\nsim log: out/seed-26328/rtl_sim/riscv_csr_test.3/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_id_stage.sv(346) @ 8452800: reporter [ASSERT FAILED] IbexImmBMuxSelValid\r\n[FAILED]: sim error seen\r\n\r\nriscv_csr_test.4\r\n----------------\r\nTest binary: out/seed-26328/instr_gen/asm_test/riscv_csr_test_4.o\r\nsim log: out/seed-26328/rtl_sim/riscv_csr_test.4/sim.log\r\nUVM_ERROR /azp/agent/_work/1/s/rtl/ibex_id_stage.sv(346) @ 7924300: reporter [ASSERT FAILED] IbexImmBMuxSelValid\r\n[FAILED]: sim error seen\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1365, "state": "closed", "title": "I git clone the riscv-gnu- toolchain and configured it and then i got the error as follows", "body": "akhil@uhdct3-OptiPlex-3040:~$ cd risc/lowrisc/ibex\r\nakhil@uhdct3-OptiPlex-3040:~/risc/lowrisc/ibex$ make build-arty-35 program-arty cd examples/sw/led && make\r\nmake[1]: Entering directory '/home/akhil/risc/lowrisc/ibex/examples/sw/led'\r\nriscv32-unknown-elf-gcc -march=rv32imc -mabi=ilp32 -static -mcmodel=medany -fvisibility=hidden -nostdlib -nostartfiles -Wall -g -Os -MMD -c -o led.o led.c\r\nmake[1]: riscv32-unknown-elf-gcc: Command not found\r\nMakefile:50: recipe for target 'led.o' failed\r\nmake[1]: *** [led.o] Error 127\r\nmake[1]: Leaving directory '/home/akhil/risc/lowrisc/ibex/examples/sw/led'\r\nMakefile:65: recipe for target 'examples/sw/led/led.vmem' failed\r\nmake: *** [examples/sw/led/led.vmem] Error 2\r\nakhil@uhdct3-OptiPlex-3040:~/risc/lowrisc/ibex$\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1362, "state": "closed", "title": "Produce a configuration matching OpenTitan", "body": "We currently don't have a configuration for Ibex that matches what we're using in OpenTitan experimental-maxperf-pmp-bmfull-icache is close, but we don't enable the B extension. And we probably need to add the SecureIbex flag to the config as well. "}
+{"org": "lowRISC", "repo": "ibex", "number": 1352, "state": "closed", "title": "Ibex simple system fails to simulate with verilator (segmentation fault)", "body": "Ibex simple system verilator simulation fails with segmentation fault. I have tracked down the fault to the function `DpiMemUtil::RegisterMemoryArea`, and I believe the fault occurs somewhere here:\r\nhttps://github.com/lowRISC/ibex/blob/8ef06de73daa7c22400f0e617088aeea06a2601c/vendor/lowrisc_ip/dv/verilator/cpp/dpi_memutil.cc#L329-L338\r\n\r\nUnfortunately I lack the context to fix it....\r\n\r\nI am simulating with verilator v. 4.200.\r\nHow to reproduce:\r\n```\r\nfusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system # build simulator\r\nmake -C examples/sw/simple_system/hello_test/ # build elf\r\n./build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/Vibex_simple_system --meminit=ram,examples/sw/simple_system/hello_test/hello_test.elf # Run sim\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1335, "state": "closed", "title": "Usage of prim_clock_gating and latch_map.v during synthesis", "body": "(1) Do I need to use both prim_clock_gating.v and latch_map.v file during synthesis when using RegfileFF as my configuration?\r\nAlso In reference with closed case #1299 @GregAC told that \r\n\r\n`prim_clock_gating.v is a file required to build Ibex, it is used for the top-level clock gate the enables/disables the CPU clock. latch_map.v allow yosys to build the latch based synthesis file by telling it what latch cells to use. This too may require adjustment for library other than nangate.`\r\n\r\nIf answer for (1) is no, then if I want to use RegfileLatch do I need to change both files if I am using a differenct library for synthesis?changing latch_map.v makes sense. What about prim_clock_gating.v, I can't see any latch maping there?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1333, "state": "open", "title": "[dv] Enable multiple configurations for CSR test", "body": "The current `riscv_csr_test` uses the file https://github.com/lowRISC/ibex/blob/master/dv/uvm/core_ibex/riscv_dv_extension/csr_description.yaml to determine what CSRs to read/write and expected values. These descriptions can change between Ibex configurations so a solution is needed to allow this test to adapt to different configurations."}
+{"org": "lowRISC", "repo": "ibex", "number": 1329, "state": "closed", "title": "[rtl] Fix RF read enables for illegal instruction/fetch error", "body": "The read enables should only be asserted where an actual RF read will\r\noccur. Where there is an illegal instruction or a fetch error the raw\r\ndecoder signals might still be asserted but should be squashed before\r\nthey become the true enable signals."}
+{"org": "lowRISC", "repo": "ibex", "number": 1313, "state": "closed", "title": "[dv] riscv_debug_ebreakmu_test: Core did not enter debug mode after execution of ebreak", "body": "* Config: experimental-maxperf-pmp-bmfull-icache\r\n* `regr.log`: \r\n```\r\nriscv_debug_ebreakmu_test.9\r\n---------------------------\r\nTest binary: out/seed-27831/instr_gen/asm_test/riscv_debug_ebreakmu_test.9.o\r\nsim log: out/seed-27831/rtl_sim/riscv_debug_ebreakmu_test.9/sim.log\r\nUVM_FATAL /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_base_test.sv(204) @ 8886400: reporter [uvm_test_top] Check failed signature_data == core_status (8 [0x8] vs 1 [0x1]) Core did not enter debug mode after execution of ebreak\r\n[FAILED]: sim error seen\r\n```\r\n* Log files and waves: [simerror-riscv_debug_ebreakmu_test.zip](https://github.com/lowRISC/ibex/files/6183819/simerror-riscv_debug_ebreakmu_test.zip)\r\n\r\n@udinator @GregAC"}
+{"org": "lowRISC", "repo": "ibex", "number": 1297, "state": "closed", "title": "[epmp] question about handling mseccfg high bits", "body": "In the [ePMP specification](https://ibex-core.readthedocs.io/en/latest/_downloads/adbc55b5b9bad5f92968b58e7b12fc57/riscv-epmp.pdf) `mseccfg` is specified as a 64-bit register that is split into two parts (low at 0x390 and high at 0x391) on 32-bit architectures.\r\n\r\nThe Ibex documentation doesn't mention this so I am curious as to how/if we are currently handling the high bits. Should we document a `mseccfgh` zero read-only register at 0x391 so that portable software can read the full 64-bit value?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1284, "state": "closed", "title": "[dv] get ibex dv co-sim to run w questa", "body": "Fixes #1280"}
+{"org": "lowRISC", "repo": "ibex", "number": 1282, "state": "closed", "title": "The output of Cycles is negative", "body": "## Observed Behavior\r\nWhen the most significant bit of `mcycleh` is 1, the output value of `Cycles` is a negative value. I feel that the cycle should be treated as an unsigned integer. Is it the expected behavior?\r\n\r\n## Steps to reproduce the issue\r\nI overwrote the program to `example/sw/simple_system/hello_test/hello_test.c`.\r\n\r\n```c\r\nint main(int argc, char **argv) {\r\n asm volatile (\"li t0, 0x80000000;\"\r\n \"csrw mcycleh, t0;\");\r\n return 0;\r\n}\r\n```\r\n\r\nBuild the processor and compile the test program.\r\nRun the test program.\r\n```\r\nfusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system\r\nmake -C examples/sw/simple_system/hello_test\r\n./build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/Vibex_simple_system --meminit=ram,./examples/sw/simple_system/hello_test/hello_test.elf\r\n```\r\n\r\nThe following value of performance counter is displayed on the standard output.\r\n```\r\nSimulation of Ibex\r\n==================\r\n\r\nTracing can be toggled by sending SIGUSR1 to this process:\r\n$ kill -USR1 30424\r\n\r\nSimulation running, end by pressing CTRL-c.\r\nTOP.ibex_simple_system.u_core.u_ibex_tracer.unnamedblk1: Writing execution trace to trace_core_00000000.log\r\nTerminating simulation by software request.\r\n- ../src/lowrisc_ibex_sim_shared_0/./rtl/sim/simulator_ctrl.sv:93: Verilog $finish\r\nReceived $finish() from Verilog, shutting down simulation.\r\n\r\nSimulation statistics\r\n=====================\r\nExecuted cycles: 91\r\nWallclock time: 0.001 s\r\nSimulation speed: 91000 cycles/s (91 kHz)\r\n\r\nPerformance Counters\r\n====================\r\nCycles: -9223372036854775722\r\nNONE: 0\r\nInstructions Retired: 66\r\nLSU Busy: 6\r\nFetch Wait: 8\r\nLoads: 0\r\nStores: 6\r\nJumps: 3\r\nConditional Branches: 6\r\nTaken Conditional Branches: 4\r\nCompressed Instructions: 39\r\nMultiply Wait: 0\r\nDivide Wait: 0\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1280, "state": "closed", "title": "[Component:DV] Add timescale to questasim", "body": "## Observed Behavior\r\nWhen attempting to run rtl_sim under `ibex/dv/uvm/core_ibex` using questasim, the sim errors out before running, in particular during the `vendor/lowrisc_ip/dv/sv/common_ifs/clk_rst_if.sv` initial block.\r\n```\r\n fork:\r\n begin:\r\n wait_for_reset(.wait_posedge(1'b0));\r\n\r\n // Wait a short time after reset before starting to drive the clock.\r\n #1ps;\r\n o_clk = 1'b0;\r\n\r\n done = 1'b1;\r\n end\r\n while (!done) #(clk_period_ps * 1ps);\r\n join\r\n```\r\n\r\noutput `dv/uvm/core_ibex/out/seed-1234/rtl_sim/riscv_machine_mode_rand_test.0/sim.log`:\r\n```\r\n############# Autofindloop Analysis ############### \r\n############# Loop found at time 0 ns ############### \r\n# Wakeup process: /core_ibex_tb_top/ibex_clk_if/#FORK#244_2a9aa4752c0 @ sub-iteration 0\r\n# Source: /home/mescobar/ibex/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv:14\r\n# Wakeup process: /core_ibex_tb_top/ibex_clk_if/#FORK#244_2a9aa4752c0 @ sub-iteration 1\r\n# Source: /home/mescobar/ibex/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv:14\r\n# Wakeup process: /core_ibex_tb_top/ibex_clk_if/#FORK#244_2a9aa4752c0 @ sub-iteration 2\r\n# Source: /home/mescobar/ibex/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv:14\r\n################# END OF LOOP ################# \r\n# ** Error (suppressible): (vsim-3601) Iteration limit 10000000 reached at time 0 ns.\r\n######## Additional Loop Analysis Started ########## \r\n############## Autofindloop Step ################## \r\n# Active process: /core_ibex_tb_top/#INITIAL#172 \r\n# Source: /home/mescobar/ibex/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv:172\r\n# Active process: /uvm_pkg::uvm_root::run_test/#FORK#500_2a9aa47512b \r\n# Source: /home/apps/Mentor/questa/2020.3/questasim/linux_x86_64/../verilog_src/uvm-1.2/src/base/uvm_root.svh:400\r\n# Active process: /uvm_pkg::uvm_phase::m_run_phases/#FORK#2213_2a9aa475060 \r\n# Source: /home/apps/Mentor/questa/2020.3/questasim/linux_x86_64/../verilog_src/uvm-1.2/src/base/uvm_phase.svh:2196\r\n################################################### \r\n```\r\n\r\n## Expected Behavior\r\nExpect the sim to generate clocks & resets then load the functional memory with code and proceed with co-simulation.\r\n\r\n## Steps to reproduce the issue\r\ncommand:\r\n```\r\ncd dv/uvm/core_ibex\r\nmake TEST=riscv_machine_mode_rand_test ITERATIONS=1 SIMULATOR=questa SEED=1234 VERBOSE=1 SIM_OPTS=\"+UVM_VERBOSITY=UVM_DEBUG\"\r\n```\r\n\r\nI was able to resolve issue when editing `dv/uvm/core_ibex/yaml/rtl_simulation.yaml`.\r\n- remove `-access=rwc` from questa vlog command (bug present in [riscv-dv](https://github.com/google/riscv-dv/issues/780) we well)\r\n- add `-timescale \\\"1 ns / 1 ps\\\"` to vlog command\r\nexample:\r\n```\r\n- tool: questa\r\n compile:\r\n cmd:\r\n - \"vmap mtiUvm $QUESTA_HOME/questasim/uvm-1.2\"\r\n - \"vlog -64\r\n -f ibex_dv.f\r\n -sv\r\n -mfcu -cuname design_cuname\r\n +define+UVM_REGEX_NO_DPI\r\n +define+UVM\r\n -timescale \\\"1 ns / 1 ps\\\"\r\n -writetoplevels /top.list\r\n -l /compile.log \"\r\n```\r\n\r\n## My Environment\r\nRunning ibex [verification](https://github.com/lowRISC/ibex/blob/master/doc/03_reference/verification.rst).\r\n\r\n**EDA tool and version:**\r\nRunning with QuestaSim 2020.3\r\n\r\n**Operating system:**\r\nCentOS 7\r\n\r\n**Version of the Ibex source code:**\r\n```\r\n$ git rev-parse HEAD\r\n99b8f612234adc76e70cfc53f00a451b3ad4662a\r\n```\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1279, "state": "closed", "title": "Interrupts during debug single stepping", "body": "Do we want to enable interrupts whilst single stepping is enabled? The RISC-V debug spec has a bit `stepie` in `dcsr` that enables/disable interrupts during single stepping. It is permitted for an implementation to hard-wire this to 0 (interrupts disabled when single stepping).\r\n\r\nCurrently Ibex does not implement this bit though does it allow it be written. We should either implement it or hardwire it to 0.\r\n\r\nI would tend towards hardwire to 0 for simplicity (note this would still allow single stepping inside an interrupt handler, it would simply prevent single stepping into one if an interrupt is raised whilst single stepping)."}
+{"org": "lowRISC", "repo": "ibex", "number": 1278, "state": "closed", "title": "Add support for mcounteren CSR", "body": "It has been reported in lowRISC/OpenTitan#5322 that Ibex doesn't implement the `mcounteren` CSR (0x306). The RISC-V Priv. Spec (20190608-Priv-MSU-Ratified) says (see Section 3.1.12): \"Registers mcounteren and scounteren are WARL registers that must be implemented if U-mode and S-mode are implemented. Any of the bits may contain a hardwired value of zero, indicating\r\nreads to the corresponding counter will cause an illegal instruction exception when executing in a less-privileged mode.\"\r\n\r\nI don't know if we want to make the register writeable and enable access to the counters in U-mode. But we should at least add the register as read only, hardwired to 0.\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1263, "state": "closed", "title": "Doubt in .dis file generated under examples/sw/", "body": "Hi,\r\nI have a doubt in the .dis file generated in the example/sw/simple_system.\r\nIn the .dis file generated there above every pc count I am seeing one more instruction, how is it generated and what is the purpose of it?\r\n\r\nIN the below snapshot if you see the bld instructions. on top of some instructions its not getting generated (1006e0 & 1006e4)\r\n\r\n **addi x10, x0, 0**\r\n 1006d8:\t4501 \tli\ta0,0\r\n \r\n **addi x11, x0, 0**\r\n 1006da:\t4581 \tli\ta1,0\r\n \r\n **jal x1, main**\r\n 1006dc:\t00a030ef \tjal\tra,1036e6 \r\n \r\n **li x5, SIM_CTRL_BASE + SIM_CTRL_CTRL**\r\n 1006e0:\t000202b7 \tlui\tt0,0x20\r\n 1006e4:\t02a1 \taddi\tt0,t0,8\r\n \r\n **li x6, 1**\r\n 1006e6:\t4305 \tli\tt1,1\r\n\r\n **sw x6, 0(x5)**\r\n 1006e8:\t0062a023 \tsw\tt1,0(t0) # 20000 <_stack_len+0x18000>\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1250, "state": "closed", "title": "[verilator] Remove clock gating waiver and add extra warning", "body": "The `-Wwarn-IMPERFECTSCH` flag is suggested in the Verilator docs (to\r\nhelp spot if we get a clock gating hint wrong). The waiver is no\r\nlonger needed because we now add the relevant hint in the\r\nRTL (vendored in `prim_generic_clock_gating.sv` from OpenTitan).\r\n\r\nCloses #212."}
+{"org": "lowRISC", "repo": "ibex", "number": 1248, "state": "closed", "title": "Issue in ibex docs regarding OVPsim and spec version setting", "body": "I note in the doc: https://github.com/lowRISC/ibex/blob/master/doc/03_reference/verification.rst you say:\r\n\r\n> The master branch of Spike and OVPSim may support a different version. It is recommended the lowRISC-specific branch of Spike is used when using a configuration with Bitmanip to ensure the simulated version of the Bitmanip specification matches with the RTL implemented version.\r\n\r\nThis is not giving the correct picture - yes you can use OVPsim with the latest version and you get the current spec version as 'master' [for today that is bitmanip 0.94-draft] but as you correctly indicate that is pretty useless for verification where you are trying to verify another version of the spec, eg v0.92.\r\n\r\nOVPsim has parameters to set the specific version of the individual ISA extensions that you are using - so if it is bitmanip, crypto, vector, debug, p-dsp, user, priv, etc., - whatever - the simulator allows specific control - so you get what you are going to silicon with - users say this is a far better approach than each of them having to maintain their own modified branches of simulators for their silicon - they make use of simulators (like OVPsim) that are focused on helping people be more effective and efficient with their verification.\r\n\r\nSo maybe you could clarify in the doc the OVPsim setting of spec versions and not just being the head like spike..\r\n\r\nAlso, if you want help setting the correct spec versions for OVPsim - let us know how we can help.\r\n\r\nThanks\r\nSimon\r\nImperas Software (creators of OVPsim)\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1245, "state": "closed", "title": "[rtl] Fix lint warning when DbgTriggerEn parameter is set", "body": "`DbgHwBreakNum - 1` is an int, so generates a warning if it's assigned\r\nto `tselect_d` (of type `logic [DbgHwNumLen-1:0]`). Explicitly generate\r\nthe value we need as a localparam.\r\n\r\nThis lint warning doesn't appear by default in the Ibex repository,\r\nbecause `DbgTriggerEn` is disabled. It does, however, appear in\r\nOpenTitan because we enable it there."}
+{"org": "lowRISC", "repo": "ibex", "number": 1231, "state": "closed", "title": "[doc/um] Updated the python requirements run command for sw simple sy…", "body": "…stem\r\n\r\nUpdated the README file for python requirements run command.\r\n@imphil \r\nSigned-off-by: Rahul Raveendran "}
+{"org": "lowRISC", "repo": "ibex", "number": 1228, "state": "open", "title": "[tracking] Activate pseudo zext.[b|h] decoding", "body": "The tracer currently does not decode the pseudo instruction.\r\nUse it once it is supported by more tools. Actually not quite which, but it was recently mentioned in https://github.com/llvm/llvm-project/commit/249d7de1190f50178181d2477aa661cd252e294c"}
+{"org": "lowRISC", "repo": "ibex", "number": 1227, "state": "closed", "title": "Remove Verilator warnings", "body": "Following the reports in #1219 I had a look at Verilator and with https://github.com/verilator/verilator/commit/47eeef485d1781f104211d96ffb7498f55ae1b2b warnings are now created for unused parameters.\r\n\r\nIt also will create a warning for latches.\r\n\r\nRemove those occurrences."}
+{"org": "lowRISC", "repo": "ibex", "number": 1224, "state": "closed", "title": "\"Decimal constant too large\" in core_ibex_tb_top.sv", "body": "I just saw this line, it's part of all regression runs.\r\n\r\n```\r\nParsing design file '/azp/agent/_work/1/s/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv'\r\n\r\nWarning-[DCTL] Decimal constant too large\r\n/azp/agent/_work/1/s/dv/uvm/core_ibex/tb/core_ibex_tb_top.sv, 62\r\n Decimal constant '2147483648' is too large as a 32bit signed constant, it \r\n should be smaller than 2147483648.\r\n VCS is using converted signed value '-2147483648' instead.\r\n To make it an unsigned constant, please use sized constant format.\r\n```\r\n\r\nThe offending line is\r\n```\r\nbit [31:0] addr = `BOOT_ADDR;\r\n```\r\n\r\nwith BOOT_ADDR being (effectively) 0x80000000. \r\n\r\n@udinator Can you have a look (not urgent, it's only a warning)? Probably an explicit cast is needed?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1219, "state": "closed", "title": "build simple system error", "body": "\r\n\r\n\r\n\r\n\r\n## My Environment\r\n\r\nHi all,\r\n\r\nI have compiled verilator from the source and installed fusesoc. when I was building the simple system under the root of ibex directory,\r\n\r\n```\r\nmake build-simple-system\r\n```\r\n\r\nit gives warning information as following,\r\n\r\n```\r\nfusesoc --cores-root=. run --target=sim --setup --build \\\r\n\tlowrisc:ibex:ibex_simple_system \\\r\n\t--RV32E=0 --RV32M=ibex_pkg::RV32MFast --RV32B=ibex_pkg::RV32BNone --RegFile=ibex_pkg::RegFileFF --BranchTargetALU=0 --WritebackStage=0 --ICache=0 --ICacheECC=0 --BranchPredictor=0 --PMPEnable=0 --PMPGranularity=0 --PMPNumRegions=4\r\nWARNING: Unknown item formal in section Target\r\nWARNING: Unknown item formal in section Target\r\nWARNING: Unknown item formal in section Target\r\nINFO: Preparing lowrisc:dv_verilator:ibex_pcounts:0\r\nINFO: Preparing lowrisc:dv_verilator:memutil_dpi:0\r\nINFO: Preparing lowrisc:dv_verilator:simutil_verilator:0\r\nINFO: Preparing lowrisc:ibex:ibex_pkg:0.1\r\nINFO: Preparing lowrisc:prim:assert:0.1\r\nINFO: Preparing lowrisc:prim:primgen:0.1\r\nINFO: Preparing lowrisc:prim:secded:0.1\r\nINFO: Preparing lowrisc:tool:check_tool_requirements:0.1\r\nINFO: Preparing lowrisc:dv_verilator:memutil_verilator:0\r\nINFO: Preparing lowrisc:ibex:ibex_tracer:0.1\r\nINFO: Preparing lowrisc:lint:common:0.1\r\nINFO: Preparing lowrisc:prim:prim_pkg:0.1\r\nINFO: Preparing lowrisc:prim:clock_gating:0\r\nINFO: Preparing lowrisc:prim:lfsr:0.1\r\nINFO: Preparing lowrisc:prim:ram_1p:0\r\nINFO: Preparing lowrisc:prim:ram_2p:0\r\nINFO: Preparing lowrisc:ibex:ibex_icache:0.1\r\nINFO: Preparing lowrisc:ibex:sim_shared:0\r\nINFO: Preparing lowrisc:ibex:ibex_core:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_core_tracing:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_simple_system:0\r\nINFO: Generating lowrisc:prim:prim_pkg-impl:0.1\r\nCreating prim_pkg.sv\r\nCore file written to prim_pkg.core.\r\nINFO: Generating lowrisc:prim:clock_gating-impl:0\r\nImplementations for primitive clock_gating: generic, xilinx\r\nInspecting generic module /home/qian/repositories/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_clock_gating.sv\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.sv\r\nCreating core file for primitive clock_gating.\r\nCore file written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_clock_gating-impl_0/prim_clock_gating.core\r\nINFO: Generating lowrisc:prim:ram_1p-impl:0\r\nImplementations for primitive ram_1p: generic, badbit\r\nInspecting generic module /home/qian/repositories/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_1p.sv\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.sv\r\nCreating core file for primitive ram_1p.\r\nCore file written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_1p-impl_0/prim_ram_1p.core\r\nINFO: Generating lowrisc:prim:ram_2p-impl:0\r\nImplementations for primitive ram_2p: generic\r\nInspecting generic module /home/qian/repositories/ibex/vendor/lowrisc_ip/ip/prim_generic/rtl/prim_generic_ram_2p.sv\r\nCreating SystemVerilog module for abstract primitive\r\nAbstract primitive written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.sv\r\nCreating core file for primitive ram_2p.\r\nCore file written to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/generated/lowrisc_prim_ram_2p-impl_0/prim_ram_2p.core\r\nINFO: Wrote dependency graph to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/lowrisc_ibex_ibex_simple_system_0.deps-after-generators.dot\r\nINFO: Wrote Makefile fragment to /home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/core-deps.mk\r\nINFO: Setting up project\r\n\r\nINFO: Running pre_build script check_tool_requirements\r\nINFO: Found sufficiently recent version of verilator (found 4.107, need 4.028)\r\nINFO: Found sufficiently recent version of edalize (found 0.2.2, need 0.2.0)\r\nINFO: Building simulation model\r\nmake[1]: Entering directory '/home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator'\r\nverilator -f lowrisc_ibex_ibex_simple_system_0.vc --trace --trace-fst --trace-structs --trace-params --trace-max-array 1024 -CFLAGS \"-std=c++11 -Wall -DVM_TRACE_FMT_FST -DTOPLEVEL_NAME=ibex_simple_system -g\" -LDFLAGS \"-pthread -lutil -lelf\" -Wall --unroll-count 72\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:26:24: Parameter is not used: 'INSN_BALL'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 26 | parameter logic [31:0] INSN_BALL = { 17'h?, 3'b010, 5'h?, {OPCODE_BRANCH} };\r\n | ^~~~~~~~~\r\n ... Use \"/* verilator lint_off UNUSED */\" and lint_on around source to disable this message.\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:85:24: Parameter is not used: 'INSN_ZEXTB'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 85 | parameter logic [31:0] INSN_ZEXTB = { 4'b0000, 8'b11111111, 5'h?, 3'b111, 5'h?, {OPCODE_OP_IMM} };\r\n | ^~~~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:87:24: Parameter is not used: 'INSN_ZEXTH'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 87 | parameter logic [31:0] INSN_ZEXTH = { 7'b0000100, 5'b00000, 5'h?, 3'b100, 5'h?, {OPCODE_OP} };\r\n | ^~~~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:296:24: Parameter is not used: 'INSN_CMV'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 296 | parameter logic [15:0] INSN_CMV = { 3'b100, 1'b0, 10'h?, {OPCODE_C2} };\r\n | ^~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:297:24: Parameter is not used: 'INSN_CADD'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 297 | parameter logic [15:0] INSN_CADD = { 3'b100, 1'b1, 10'h?, {OPCODE_C2} };\r\n | ^~~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:298:24: Parameter is not used: 'INSN_CEBREAK'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 298 | parameter logic [15:0] INSN_CEBREAK = { 3'b100, 1'b1, 5'h0, 5'h0, {OPCODE_C2} };\r\n | ^~~~~~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:299:24: Parameter is not used: 'INSN_CJR'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 299 | parameter logic [15:0] INSN_CJR = { 3'b100, 1'b0, 5'h0, 5'h0, {OPCODE_C2} };\r\n | ^~~~~~~~\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_tracer_0.1/rtl/ibex_tracer_pkg.sv:300:24: Parameter is not used: 'INSN_CJALR'\r\n : ... In instance ibex_simple_system.u_core.u_ibex_core\r\n 300 | parameter logic [15:0] INSN_CJALR = { 3'b100, 1'b1, 5'h?, 5'h0, {OPCODE_C2} };\r\n | ^~~~~~~~~~\r\n%Warning-LATCH: ../src/lowrisc_ibex_sim_shared_0/./rtl/bus.sv:61:3: Latch inferred for signal 'ibex_simple_system.u_bus.host_sel_req' (not all control paths of combinational always assign a value)\r\n : ... Suggest use of always_latch for intentional latches\r\n 61 | always_comb begin\r\n | ^~~~~~~~~~~\r\n%Warning-LATCH: ../src/lowrisc_ibex_sim_shared_0/./rtl/bus.sv:70:3: Latch inferred for signal 'ibex_simple_system.u_bus.device_sel_req' (not all control paths of combinational always assign a value)\r\n : ... Suggest use of always_latch for intentional latches\r\n 70 | always_comb begin\r\n | ^~~~~~~~~~~\r\n%Error: Exiting due to 10 warning(s)\r\nMakefile:16: recipe for target 'Vibex_simple_system.mk' failed\r\nmake[1]: *** [Vibex_simple_system.mk] Error 1\r\nmake[1]: Leaving directory '/home/qian/repositories/ibex/build/lowrisc_ibex_ibex_simple_system_0/sim-verilator'\r\n```\r\n\r\nIt seems there are too many warnings to stall the build process, how could I fix it ? Please help me, thanks in advance.\r\n\r\n\r\n\r\n**EDA tool and version:**\r\n\r\nverilator version: Verilator 4.107 devel rev v4.106-155-ga1170027\r\nfusesoc version: 1.11.dev57+g1fb8c93\r\n\r\n**Operating system:**\r\n\r\nUbuntu 18.04 LTS\r\n\r\n**Version of the Ibex source code:**\r\n\r\nmaster branch(0199bbae665b9b142144e6688279e2ecef7d83a0)"}
+{"org": "lowRISC", "repo": "ibex", "number": 1213, "state": "closed", "title": "'Assert' line 836 of file ibex_controller.sv not understood by some version of Xcelium", "body": "Current code:\r\n`ASSERT(AlwaysInstrClearOnMispredict, nt_branch_mispredict_o -> instr_valid_clear_o)\r\n\r\nSuggested code (a 'pipe'='|' added):\r\n`ASSERT(AlwaysInstrClearOnMispredict, nt_branch_mispredict_o |-> instr_valid_clear_o)\r\n\r\nCurrent code fails with Xcellium 19.03-s001 for example. But works with a more recent version (20.10...)\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1193, "state": "closed", "title": "syn_yosys.sh failure at 'translate_timing_csv.py' phase", "body": "Hi,\r\nNot sure if this is related to an environment, python setup or anything else but I'm getting below error towards the end of syn_yosys.sh script execution (yosys completed, sta completed - conversion of timing results failed):\r\n\r\n```\r\nReplacing existing blackbox module XOR2_X1.\r\nReplacing existing blackbox module XOR2_X2.\r\nImported 134 cell types from liberty file.\r\n\r\n3. Executing Verilog-2005 frontend: ./syn_out/ibex_16_11_2020_16_16_55/generated/ibex_core_netlist.v\r\nParsing Verilog input from `./syn_out/ibex_16_11_2020_16_16_55/generated/ibex_core_netlist.v' to AST representation.\r\nGenerating RTLIL representation for module `\\ibex_core'.\r\nSuccessfully finished Verilog frontend.\r\n\r\nEnd of script. Logfile hash: 74b8848413, CPU: user 2.85s system 0.10s, MEM: 201.43 MB peak\r\nYosys 0.9+3675 (git sha1 71ca9a82, gcc 7.5.0-3ubuntu1~18.04 -fPIC -Os)\r\nTime spent: 88% 2x read_verilog (2 sec), 11% 4x read_liberty (0 sec), ...\r\n**Traceback (most recent call last):\r\n File \"./python/translate_timing_csv.py\", line 41, in \r\n main()\r\n File \"./python/translate_timing_csv.py\", line 28, in main\r\n path_info, '{}/{}'.format(args.gen_out, ys_translated_names))\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 69, in translate_path_info\r\n translated_names_dict = build_translated_names_dict(translated_names_file)\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 54, in build_translated_names_dict\r\n translated_names = open(translated_names_file)\r\nFileNotFoundError: [Errno 2] No such file or directory: './syn_out/ibex_16_11_2020_16_16_55/generated/ys_translated_names'\r\nTraceback (most recent call last):\r\n File \"./python/translate_timing_csv.py\", line 41, in \r\n main()\r\n File \"./python/translate_timing_csv.py\", line 28, in main\r\n path_info, '{}/{}'.format(args.gen_out, ys_translated_names))\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 69, in translate_path_info\r\n translated_names_dict = build_translated_names_dict(translated_names_file)\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 54, in build_translated_names_dict\r\n translated_names = open(translated_names_file)\r\nFileNotFoundError: [Errno 2] No such file or directory: './syn_out/ibex_16_11_2020_16_16_55/generated/ys_translated_names'\r\nTraceback (most recent call last):\r\n File \"./python/translate_timing_csv.py\", line 41, in \r\n main()\r\n File \"./python/translate_timing_csv.py\", line 28, in main\r\n path_info, '{}/{}'.format(args.gen_out, ys_translated_names))\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 69, in translate_path_info\r\n translated_names_dict = build_translated_names_dict(translated_names_file)\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 54, in build_translated_names_dict\r\n translated_names = open(translated_names_file)\r\nFileNotFoundError: [Errno 2] No such file or directory: './syn_out/ibex_16_11_2020_16_16_55/generated/ys_translated_names'\r\nTraceback (most recent call last):\r\n File \"./python/translate_timing_csv.py\", line 41, in \r\n main()\r\n File \"./python/translate_timing_csv.py\", line 28, in main\r\n path_info, '{}/{}'.format(args.gen_out, ys_translated_names))\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 69, in translate_path_info\r\n translated_names_dict = build_translated_names_dict(translated_names_file)\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 54, in build_translated_names_dict\r\n translated_names = open(translated_names_file)\r\nFileNotFoundError: [Errno 2] No such file or directory: './syn_out/ibex_16_11_2020_16_16_55/generated/ys_translated_names'\r\nTraceback (most recent call last):\r\n File \"./python/translate_timing_csv.py\", line 41, in \r\n main()\r\n File \"./python/translate_timing_csv.py\", line 28, in main\r\n path_info, '{}/{}'.format(args.gen_out, ys_translated_names))\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 69, in translate_path_info\r\n translated_names_dict = build_translated_names_dict(translated_names_file)\r\n File \"/home/yanek/Sources/riscv/ibex/syn/python/flow_utils.py\", line 54, in build_translated_names_dict\r\n translated_names = open(translated_names_file)\r\nFileNotFoundError: [Errno 2] No such file or directory: './syn_out/ibex_16_11_2020_16_16_55/generated/ys_translated_names'**\r\nArea in kGE = 26.37\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 1181, "state": "closed", "title": "PMP CSR enhancement / bug", "body": "Looking PMP granularity as part of #1178 I noticed we always keep the PMP address CSRs as 32bits despite the granularity. At best this is inefficient as we're missing out on area savings, at worst it's a bug since we use the raw address in the matching logic (which doesn't match the modified version the user sees on a CSR read)."}
+{"org": "lowRISC", "repo": "ibex", "number": 1178, "state": "closed", "title": "PMP NAPOT masks are incorrect when the region address spans the entire granule", "body": "The address masking logic in [`ibex_pmp.sv`](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_pmp.sv) always considers the lowest bit of the granule of the PMP address configuration register (i.e. `csr_pmp_addr_i[r][PMPGranularity+2]`) not to be part of the range address in NAPOT mode. This is correct when `PMPGranularity == 0`, since then NA4 mode must be selected if the range address uses all bits, but it is incorrect when `PMPGranularity > 0`, since then it is legal in NAPOT mode to have a range address span the entire granule, with the next-lowest bit (i.e. `csr_pmp_addr_i[r][PMPGranularity+1]`) cleared to indicate that all higher bits are part of the range address.\r\n\r\nFor instance with `PMPGranularity == 28`, the granule covers bits `csr_pmp_addr_i[r][33:30]`, yet bit `csr_pmp_addr_i[r][29]` must also be considered to check whether a range address spans all 4 bits of the granule. A range address of `csr_pmp_addr_i[r] == 34'b00_0101_1111_1111_1111_1111_1111_1111_1111` could be used to specify a range from 1 GiB to 2 GiB for example and in that case the region address mask should be `region_addr_mask [r] == 4'b1111` (i.e. the entire granule). However, since only bits `csr_pmp_addr_i[r][33:30]` are currently considered when generating the mask, it is incorrectly set to `region_addr_mask [r] == 4'b1100`.\r\n\r\nThe specification states that bits `G-2:0` (i.e. bits `csr_pmp_addr_i[r][PMPGranularity:0]`) are implicitly set to all ones and hence do not need to be considered, but that implies that bit `G-1` (i.e. `csr_pmp_addr_i[r][PMPGranularity+1]`) is still used to specify the range:\r\n\r\n> When G≥1, the NA4 mode is not selectable. When G≥2 and pmpcfgi.A[1] is set, i.e. the mode is NAPOT, then bits pmpaddri[G-2:0] read as all ones.\r\n> -- [Volume II: RISC-V Privileged Architectures V20190608-Priv-MSU-Ratified, Sect. 3.6.1](https://github.com/riscv/riscv-isa-manual/releases/download/Ratified-IMFDQC-and-Priv-v1.11/riscv-privileged-20190608.pdf)"}
+{"org": "lowRISC", "repo": "ibex", "number": 1177, "state": "closed", "title": "[dv/uvm] Fix ecall / irq race condition", "body": "If an irq is driven on the same cycle as the end of test ecall\r\ninstruction, the irq checks can fail since the ecall will have modified\r\nexpected csr values. This fix just abandons the irq sequence if the\r\necall has already happened.\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 1174, "state": "closed", "title": "[DV] SV disable fork label - Xcelium simulator differences", "body": "While running and debugging Ibex regression we came across some differences in how Cadence Xcelium simulates disable of fork labels. \r\nWe've locally fixed this issue in 6 different testbench files and we can submit the change requests ourselves,\r\nI wanted to raise an issue on this as it is something that needs to be monitored in the future. \r\nI am not sure if the testbench code is linted, but is it possible to lint for the disable label construct and flag it in future? \r\n\r\nBelow is a summary of the issue we've found, we will follow up with the changes to the Ibex git repo this week. \r\n\r\n**Issue: Disabling a fork process by label name.** \r\nCadence support site recommends that when a fork is to be disabled it is to be disabled using the \"disable fork\" statement and not the \"disable fork_process_label\" construct, \r\nthe reason being that the \"disable fork_process_label\" construct for forks is not defined in the IEEE Std 1800-2017 LRM. See section 9.6.2 of the LRM (2017). \r\nAs far as we have seen Cadence Xcelium will ignore a \"disable fork_process_label\" line and continue, thereby leaving the process running and altering the function of the testcase. \r\nThis cause multiple test failures in a Ibex Xcelium regression and lead to particular problems with the riscv_reset_test. \r\n\r\nSo for example in the following Ibex code in core_ibex_test_lib.sv: The \"**disable imem_fork**\" should be replaced with \"**disable fork**\" in order to be compatible with Cadence Xcelium. \r\nWe have done very limited testing on these changes on EDA playground for Cadence Xcelium 19.09, Mentor Questa 2020.1, and Synopsys VCS 2019.06 and the \"disable fork\" code seem executes correctly for all these simulators. \r\n\r\n fork : imem_fork\r\n begin\r\n check_next_core_status(HANDLING_EXCEPTION, \"Core did not jump to exception handler\");\r\n check_priv_mode(PRIV_LVL_M);\r\n latched_imem_err = 1'b1;\r\n `uvm_info(`gfn, $sformatf(\"latched_imem_err: 0x%0x\", latched_imem_err), UVM_LOW)\r\n end\r\n begin\r\n clk_vif.wait_clks(750);\r\n end\r\n join_any\r\n **disable fork; // (Changed from: disable imem_fork;)** \r\n\r\nCadence support ticket referencing the above issue (NOTE: you will need a Cadence support account to view these): \r\n\r\nhttps://support.cadence.com/apex/ArticleAttachmentPortal?id=a1Od0000000syTQEAY&pageName=ArticleContent\r\n\r\nOther Cadence support issues that deal with fork-join disable behaviour: \r\n\r\nhttps://support.cadence.com/apex/ArticleAttachmentPortal?id=a1O0V000006DeTOUA0&pageName=ArticleContent \r\n\r\nhttps://support.cadence.com/apex/ArticleAttachmentPortal?id=a1Od0000000uSMiEAM&pageName=ArticleContent"}
+{"org": "lowRISC", "repo": "ibex", "number": 1167, "state": "closed", "title": "riscv_debug_single_step_test fail ", "body": "Hi ,\r\nwhen SEED=27754, IBEX_CONFIG=small, ISS=ovpsim, riscv_debug_single_step_test fail because dpc record the branch target address when core executes a branch instruction, but the test bench think the dpc of the core should record the address of the branch instruction address +4, I think the RTL is right, please help double check it.\r\n\r\n\r\nThanks,\r\nLihua"}
+{"org": "lowRISC", "repo": "ibex", "number": 1159, "state": "closed", "title": "[DV] Failing regression at riscv_debug_basic_test.0 for experimental-maxperf-pmp-bmfull", "body": "* Config: experimental-maxperf-pmp-bmfull\r\n* Test: riscv_debug_basic_test\r\n* Seed: 11904\r\n* Message: No dret detected, or incorrect privilege mode switch in timeout period of 100000 cycles\r\n\r\n\r\nSee https://dev.azure.com/lowrisc/lowrisc-private/_build/results?buildId=25194&view=results for full logs (you can find the artifacts under the \"Related\" heading on that page where it says \"1 published\").\r\n\r\nThe test log says:\r\n\r\n```\r\nTest binary: out/seed-11904/instr_gen/asm_tests/riscv_rand_instr_test.0.o\r\nibex uvm log : out/seed-11904/rtl_sim/riscv_rand_instr_test.0/sim.log\r\nriscv_rand_instr_test : [PASSED]\r\n\r\nibex : out/seed-11904/rtl_sim/riscv_rand_instr_test.0/trace_core_00000000.csv\r\nspike : out/seed-11904/instr_gen/spike_sim/riscv_rand_instr_test.0.csv\r\n[PASSED]: 694 matched\r\n\r\nTest binary: out/seed-11904/instr_gen/asm_tests/riscv_debug_basic_test.0.o\r\nibex uvm log : out/seed-11904/rtl_sim/riscv_debug_basic_test.0/sim.log\r\nriscv_debug_basic_test : [FAILED]\r\n\r\nTest binary: out/seed-11904/instr_gen/asm_tests/riscv_multiple_interrupt_test.0.o\r\nibex uvm log : out/seed-11904/rtl_sim/riscv_multiple_interrupt_test.0/sim.log\r\nriscv_multiple_interrupt_test : [PASSED]\r\n\r\nibex : out/seed-11904/rtl_sim/riscv_multiple_interrupt_test.0/trace_core_00000000.csv\r\nspike : out/seed-11904/instr_gen/spike_sim/riscv_multiple_interrupt_test.0.csv\r\n[PASSED]: 0 matched\r\n\r\n2 PASSED, 1 FAILED\r\n```\r\n\r\nsim.log says:\r\n```\r\nucli% run\r\nUVM_INFO @ 0: reporter [RNTST] Running test core_ibex_debug_intr_basic_test...\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_base_test.sv(111) @ 202500: uvm_test_top [uvm_test_top] Running test : out/seed-11904/instr_gen/asm_tests/riscv_debug_basic_test_0.bin\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_response_seq_lib.sv(28) @ 202500: uvm_test_top.env.instr_if_response_agent.sequencer@@instr_intf_seq [uvm_test_top.env.instr_if_response_agent.sequencer.instr_intf_seq] is_dmem_seq: 0x0\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/common/ibex_mem_intf_agent/ibex_mem_intf_response_seq_lib.sv(28) @ 202500: uvm_test_top.env.data_if_response_agent.sequencer@@data_intf_seq [uvm_test_top.env.data_if_response_agent.sequencer.data_intf_seq] is_dmem_seq: 0x1\r\ncore_ibex_tb_top.dut.u_ibex_tracer.printbuffer_dumpline.unnamed$$_0: Writing execution trace to out/seed-11904/rtl_sim/riscv_debug_basic_test.0/trace_core_00000000.log\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_seq_lib.sv(39) @ 4126500: reporter@@debug_seq_stress_h [debug_seq_stress_h] Starting sequence...\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_seq_lib.sv(60) @ 2163400500: reporter@@debug_seq_stress_h [debug_seq_stress_h] Stopping sequence\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_seq_lib.sv(51) @ 2163870500: reporter@@debug_seq_stress_h [debug_seq_stress_h] Exiting sequence\r\nUVM_INFO /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_base_test.sv(127) @ 2163870500: uvm_test_top [uvm_test_top] ECALL instruction is detected, test done\r\nUVM_FATAL /azp/agent/_work/1/s/dv/uvm/core_ibex/tests/core_ibex_test_lib.sv(346) @ 2364258500: uvm_test_top [uvm_test_top] No dret detected, or incorrect privilege mode switch in timeout period of 100000 cycles\r\n```\r\n\r\n@udinator would you mind having a look if we just need to increase the timeout in this test, or if there's something going wrong?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1158, "state": "closed", "title": "Unexpected behavior when OUTPUT=sim", "body": "Hello @rswarbrick ,\r\n\r\nBellow command leads to a repetitive (redundant) operation because of having \"sim\" as the output directory (this will be fixed by simply changing the directory name to something else, say SIM). The unexpected behavior is that I think since 'sim' is the main target in the Makefile of `dv/uvm/core_ibex`, it repeats the whole process (program generation/compilation/execution) under a new random seed because it detects a change in COMPILE_OPTS. \r\n\r\nCommand: \r\n`make -C dv/uvm/core_ibex/ COV=1 TIMEOUT=10000 ISA=rv32imc ISS=spike SIMULATOR=vcs WAVES=0 TESTLIST=/path/to/testlist OUT=sim`\r\n\r\nConsole output:\r\nmake: Entering directory '/dv/uvm/core_ibex'\r\nmkdir -p sim/seed-20667/.metadata\r\nFri, 30 Oct 2020 02:46:59 INFO Creating output directory: sim/seed-20667/instr_gen\r\nFri, 30 Oct 2020 02:46:59 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:46:59 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:46:59 INFO Processing simulator setup file : vendor/google_riscv-dv/yaml/simulator.yaml\r\nFri, 30 Oct 2020 02:46:59 INFO Found matching simulator: vcs\r\nFri, 30 Oct 2020 02:46:59 INFO Building RISC-V instruction generator\r\nFri, 30 Oct 2020 02:47:32 INFO Running RISC-V instruction generator\r\nFri, 30 Oct 2020 02:47:32 INFO Generating 1 riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:47:32 INFO Running riscv_rand_instr_test with 1 batches\r\nFri, 30 Oct 2020 02:47:32 INFO Running riscv_rand_instr_test, batch 1/1, test_cnt:1\r\nFri, 30 Oct 2020 02:47:36 INFO Creating output directory: sim/seed-20667/instr_gen\r\nFri, 30 Oct 2020 02:47:36 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:47:36 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:47:36 INFO Compiling sim/seed-20667/instr_gen/asm_tests/riscv_rand_instr_test_0.S\r\nFri, 30 Oct 2020 02:47:36 INFO Converting to sim/seed-20667/instr_gen/asm_tests/riscv_rand_instr_test_0.bin\r\nFri, 30 Oct 2020 02:47:36 INFO Creating output directory: sim/seed-20667/instr_gen\r\nFri, 30 Oct 2020 02:47:36 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:47:36 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:47:36 INFO Processing ISS setup file : vendor/google_riscv-dv/yaml/iss.yaml\r\nFri, 30 Oct 2020 02:47:36 INFO Found matching ISS: spike\r\nFri, 30 Oct 2020 02:47:36 INFO spike sim log dir: sim/seed-20667/instr_gen/spike_sim\r\nFri, 30 Oct 2020 02:47:36 INFO Running spike sim: sim/seed-20667/instr_gen/asm_tests/riscv_rand_instr_test_0.o\r\nmkdir -p sim/rtl_sim\r\nFri, 30 Oct 2020 02:47:36 INFO Processing simulator setup file : yaml/rtl_simulation.yaml\r\nFri, 30 Oct 2020 02:47:36 INFO Compiling TB\r\nrm -rf sim/seed-20667/rtl_sim\r\ncp -r sim/rtl_sim sim/seed-20667\r\nFri, 30 Oct 2020 02:48:02 INFO Processing simulator setup file : yaml/rtl_simulation.yaml\r\nFri, 30 Oct 2020 02:48:03 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:03 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:48:03 INFO Running RTL simulation...\r\nFri, 30 Oct 2020 02:48:03 INFO Running core_ibex_base_test with sim/seed-20667/instr_gen/asm_tests/riscv_rand_instr_test_0.bin\r\nFri, 30 Oct 2020 02:48:07 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:07 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:48:07 INFO Comparing spike/DUT sim result : sim/seed-20667/instr_gen/asm_tests/riscv_rand_instr_test.0.o\r\nFri, 30 Oct 2020 02:48:07 INFO Processing ibex log : sim/seed-20667/rtl_sim/riscv_rand_instr_test.0/trace_core_00000000.log\r\nFri, 30 Oct 2020 02:48:07 INFO Processed instruction count : 193\r\nFri, 30 Oct 2020 02:48:07 INFO CSV saved to : sim/seed-20667/rtl_sim/riscv_rand_instr_test.0/trace_core_00000000.csv\r\nFri, 30 Oct 2020 02:48:07 INFO Processing spike log : sim/seed-20667/instr_gen/spike_sim/riscv_rand_instr_test.0.log\r\nFri, 30 Oct 2020 02:48:07 INFO Processed instruction count : 195\r\nFri, 30 Oct 2020 02:48:07 INFO CSV saved to : sim/seed-20667/instr_gen/spike_sim/riscv_rand_instr_test.0.csv\r\nFri, 30 Oct 2020 02:48:07 INFO 1 PASSED, 0 FAILED\r\nFri, 30 Oct 2020 02:48:07 INFO RTL & ISS regression report at sim/seed-20667/regr.log\r\nFri, 30 Oct 2020 02:48:07 INFO Searching sim/seed-20667 for coverage database\r\nFri, 30 Oct 2020 02:48:07 INFO Generating merged coverage directory\r\n**_mkdir -p sim\r\nRepeating compiling TB because variable COMPILE_OPTS has changed value._**\r\nmkdir -p sim/seed-14582/.metadata\r\nFri, 30 Oct 2020 02:48:12 INFO Creating output directory: sim/seed-14582/instr_gen\r\nFri, 30 Oct 2020 02:48:12 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:12 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:48:12 INFO Processing simulator setup file : vendor/google_riscv-dv/yaml/simulator.yaml\r\nFri, 30 Oct 2020 02:48:12 INFO Found matching simulator: vcs\r\nFri, 30 Oct 2020 02:48:12 INFO Building RISC-V instruction generator\r\nFri, 30 Oct 2020 02:48:43 INFO Running RISC-V instruction generator\r\nFri, 30 Oct 2020 02:48:43 INFO Generating 1 riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:43 INFO Running riscv_rand_instr_test with 1 batches\r\nFri, 30 Oct 2020 02:48:43 INFO Running riscv_rand_instr_test, batch 1/1, test_cnt:1\r\nFri, 30 Oct 2020 02:48:46 INFO Creating output directory: sim/seed-14582/instr_gen\r\nFri, 30 Oct 2020 02:48:46 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:46 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:48:46 INFO Compiling sim/seed-14582/instr_gen/asm_tests/riscv_rand_instr_test_0.S\r\nFri, 30 Oct 2020 02:48:46 INFO Converting to sim/seed-14582/instr_gen/asm_tests/riscv_rand_instr_test_0.bin\r\nFri, 30 Oct 2020 02:48:46 INFO Creating output directory: sim/seed-14582/instr_gen\r\nFri, 30 Oct 2020 02:48:46 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:48:46 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:48:46 INFO Processing ISS setup file : vendor/google_riscv-dv/yaml/iss.yaml\r\nFri, 30 Oct 2020 02:48:46 INFO Found matching ISS: spike\r\nFri, 30 Oct 2020 02:48:46 INFO spike sim log dir: sim/seed-14582/instr_gen/spike_sim\r\nFri, 30 Oct 2020 02:48:46 INFO Running spike sim: sim/seed-14582/instr_gen/asm_tests/riscv_rand_instr_test_0.o\r\nFri, 30 Oct 2020 02:48:47 INFO Processing simulator setup file : yaml/rtl_simulation.yaml\r\nFri, 30 Oct 2020 02:48:47 INFO Compiling TB\r\nrm -rf sim/seed-14582/rtl_sim\r\ncp -r sim/rtl_sim sim/seed-14582\r\nFri, 30 Oct 2020 02:49:10 INFO Processing simulator setup file : yaml/rtl_simulation.yaml\r\nFri, 30 Oct 2020 02:49:10 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:49:10 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:49:10 INFO Running RTL simulation...\r\nFri, 30 Oct 2020 02:49:10 INFO Running core_ibex_base_test with sim/seed-14582/instr_gen/asm_tests/riscv_rand_instr_test_0.bin\r\nFri, 30 Oct 2020 02:49:15 INFO Processing regression test list : vendor/google_riscv-dv/yaml/base_testlist_single.yaml, test: riscv_rand_instr_test\r\nFri, 30 Oct 2020 02:49:15 INFO Found matched tests: riscv_rand_instr_test, iterations:1\r\nFri, 30 Oct 2020 02:49:15 INFO Comparing spike/DUT sim result : sim/seed-14582/instr_gen/asm_tests/riscv_rand_instr_test.0.o\r\nFri, 30 Oct 2020 02:49:15 INFO Processing ibex log : sim/seed-14582/rtl_sim/riscv_rand_instr_test.0/trace_core_00000000.log\r\nFri, 30 Oct 2020 02:49:15 INFO Processed instruction count : 195\r\nFri, 30 Oct 2020 02:49:15 INFO CSV saved to : sim/seed-14582/rtl_sim/riscv_rand_instr_test.0/trace_core_00000000.csv\r\nFri, 30 Oct 2020 02:49:15 INFO Processing spike log : sim/seed-14582/instr_gen/spike_sim/riscv_rand_instr_test.0.log\r\nFri, 30 Oct 2020 02:49:15 INFO Processed instruction count : 197\r\nFri, 30 Oct 2020 02:49:15 INFO CSV saved to : sim/seed-14582/instr_gen/spike_sim/riscv_rand_instr_test.0.csv\r\nFri, 30 Oct 2020 02:49:15 INFO 1 PASSED, 0 FAILED\r\nFri, 30 Oct 2020 02:49:15 INFO RTL & ISS regression report at sim/seed-14582/regr.log\r\nFri, 30 Oct 2020 02:49:15 INFO Searching sim/seed-14582 for coverage database\r\nFri, 30 Oct 2020 02:49:15 INFO Searching sim/seed-20667 for coverage database\r\nFri, 30 Oct 2020 02:49:15 INFO Generating merged coverage directory\r\nmkdir -p sim\r\nmake: Leaving directory 'dv/uvm/core_ibex'\r\n\r\nThanks,\r\nHodjat"}
+{"org": "lowRISC", "repo": "ibex", "number": 1154, "state": "closed", "title": "[dv] Regression failure for riscv_multiple_interrupt_test with config experimental-branch-predictor", "body": "* Seed: 3116\r\n* `make -C dv/uvm/core_ibex ITERATIONS=1 TEST=riscv_rand_instr_test,riscv_multiple_interrupt_test,riscv_debug_basic_test ISS=spike IBEX_CONFIG=experimental-branch-predictor`\r\n* CI run: https://dev.azure.com/lowrisc/lowrisc-private/_build/results?buildId=24876&view=logs&j=89b1484e-e59b-56b8-bef8-ec534b74be7c&t=69a04726-f3d2-5f59-d3f4-a33300a2ed9f\r\n* Full build log in CI: https://artproduks1.artifacts.visualstudio.com/Ace3fc167-bb91-4c33-a65a-ae648df7f974/4efdbdf8-a184-4518-9864-57d2a49c2aed/_apis/artifact/cGlwZWxpbmVhcnRpZmFjdDovL2xvd3Jpc2MvcHJvamVjdElkLzRlZmRiZGY4LWExODQtNDUxOC05ODY0LTU3ZDJhNDljMmFlZC9idWlsZElkLzI0ODc2L2FydGlmYWN0TmFtZS9vdXQ1/content?format=file&subPath=%2Fout.tar.xz\r\n\r\n```\r\nTue, 27 Oct 2020 15:01:21 ERROR Timeout[300s]: env SIM_DIR=out/seed-3116/rtl_sim/riscv_multiple_interrupt_test.0 out/seed-3116/rtl_sim/vcs_simv +vcs+lic+wait +signature_addr=8ffffffc -ucli -do ./vcs.tcl +ntb_random_seed=3116 +UVM_TESTNAME=core_ibex_debug_intr_basic_test +bin=out/seed-3116/instr_gen/asm_tests/riscv_multiple_interrupt_test_0.bin +ibex_tracer_file_base=out/seed-3116/rtl_sim/riscv_multiple_interrupt_test.0/trace_core -l out/seed-3116/rtl_sim/riscv_multiple_interrupt_test.0/sim.log +require_signature_addr=1 +enable_irq_multiple_seq=1 \r\n```\r\n\r\n@udinator @GregAC is this something you can have a look at? The logs should contain all necessary information."}
+{"org": "lowRISC", "repo": "ibex", "number": 1134, "state": "closed", "title": "Access rights - Illegal Write to Read Only Field - DCSR's cause", "body": "#### RISC-V Specification\r\n\r\n> External Debug Support [4.8.1]\r\n\r\n#### Issue Description\r\n\r\nA read only field of `dcsr` is written. \r\n\r\n#### Steps to Reproduce\r\n\r\nAs shown below, while in debug mode, the instruction `csrrwi x17, dcsr, 0x4` updates the value of the `cause` field of `dcsr`, which has a read only access right.\r\n\r\n\r\n\r\n---\r\nProduct: OneSpin 360 DV-Verify\r\nApp: Processor Verification App\r\nTool's version: 2020.2.0"}
+{"org": "lowRISC", "repo": "ibex", "number": 1132, "state": "open", "title": "Illegal Instruction Retires", "body": "#### RISC-V Specification\r\n\r\n> 3.1.11: \"The minstret CSR counts the number of instructions the hart has retired. The mcycle and minstret registers\r\nhave 64-bit precision on all RV32 and RV64 systems.\r\n\r\n> The counter registers have an arbitrary value after system reset, and can be written with a given value. Any CSR write takes effect after the writing instruction has otherwise completed.\"\r\n\r\n> The counter-inhibit register mcountinhibit is a 32-bit WARL register that controls which of the hardware performance-monitoring counters increment. The settings in this register only control whether the counters increment; their accessibility is not affected by the setting of this register.\r\n\r\n> When the CY, IR, or HPMn bit in the mcountinhibit register is clear, the cycle, instret, or hpmcountern register increments as usual. When the CY, IR, or HPMn bit is set, the corresponding counter does not increment.\r\n\r\n#### Issue Description\r\nAn illegal instruction increments the minstret counter as if it was a legal one.\r\n\r\n#### Steps to Reproduce\r\n\r\nAs shown below, the minstret counter is incremented for the illegal instruction csrrw x8, 0x010, x3, knowing that IR bit of mcountinhibit is set to '0 and thus allowing for the minstret to be incremented. \r\n\r\n\r\n\r\n---\r\nProduct: OneSpin 360 DV-Verify\r\nApp: Processor Verification App\r\nTool's version: 2020.2.0"}
+{"org": "lowRISC", "repo": "ibex", "number": 1129, "state": "closed", "title": "Illegal Instruction Exception not Raised", "body": "**RISC-V Specification:**\r\n\r\n> Unprivileged ISA\r\n\r\n**Issue Description:**\r\n\r\nAn illegal instruction updates the register file and the associated csrs and executes normally without raising an illegal instruction exception.\r\n\r\n**Example:**\r\n\r\nThe instruction 32'h2820d013 is decoded and executed with no illegal instruction exception being flagged, as machine csrs: mepc, mstatus and mcause aren't updated. \r\n\r\n\r\n\r\n---\r\n\r\nProduct: OneSpin 360 DV-Verify\r\nApp: Processor Verification App\r\nTool's version: 2020.2.0"}
+{"org": "lowRISC", "repo": "ibex", "number": 1119, "state": "closed", "title": "Restructure documentation", "body": "Restructure the existing documentation to group the content by intended\naudience. This produces four sections:\n\n* An introduction section, relevant to \"newcomers\" to Ibex.\n* An user guide, intended for hardware designers (integrators) and\n software developers who want to integrate Ibex, and develop software\n for it.\n* A reference guide, which provides background information on the\n design. This section is essential when working on Ibex, and also\n documents our design decisions.\n* A developer guide aimed at people modifying Ibex itself. It consists\n mostly of process and tool documentation: how to run the verification\n after a code change, how to use GitHub, etc.\n\nThis commit is large, but text is mostly unchanged. A couple of\nintroductions and tables of content were added, but no significant\nchanges to the text have been made. These will be done in follow-ups."}
+{"org": "lowRISC", "repo": "ibex", "number": 1117, "state": "closed", "title": "[rtl] Double fault handling", "body": "Consider the case where an exception occurs on the first instruction of an exception handler (e.g. due to a bus fault or PMP access fault), what should happen?\r\n\r\nI suspect Ibex currently enters some kind of infinite loop or deadlocks.\r\n\r\nWe need to define and document a sensible behaviour here.\r\n\r\nI would suggest some kind of double fault detection that causes the core to halt and assert a top-level signal e.g. `double_fault_o`. System implementers are then left with the choice of what to do (e.g. immediately reset the core). I don't think Ibex should perform a reset itself, simply halt and let the system decide what to do."}
+{"org": "lowRISC", "repo": "ibex", "number": 1106, "state": "closed", "title": "The step operation is error when the SW bp is set in a J instruction.", "body": "Hi Guys: \r\n I use the Ibex core running a simple test C code. \r\n I set a SW bp before a “jump” instruction, when the cpu fetched the SW bp instruction, the cpu is halted. \r\n But after that, i use the “step\" cmd in telnet, the PC in CPU is wrong, it's not the correct PC which the JUMP instruction expected , the dpc has been changed. \r\n When I use the HW bp, the dpc has‘t been changed.\r\n So, i think this is a bug\r\n please see the following figure.\r\n \r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1105, "state": "closed", "title": "Update fetch_enable signal", "body": "We have a requirement from OpenTitan to be able to block the CPU from executing at certain points. I propose we update the existing fetch_enable signal to do that, since it's current behavior is a bit confusing and probably not that useful."}
+{"org": "lowRISC", "repo": "ibex", "number": 1101, "state": "closed", "title": "Failing randomization in ibex_icache_stress_all", "body": "Hey!\r\nI have problem with randomization in test `ibex_icache_stress_all` in file `ibex_icache_core_base_seq.sv`:\r\n```\r\n `DV_CHECK_RANDOMIZE_WITH_FATAL(\r\n req,\r\n\r\n // Force a branch if necessary\r\n force_branch -> req.trans_type == ICacheCoreTransTypeBranch;\r\n\r\n // If this is a branch and constrain_branches is true then constrain any branch target.\r\n (constrain_branches && (req.trans_type == ICacheCoreTransTypeBranch)) ->\r\n req.branch_addr inside {[base_addr:top_restricted_addr]};\r\n\r\n // If this is a branch and constrain_branches is false, we don't constrain the branch target,\r\n // but we do weight the bottom and top of the address space a bit higher. This is a weaker\r\n // version of the weighting that we place on base_addr.\r\n (!constrain_branches && (req.trans_type == ICacheCoreTransTypeBranch)) ->\r\n req.branch_addr dist { [0:63] :/ 1,\r\n [64:32'hffffffbf] :/ 20,\r\n [32'hffffffc0:32'hffffffff] :/ 1 };\r\n\r\n // If this is a branch and constrain_branches is true, we can ask for up to 100 instructions\r\n // (independent of insns_since_branch)\r\n (constrain_branches && (req.trans_type == ICacheCoreTransTypeBranch)) ->\r\n num_insns <= 100;\r\n\r\n // If this isn't a branch and constrain_branches is true, we can ask for up to 100 -\r\n // insns_since_branch instructions. This will be positive because of the check above.\r\n (constrain_branches && (req.trans_type != ICacheCoreTransTypeBranch)) ->\r\n num_insns <= 100 - insns_since_branch;\r\n\r\n const_enable -> enable == cache_enabled;\r\n\r\n // Toggle the cache enable line one time in 50. This should allow us a reasonable amount of\r\n // time in each mode (note that each transaction here results in multiple instruction\r\n // fetches)\r\n enable dist { cache_enabled :/ gap_between_toggle_enable, ~cache_enabled :/ 1 };\r\n\r\n // If must_invalidate is set, we have to invalidate with this item.\r\n must_invalidate -> invalidate == 1'b1;\r\n\r\n // If no_invalidate is set, we shouldn't ever touch the invalidate line, unless\r\n // must_invalidate is set (which will only apply once).\r\n (no_invalidate && !must_invalidate) -> invalidate == 1'b0;\r\n\r\n // Start an invalidation every 1+gap_between_invalidations items.\r\n invalidate dist { 1'b0 :/ gap_between_invalidations, 1'b1 :/ 1 };\r\n\r\n // If we have seen a new seed since the last invalidation (which must have happened while the\r\n // cache was disabled) and this item is enabled, force the cache to invalidate.\r\n stale_seed && enable -> invalidate == 1'b1;\r\n\r\n )\r\n```\r\nproblem is with this constraint, I think better way to do this will be change line:\r\n`stale_seed && enable -> invalidate == 1'b1;` to `!(no_invalidate && !must_invalidate) && stale_seed && enable -> invalidate == 1'b1;`\r\nIn this way we are sure that this constrain won't be overconstrained "}
+{"org": "lowRISC", "repo": "ibex", "number": 1095, "state": "closed", "title": "[rtl] PC mismatch alarm caused by dummy instruction insertion", "body": "Hi,\r\n\r\nThe PC mismatch alarm fires when a dummy instruction is inserted.\r\n\r\nconditions:\r\n\r\n- parameter bit SecureIbex = 1'b1,\r\n- Bit 2 of cpuctrl register (dummy_instr_en) is set\r\n\r\n\r\n\r\nMay I suggest following change in ibex_if_stage.sv : \r\n\r\n // Check that the address equals the previous address +2/+4\r\n assign pc_mismatch_alert_o = prev_instr_seq_q & (pc_if_o != prev_instr_addr_incr) **& ~dummy_instr_id_o**;"}
+{"org": "lowRISC", "repo": "ibex", "number": 1094, "state": "closed", "title": "[rtl] PC mismatch alarm caused by an instruction bus error", "body": "Hi,\r\n\r\nThe PC mismatch alarm fires on an instruction bus error. \r\n\r\nconditions: \r\n- parameter bit SecureIbex = 1'b1\r\n- A bus error is generated by the system, instr_err_i = 1'b1\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1092, "state": "closed", "title": "Possible Problem with Coremark on Simple System: Access to Uninitialized Memory ", "body": "Hi all, \r\n\r\nI may have run into a problem when simulating coremark on the simple system example.\r\n\r\nI have been trying to run the simulation with synopsys VCS (since I am using the same framework to benchmark another core, whose tracer is not supported by verilator), and have found that the simulation fails throwing illegal instruction exceptions after some time. I have compared the traces and found that the differences start an access to apparently uninitialized memory. Since verilator defaults unknown values to 0, it seems that there is no problem and the program continues to the end. However when simulating with VCS, the program starts deviating at some point and starts to offend a range of assert statements due to unknown signals.\r\nI can make the simulation run with VCS by padding the entire memory with 0. The results are then the same as with verilator. However, I am not sure if we should trust those results.\r\n\r\nYou can look into the trace logs here (large files):\r\nhttps://drive.google.com/drive/folders/16SJRj9_kDt-uGIyC2Aie4j6XNU0LWnH1?usp=sharing\r\n\r\nThe first occurance of an uninitialized memory access is at time 2402. \r\n\r\nThe Process I used for simulating with verilator: ( as specified in the readme).\r\n```\r\n#compile benchmark\r\nmake -C examples/sw/benchmark/coremark\r\n\r\n#build the simulation\r\nfusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system\r\n\r\n#run the simulation\r\n./build/lowrisc_ibex_ibex_simple_system_0/sim_verilator/Vibex_simple_system --meminit=ram,examples/sw/benchmark/coremark/coremark.elf\r\n```\r\n\r\nFor simulation with VCS:\r\n```\r\n#compile benchmark\r\nmake -C examples/sw/benchmark/coremark\r\n\r\n#create vmem\r\nriscv32-unknown-elf-objcopy -O binary examples/sw/coremark/coremark.elf examples/sw/coremark/coremark.bin\r\nsrec_cat examples/sw/coremark/coremark.bin --binary --offset 0x0000 --byte-swap 4 --fill 0xff -within examples/sw/coremark/coremark.bin -binary -range-pad 4 --output examples/sw/coremark/coremark.vmem --vmem 32\r\n\r\n#build the simulation\r\nfusesoc --cores-root=. run --target=sim --tool=vcs --setup --build lowrisc:ibex:ibex_simple_system --SRAMInitFile=examples/sw/coremark/coremark.vmem\r\n\r\n#run the simulation\r\n./build/lowrisc_ibex_ibex_simple_system_0/sim-vcs/lowrisc_ibex_ibex_simple_system_0\r\n```\r\nTo pad the memory with 0 I add `--pad-to=0x1fffff` to the `objcopy` command.\r\n\r\n "}
+{"org": "lowRISC", "repo": "ibex", "number": 1080, "state": "closed", "title": "[RTL] Illegal Instructions occur when dummy instructions are enabled and RV32M = 0", "body": "Bug conditions:\r\n- parameter bit RV32M = 1'b0,\r\n- parameter bit SecureIbex = 1'b1,\r\n- Bit 2 of cpuctrl register (dummy_instr_en) is set \r\n\r\nDescription:\r\nWhen a dummy instruction is executed, an illegal opcode is set when the dummy instruction opcode corresponds to a MUL or DIV.\r\n\r\nI would recommend to remove MUL and DIV from dummy opcodes.\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1070, "state": "closed", "title": "Add more HW breakpoints", "body": "Support for additional HW breakpoints would make software debug easier / more flexible"}
+{"org": "lowRISC", "repo": "ibex", "number": 1050, "state": "closed", "title": "[dv/ibex] Update CSR listings", "body": "This PR updates the `implemented_csr` list in `riscv_core_setting.sv`\r\nand adds the two custom CSRs `cpuctrl` and `secureseed` to the\r\n`custom_csr` list. Both are for use by the riscv-dv generator.\r\n\r\nThis PR can only be merged after #1049 , which vendors in some updates to riscv-dv,\r\nincluding basic support for custom CSRs.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 1049, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@3cf691d", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 3cf691dcb96f2cd72250690216b60f2b0c0ac804\r\n\r\n* remove hardcoded CSR names (Udi Jonnalagadda)\r\n* initial custom CSR support (Udi Jonnalagadda)\r\n* Add support for segmented load/store instructions (google/riscv-\r\n dv#656) (taoliug)\r\n* fix post_randomize issue (aneels3)\r\n* add MAX_LMUL to rv32i config (google/riscv-dv#649) (udinator)\r\n* Ignore log and asm file (aneels3)\r\n* Add Command Line Support (aneels3)\r\n* support for command-line arguments (pvipsyash)\r\n* Reorder import statements (aneels3)\r\n* Modified function randomize_gpr in instr_stream file\r\n (ShraddhaDevaiya)\r\n* Updated riscv_instr_sequence file and modified other python files to\r\n get main block in asm file. (ShraddhaDevaiya)\r\n* Modify get_rand_instr() (aneels3)\r\n* added uvm_glob_to_re in uvm_re_match (Dawid Zimonczyk)\r\n* Aldec Riviera-PRO compiler command line arguments modified.\r\n (google/riscv-dv#638) (Dariusz Stachańczyk)\r\n* allow coverage compilation to be run on LSF (google/riscv-dv#637)\r\n (udinator)\r\n* Add CHIPS Alliance work group information to the README\r\n (google/riscv-dv#633) (taoliug)\r\n* Add indexed/strided vector load/store instrution stream\r\n (google/riscv-dv#632) (taoliug)\r\n* Add constraint for mtvec alignment in vectored interrupt mode\r\n (google/riscv-dv#631) (taoliug)\r\n* Add bitstring requirement to pygen/experimental README\r\n (google/riscv-dv#630) (taoliug)\r\n* Add unsupported load/store instruction filtering (google/riscv-\r\n dv#629) (taoliug)\r\n* Add different methods to initialize the vregs (google/riscv-dv#627)\r\n (Josep Sans)\r\n* Support a vetor instruction only mode (google/riscv-dv#626)\r\n (taoliug)\r\n* Add riscv_instr_stream.py file (aneels3)\r\n* Importing PyVSC module (google/riscv-dv#625) (Hodjat Asghari\r\n Esfeden)\r\n* update pygen_src files (google/riscv-dv#612) (BharathNR1030)\r\n* Fix typo (google/riscv-dv#624) (taoliug)\r\n* Fix B-ext instruction generation issue (google/riscv-dv#620)\r\n (taoliug)\r\n\r\nMust be merged before #1050.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 1048, "state": "closed", "title": "Fix comment or code in decoder regarding FENCE behavior", "body": "I just stumbled across this comment in the decoder:\r\n\r\nhttps://github.com/lowRISC/ibex/blob/94d505716870ddf240d0896021871176d6336579/rtl/ibex_decoder.sv#L538-L540\r\n\r\n@tomroberts-lowrisc Can you have a look at that behavior and (probably) update the comment to what we have today?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1044, "state": "closed", "title": "PMP TOR writes and behavior", "body": "1. There appears to be a functional difference between [spike](https://github.com/riscv/riscv-isa-sim/blob/67b7edd0270d5d074136eb45474477d15aeee725/riscv/processor.cc#L809) and [ibex](https://github.com/lowRISC/ibex/blob/d7c13aa9045838e7b9751e87b6b4630e7893db39/rtl/ibex_cs_registers.sv#L828) in the interaction between L and A=TOR; riscv/riscv-isa-manual#545 endorsed the spike interpretation.\r\n\r\n2. Should https://github.com/lowRISC/ibex/blob/master/rtl/ibex_pmp.sv#L92-L93 be generating both ends of the TOR range from the same pmpaddr?"}
+{"org": "lowRISC", "repo": "ibex", "number": 1038, "state": "closed", "title": "Sporadic failures in `riscv_illegal_instr_test`", "body": "@vogelpi and I have both seen some failures in the `riscv_illegal_instr_test`. I did look into some and I believe they're happening because when running with Spike as a simulator the 'F' extension and potential others are turned on. So illegal instruction for Ibex get executed on Spike and a trace mis-match results.\r\n\r\nWe should look into the failures in more detail and if my diagnosis is correct ensure Spike runs with the correct ISA."}
+{"org": "lowRISC", "repo": "ibex", "number": 1034, "state": "closed", "title": "[rtl] remove lsu_req_in_id signal", "body": "This signal aimed to ensure loads/stores completed succesfully when an\r\ninterrupt or debug request appeared at the same time they were being\r\nexecuted when the writeback stage is present. However other stall logic\r\nsuffices for this purpose (debug/interrupt will wait for instruction to\r\nunstall in ID/EX which only happens once request has been sent out, then\r\nfirst instruction of debug/interrupt handler will stall until load/store\r\nresponse has been seen based on the generic stall logic for lsu requests\r\nin the writeback stage).\r\n\r\nWith this signal in place debug single stepping was broken around loads\r\nand stores.\r\n\r\nFixes #1029\r\n\r\nThis half undoes the fix from this PR: https://github.com/lowRISC/ibex/pull/928 which was in response to this OT issue: https://github.com/lowRISC/opentitan/issues/2405\r\n\r\nI'm happy to accept this is not the correct fix but I did have a play with interrupts appearing the same cycle as a load in simple system with various delays on gnt/rvalid and it all seems to work fine. The DV interrupt tests all looked fine. The test in OT that found the original bug was broken on main yesterday (chip_uart_tx_rx) but looking at the latest nightly it seems to be fixed, so I'll have another play with that. Also realised there's some other timing scenarios I can check out with simple system.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 1029, "state": "closed", "title": "Single stepping over `lw` doesn't cause a jump back to Debug Mode", "body": "Hi all,\r\nI'm seeing something interesting occur when I run `riscv_debug_single_step_test` on Ibex in the `experimental-maxperf-pmp-bmfull` configuration.\r\n\r\nIn the waveform, Ibex has just finished single stepping over the instruction at `pc_id=0x8000_b25e`, and has just executed the `dret` indicating the end of the debug rom at `pc_id=0x8000_b7ca` (`debug_single_step_i` in the controller is still high, so I am expecting Ibex to execute the next instruction it sees and re-enter debug mode).\r\nIbex correctly returns to execute the instruction at `pc_id=0x8000_b262`, which is a `lw` instruction, and the controller raises `enter_debug_mode` accordingly as the core stalls to allow the memory transaction to finish. However after the load transaction has cleared (the cycle before marker `M1`), `enter_debug_mode` drops to 0 as `instr_valid_i` suddenly drops to 0. \r\nThis causes the core to incorrectly execute the next instruction (`pc_id=0x8000_b266`) and step into debug mode only after this instruction has passed through the ID stage (at marker `M2`) - Ibex should have stepped into debug mode after `pc_id=0x8000_b262`."}
+{"org": "lowRISC", "repo": "ibex", "number": 1019, "state": "closed", "title": "We should list the (non-Python) requirements to build/run Ibex examples", "body": "The simplest thing would be to hoist the list of Ubuntu packages currently installed by `azure-pipelines.yml`. Maybe better would be a file with dependencies for the various things you might want to do (verilate simple_system? synthesize with yosys?), which could be picked up by documentation and the Azure pipeline."}
+{"org": "lowRISC", "repo": "ibex", "number": 1018, "state": "closed", "title": "Illegal Instruction Exception not Raised - Shift Instructions", "body": "**RISC-V Specification:**\r\n\r\n- _\"Chapter 2.4 of Unprivileged ISA\"_\r\n\r\n**Issue Description:**\r\n\r\nAn illegal instruction updates the register file and the associated csrs and executes normally without raising an illegal instruction exception.\r\n\r\n**Example:**\r\n\r\nThe instruction 32'h02005913 is decoded at time point t##0 with no illegal instruction being flagged, as illegal_insn_did is de-asserted.\r\n\r\n\r\n\r\n---\r\n\r\nProduct: OneSpin 360 DV-Verify\r\nApp: RVV\r\nTool's version: 2020.1.3"}
+{"org": "lowRISC", "repo": "ibex", "number": 993, "state": "closed", "title": "Hook up real Gift cipher core", "body": "I hook up real gift cipher core. Currently there are some line errors in the gift module, but I will fix it in another PR."}
+{"org": "lowRISC", "repo": "ibex", "number": 985, "state": "open", "title": "[DV] Remove all copies of OpenTitan files except when vendored in", "body": "We are vendoring in Ibex into OT, and we need to avoid files being duplicated, or core files in Ibex overriding ones in OT.\r\n\r\nGeneral rules:\r\n- If code from OT is needed, it *must be* vendored in.\r\n- If code is not vendored in, it *may not* use the same `name` in the core file, and ideally also not the same file names.\r\n\r\nOne example we know of right now is the mem_model at https://github.com/lowRISC/ibex/tree/master/dv/uvm/core_ibex/common/mem_model; there might be others.\r\n\r\nThis issue is to double-check all core files, and to ensure that the rules outlined hold."}
+{"org": "lowRISC", "repo": "ibex", "number": 983, "state": "closed", "title": "Debug single step test failure", "body": "The debug single step test (small config, seed 1) is currently failing with the following message:\r\n`DPC value [0x8000333e] is not the next instruction after ret_pc [0x8000b23a]`\r\nAs far as I can tell, the test is checking that DPC increments by 2 or 4 for every step taken. In this case, the instruction stepped over is a jump, and so the next PC does not equal the previous value - 2/4. The test is not expecting any jump/branch instructions to be generated, but there is one jump at the end (jump to test done) which it ends up stepping to, which causes the faliure."}
+{"org": "lowRISC", "repo": "ibex", "number": 980, "state": "closed", "title": "[top_pkg] Fix style lint warnings", "body": "This fixes several style lint warnings in Ibex. Note that the `top_pkg` from Ibex seems to override the `top_pkg` from OpenTitan (hence we get all these duplicate warnings about missing parameter types in https://reports.opentitan.org/hw/ip/rv_core_ibex/lint/veriblelint/latest/results.html). This is another instance of https://github.com/lowRISC/opentitan/issues/1231 and we should resolve this.\r\n\r\nSigned-off-by: Michael Schaffner "}
+{"org": "lowRISC", "repo": "ibex", "number": 966, "state": "closed", "title": "Docs: Mention B extension in overview page", "body": "We don't mention the B extension on https://ibex-core.readthedocs.io/en/latest/introduction.html yet, we should do so.\r\n\r\n@ganoam "}
+{"org": "lowRISC", "repo": "ibex", "number": 965, "state": "closed", "title": "[bitmanip] Optimizations and Parametrization", "body": "This commit contains some final optimizations regarding the bit\r\nmanipulation extension as well as the parametrization into a balanced\r\nversion and a full performance version.\r\n\r\nBalanced Version:\r\n * Supports ZBB, ZBS, ZBF and ZBT extensions\r\n * Dual cycle instructions:\r\n ror[i], rol, cmov, cmix fsl, fsr[i]\r\n * Everything else completes in a single cycle.\r\n\r\nFull Version:\r\n * Supports all 32b sub extensions.\r\n * Dual cycle instructions:\r\n ror[i], rol, cmov, cmix fsl, fsr[i], crc32[c], bext, bdep\r\n * Everything else completes in a single cycle.\r\n\r\nNotable Changes:\r\n * bext/bdep are now multi-cycle: Sharing additional register\r\n with multiplier module\r\n * grev/gorc instructions are implemented in separate structures\r\n rather than sharing the shifter or butterfly network.\r\n * Speed up decision on using rs1 or rs3 for alu_operand_a by\r\n introducing single-bit register, to identify ternary\r\n instructions in their first cycle.\r\n * Introduce enumerated parameter to chose bit manipulation\r\n implementation\r\n\r\nSigned-off-by: ganoam "}
+{"org": "lowRISC", "repo": "ibex", "number": 964, "state": "closed", "title": "Is parameter ICacheECC need to be passed by FuseSoC?", "body": "Hey!\r\nI have question about `ICacheECC `, is this parameter need to be passed by FuseSoC? I've problem with this, because when I generate files for Riviera and Xcelium by command `./vendor/lowrisc_ip/dvsim/dvsim.py dv/uvm/icache/dv/ibex_icache_sim_cfg.hjson -t [riviera/xcelium]` FuseSoC create: ` -pvalue+tb.ICacheECC=1` in file list."}
+{"org": "lowRISC", "repo": "ibex", "number": 957, "state": "closed", "title": "internal gated clock running during reset", "body": "from a low-power point-of-view, having the main clock running before fetch_enable_i is set high to kick-start it, is not a great idea ;)\r\n\r\nI've traced it up to ibex_controller.sv, where in RESET state, the ctrl_busy is still on default 1'b1. Could we maybe make it 1'b0 in reset state?\r\n\r\nTo make it work, I also add to activate the internal clock when fetch_enable_i is high, otherwise if fetch_enable_i is only 1 cycle long, you miss it."}
+{"org": "lowRISC", "repo": "ibex", "number": 954, "state": "closed", "title": "UVM DV: Unsynchronized DUT probe signals", "body": "In PR #953 I corrected some paths that were causing spurious triggering of internal TB events. Even with that fix, the spurious triggers remain due to glitchy sampling of those signals.\r\n\r\nI hacked around it by replacing all instances of `wait (signal);` with `while (!signal) @(posedge clk);` but I guess the correct fix is a clocking block."}
+{"org": "lowRISC", "repo": "ibex", "number": 935, "state": "closed", "title": "Wire in the branch_spec signal properly in ICache testbench", "body": "This should have no functional change - it's still set iff branch is\r\nset - but the logic now lies in the UVM code, rather than the\r\nstructural code in tb.sv."}
+{"org": "lowRISC", "repo": "ibex", "number": 930, "state": "closed", "title": "Missing dependency on python3-bitstring", "body": "The riscv-dv code uses it and I don't think we have it in python-requirements."}
+{"org": "lowRISC", "repo": "ibex", "number": 928, "state": "closed", "title": "Fix some interrupt related issues found in OT chip tests", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 912, "state": "closed", "title": "Back to back exceptions", "body": "Hi all,\r\nI found an interesting issue when running a PMP test, the waves are shown below:\r\n\r\n\r\nThe situation is as follows.\r\nThe instruction at `PC=0x8000921c` raises a PMP exception trying to store data to address `0x80014d04`, which is correctly propagated through the LSU and to the controller, which sees its `store_err_i` and `store_err_q` go high at the yellow marker.\r\nThe very next instruction at `PC=80009220` raises a PMP fetch exception in the IF stage, which again gets propagated to the controller correctly, as its `instr_fetch_err_i` and `instr_fetch_err` signals both go high.\r\nThe problem here arises due to the fact that `instr_fetch_err` and `store_err_q` are both high in the controller during the cycle when it transitions to the `FLUSH` state to handle an exception, causing the core to re spond to the instruction fetch exception and ignore the store fault completely due to exception prioritization.\r\n\r\nI'm pretty certain that this can be recreated with non-PMP exceptions as it just requires exceptions raised by two sequential instructions (as long as one is a memory-related exception) to be seen by the controller on the same cycle."}
+{"org": "lowRISC", "repo": "ibex", "number": 906, "state": "closed", "title": "[dv] Add missing signal to i$ tb", "body": "- Fixes #904\r\n- Will need a future update to drive the new signal properly\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 904, "state": "closed", "title": "Failing UVM sanity with commit \"[rtl] Add speculative branch signal\"", "body": "Commit 12b39476c0c6bb16dc0d43057730f263836dac95 (`[rtl] Add speculative branch signal`) broke the UVM sanity tests.\r\n\r\nRunning `./vendor/lowrisc_ip/dvsim/dvsim.py dv/uvm/icache/dv/ibex_icache_sim_cfg.hjson -t vcs --waves` I get:\r\n\r\n## List of Failures\r\n\r\n**TEST:** ibex_icache_sanity, **SEED:** 3278749286
\r\n**LOG:** $scratch_path/0.ibex_icache_sanity/out/run.log
\r\n```\r\nUVM_FATAL @ 189350 ps: (ibex_icache_mem_resp_seq.sv:113) uvm_test_top.env.mem_agent.sequencer [uvm_test_top.env.virtual_sequencer.ibex_icache_sanity_vseq.mem_seq] Check failed (i < N) No pending grant for address 0xxxxxxxxX (1 items in queue). \r\nUVM_INFO @ 189350 ps: (uvm_report_server.svh:894) [UVM/REPORT/SERVER] \r\n--- UVM Report Summary ---\r\n\r\nQuit count : 0 of 1\r\n```\r\n\r\n**TEST:** ibex_icache_passthru, **SEED:** 1046335328
\r\n**LOG:** $scratch_path/0.ibex_icache_passthru/out/run.log
\r\n```\r\nUVM_FATAL @ 688601 ps: (ibex_icache_mem_resp_seq.sv:113) uvm_test_top.env.mem_agent.sequencer [uvm_test_top.env.virtual_sequencer.ibex_icache_passthru_vseq.mem_seq] Check failed (i < N) No pending grant for address 0xxxxxxxxX (1 items in queue). \r\nUVM_INFO @ 688601 ps: (uvm_report_server.svh:894) [UVM/REPORT/SERVER] \r\n--- UVM Report Summary ---\r\n\r\nQuit count : 0 of 1\r\n```\r\n\r\n@tomroberts-lowrisc @rswarbrick "}
+{"org": "lowRISC", "repo": "ibex", "number": 903, "state": "closed", "title": "[rtl] Fix PMP NA4 address matching", "body": "- Apply address masking to the bottom address bit for NA4 as well as\r\n NAPOT\r\n- Relates to #902\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 902, "state": "closed", "title": "Incorrect pmp NA4/NAPOT address matching", "body": "#875 seems to have introduced an issue with `NA4/NAPOT` address matching modes - the scenario is as follows.\r\n\r\nIn my test, `csr_pmp_addr[3]` is `0x8000_3f54` with its corresponding configuration bits `csr_pmp_cfg[3]` set to `{0, PMP_MODE_NA4, 0, 1, 1}`, and the core requests an instruction fetch from `pmp_req_addr_i[0] = 0x8000_3f54`. Note that since we are using NA4 mode, `region_start_addr[3] = 0x8000_3f54` and `region_addr_mask[3] = 0xffff_ffff`. We are also using a granularity of 0.\r\n\r\nWith this setup, we should expect that the requested instruction fetch should match `pmpaddr3` but then then fail due to a fetch error since the corresponding access bit is disabled.\r\n\r\nHowever, `region_match_low[0][3]` goes high as expected since\r\n`pmp_req_addr_i[0][33:2] >= region_start_addr[3][33:2]`,\r\nbut `region_match_high[0][3]` stays low since the check\r\n`pmp_req_addr_i[0][33:2] < csr_pmp_addr[3][33:2]` will fail due to lack of equality checking - this causes an altogether mismatch with this PMP region.\r\n\r\nI think we still need to include equality checking to cover NA4 and NAPOT matching (as the error I describe above can also easily occur in NAPOT mode with any granularity), but these equality checks should only be enabled when we are in one of those two modes."}
+{"org": "lowRISC", "repo": "ibex", "number": 893, "state": "open", "title": "DV: Use FuseSoC instead of hardcoding file list in ibex_dv.f", "body": "Similar to what we do in OpenTitan, we must move away from a hard-coded file list to make full use of our primitives system and other functionality enabled by FuseSoC and its `.core` files."}
+{"org": "lowRISC", "repo": "ibex", "number": 864, "state": "closed", "title": "PMP fetch exception causing `X` propagation through IF stage", "body": "Hi Tom,\r\nI ran into 2 related (at least in this situation) issues when running some PMP tests, the waves and a code snippet are shown below:\r\n\r\n\r\nIn this situation, all PMP regions are using TOR address matching, `pmpaddr0` is set to the address of `` (which gets word-aligned to `0x80001e14`) with all permissions enabled, and `pmpaddr1` is set to `0x8000447c` with all permissions initially disabled. With regards to instruction execution order, Ibex has just executed a jump instruction located at `0x80000314` and has jumped to ``.\r\nJust before the M3 marker in the waves, Ibex is executing an instruction fetch from `80001e14` to handle the first half of the misaligned instruction located at ``, we can see that the `request` line goes high successfully and the testbench responds by asserting the `grant` line which goes high right at the M3 marker.\r\nThe first issue I see here is that given the PMP configuration this fetch to `80001e14` should raise an exception immediately as this address is controlled by the `pmpaddr1` region, but the core allows this fetch to succeed as it has somehow matched this to region0. I think this error is due to how `region_match_high[c][r]` is assigned within the PMP matching logic - it seems like it should be a strict `<` inequality instead of a `<=` to check equality of the upper bound as per the PMP specification of TOR matching.\r\nGoing past this error, what happens next is also fairly interesting; first just after M3, the core is about to send a second fetch request to `0x80001e18` to fulfill the second part of the misaligned instruction at ``, but correctly flags it as a PMP fault and does not raise the top level `request` line to the testbench to complete the misaligned instruction fetch.\r\nAt marker M1, the testbench asserts `rvalid` on the IMEM interface and responds with the data word `0x61170000` to fulfill the fetch request to `0x80001e14`, the upper half of which matches the lower half of the instruction at ``, and the lower half of which matches the `ecall` at `80001e12`. The fifo in the prefetcher however seems to think that it should still output a valid instruction on the following cycle, constructs an `rdata_unaligned` out of `in_rdata_i[15:0]` and `rdata[31:16]` (which results in `0xXXXX6117`), and raises `out_valid_o` to qualify this instruction to the rest of the pipeline, resulting in `ASSERT_KNOWN_IF` failures later on in the decode stage, the IbexBranchDecisionValid assertion in particular."}
+{"org": "lowRISC", "repo": "ibex", "number": 859, "state": "closed", "title": "[dv/makefile] Same seed used for each iteration of Ibex regressions", "body": "Hi,\r\nI've been seeing an issue with Ibex regressions where if I run a test (say riscv_debug_basic_test) 10 times, each of the ten iterations of this test all use the exact same seed since it is now generated in the top level makefile and passed down to every simulation iteration.\r\nThis is totally fine for sanity regressions where each test is run exactly once, but for large regressions (nightly, etc...), having every iteration of a test use the exact same seed runs counter to the point of having large numbers of tests in regressions to begin with.\r\nIdeally, if I specify `ITERATIONS=10` on the command line, I expect that each of the ten iterations is using different seeds - I'm not quite sure if having the Makefile generate a top level seed used for every iteration would be the best approach here.\r\nCould you please take a look?\r\nThanks!"}
+{"org": "lowRISC", "repo": "ibex", "number": 857, "state": "closed", "title": "How to classify and deal with multiple configurations", "body": "The current multi-config setup for Ibex is simple. We have a number of named configs and they all supply settings for the same parameters, this is one example:\r\n\r\nhttps://github.com/lowRISC/ibex/blob/863fb56eb166dc8d6e25f4e98b7319f0c7088564/ibex_configs.yaml#L10-L16\r\n\r\nAre we happy with this setup or do want something more complex? In particular for PMP this isn't really something that pairs nicely with a 'high performance' config you could equally want it with the lower performance or higher performance config. We could define multiple configs one with -pmp one without to have every config (or some subset of them) with pmp on or off (so you'd have a `small-3cmult-pmp-off` and a `small-3cmult-pmp-on`. Alternatively we could introduce config 'add-ons'. Extra bits in the YAML file that could be paired with any config:\r\n\r\n```yaml\r\npmp16-on:\r\n PMPRegions: 16\r\n PMPGranularity: 0\r\n```\r\n\r\nThis would be given to `ibex_config.py` along with the main config name\r\n\r\n```\r\n./util/ibex_config.py experimental-maxperf-bm-1cmult pmp16-on fusesoc_opts\r\n```\r\n\r\nI was tending towards the config add-ons option, as doing multiple configs with names like '-pmp-on' doesn't scale very well.\r\n\r\n(Lets try and divorce this from the what is a supported configuration discussion, my view is we can define supported configs in the documentation and flag them specifically in the `ibex_configs.yaml` but it can still give functionality/parameters for non-supported configs, we could even add a warning output from `ibex_config.py` if you use an unsupported config setup)."}
+{"org": "lowRISC", "repo": "ibex", "number": 852, "state": "closed", "title": "'VERBOSE' mode doesn't give any extra information when running a single test", "body": "I was having an issue running a simulation using OVPSim. It wasn't dumping anything in the log file and the comparison was failing. I tried running with `make ... VERBOSE=1`, hoping that it will give me some more log output to figure out what the issue was. The output was the same.\r\n\r\nIn the end, I solved my issue using good old fashioned print debugging (https://github.com/google/riscv-dv/issues/565)."}
+{"org": "lowRISC", "repo": "ibex", "number": 850, "state": "closed", "title": "ICache <-> core valid signal depends on ready", "body": "As it currently stands, the documentation (that I wrote) suggests this shouldn't be the case. We either need to fix the documentation or change the code."}
+{"org": "lowRISC", "repo": "ibex", "number": 849, "state": "closed", "title": "PMP store fault does not jump to exception handler", "body": "Hi Tom,\r\nI ran into this situation when debugging a PMP test (with icache disabled):\r\n\r\nThe instruction at `PC=0x8001fb0a` (under the cursor) is a store instruction to address `0x80031034`, which the PMP detection logic correctly flags as an error for not matching any pmp_cfg CSR in user-mode and prevents a request from being sent to the memory.\r\nDuring this, the controller is in the `DECODE` state, but it does not actually detect `special_req_all` going high because `instr_valid_i` has already gone low by the time it reflects the rising `exc_req_lsu` wire - as a result the core pretends everything is okay and goes on to execute the instruction at the next PC.\r\nI suspect this has to do with how `instr_valid_id_d/q` are set in the IF stage, as they appear to be dropping one cycle too early - additionally, when I enabled the icache and reran this test, this issue did not appear, e.g. `instr_valid_i` in the controller went high at the same time as `special_req_all` to qualify it due to `instr_valid_id_d/q` staying high for an additional cycle:\r\n\r\nWe can see that with the icache, `instr_valid_id_d/q` stay high for extra cycles, allowing the controller to correctly qualify the PMP exception and then start fetching the address of the exception handler (`0x80001400`)."}
+{"org": "lowRISC", "repo": "ibex", "number": 845, "state": "closed", "title": "Unique case isn't unique in ibex_alu.sv", "body": "On the head of master (`7dafdf64`), run the following command:\r\n\r\n``` bash\r\ncd dv/uvm/core_ibex\r\nmake WAVES=1 VERBOSE=1 ISS=spike COV=1 SEED=26187 TEST=riscv_arithmetic_basic_test\r\n```\r\n\r\nOnce this has finished, have a look at one of the simulation logs. For example, [`out/seed-26187/rtl_sim/riscv_arithmetic_basic_test.0/sim.log`](https://github.com/lowRISC/ibex/files/4587033/sim.log) (attached). You'll see VCS warning about incorrect unique case:\r\n\r\n```\r\nWarning-[RT-MTOCMUCS] More than one condition match in statement\r\n/src/lr/ibex/rtl/ibex_alu.sv, 78\r\n More than one condition matches are found in 'unique case' statement inside \r\n core_ibex_tb_top.dut.u_ibex_core.ex_block_i.alu_i, at time 32370000ps.\r\n \r\n Line number 79 and 80 are overlapping.\r\n```\r\n\r\nRather upsettingly, this doesn't actually cause the test to fail. But it does suggest a problem with the RTL."}
+{"org": "lowRISC", "repo": "ibex", "number": 844, "state": "closed", "title": "[memutils] Make memutils work with wider RAMs", "body": "- Using the RAM width in the DPI function definition causes Verilator\r\n compilation failures where there are multiple memory instances with\r\n different widths.\r\n- With this patch, the width of the function is fixed at 128bits, and\r\n the memory loader can load any width of data (+ ECC bits) that it\r\n likes (up to 128bits total). The RAM on the SystemVerilog side will\r\n discard any extra unused bits.\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 840, "state": "closed", "title": "The contents of dv/uvm/data are not vendored properly from OpenTitan", "body": "These were copied from OpenTitan as part of the mega-commit at PR #711. Since they are copied into the main Ibex repo, rather than vendored in, they don't stay in-sync with changes there.\r\n\r\nRecently (30th March), some of the keys for coverage generation changed (see OpenTitan commit 39ffebd). These don't now match and you can't run `dvsim.py` to generate coverage without hacking `dv/uvm/data/vcs/vcs.hjson`, at least.\r\n\r\nI think we should probably be vendoring this in properly. Is it part of dvsim? In which case, maybe it needs moving around in the OT repo and getting pulled in with the existing rules. If not, we need (yet) another vendor rule and either way this code needs to live under `/vendor`."}
+{"org": "lowRISC", "repo": "ibex", "number": 833, "state": "closed", "title": "Trigger cause", "body": "Hi,\r\nI just noticed that the \"2 - Trigger cause\" is absent in the doc\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 832, "state": "closed", "title": "PMP load error qualifies register writeback", "body": "Hi,\r\nI encountered this situation when running some pmp tests on Ibex:\r\n\r\nThe instruction at `PC=0x80002250` is an `lb` instruction that tries to access the address `0x800148e4`. One cycle after this instruction reaches the decode stage, it causes a PMP fault and `pmp_err_q` goes high for two cycles, but `lsu_rdata_valid_o` still goes high to `1'b1` even though the DMEM interface has not sent out a request at all, triggering an incorrect register writeback of of `XXXX_XXXX`."}
+{"org": "lowRISC", "repo": "ibex", "number": 826, "state": "closed", "title": "[bitmanip] [zbe] bit deposit and bit extract (bdep/bext) instructions", "body": "The zbe instruction group implements the generic bit extract and bit deposit functions. `bext` collects LSB justified bits to rd from rs1 using extract mask in rs2. `bdep` writes LSB justifie dbits from rs1 to rd using deposit mask in rs2. \r\n\r\nThe implementation is planned to base upon the butterfly network as described in [Hilewitz et al.](http://palms.ee.princeton.edu/system/files/Hilewitz_JSPS_08.pdf). \r\n\r\nSimilar reference implemnetations by Claire Wolf indicate a rather large increase in area caused by this architecture. There are several possibilities to trade some latency for a smaller core, but the benefits are limited. However, in a complete RV32B implementation there are several functionalities, which could share the butterfly network, and therefore somewhat mitigate the area increase. For example it should be possible, to reuse zbe structures for bitcount instructions (ctz, clz, pcnt), single-bit instructions (zbs), bit ppermutation (zbp), pack, rotate and cmix instructions. \r\n\r\nThe plan is to first implement the butterfly network just for bdep and bext. At that point we will see how bad the area increase is. I will then try to incorporate as many of the existing instructions as possible into the structure. \r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 819, "state": "closed", "title": "[rtl/icache] Fix typo in ram req", "body": "Signed-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 808, "state": "closed", "title": "SpecialReqAllGivesSpecialReqBranchIfBranchInst assertion failure", "body": "Hi all,\r\nWhen running the `riscv_mmu_stress_test` with PMP regions enabled, I noticed that the `SpecialReqAllGivesSpecialReqBranchIfBranchInst` assertion was failing, shown below:\r\n\r\nA snippet of the OVPsim log of the relevant instruction execution is shown below:\r\n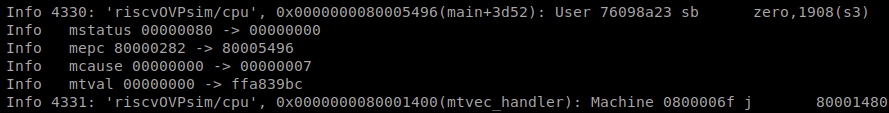\r\nA waveform snippet of when the assertion fails is below, the failure occurs one cycle after the yellow marker, where the small red arrow is located:\r\n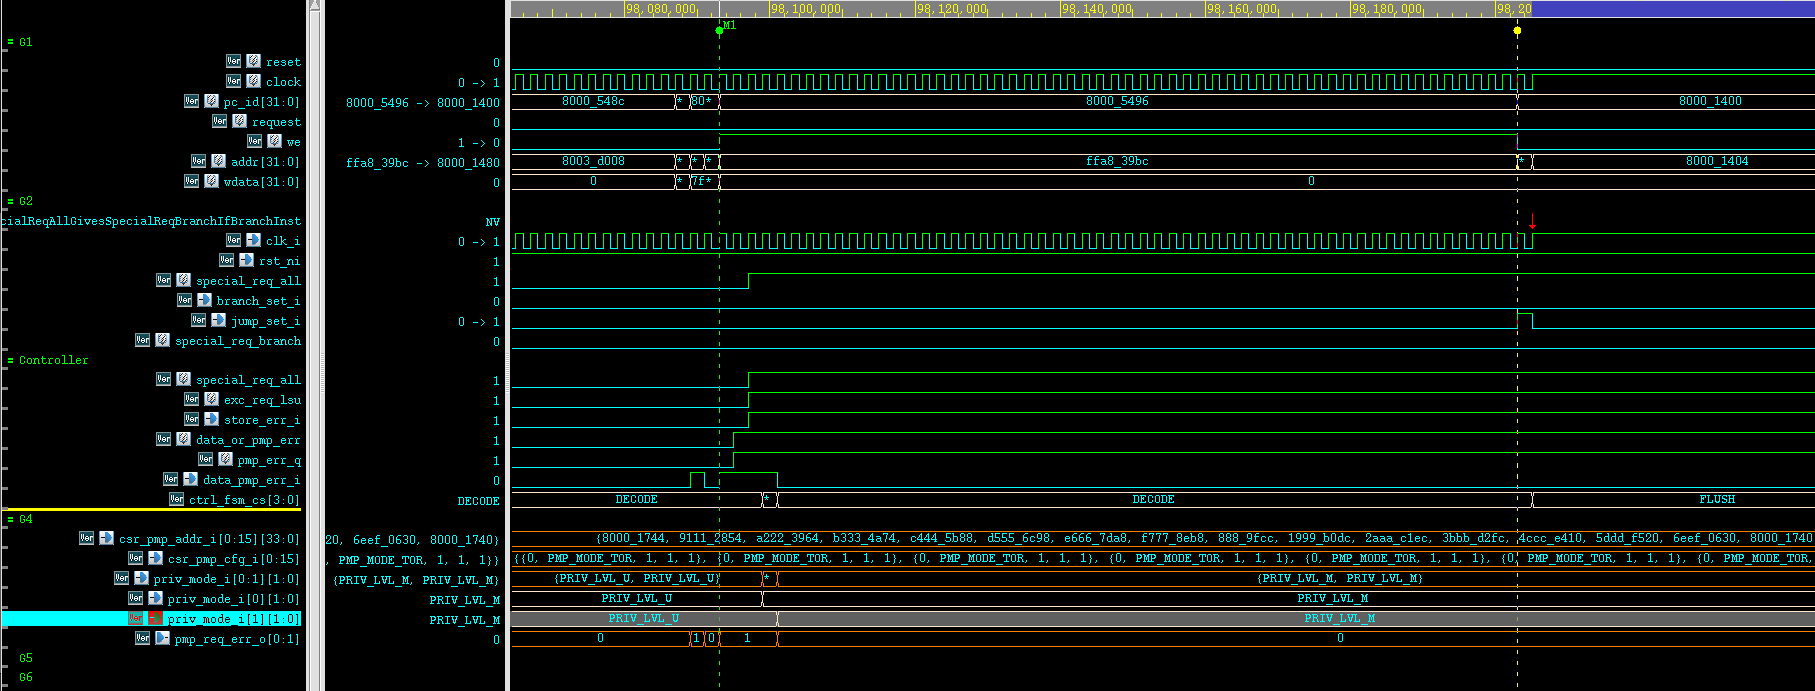\r\nThe situation is as follows: the `sb` instruction at `PC=0x80005496` (at the green `M1` marker accesses memory at `0xffa839bc` from User-mode and this access correctly causes a PMP store address exception (all 16 regions are enabled and set to `TOR` mode, the address being accessed here is not contained within any of the enabled regions). The core then jumps to the PC stored in `mtvec`, which is a jump instruction at `PC=0x80001400`.\r\nHowever, one cycle after starting to execute this jump, the previously mentioned assertion fails, as even though `special_req_all` and `jump_set_i` are both high due to the PMP store exception and the resultant branch, the `special_req_branch` signal does not go high at all."}
+{"org": "lowRISC", "repo": "ibex", "number": 807, "state": "closed", "title": "Monitor and SVA assertions for core agent in icache UVM testbench", "body": "Since the memory agent PR (#793) is slightly stalled, I've split out the follow-up work that adds monitors and SVA assertions. This is the code that applies to the core agent.\r\n\r\nYou should be able to build it, but it won't run to completion because there is no memory agent. I have (of course) checked that rebasing the patches from #793 on top of this patchset results in something that works."}
+{"org": "lowRISC", "repo": "ibex", "number": 793, "state": "closed", "title": "Initial memory agent for ICache UVM tests", "body": "The main patch is the first in the sequence: the second just disables PMP/memory errors to work around a bug in some different code, so we can land this PR independently of that fix.\r\n\r\nHere's the commit message for the first patch:\r\n\r\n> **Initial memory agent for ICache UVM testbench**\r\n> \r\n> As with the core agent, this doesn't yet have any proper monitoring,\r\n> and the testbench has no scoreboard, so we're not actually checking\r\n> anything.\r\n> \r\n> However, it *does* implement a slave agent which can respond to\r\n> instruction fetches from the icache. This runs a test to completion,\r\n> try:\r\n> \r\n> `make -C dv/uvm/icache/dv run WAVES=1`\r\n> \r\n> Note that the timeout in the hjson file was too small, so this bumps\r\n> it to a larger value. A later patch will replace the timeout with a\r\n> heartbeat monitor, which should be much cleaner.\r\n>\r\n> The exact dance for the UVM reactive slave is complicated. See\r\n> [dv/uvm/icache/dv/ibex_icache_mem_agent/README.md](https://github.com/rswarbrick/ibex/blob/mem-agent/dv/uvm/icache/dv/ibex_icache_mem_agent/README.md) for the details."}
+{"org": "lowRISC", "repo": "ibex", "number": 790, "state": "closed", "title": "Verilator memutil: Support 64 bit wide memories", "body": "Currently memutil expects the input file (ELF/BIN) to be 32 bit words, and the memory also to be 32 bit words. We need to support the case where the input file stays 32 bit wide, but the memory is a multiple of that, e.g. 64 bit.\r\n\r\nhttps://github.com/lowRISC/ibex/blob/master/dv/verilator/memutil/cpp/verilator_memutil.cc#L426\r\n\r\nhttps://github.com/lowRISC/ibex/blob/master/shared/rtl/prim_generic_ram_1p.sv#L93\r\n\r\nThis change is also needed in OT. First, do a PR in Ibex. Then do a PR in OT, updating Ibex through the vendor tool, and the primitive separately."}
+{"org": "lowRISC", "repo": "ibex", "number": 787, "state": "closed", "title": "Add fixed-time execution features to multiply and divide", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 786, "state": "closed", "title": "Add clocking blocks to icache core agent interface", "body": "As discussed in issue #778.\r\n\r\nThe other two patches in the queue are embarrassing: it seems my \"edit a long patch queue and push something near the bottom\" flow missed a couple of typos which were fixed further down the list. I've checked, and you can actually run the code after this."}
+{"org": "lowRISC", "repo": "ibex", "number": 781, "state": "closed", "title": "ID/EX: Use `multdiv_sel` instead of `multdiv_en` and variants where possible", "body": "While reviewing #746 I noted two things in ID/EX:\r\n- In `ibex_ex_stage.sv` we are generating `multdiv_en` based on `mult_en_*` and `div_en_*` signals to control the result mux.\r\n- Inside `ibex_multdiv_fast/slow.sv` we are using the same `mult_en_*` and `div_en_*` to control both FSMs and muxes. The `multdiv_sel` signal is not available (only inside the ALU).\r\n\r\nThe main difference between these signals is that `multdiv_sel` directly comes out of the decoder where as `mult_en_*` and `div_en_*` are qualified with `instr_executing` inside the ID stage (which itself depends on various other signals from ID stage and the controller).\r\n\r\nAs far as I understand, this is needed to control the FSMs inside `ibex_multdiv_fast/slow.sv` but not for most of the muxes. These muxes or at least some of them could be controlled depending on the decoder output only. Since all those muxes are critical, I would suggest to investigate which of the muxes can be controlled by the less critical `multdiv_sel` inside the ID/EX stage.\r\n\r\nDo you @GregAC , @tomroberts-lowrisc , @rswarbrick , @imphil think this makes sense? Do you have any thoughts on this?\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 778, "state": "closed", "title": "[dv] Add clocking blocks to icache UVM code", "body": "See discussion on PR #761, in particular [these comments](https://github.com/lowRISC/ibex/pull/761#discussion_r405777417).\r\n\r\nSri and Udi have suggested that the code would be better if the interface included clocking blocks. Suggested code:\r\n```systemverilog\r\nclocking driver_cb @(posedge clk_i);\r\n output req;\r\n output branch;\r\n output branch_addr;\r\n output ready;\r\n output enable;\r\n output invalidate;\r\nendclocking\r\n\r\nclocking monitor_cb @(posedge clk_i);\r\n input valid;\r\n input rdata;\r\n input addr;\r\n input err;\r\n input err_plus_2;\r\n input busy;\r\nendclocking\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 776, "state": "closed", "title": "RTL Simulation timeout in full regression", "body": "Hi,\r\n\r\nWhile running full regression using command `make WAVES=1 VERBOSE=1 ISS=spike COV=1` , RTL simulation gets multiple time outs of the following nature:\r\n\r\n```\r\nINFO Running RTL simulation...\r\nTue, 14 Apr 2020 18:58:31 INFO Command progress: 0/371\r\nTue, 14 Apr 2020 19:02:48 INFO Command progress: 1/371\r\nTue, 14 Apr 2020 19:02:49 INFO Command progress: 2/371\r\nTue, 14 Apr 2020 19:02:49 INFO Command progress: 3/371\r\nTue, 14 Apr 2020 19:02:49 INFO Command progress: 4/371\r\nTue, 14 Apr 2020 19:12:49 ERROR Timeout[600s]: env SIM_DIR=out/seed-26187/rtl_sim/riscv_pmp_test.0 out/seed-26187/rtl_sim/vcs_simv +vcs+lic+wait +signature_addr=8ffffffc -ucli -do ./vcs.tcl -cm line+tgl+assert+fsm+branch -cm_dir out/seed-26187/rtl_sim/test.vdb -cm_log /dev/null -assert nopostproc -cm_name test_riscv_pmp_test_0 +ntb_random_seed=26187 +UVM_TESTNAME=core_ibex_base_test +bin=out/seed-26187/instr_gen/asm_tests/riscv_pmp_test_0.bin +ibex_tracer_file_base=out/seed-26187/rtl_sim/riscv_pmp_test.0/trace_core -l out/seed-26187/rtl_sim/riscv_pmp_test.0/sim.log\r\n```\r\n\r\nOne thing I figured out is that there is no file present at path specified here: `+ibex_tracer_file_base=out/seed-26187/rtl_sim/riscv_pmp_test.0/trace_core` . \r\n\r\nTrace log is generated only at following places:\r\n```\r\n./riscv_arithmetic_basic_test.0/trace_core_00000000.log\r\n./riscv_arithmetic_basic_test.1/trace_core_00000000.log\r\n./riscv_arithmetic_basic_test.2/trace_core_00000000.log\r\n./riscv_arithmetic_basic_test.3/trace_core_00000000.log\r\n./riscv_machine_mode_rand_test.2/trace_core_00000000.log\r\n./riscv_machine_mode_rand_test.3/trace_core_00000000.log\r\n./riscv_machine_mode_rand_test.7/trace_core_00000000.log\r\n./riscv_rand_instr_test.2/trace_core_00000000.log\r\n./riscv_rand_instr_test.3/trace_core_00000000.log\r\n./riscv_rand_instr_test.7/trace_core_00000000.log\r\n./riscv_rand_instr_test.8/trace_core_00000000.log\r\n./riscv_rand_jump_test.5/trace_core_00000000.log\r\n./riscv_rand_jump_test.7/trace_core_00000000.log\r\n./riscv_rand_jump_test.8/trace_core_00000000.log\r\n./riscv_jump_stress_test.4/trace_core_00000000.log\r\n./riscv_mmu_stress_test.2/trace_core_00000000.log\r\n./riscv_debug_basic_test.0/trace_core_00000000.log\r\n./riscv_debug_basic_test.4/trace_core_00000000.log\r\n./riscv_debug_basic_test.8/trace_core_00000000.log\r\n./riscv_debug_stress_test.11/trace_core_00000000.log\r\n./riscv_debug_stress_test.13/trace_core_00000000.log\r\n./riscv_debug_branch_jump_test.5/trace_core_00000000.log\r\n./riscv_debug_wfi_test.4/trace_core_00000000.log\r\n./riscv_debug_wfi_test.5/trace_core_00000000.log\r\n./riscv_debug_wfi_test.6/trace_core_00000000.log\r\n./riscv_debug_wfi_test.8/trace_core_00000000.log\r\n./riscv_debug_ebreak_test.9/trace_core_00000000.log\r\n./riscv_debug_ebreakmu_test.0/trace_core_00000000.log\r\n./riscv_debug_ebreakmu_test.2/trace_core_00000000.log\r\n./riscv_debug_ebreakmu_test.10/trace_core_00000000.log\r\n./riscv_debug_csr_entry_test.2/trace_core_00000000.log\r\n./riscv_debug_csr_entry_test.4/trace_core_00000000.log\r\n./riscv_debug_csr_entry_test.5/trace_core_00000000.log\r\n./riscv_irq_in_debug_mode_test.5/trace_core_00000000.log\r\n./riscv_irq_in_debug_mode_test.7/trace_core_00000000.log\r\n./riscv_single_interrupt_test.7/trace_core_00000000.log\r\n./riscv_single_interrupt_test.11/trace_core_00000000.log\r\n./riscv_single_interrupt_test.14/trace_core_00000000.log\r\n./riscv_debug_single_step_test.12/trace_core_00000000.log\r\n```\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 767, "state": "closed", "title": "Dv error changes", "body": "Before I added the set_max_quit_count call I had a failure (xprop related that caused several assertions to fire each cycle) that caused a ~2GB log file and a failure to dump waves (the simulation timed out which seemed to mess up the wave dump).\r\n\r\nI set the default to 10 rather than 1 as it can be useful to let the simulation run a little past the first error if only to get another cycle or two in the waves."}
+{"org": "lowRISC", "repo": "ibex", "number": 766, "state": "closed", "title": "Ibex xprop fixes", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 765, "state": "closed", "title": "Initial icache testplan", "body": "This doesn't list all that many entries, possibly because the icache\r\ndoesn't really have many modes of operation (enabled/disabled;\r\ninvalidating)."}
+{"org": "lowRISC", "repo": "ibex", "number": 757, "state": "open", "title": "Ease of adapting Ibex memory protocol to tilelink for non 32-bit access", "body": "Tilelink has a `size` field it its message payload, that the native Ibex protocol does not have.\r\n\r\nWhen accessing 'standard' memory this is not a big problem. An Ibex -> Tilelink adapater could just always use 32-bit sizes and set all byte-enables for read (`Get` in Tilelink terms) and for writes take the byte-enables from the `data_be_o` from Ibex.\r\n\r\nHowever this could give some difficulties around reads to devices where a read could trigger some action. Specifically if a device triggers some action on particular byte reads and the simple adapter described above is used a single `lb` instruction will turn into a 4-byte `Get` in Tilelink. The device might then trigger an action because certain bytes have been read but from a programmer's perspective these bytes haven't been touched. \r\n\r\nIn Tilelink for a `Get` message you cannot partially set the byte mask, so you must use the `size` field to communicate what bytes you actually intend to read where this matters. Ibex (from a quick look at the RTL anyway) does generate `data_be_o` that indicates the precise bytes you want so it would be possible to build some logic that can work out an appropriate `size` from the `data_be_o`.\r\n\r\nYou may also find that your TileLink devices only respond to `PutFullData` so in order to do a byte-write to such a device you'd need to generate `PutFullData` with a byte size. Again the logic mentioned above could be employed to ensure the correct `size` field is generated along with some logic to understand if it's a `PullFullData` or not.\r\n\r\nThis logic would be a little fiddly, add extra area and increase the depth of logic. In some sense it's simply undoing what `ibex_load_store_unit` has done internally (taking the size and address and generating a be). We could introduce a `data_size_o` to the Ibex top-level interface allowing simpler adaption to Tilelink and other similar protocols.\r\n\r\nWe probably also want a requirement that `data_be_o` matches tilelink requires for its `mask` field but I think this is already the case, but worth documenting.\r\n\r\nAnother potential addition would a `data_full_o` that indicates `data_be_o` is set for every byte that's covered by `data_size_o`. This would allows a simple way to choose `PutPartialData` vs `PutFullData` on the tilelink interface. However it may be the adapter would always emit `PutPartialData` anyway. I will open an OpenTitan issue to discuss this point.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 756, "state": "closed", "title": "[rtl] Add fixed time execution of branches", "body": "- A new parameter and a run-time control bit (SecureIbex and\r\n secure_mode) enable different behaviour for running security critical\r\n code sections.\r\n- In the new mode, all branches act as if taken, with not-taken\r\n branches executing as a branch to the next instruction.\r\n- This should give similar execution time/power characteristics\r\n regardless of the branch condition.\r\n- Note that with the BranchTargetALU, branches stall an extra cycle in\r\n secure mode to avoid factoring the branch-taken decision into the\r\n branch target address mux.\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 755, "state": "closed", "title": "[dv] update Makefile gen step dependency", "body": "Appends `GEN_DIR` to the list of dependencies for the `gen` step in the simulation flow, as we want instruction generation to also be dependent on the generation source directory (for example to test changes to riscv-dv that have not been vendored into Ibex yet).\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 754, "state": "closed", "title": "Fill out an initial DV plan for the icache", "body": "This currently has quite a lot of TBD sections, but should hopefully\r\ndescribe my plan for the UVM testing reasonably well."}
+{"org": "lowRISC", "repo": "ibex", "number": 751, "state": "closed", "title": "[doc] Add Ibex Concierge documentation", "body": "Add a document how we plan to run the Ibex Concierge duty."}
+{"org": "lowRISC", "repo": "ibex", "number": 747, "state": "closed", "title": "[dv] move all SV interface includes into ibex_dv.f", "body": "This PR moves all SV interface includes from the relevant *_pkg.sv file into ibex_dv.f, as a follow up to #711.\r\nIn order to get the Icache testbench to compile with dvsim in #711, the ibex_mem_intf.sv file had to be removed from its `include` inside the `ibex_mem_intf_agent_pkg`, and thus had to be manually added in `ibex_dv.f` to get Ibex simulation (which don't use dvsim yet) to successfully pass.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 745, "state": "closed", "title": "Add a CI configuration for the B extension", "body": "With work on the B extension landing we should add a CI configuration that tests this config. It can use the new framework added by @GregAC in #714."}
+{"org": "lowRISC", "repo": "ibex", "number": 736, "state": "closed", "title": "Verible lint: Use config file", "body": "Currently we specify the Verible configuration in the `.core` files. Now that Verible has support for config files, we should read the config from a config file instead.\r\n\r\nhttps://github.com/google/verible/pull/229"}
+{"org": "lowRISC", "repo": "ibex", "number": 733, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@7675315", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 76753158d940fffc53fbb92942ae5d1d768a7cdc\r\n\r\n* configurable mtvec alignment (google/riscv-dv#527) (udinator)\r\n* Update b-extention (google/riscv-dv#526) (weicaiyang)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 731, "state": "closed", "title": "Correct PMP granularity equation", "body": "The `+2` part should have been part of the exponent, as indicated by the\nRISC-V spec."}
+{"org": "lowRISC", "repo": "ibex", "number": 730, "state": "closed", "title": "[DV] UVM environment should obey/understand mtvec alignment constraints", "body": "I am seeing a failure in the riscv_illegal_instr_test. The root of the issue is Ibex jumps to a different PC upon seeing an illegal instruction compare to spike. There are further tests with similar looking failures that I suspect have the same root cause.\r\n\r\nThe reason for this is in the particular test I'm looking at mtvec is set to 0x80001229 at the beginning of the test.\r\n\r\nThe privileged spec allows implementation defined alignment of mtvec base\r\n\r\n> An implementation may have different alignment constraints for different modes. In particular,\r\nMODE=Vectored may have stricter alignment constraints than MODE=Direct.\r\n\r\nOn Ibex mtvec is hardcoded into vectored mode (mtvec[1:0] == 2'b01) and mtvec base must be aligned to a 256-byte boundary so the [7:0] bits are ignored when writing an mtvec value.\r\n\r\nThis results in Ibex jumping to 0x80001200 and spike (which seems to accept any 4-byte aligned address for base) jumping to 0x80001228 leading to a mismatch.\r\n\r\nA simple fix would be for the UVM environment to always generate an appropriately aligned mtvec but this would mean no testing of the scenario where mtvec is written with a mis-aligned base. It would be preferable if it could understand instead that when a mis-aligned base is written to mtvec the exception handler will be located at the aligned base address instead. This could give some difficulties it matching up traces with spike however."}
+{"org": "lowRISC", "repo": "ibex", "number": 729, "state": "closed", "title": "Fix incorrect indentation in sim.py", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 728, "state": "closed", "title": "Added simulation option , added sv_seed in sim cmd for Riviera", "body": "Hey!\r\nIn UVM makefile, I added passing parameter value from macro and in `rtl_simulation.yaml` sv_seed in cmd option"}
+{"org": "lowRISC", "repo": "ibex", "number": 725, "state": "closed", "title": "[rtl] Extend BT ALU to be used for all jumps", "body": "- Create separate operand muxes for the branch/jump target ALU\r\n- Complete jump instructions in one cycle when BT ALU configured\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 722, "state": "closed", "title": "[rtl/icache] Fix an inconsistency in data output", "body": "- valid_o could be asserted for one cycle then dropped when receiving\r\n rvalid data for a request which has branched into the middle of a\r\n line.\r\n- This fix keeps valid_o asserted by using the offset version of\r\n fill_rvd_cnt_q (fill_rvd_beat) to compare against fill_out_cnt_q\r\n (which is also offset by the branch).\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 720, "state": "closed", "title": "[dv] fix irq timing in irq_in_debug_mode_test", "body": "Tighten up the interrupt raise/drop timings in irq_in_debug_mode_test to fix test failures.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 719, "state": "open", "title": "[fpv] Write properties for top-level Ibex interface", "body": "It would be worth writing properties for the top-level Ibex interfaces and then trying them out on Yosys. @rswarbrick has been working on properties around the icache using Yosys so has already done some of the work here.\r\n\r\nFrom prior experience simple properties around protocol checking can find a surprising number of bugs (e.g. properties on correct behaviour on the data interface could unearth things that are broken with the writeback stage)."}
+{"org": "lowRISC", "repo": "ibex", "number": 716, "state": "closed", "title": "[dv] workaround for dsim compile error", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 715, "state": "closed", "title": "[verilator] Fix --term-after-cycles", "body": "The option to limit the verilator simulation's maximum number of cycles was\r\nimplemented in terms of the `time_` variable, which counts half cycles. This\r\npatch makes the limit respect the requested number of full cycles.\r\n\r\nThe patch divides `time_` by 2, instead of multiplying `term_after_cycles_`\r\nby 2, as that better conveys the intended semantics, and slightly increases\r\nthe range of the limit. Related computations were modified for consistency."}
+{"org": "lowRISC", "repo": "ibex", "number": 711, "state": "closed", "title": "[dv] initial icache testbench", "body": "The initial commit of the testbench for the ibex_icache module generated by the `uvmdvgen` tool.\r\nThe testbench files and .hjson supporting files for `dvsim` tool are all contained within `dv/uvm/icache/[data/doc/dv]`.\r\n\r\nThere are several things to note with this PR:\r\n1) A directory `vendor/lowrisc_ip` has been created, which contains the `dv_base` testbench library, the `dv_utils` package, and various common tools, including the `uvmdvgen` tool for auto-generating testbenches and most importantly, the `dvsim` tool by which to actually simulate this icache testbench. For the time being, these tools have been manually copied over from the lowRISC/opentitan repository until they are spun off into a separate repo themselves. These tools and utilities from lowRISC/opentitan are the bulk of this PR and should not warrant a review.\r\n2) Several fusesoc .core files have been created in the existing Ibex testbench environment and agent directories, these are required since the icache testbench will use the currently existing ibex memory interface agent. These core files are dual purpose, as they will also be used when the Ibex testbenches switches over to using the `dvsim` .hjson based flow.\r\n3) To run builds and simulations, the `dvsim` tool must be invoked from the `ibex/` top level directory.\r\n\r\nThis PR provides all of the testbench components and run flow utilities needed to compile the icache testbench and run tests once they have been implemented.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 710, "state": "closed", "title": "[cov] fix extra backslash in makefile path", "body": "Fix the extraneous forward slash in the makefile coverage generation step to allow OUT to be full paths, instead of constraining them to relative paths.\r\n\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 709, "state": "closed", "title": "Wrong mtval recorded for instruction access fault", "body": "The RISCV Privileged ISA specification specifies:\r\n\"For instruction-fetch access or page-fault exceptions on systems with variable-length instructions, `mtval` will contain the virtual address of the portion of the instruction that caused the fault while `mepc` will point to the beginning of the instruction.\"\r\n\r\nIn Ibex currently, both `mepc` and `mtval` will point to the beginning of the instruction, even if the fault originated in the second half of a misaligned uncompressed instruction.\r\n\r\nI see two solutions:\r\n1) Wire `mtval` to zero on instruction access faults to indicate that this reporting feature is not supported.\r\n2) Capture the second address somehow in this particular case. (It will always be the ID stage PC + 2)"}
+{"org": "lowRISC", "repo": "ibex", "number": 708, "state": "closed", "title": "[bitmanip] Ternary Bit-Manipulation Instructions cmix, cmov, fsl, fsr[i]", "body": "Hi Guys,\r\n\r\nFor the bitmanip ternary instructions, three registers have to be read. Since our register file only has two read ports, I will implement those instructions in two cycles.\r\n\r\nI will take inspiration from the existing structures which require pipeline stalls. As soon as I have a verified implementation I will again open a draft PR.\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 704, "state": "closed", "title": "[dv] coverage generation", "body": "Add a step to the simulation flow for merged coverage generation.\r\nAdditionally changed the naming of coverage databases created by VCS to `test__` to make unique each database name and avoid overwriting, since seeds are generated in the top level Makefile.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 703, "state": "closed", "title": "[DV] Prerequisites for bitmanip DV", "body": "We are making progress on implementing the bitmanip (B) extension in Ibex in #89. This issue tracks things we need to have before we can start DV work on it.\r\n\r\n- [x] A compiler toolchain with bitmanip support in its assembler (at least). Tracking in https://github.com/lowRISC/lowrisc-toolchains/issues/8, https://github.com/lowRISC/ibex/pull/724\r\n- [x] Bitmanip support in spike and ovpsim (that exists AFAIK, we might need to adjust the build instructions)\r\n- [x] Bitmanip support in riscv-dv: https://github.com/google/riscv-dv/issues/520"}
+{"org": "lowRISC", "repo": "ibex", "number": 700, "state": "closed", "title": "Cannot get seed value by default from Makefile", "body": "I got error when I run the Makefile with default seed value. It seems it does not generate random seed value. Reproduce:\r\n\r\n```\r\ndanghai@ubuntu:~/ibex/dv/uvm/core_ibex$ make SIMULATOR=qrun VERBOSE=1 OUT=output\r\nmkdir -p output/seed-/.metadata\r\nusage: run.py [-h] [--target TARGET] [-o O] [-tl TESTLIST] [-tn TEST]\r\n [--seed SEED] [-i ITERATIONS] [-si SIMULATOR] [--iss ISS] [-v]\r\n [--co] [--cov] [--so] [--cmp_opts CMP_OPTS]\r\n [--sim_opts SIM_OPTS] [--gcc_opts GCC_OPTS] [-s STEPS]\r\n [--lsf_cmd LSF_CMD] [--isa ISA] [-m MABI]\r\n [--gen_timeout GEN_TIMEOUT]\r\n [--end_signature_addr END_SIGNATURE_ADDR] [--iss_opts ISS_OPTS]\r\n [--iss_timeout ISS_TIMEOUT] [--iss_yaml ISS_YAML]\r\n [--simulator_yaml SIMULATOR_YAML] [--csr_yaml CSR_YAML]\r\n [--seed_yaml SEED_YAML] [-ct CUSTOM_TARGET]\r\n [-cs CORE_SETTING_DIR] [-ext USER_EXTENSION_DIR]\r\n [--asm_tests ASM_TESTS] [--c_tests C_TESTS]\r\n [--log_suffix LOG_SUFFIX] [--exp] [-bz BATCH_SIZE]\r\n [--stop_on_first_error] [--noclean] [-d DEBUG]\r\nrun.py: error: argument --seed: invalid int value: ''\r\nMakefile:222: recipe for target 'output/seed-/.metadata/instr_gen.gen.stamp' failed\r\nmake: *** [output/seed-/.metadata/instr_gen.gen.stamp] Error 2\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 699, "state": "closed", "title": "Remove property from assert message", "body": "Assert macros in prim_assert.sv report the asserted property as part of\nthe error message if the assertion fails. Doing that requires us to\nstringify the property. If the property is multi-line in the source\ncode, this produces a multi-line string. According to the\nSystemVerilog standard, a multi-line string requires a backslash (`\\`)\nat the end of a line. Adding this backslash through a macro is not\npossible (at least to my knowledge), giving us no way to produce a\nstandards-compliant implementation of the `ASSERT` macros that report\nthe property as string.\n\nThis commit therefore removes the property from the error message if an\nassertion fails. It makes these messages less useful, but the\ninformation can still be recovered in a less convenient way through the\nname of the assertion, and the file and line numbers.\n\nFixes #669"}
+{"org": "lowRISC", "repo": "ibex", "number": 698, "state": "closed", "title": "Command for sanity regression in CI", "body": "We'd like to run a sanity regression in CI, with a runtime of 5-15 min. \r\n\r\n@udinator what command should we use for this run?"}
+{"org": "lowRISC", "repo": "ibex", "number": 697, "state": "closed", "title": "Questa qrun: Extra checking for conflicts with always_comb and always_latch variables is done at vopt time", "body": "I make PR to suppress warning vlog-2583 for silence warning\r\nFixed: #696"}
+{"org": "lowRISC", "repo": "ibex", "number": 696, "state": "closed", "title": "Questa: [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.", "body": "In Questa we get the following warning:\r\n\r\n```\r\n 18 ** Warning: /home/danghai/ibex/rtl/ibex_cs_registers.sv(730): (vlog-2583) [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.\r\n 19 ** Warning: /home/danghai/ibex/rtl/ibex_cs_registers.sv(732): (vlog-2583) [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.\r\n 20 ** Warning: /home/danghai/ibex/rtl/ibex_cs_registers.sv(739): (vlog-2583) [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.\r\n 21 ** Warning: /home/danghai/ibex/rtl/ibex_cs_registers.sv(742): (vlog-2583) [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.\r\n 22 ** Warning: /home/danghai/ibex/rtl/ibex_cs_registers.sv(745): (vlog-2583) [SVCHK] - Extra checking for conflicts with always_comb and always_latch variables is done at vopt time.\r\n\r\n```\r\n\r\n_Originally posted by @danghai in https://github.com/lowRISC/ibex/issues/669#issuecomment-597823073_\r\n\r\n\r\n\r\nMy gut feeling is that this warning can be safely ignored. @danghai can you give us the output of `verror 2583` to see if Questa suggests anything that can be done here on the RTL side? Otherwise I'd propose we find a way to silence this warning."}
+{"org": "lowRISC", "repo": "ibex", "number": 689, "state": "open", "title": "Possible optimisations in UVM Makefile", "body": "This issue separately tracks a specific part of issue #674.\r\n\r\nThe Makefile in `dv/uvm/core_ibex/Makefile` tries to be careful to regenerate targets if you change an option. This way, we ensure that if you run make twice with the same test (say) but change options, the test will actually be rebuilt and re-run.\r\n\r\nOne unfortunate side-effect is that the second command in\r\n\r\n make SEED=123 TEST=foo\r\n make SEED=123 TEST=bar\r\n\r\nwill start by deleting the results for the `foo` test. (As far as the Makefile is concerned, TEST is just another option that affects the output of the test generation stage).\r\n\r\nThis issue is to track whether we can avoid that somehow. Also, maybe there are other rebuilds we can avoid, such as rebuilding the instruction generator when you've just changed the test list.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 682, "state": "closed", "title": "Fix typo in uvm/core_ibex/Makefile", "body": "Reported in issue #674."}
+{"org": "lowRISC", "repo": "ibex", "number": 681, "state": "closed", "title": "update riscvOVPsim.ic for semihosting mode", "body": "This PR updates the riscvOVPsim ISS configuration file to disable the semihosting mode, otherwise EBREAK instructions will cause end of test to be reached.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 674, "state": "closed", "title": "[dv] minor Makefile issues", "body": "Hi @rswarbrick, this issue is just meant as a tracker of sorts for some minor issues I may encounter with the updated Makefile flow. Admittedly, many of these potential issues will just be my relative unfamiliarity with the new simulation output format or other minor questions, so this thread will just act as a place to consolidate all of these questions."}
+{"org": "lowRISC", "repo": "ibex", "number": 670, "state": "closed", "title": "Questa: Defaulting port to var rather than wire", "body": "(Spin-off from #622 by @danghai)\r\n\r\nQuesta reports:\r\n\r\n> ** Warning: /home/danghai/hhoangda/ibex/rtl/ibex_controller.sv(60): (vlog-13314) Defaulting port 'irqs_i' kind to 'var' rather than 'wire' due to default compile option setting of -svinputport=relaxed.\r\n\r\n(We get a similar message for other ports where we have a `struct` as input port.)\r\n\r\nThe code in question is:\r\n\r\n```verilog\r\n// in ibex_controller.sv\r\ninput ibex_pkg::irqs_t irqs_i,\r\n\r\n\r\n// in ibex_pkg.sv\r\n// Interrupt requests\r\ntypedef struct packed {\r\n logic irq_software;\r\n logic irq_timer;\r\n logic irq_external;\r\n logic [14:0] irq_fast; // 15 fast interrupts,\r\n // one interrupt is reserved for NMI (not visible through mip/mie)\r\n} irqs_t;\r\n```\r\n\r\nI don't see anything wrong with this code, it looks like the warning is not helping here. \r\n\r\n@danghai can you run `verror 13314` in Questa to learn more about the error? It can probably be silenced unless the output shows something that we should fix on our side.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 669, "state": "closed", "title": "Questa complains about newlines in ASSERT macros", "body": "(Spin-off from #622 by @danghai)\r\n\r\nCompiling Ibex with Questa gives the following warning:\r\n\r\n```\r\n** Warning: ** while parsing macro expansion: 'ASSERT' starting at /home/danghai/hhoangda/ibex/rtl/ibex_compressed_decoder.sv(286)\r\n** at /home/danghai/hhoangda/ibex/rtl/ibex_compressed_decoder.sv(286): (vlog-2643) Unterminated string literal continues onto next line.\r\n```\r\n\r\nThe code in question is\r\n\r\n```verilog\r\n// in ibex_compressed_decoder.sv\r\n `ASSERT(IbexInstrLSBsKnown, valid_i |->\r\n !$isunknown(instr_i[1:0]))\r\n\r\n// in prim_assert.sv\r\n`define ASSERT(__name, __prop, __clk = `ASSERT_DEFAULT_CLK, __rst = `ASSERT_DEFAULT_RST) \\\r\n`ifdef INC_ASSERT \\\r\n __name: assert property (@(posedge __clk) disable iff (__rst !== '0) (__prop)) \\\r\n else `ASSERT_RPT(`PRIM_STRINGIFY(__name), `PRIM_STRINGIFY(__prop)) \\\r\n`endif\r\n\r\n// Converts an arbitrary block of code into a Verilog string\r\n`define PRIM_STRINGIFY(__x) `\"__x`\"\r\n\r\n`define ASSERT_RPT(__name, __msg) \\\r\n`ifdef UVM \\\r\n assert_rpt_pkg::assert_rpt($sformatf(\"[%m] %s: %s (%s:%0d)\", \\\r\n __name, __msg, `__FILE__, `__LINE__)); \\\r\n`else \\\r\n $error(\"[ASSERT FAILED] [%m] %s: %s\", __name, __msg); \\\r\n`endif\r\n\r\n```\r\n\r\nGiven this code, I'm assuming the error message actually comes from the fact that `prop` (the second argument to `ASSERT`) is converted to a string before being used in `ASSERT_RPT`, and this use of `prop` with newlines isn't liked by Questa.\r\n\r\nAccording to SV2017, the definition of a string literal is \r\n\r\n\r\n\r\nWhich indicates our code is actually wrong. I see a couple of options:\r\n- Remove the reporting of the property in `ASSERT_RPT`, and only report the message.\r\n- Add backslashes to the end-of-line of each multi-line property. I'm not sure if that's actually valid for the non-string case?\r\n- Avoid newlines in properties when writing `ASSERT` macros.\r\n\r\n\r\n@danghai:\r\n- First, let's check if the hypothesis holds: Does the warning go away if you remove the `ASSERT_RPT()` call from the definition of the `ASSERT` macro?\r\n- Can you try to add a backslash at the end of the property in `ibex_compressed_decoder.sv`, e.g. \r\n\r\n ```systemverilog\r\n `ASSERT(IbexInstrLSBsKnown, valid_i |-> \\\r\n !$isunknown(instr_i[1:0]))\r\n ```\r\n\r\n\r\nQuesta version info: QuestaSim-64 qrun 2019.4 Utility 2019.10 Oct 15 2019\r\n\r\n\r\nCC @msfschaffner @sriyerg "}
+{"org": "lowRISC", "repo": "ibex", "number": 666, "state": "closed", "title": "[rtl] IF stage timing fix", "body": "- ready_i input to the prefetch buffer factored both it's own valid_o\r\n output and the pc_set branch signal, neither of which are required.\r\n- Refactoring the ready_i signal to just id_in_ready_i improves timing\r\n significantly for the icache.\r\n- Also removed offset_in_init signal which appeared to serve no purpose."}
+{"org": "lowRISC", "repo": "ibex", "number": 661, "state": "closed", "title": "ERROR while compiling assembler programs", "body": "Hello, I got the exact error that was described in Issue: https://github.com/lowRISC/ibex/pull/657.\r\n\r\nAfter updating the repository, I run the make file and get the following error:\r\n\r\n```\r\nout/seed-24236/instr_gen/asm_tests/riscv_csr_test_0.S:526: Error: illegal operands li x2,0x0x8ffffffc \r\n\r\nout/seed-24236/instr_gen/asm_tests/riscv_csr_test_0.S:533: Error: illegal operands li x2,0x0x8ffffffc\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 659, "state": "closed", "title": "[ml] add condensed test targets for ML (and constraints)", "body": "Currently only the riscv_rand_test target fully works with RTL simulation, the other two test targets both fail RTL simulation due to some testbench error, which I think was introduced by a previous commit, will debug this issue.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 658, "state": "closed", "title": "Remove stray semicolon", "body": "This seems to cause lint errors with ncsim (see bug #650)."}
+{"org": "lowRISC", "repo": "ibex", "number": 656, "state": "closed", "title": "Loop fix", "body": "Two commits on this, one is a lint waiver fix that is unrelated to the change but without it I'm getting lint error locally, maybe a Verilator version issue (I'm using 4.028) and otherwise I don't know how it got past CI in the first place?"}
+{"org": "lowRISC", "repo": "ibex", "number": 650, "state": "closed", "title": "unexpected semicolon in ibex_id_stage.sv", "body": "Looks, like there is small typo [here](https://github.com/lowRISC/ibex/blob/cb9413e38bc43117a0a5dfd7221bbf8155815478/rtl/ibex_id_stage.sv#L687). \r\nWarning message:\r\n ncvlog: *W,UEXPSC (ibex/rtl/ibex_id_stage.sv,687|89): Ignored unexpected semicolon following SystemVerilog description keyword (endif)."}
+{"org": "lowRISC", "repo": "ibex", "number": 649, "state": "closed", "title": "Path from data_error_i to instr_req_o", "body": "As reported by this OpenTitan issue: https://github.com/lowRISC/opentitan/issues/1657 there may be a path from data_error_i to instr_req_o. We probably don't want this (for one thing it is a long feedthrough path that will cause timing issues)."}
+{"org": "lowRISC", "repo": "ibex", "number": 638, "state": "closed", "title": "[dv] remove usage of 0x from sim flow", "body": "As per some discussions in #620 , this PR removes the `0x` prefixing for the signature_addr in various steps of the Makefile flow.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 637, "state": "closed", "title": "[dv] Increase timeouts to fix failures", "body": "I was seeing various failures due to these timeouts. Upon looking at the waves seems things were working fine it just needed more time to get to the store instructions that output the CSR info wait_for_csr_write is waiting for. So I added a large timeout increase here (it'll still die pretty quickly if we actually need the timeout).\r\n\r\nSurprised this has only just become an issue, perhaps we're seeing a greater range of delays on the iside interface so the instruction sequence leading up to the SW that outputs what we're waiting for takes longer?"}
+{"org": "lowRISC", "repo": "ibex", "number": 633, "state": "closed", "title": "update riscv_core_setting", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 632, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@33ded53", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 33ded53224abca7247e1a49efd7369278f2683cb\r\n\r\n* Move instruction sections together for multi-harts (google/riscv-\r\n dv#495) (taoliug)\r\n* add seed capability to CSR test generation (Udi Jonnalagadda)\r\n* fix pmp/shifted_addr compile warning (google/riscv-dv#493)\r\n (udinator)\r\n* User long jump to switch between different harts (google/riscv-\r\n dv#491) (taoliug)\r\n* Fix s_region generation (google/riscv-dv#487) (taoliug)\r\n* update rv32imc/riscv_pmp_test testlist options (google/riscv-dv#486)\r\n (udinator)\r\n* Fix default value of num_of_harts (google/riscv-dv#485) (taoliug)\r\n* Add shared memory region for multi-harts AMO (google/riscv-dv#484)\r\n (taoliug)\r\n* Add a runtime option num_of_harts (google/riscv-dv#483) (taoliug)\r\n* Add multi-thread support (google/riscv-dv#482) (taoliug)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 631, "state": "closed", "title": "Tiny docs fix in examples/simple_system", "body": "Missing \"can\" (which sounds a bit like a pirate!) and full stop."}
+{"org": "lowRISC", "repo": "ibex", "number": 630, "state": "closed", "title": "Dump to VPD in dv/uvm if Verdi is not available", "body": "If VERDI_HOME is not set, calling fsdbDumpfile makes VCS hang with an\r\nerror message. This patch checks whether we think FSDB dumping is\r\nactually going to work and, if not, dumps with the default VCD+\r\nformat (also called VPD) instead."}
+{"org": "lowRISC", "repo": "ibex", "number": 629, "state": "closed", "title": "Fix previous gitignore change for uvm directory rejig", "body": "I'd written the original patch (b157573) on a branch that didn't\r\ninclude commit 2431551 (which moves stuff that was in dv/uvm into\r\ndv/uvm/core_ibex). Apparently, I'd fixed up the rule for the output\r\ndirectory, but I'd missed the ucli.key file."}
+{"org": "lowRISC", "repo": "ibex", "number": 627, "state": "closed", "title": "Add .gitignore rules for auto-generated files", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 626, "state": "closed", "title": "Improve docs for getting started in verification.rst", "body": "The important change is that we now tell the user to configure spike\r\nwith --enable-misaligned. This is needed because Ibex handles\r\nmisaligned loads and stores rather than jumping to a trap handler (the\r\ndefault behaviour in spike).\r\n\r\nThis patch also points a user at the manual from the riscv-dv\r\nrepository, rather than duplicating the list of steps here."}
+{"org": "lowRISC", "repo": "ibex", "number": 625, "state": "closed", "title": "Optimize Bit-Shift Operations for FPGA Implementation", "body": "Hi everyone,\r\n\r\nI have investigated the possibility to optimize the bit-shift operation on FPGA targets by using Multipliers to incorporate the logic. I have drafted two versions of this. 'NoFlatten' and 'Rebuilt' refer to the `FLATTEN_HIERARCHY` synthesis attribute used when generating the results.\r\n\r\n* [ibex_alu_dspshift.sv](https://github.com/ganoam/ibex/blob/fpga-opt-dspbarrelshift/rtl/ibex_alu_dspshift.sv)\r\n Two 16x16 multiplier units describe left shifts. The resulting upper and lower bit arrays are reordered using the shift amount MSB. Concatenation is handled via addition, using one more DSP.\r\n ```\r\n DSP Utilization: 3\r\n Total LUT Utilization: 2478 / 2334 (NoFlatten / Rebuilt)\r\n ```\r\n\r\n* [ibex_alu_circulardspshift.sv](https://github.com/ganoam/ibex/blob/fpga-opt-dspbarrelshift/rtl/ibex_alu_circulardspshift.sv)\r\n Cyclic barrel shifter, using 4 8x16 bit multipliers. The two MSB of `shift_amt` are used for the byte ordering MUX. Right shifts are done by shifting by `32-shift_amt`. The results are generated using a bitmask for shifted-out bits. Idea from: [Implementing Barrel Shifters Using Multipliers](https://www.xilinx.com/support/documentation/application_notes/xapp195.pdf)\r\n \r\n ```\r\n DSP Utilization: 4\r\n LUT Utilization: 2440 / 2339 (NoFlatten / Rebuilt)\r\n ```\r\nThe baseline implementation's resource utilization is:\r\n```\r\nTotal LUT Utilization: 2486 / 2339\r\n```\r\n\r\nWe can see a slight improvement when we prohibit hierarchy flattening during synthesis. However by when synthesising with the default settings, no improvements are observed. \r\n\r\nI suggest to not persue the issue further.\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 624, "state": "closed", "title": "Modifiy Performance Counter for DSP Inference", "body": "This commit modifies the cs_registers module to allow inference of DSP\r\nslices to absorb counter logic. A preprocessor variable is introduced\r\nto include the required synthesis pragma. DSP inferrence is supported\r\nfor Xilinx FPGA devices featuring DSP48E1 slices or similar and for\r\ncounter widths up to 48 bit.\r\n\r\nThe resulting relative logic utilizations with respect to the non-DSP\r\n32 bit counter implementation are 84% and 90% respectively for 32 and\r\n48 bit counters. For 32 bit counters only, the corresponding\r\nflip-flops can be incorporated into the DSP's output pipeline\r\nregister, resulting in a reduction of the number of flip-flops to 50%.\r\nIn order to infer DSP slices for performance counters, define the\r\npreprocessor variable XILINX_DSP_COUNTERS.\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 622, "state": "closed", "title": "Add support for Qrun Questa", "body": "Hi, I make PR to support for qrun simulator. I try to run; however, I got a lot of warning for compilation, and optimization. I attach the output file. Could you help me take the look? I hope qrun can support for running `ibex`. Thank you\r\n[qrun_compile_optimize.log](https://github.com/lowRISC/ibex/files/4238391/qrun_compile_optimize.log)\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 620, "state": "closed", "title": "Separate 0x from hex number", "body": "Hey!\r\nI add `if` statement for separate `0x` from hex number, because when `0x` is argument of `atohex`, this function returns wrong number"}
+{"org": "lowRISC", "repo": "ibex", "number": 616, "state": "closed", "title": "VCS compile fix", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 615, "state": "closed", "title": "[doc] Fix reference link", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 614, "state": "closed", "title": "CI: Pin riscv-compliance repo to specific commit", "body": "Recently changes in the RISC-V compliance repo have caused our tests to\nfail. That indicent highlighted the issue that we use the latest master\nversion of the compliance suite without pinning the version.\n\nThis PR fixes that by pinning to a specific version where our tests\nstill succeeded.\n\nUpstream PR to fix actual failure: https://github.com/riscv/riscv-compliance/pull/92\nWorks around #608"}
+{"org": "lowRISC", "repo": "ibex", "number": 613, "state": "closed", "title": "[rtl] Change misa for RV32E", "body": "Following RISC-V privileged architecture version 1.11,\r\nthe \"E\" bit of misa should return the complement of the \"I\" bit.\r\n\r\nSet the \"I\" bit only if RV32E is not used.\r\n\r\nCloses lowRISC/ibex#612."}
+{"org": "lowRISC", "repo": "ibex", "number": 612, "state": "closed", "title": "CSR misa \"I\" bit value for \"E\" extension", "body": "The \"I\" bit of the CSR misa is always set:\r\nhttps://github.com/lowRISC/ibex/blob/f90faa6ca365e02047d456ac3ad084ecc457ada0/rtl/ibex_cs_registers.sv#L113\r\n\r\nBut I think it should no be set if RV32E is used.\r\nThe priv spec says it 3.1.1 p. 16\r\n\r\n> The “I” bit will be set for RV32I, RV64I, RV128I base ISAs, and the “E” bit will be set for RV32E.\r\n\r\nand\r\n\r\n>The “E” bit is read-only.\r\n>Unless misa is hardwired to zero, the “E” bit always reads as the\r\n>complement of the “I” bit. An implementation that supports both RV32E and RV32I can select\r\n>RV32E by clearing the “I” bit.\r\n\r\nAny objections to the following change?\r\n```verilog\r\n| 32'(!RV32E) << 8)\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 610, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@a216407", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision a216407f3ebb6c1aef2410a3cef1513bedd2dff5\r\n\r\n* Improve pmp config object - enable cmdline args (Udi Jonnalagadda)\r\n* Fix ovpsim setting (google/riscv-dv#478) (taoliug)\r\n* IUS - enable rand structs in simulation (google/riscv-dv#477)\r\n (udinator)\r\n* fix macro definition compile issue (Udi Jonnalagadda)\r\n* add ISS command line options (google/riscv-dv#474) (udinator)\r\n* Add style check (Weicai Yang)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 609, "state": "closed", "title": "Ibex coremark", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 608, "state": "closed", "title": "CI failing due to riscv-compliance updates", "body": "Just a quick note that there is currently a CI failure in the riscv-compliance build. Fix is in progress riscv/riscv-compliance#92 "}
+{"org": "lowRISC", "repo": "ibex", "number": 603, "state": "closed", "title": "Document and enforce minimum Verilator version", "body": "We continue to use features in Verilator which require a sufficiently up-to-date version of Verilator. We need to\r\n\r\n- Document our minimum-supported Verilator version.\r\n- Somehow signal to users that they are running a version of Verilator which is too old. Ideally, this check happens in the fusesoc run to display this information when it is actually needed.\r\n\r\nI'll give it a try with a fusesoc hook."}
+{"org": "lowRISC", "repo": "ibex", "number": 602, "state": "closed", "title": "DO NOT MERGE: test", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 601, "state": "closed", "title": "Optimize CSRs and performance counters for FPGA Implementation", "body": "The CSRs and most importantly performance counters map poorly on FPGA. We should investigate the effect of the performance counter width on resource utilization and timing (64-bit counters are known to map badly to FPGA) and see if they can e.g. be implemented differently (Xilinx DSP slices can be used to implement 48-bit counters)."}
+{"org": "lowRISC", "repo": "ibex", "number": 600, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@1fab1cf", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 1fab1cfa2ec4c372b093a0304b19a3f3bc675966\r\n\r\n* add ISS command line options (google/riscv-dv#474) (udinator)\r\n* Add style check (Weicai Yang)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 599, "state": "closed", "title": "[dv] add command line PMP option configurability", "body": "- PMP options num_regions and granularity are needed to parameterize the RTL at compile time, and are also needed by the riscv-dv generator and ISS simulator, so these options are now controlled through the Makefile and their defaults are set accordingly\r\n- Cleaned up Makefile slightly to have consistent use of plaintext variables for ease of use\r\n- The ISS options code is also implemented in the generator, in PR https://github.com/google/riscv-dv/pull/474\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 598, "state": "closed", "title": "Fix failing pip install in CI", "body": "Fixes #597"}
+{"org": "lowRISC", "repo": "ibex", "number": 597, "state": "closed", "title": "Fix zypp dependency on Python 3.5", "body": "In [CI we get](https://dev.azure.com/lowrisc/ibex/_build/results?buildId=7828&view=logs&j=e92b124b-3ef9-5461-84e3-a5c4020c184a&t=c6688988-a2fe-54a8-1baf-ba20316d2af5)\r\n\r\n```\r\nTraceback (most recent call last):\r\n File \"/usr/local/bin/fusesoc\", line 6, in \r\n from pkg_resources import load_entry_point\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 3253, in \r\n @_call_aside\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 3237, in _call_aside\r\n f(*args, **kwargs)\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 3266, in _initialize_master_working_set\r\n working_set = WorkingSet._build_master()\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 584, in _build_master\r\n ws.require(__requires__)\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 901, in require\r\n needed = self.resolve(parse_requirements(requirements))\r\n File \"/usr/local/lib/python3.5/dist-packages/pkg_resources/__init__.py\", line 787, in resolve\r\n raise DistributionNotFound(req, requirers)\r\npkg_resources.DistributionNotFound: The 'zipp>=0.5' distribution was not found and is required by importlib-metadata\r\n##[error]Verilog lint failed. Run 'fusesoc --cores-root . run --target=lint lowrisc:ibex:ibex_core_tracing' to check and fix all errors.\r\n```\r\n\r\nThe root cause is that the zipp library did a release that doesn't support Python 3.5 any more. It's not quite clear to me yet why the dependency resolution logic in pip chooses this version then, and doesn't stick with an older version. \r\n\r\nI've seen the same problem (with a slightly different error message) in OpTiMSoC as well for ~2 weeks and hoped it would be resolved by just waiting, turns out that's not the case."}
+{"org": "lowRISC", "repo": "ibex", "number": 596, "state": "closed", "title": "Docs: Enable PR builds of readthedocs", "body": "Enable readthedocs builds per pull request.\r\n\r\nI've emailed RTD support to get this feature enabled for our project, and will follow up once that's done."}
+{"org": "lowRISC", "repo": "ibex", "number": 594, "state": "closed", "title": "[syn] Fix synthesis script", "body": "* prim_assert now an include so add appropriate include dir\r\n* remove FPGA reg file from synthesised files"}
+{"org": "lowRISC", "repo": "ibex", "number": 593, "state": "closed", "title": "update testlist typo", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 591, "state": "closed", "title": "[rtl] Fix assertion issues", "body": "Fixes #548\r\n\r\nFixes the long standing assertion problem from the linked issue as well as a new problem that was introduced with the branch target ALU."}
+{"org": "lowRISC", "repo": "ibex", "number": 590, "state": "closed", "title": ":zap: Reduce latency of slow multiplier", "body": "- The slow multiplier is modified to terminate iterations early instead\r\n of always going the full 32 iterations.\r\n- Multiplications now terminate early after clog2(`op_b`) iterations.\r\n- The slow multiplier can be further optimized by swapping the smaller\r\n operand into `op_b` when in the `MD_IDLE` state."}
+{"org": "lowRISC", "repo": "ibex", "number": 589, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@6e2bc2e", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 6e2bc2e01fb20799c9eff29a26852eb1917b977a\r\n\r\n* fix a missed syntax error in pmp_cfg (Udi Jonnalagadda)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 584, "state": "closed", "title": "[doc] Riviera-PRO instructions for Simple System", "body": "@dawidzim does this look ok to you?"}
+{"org": "lowRISC", "repo": "ibex", "number": 583, "state": "closed", "title": "Extend riscv-compliance description", "body": "Include all tests in the description which can be executed for Ibex and\r\nriscv-compliance."}
+{"org": "lowRISC", "repo": "ibex", "number": 581, "state": "closed", "title": "[verilator] Fix ELF loading", "body": "In `VerilatorMemUtil::WriteElfToMem`, the verilator memory is written\r\nwith the ELF segment data, 4 bytes at a time . If the segment size isn't\r\na multiple of 4 (e.g. when using the RISC-V C extension) the last word\r\nwouldn't be written. This patch rounds the size up to a multiple of 4,\r\nsolving that issue."}
+{"org": "lowRISC", "repo": "ibex", "number": 580, "state": "closed", "title": "Fix FPGA part number for Arty A7-100T", "body": "For some reason the part number between the Arty A7-35T and the Arty\r\nA7-100T differs by 1 letter (TICSG vs TCSG). This patch fixes the part\r\nnumber for the Arty A7-100T to remove the \"i\".\r\n\r\nSigned-off-by: Stephano Cetola "}
+{"org": "lowRISC", "repo": "ibex", "number": 579, "state": "closed", "title": "[tracking] Use Verible for lint", "body": "We want to use verible_lint (https://github.com/google/verible) as one of our lint tools. There are a couple things to be solved first.\r\n\r\nA run of Verible today shows that most lint rules match our use of SV, with the exception of localparam naming (which verible_lint expects to be UpperCamelCase, while we go for ALL_CAPS).\r\n\r\n- [x] Extend edalize to support verible: https://github.com/olofk/edalize/issues/95\r\n- [x] Add Verible as a lint target to our .core files: #686 \r\n- [x] Add Verible in non-enforcing mode to CI. #686 \r\n\r\nIf we want to run Verible in \"enforcing\" mode (e.g. in CI) we additionally need:\r\n- [x] Waiver support: https://github.com/google/verible/issues/105\r\n- [x] parse error for define-to-string conversions: https://github.com/google/verible/issues/166\r\n- [x] string parameters without type: https://github.com/google/verible/issues/167 or waivers. #735 \r\n\r\nOptional, but very helpful:\r\n- [x] Have pre-compiled binaries of verible available. Verible requires a C++17-capable compiler, which typically isn't available by default in our supported platforms, e.g. RHEL7. Binaries are statically linked, so should be reasonably easy to distribute. Opened https://github.com/google/verible/issues/168 to see if that's something that Verible can provide us with.\r\n- [x] Use config files #736 \r\n\r\nCC @fangism @msfschaffner @mithro"}
+{"org": "lowRISC", "repo": "ibex", "number": 578, "state": "closed", "title": "Update Ibex Simple System readme for Riviera-PRO", "body": "Hey!\r\nCan you update Ibex Simple System readme for Riviera-PRO?\r\nTo build and run this example on Riviera-PRO we need to use command:\r\n\r\nfusesoc --cores-root=. run --target=sim --tool=rivierapro lowrisc:ibex:ibex_simple_system --RV32M=1 --RV32E=0 --SRAM_INIT_FILE=../../../examples/sw/simple_system/hello_test/hello_test.vmem --vsim_options=+ibex_tracer_file_base=test_results\r\n\r\n--SRAM_INIT_FILE - path to hello_world binary\r\n--vsim_options=+ibex_tracer_file_base=output_file_name - here we can change the output file name"}
+{"org": "lowRISC", "repo": "ibex", "number": 574, "state": "closed", "title": "Fetch FIFO blocks instruction request when full.", "body": "Hi everyone, \r\n\r\nI may have found an issue with the prefetch buffer. The situation: I have implemented a second memory port in the simple system example (PR #571) and run both the hello_test example and coremark on it. Since I would expect no memory contention on the instruction line, i would expect to record less IFetch waits with coremark. however the opposite was the case: Using the separated data and instruction ports, coremark recoreded around 200 more IFetch wait than using a single memory port.\r\nFor the hello_test example, I have found that the new implementation takes two more cycles than the baseline, which already is unexpected. So I have analyzed the situation using this simulation. By comparing the traces of the two hello_test runs, I think I can pinpoint exactly where the problem is:\r\n\r\n\r\nThe top level instruction request signal `instr_req_o` is set in `prefetch_buffer.sv` lines 108-111 by the signal `valid_req`: \r\n``` \r\n// Make a new request any time there is space in the FIFO, and space in the request queue\r\nassign valid_new_req = req_i & (fifo_ready | branch_i) & ~rdata_outstanding_q[NUM_REQS-1];\r\nassign valid_req = valid_req_q | valid_new_req;\r\n```\r\nSo if we re not branching, a memory request can only be issued when the fifo is ready. The fifo ready signal is set in `ibex_fetch_fifo.sv` line 155:\r\n```\r\nassign in_ready_o = ~valid_q[DEPTH-NUM_REQS]; // DEPTH = 3, NUM_REQS=2\r\n```\r\nNow, by comparing the traces I have found that the delay is introduced around 154ns into the hello_test simulation. The waveform for the baseline implementation is here:\r\n\r\n\r\nThe waveform for the implementation with dual port memory is here:\r\n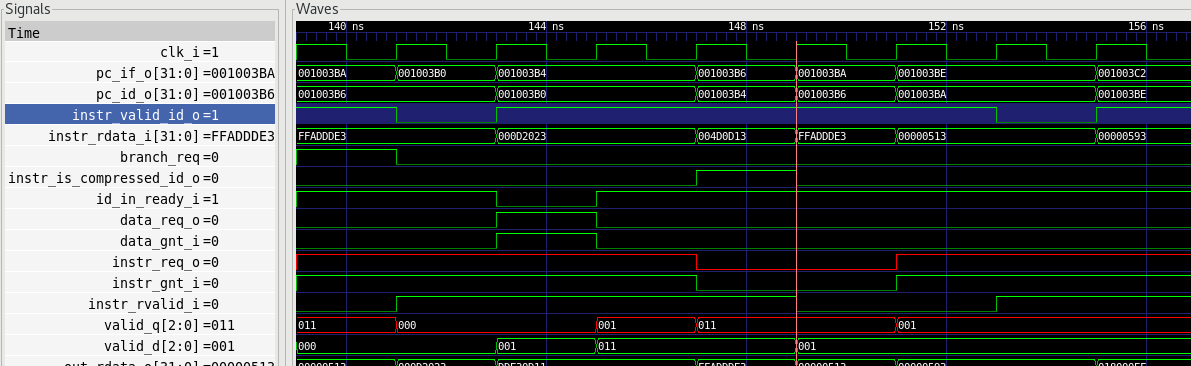\r\n\r\n\r\nAt 143ns you can see that the pipeline is stalled due to the `id_stage` being busy. This is a store-word instruction, so it makes a data request. In the baseline implementation the data and instruction line is shared, so in the meantime no instruction can be fetched. However for the dual-port implementation a new instruction is fetched, and the fetch-fifo after that has stored two memory words. therefore the fifo ready signal will be low, and no new memory request will be made (`instr_req_o`). \r\nThe first instruction (`PC=001003B4`) in the FIFO is compressed. So, after that the word can not be popped and the fifo is still full. Here is content of the fifo at that point (at 149ns):\r\n```\r\n | 31 16 | 15 0 |\r\nFIFO entry 0 | PC001003B6 [15:0] | PC001003B4 [15:0] |\r\nFIFO entry 1 | PC001003BA [15:0] | PC001003B6 [31:16]| \r\n```\r\nSo instruction `001003B6` is fetched and in the next cycle the fifo is not full anymore. \r\n```\r\n | 31 16 | 15 0 |\r\nFIFO entry 0 | PC001003BA [15:0] | | \r\nFIFO entry 0 | | |\r\n```\r\nSo `instr_req_o` is raised again (at 151ns), but `instr_rvalid_i` is only received in the cycle after that, leading to a 1 cycle stall, since the instruction in the fifo is incomplete.\r\n\r\nFor the baseline implementation the fifo does not get full and therefore `instr_req_o` is never lowered and we never have to wait for `instr_rvalid_i`. That's the reason why the single-port implementation finishes faster.\r\n\r\nSo, as far as I can tell, at least while there are unaligned, uncompressed instructions in the fetch fifo, it can never remain full. Thus there is always a stall while waiting for `instr_rvalid_i`. \r\n\r\n\r\nI think the fundamental problem is that no simultaneous pop and push is possible while the FIFO is full. If we would take into account the anticipated next-cycle occupancy when setting the fifo `in_ready_o` signal, i. e. change line 155 `ibex_fetch_fifo.sv` to\r\n```\r\nassign in_ready_o = ~valid_d[DEPTH-NUM_REQS]; \r\n```\r\nthe memory request could be done one cycle earlier and the valid signal will arrive only once there is space in the fetch FIFO. \r\n\r\nI have run the hello_test and coremark programs using this fix. The number of IFetch waits for coremark using the fix on the baseline (single-port) implementation decreases from 14968 to 5215. Total ticks decrease from 423620 to 416639. \r\n\r\nExecuting the hello_test program, there is no improvement for the single-port implementation. However the additional two cycles of latency that were observed for the dual-port implementation disappear. \r\n\r\nAlso coremark now executes with exactly the same statistics for single- and dual-port implementation. This is disapointing, but I think very well possible for non-data intensive workloads. \r\n\r\nI do not know if my fix is fully correct, since there are some parts in the Prefetch Buffer and the Fetch FIFO, that I don't yet completely understand. But I hope that my account may help somebody investigate and fix the problem.\r\n\r\nI will attatch the output of my simulation runs. For coremark I will omit the trace_core log and waveforms, since those are huge files. If you are interested in them let me know.\r\n\r\n[edit: changed this file, since I have mixed up waveform files. ]\r\n[prefetch-buff-issue_sim-out_new.zip](https://github.com/lowRISC/ibex/files/4127676/prefetch-buff-issue_sim-out_new.zip)\r\n\r\n\r\n\r\n\r\nNomenclature of the folders: master = single-port implementation, perf-eval = dual-port implementation\r\n\r\nIn perf-eval_hello_test-out, there is a gtkwave save-file `waveconfig.gtkw which you can use with all the simulation waveforms to directly display the waveforms as they are in my screenshots.\r\n\r\ncheers, Noam\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 573, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@f7e35d7", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision f7e35d7939a27ae17b0481eb070e9a36ea335d1f\r\n\r\n* remove deprecated code (google/riscv-dv#460) (udinator)\r\n* Integrate directed C test with yaml flow (google/riscv-dv#455) (Hai\r\n Hoang Dang)\r\n* Qrun is missing -access=wrc option (google/riscv-dv#457) (Hai Hoang\r\n Dang)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 571, "state": "closed", "title": "[examples] Add Dual-Port Memory to Simple System", "body": "This commit adds a separate memory ports for instruction and data\r\nfetches to the Simple System example.\r\n\r\n* Add Dual-Port RAM with 1 cycle read/write delay, 32 bit words.\r\n\r\n* Introduce parametric signal width definitions for bus implementation\r\n to work with a single host / device.\r\n\r\n* Modify Simple System top module to instantiate the new dual-port RAM."}
+{"org": "lowRISC", "repo": "ibex", "number": 570, "state": "closed", "title": "RTL fixes discovered by running Riviera", "body": "This is a spin-off from https://github.com/lowRISC/ibex/pull/566 with only the fixes that affect RTL. All issues were caught when running Riviera 2019.10 on our code base.\nThe fixes are generally and not related to Riviera per se, keeping them in this PR to reduce the dependency chain. Support for Riviera running DV will come in a follow-up."}
+{"org": "lowRISC", "repo": "ibex", "number": 569, "state": "closed", "title": "Add missing casts to enums (most likely in DV code only)", "body": "@danielmlynek discovered this in https://github.com/lowRISC/ibex/pull/566:\r\n\r\n\r\nAll line where illegal assignment are done is now marked with warning ie:\r\nWARNING VCP2694 \"Assignment to enum variable from expression of different type.\" \"/home/danielm/gitlab/ibex/dv/uvm/tests/core_ibex_test_lib.sv\" 781 1\r\n\r\nThis argument will be no longer needed when explicit cast will be used on such illegal assignment ie in file :\r\n /home/danielm/gitlab/ibex/dv/uvm/tests/core_ibex_test_lib.sv, line 201\r\n` operating_mode = core_init_mstatus[12:11];`\r\nneed to be changed to:\r\n` operating_mode = priv_lvl_e'(core_init_mstatus[12:11]);`\r\n\r\n\r\n\r\n@danielmlynek do you know of more cases where such a cast is missing?\r\n\r\n@msfschaffner I suppose currently the DV code isn't running through Lint, which should have caught that. Can you think of an easy way to lint that code as well? (Either here, or in OpenTitan.)"}
+{"org": "lowRISC", "repo": "ibex", "number": 568, "state": "closed", "title": "Third pipe stage", "body": "As the branch target ALU isn't in yet I'm afraid this PR is both branch target ALU and third pipeline stage, it will be rebased on master once that's in (i.e. this PR will be 3rd pipe stage only before it gets merged, it isn't intended to do both at once)\r\n\r\nThis is a draft for now as there's three things that must be done before it is committed:\r\n\r\n* Update the documentation\r\n* Run the riscv-dv testbench on UVM on the 2 stage configuration and check I haven't broken anything\r\n* Check I haven't killed timing on the FPGA for two stage\r\n\r\nI think performance counters may also be a bit dodgy.\r\n\r\nriscv compliance passes for both 2 and 3 stage configs, coremark runs and gives around a 14.5% speed-up vs branch target ALU alone (when using a hacked up version of simple system that gives dual-port memory, I believe @ganoam is working on a proper version of this)"}
+{"org": "lowRISC", "repo": "ibex", "number": 567, "state": "closed", "title": "Reads of `mip` CSR should not depend on corresponding fields in `mie`", "body": "Currently, the bits in `mip` are ANDed with those in `mie`:\r\nhttps://github.com/lowRISC/ibex/blob/43752a6c193893d4750daceff5f284f22da52f77/rtl/ibex_cs_registers.sv#L241-L245\r\nThis is at odds with the specification, which states the mechanisms by which those bits would be cleared:\r\n- The MTIP bit is read-only and is cleared by writing to the memory-mapped machine-mode timer compare register\r\n- MEIP is set and cleared by a platform-specific interrupt controller\r\n\r\nAnd while it does state that \"An interrupt _i_ will be taken if bit _i_ is set in both `mip` and `mie`, and if interrupts are globally enabled.\", it makes no mention of the asserted bit(s) in `mip` depending on their `mie` counterpart(s).\r\n\r\nLooking for other interpretations of this issue, I found that qemu-riscv treats `mip` similarly, where `mie` used to determine if CPU execution should be interrupted, but not whether bits are asserted in `mip`. A survey of some other open-source RISC-V cores ([e200](https://github.com/SI-RISCV/e200_opensource), [scr1](https://github.com/syntacore/scr1)) yielded the same result: reads of `mip` yielding results not ANDed through `mie`.\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 566, "state": "closed", "title": "Support for Riviera 2019 10", "body": "Initial support for Riviera 2019.10 and some issue fixed in ibex it self.\r\nThere is also riscv-dv changed to work with Riviera added. "}
+{"org": "lowRISC", "repo": "ibex", "number": 562, "state": "closed", "title": "failed in running make", "body": "the hierarchy of riscv compiler is \r\n/opt/riscv/\r\n|--bin\r\n|--include\r\n|--lib\r\n|--libexec\r\n|--riscv32-unknown-elf\r\n|--riscv64-unknown-linux-gnu\r\n|--share\r\n|--sysroot\r\n\r\nin example/sw/led directory, run command: make CC=/opt/riscv\r\nlog is:\r\n\r\n/opt/riscv -march=rv32imc -mabi=ilp32 -static -mcmodel=medany -fvisibility=hidden -nostdlib -nostartfiles -Wall -g -Os -MMD -c -o led.o led.c\r\nmake: execvp: /opt/riscv: Permission denied\r\nMakefile:50: recipe for target 'led.o' failed\r\nmake: *** [led.o] Error 127\r\n\r\nAny advice? thanks."}
+{"org": "lowRISC", "repo": "ibex", "number": 560, "state": "closed", "title": "[DV] Test nested interrupts", "body": "Tests scenarios where Ibex is executing an interrupt handler and receives a second set of interrupts in the middle of the first handler.\r\nAs per the discussion in #557, I have eliminated nested NMI interrupt test scenarios from this testcase.\r\nThis PR relies on https://github.com/google/riscv-dv/pull/444 to be functionally correct, so will only merge this PR after vendoring the latest riscv-dv copy.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 559, "state": "closed", "title": "[rtl] Add Single Cycle Multiplier for FPGA", "body": "This commit adds a single cycle multiplier implementation designed to be\r\nsynthesized into DSP block primitives.\r\n\r\nFor the artya7-100 example the multiplier is implemented by 4 DSP48E1\r\nslices. Savings in terms of logic LUTs is minimal, however faster\r\nmultiplication capability will result in higher IPC. "}
+{"org": "lowRISC", "repo": "ibex", "number": 557, "state": "closed", "title": "Nested NMI interrupts", "body": "Hi,\r\nWhen debugging a test case in which I asserted two nested NMI interrupts to force the core to respond to the second NMI interrupt while executing the handler for the first NMI, resulting in this waveform:\r\n\r\nAt the location of the cursor, Ibex is in the middle of executing the NMI interrupt handler and sees the input interrupt lines being changed to another set of incoming interrupts; these new interrupts are processed when `csr_save_cause_i` goes high at `3,843,000ns`. Note that `nmi_mode_q` in the controller is high before the second set of interrupts due to the NMI detection.\r\nHowever, this second set of interrupts also includes a NMI, but Ibex sets `mcause` to `0b11_1110 = 0x3e` indicating a fast interrupt, causing a testbench failure since we should expect `mcause` to be `0b11_1111 = 0x3f` for the NMI. This mismatch is due to the `IRQ_TAKEN` state in the controller, specifically this section:\r\n.\r\nSince `nmi_mode_q` is already high from the first NMI that Ibex was initially handling, the core does not recognize the NMI asserted inside of the interrupt handler, and as such delegates it to be a fast interrupt, causing a mismatch in `mcause`.\r\n\r\nAnother potential issue that could arise is from this section in the CSR register file:\r\n\r\nSince Ibex restores CSR state from the `mstack` CSRs only in the case of NMI interrupts, I don't think the core would be able to correctly return from a series of nested NMIs, as the saved state from the first NMI in the `mstack` CSRs would be overwritten by the state of the second NMI.\r\n\r\nGiven these potential issues, my question is if this situation of nested NMI interrupts is something that Ibex can handle at all?"}
+{"org": "lowRISC", "repo": "ibex", "number": 555, "state": "closed", "title": "[rtl] Add FPGA Register File", "body": "This commit adds a register file designed to be synthesized into FPGA\r\nsynchronous-write / asynchronous-read design elements.\r\n\r\nFor the artya7-100 example, the register file is implemented by 12\r\nRAM32M primitives, conserving approximately 600 Logic LUTs and 1000\r\nflip-flops at the expense of 48 LUTRAMs.\r\n\r\nSigned-off-by: ganoam "}
+{"org": "lowRISC", "repo": "ibex", "number": 551, "state": "closed", "title": "[lint] Delete outdated comment in lint target", "body": "Signed-off-by: Michael Schaffner "}
+{"org": "lowRISC", "repo": "ibex", "number": 548, "state": "closed", "title": "Illegal instruction assertion fire", "body": "Hi all,\r\nI'm seeing a potential issue where, upon decoding an illegal instruction that contains `x` within it, Ibex will display that the instruction is illegal, but assertions in the LSU will fire, causing the simulation to error out. The simulation log is shown below,\r\n\r\nWe can see that at `PC=0x80006232` Ibex recognizes that there is an illegal instruction, and the core does in fact respond correctly by trapping to the proper exception handler, but then the `IbexDataOffsetKnown` assertion in the LSU constantly fires due to an `x` from this instruction propagating through the design, failing the simulation.\r\nWhat do you think about additionally qualifying these assertions that use `$isunknown` with a check ensuring the instruction is not illegal?\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 546, "state": "closed", "title": "[rtl] Update prim assert with OpenTitan version", "body": "This updates the assertion macros in `prim_assert` to coincide with the ones used in OpenTitan. \r\n\r\n@udinator, could you do me a favor and double check whether this introduces any issues with your DV environment?"}
+{"org": "lowRISC", "repo": "ibex", "number": 545, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@473dc68", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 473dc68630e2210f48fe9ea4352c6e9659db5656\r\n\r\n* Sphinx: Add generating pdf file (google/riscv-dv#431) (Hai Hoang\r\n Dang)\r\n* integrate directed asm_tests with yaml flow (Udi Jonnalagadda)\r\n* Fix running cov without arguments (google/riscv-dv#433) (Hai Hoang\r\n Dang)\r\n* Add setup Travis CI for tracking build docs, and install\r\n (google/riscv-dv#430) (Hai Hoang Dang)\r\n* Add handling KeyboardInterrupt for run_cmd and run_parallel_cmd\r\n (google/riscv-dv#424) (Hai Hoang Dang)\r\n* Sphinx: add basic page for structure of the document (google/riscv-\r\n dv#428) (Hai Hoang Dang)\r\n* README.md: Update the information relating to usage (google/riscv-\r\n dv#426) (Hai Hoang Dang)\r\n* Add initial Sphinx docs (google/riscv-dv#427) (Hai Hoang Dang)\r\n* Fix typo in the testlist (google/riscv-dv#423) (taoliug)\r\n* Add try-except for handling KeyboardInterrupt (google/riscv-dv#421)\r\n (Hai Hoang Dang)\r\n* Update information about instruction for running scripts\r\n (google/riscv-dv#420) (Hai Hoang Dang)\r\n* Add vector permutation, reduction, mask instructions (google/riscv-\r\n dv#422) (taoliug)\r\n* Python package (google/riscv-dv#419) (Hai Hoang Dang)\r\n* Refactor the code for cov.py (google/riscv-dv#416) (Hai Hoang Dang)\r\n* Update ovpsim config for vector extesion (google/riscv-dv#415)\r\n (taoliug)\r\n* Fix coverage flow issue (google/riscv-dv#414) (taoliug)\r\n* Add missing license header (google/riscv-dv#412) (taoliug)\r\n* Fix typo in cov_test (google/riscv-dv#410) (taoliug)\r\n* Add vector floating point instructions (google/riscv-dv#409)\r\n (taoliug)\r\n* Add fixed point arithmetic vector instruction (google/riscv-dv#408)\r\n (taoliug)\r\n* cov.py: Generate error when it cannot find spike_sim directory\r\n (google/riscv-dv#407) (Hai Hoang Dang)\r\n* Add vector CSR initialization routine (google/riscv-dv#405)\r\n (taoliug)\r\n* Create vector extension target, add basic enums (google/riscv-\r\n dv#404) (taoliug)\r\n* Fix qrun sim warning (google/riscv-dv#402) (taoliug)\r\n* Try fix qrun constraint solver issue (google/riscv-dv#401) (taoliug)\r\n* Fix simulation warning (google/riscv-dv#400) (taoliug)\r\n* run.py: Generate error for gcc compile when it cannot find assembly\r\n files (google/riscv-dv#398) (Hai Hoang Dang)\r\n* Add numeric corner case test, misc coverage fixes (google/riscv-\r\n dv#396) (taoliug)\r\n* Switch to new CSV format (google/riscv-dv#395) (taoliug)\r\n* misc fixes for the coverage model (google/riscv-dv#394) (taoliug)\r\n* Fix new CSV coverage flow issue (google/riscv-dv#392) (taoliug)\r\n* Integrate new trace CSV format with coverage flow (google/riscv-\r\n dv#390) (taoliug)\r\n* Add experimental script for the new CSV format (google/riscv-dv#389)\r\n (taoliug)\r\n* Support flexible running directed assembly tests (google/riscv-\r\n dv#386) (Hai Hoang Dang)\r\n* run.py: Enhance passing argument for gen function (google/riscv-\r\n dv#382) (Hai Hoang Dang)\r\n* Fix qrun issue, take 2 (google/riscv-dv#384) (taoliug)\r\n* Attempt to fix qrun issue (google/riscv-dv#383) (taoliug)\r\n* Fix (google/riscv-dv#381) (taoliug)\r\n* Fix typo (google/riscv-dv#380) (taoliug)\r\n* Fix qrun simulation issue (google/riscv-dv#379) (taoliug)\r\n* Cleaning the output directory by default. Using exist output\r\n directory (google/riscv-dv#377) (Hai Hoang Dang)\r\n* Fix ius compilation error temporarily (google/riscv-dv#378)\r\n (taoliug)\r\n* Functional coverage improvement (google/riscv-dv#376) (taoliug)\r\n* Add unaligned jump instruction support (google/riscv-dv#375)\r\n (taoliug)\r\n* move handcoded asm_test generation into separate output directory\r\n (Udi Jonnalagadda)\r\n* Ignore return code for ovpsim sim (google/riscv-dv#371) (taoliug)\r\n* Fix mie compare mismatch (google/riscv-dv#370) (taoliug)\r\n* Fix directory/file name for assembly test flow (google/riscv-dv#369)\r\n (taoliug)\r\n* Fix error in README (google/riscv-dv#368) (taoliug)\r\n* Add sample rv32imc test (google/riscv-dv#367) (taoliug)\r\n* Fix typo (google/riscv-dv#366) (taoliug)\r\n* Support running regression with hand-coded assembly tests\r\n (google/riscv-dv#365) (taoliug)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 543, "state": "closed", "title": "[syn] Synth flow improvements", "body": "Adds significant functionality to synthesis flow. Timing reports are\r\ngenerated using OpenSTA and an area report is generated. Flow supports\r\nopen Nangate45 library from OpenROAD.\r\n\r\nWhilst there's plenty of room for improvement this works well enough for now. I'd like to avoid spending much more time on this right now so if there's any major changes wanted (unless they're fundamental for the flow to work properly) I'd prefer to let this through then create a issue to make said changes.\r\n\r\nReplacing the shell script with fusesoc certainly needs doing but we've already got an issue open for that (https://github.com/lowRISC/ibex/issues/502)"}
+{"org": "lowRISC", "repo": "ibex", "number": 542, "state": "closed", "title": "[examples] Add timer example to simple system", "body": "Not particularly useful in the current system, but gives an example of\r\nhow to handle interrupts."}
+{"org": "lowRISC", "repo": "ibex", "number": 540, "state": "closed", "title": "Check how X values end up in C decoder", "body": "Currently, X values can end up in the C decoder when the IF stage does not have a valid instruction. This requires the assertions in the C decoder to be qualified with `instr_valid` (see #536).\r\n\r\nWe allow X values for uninitialized memories and the DV environment can drive them on the external bus. It seems that the X can come from both the uninitialized flops in the prefetch buffer (`ibex_fetch_fifo.sv`) or the bus signal directly, or a combination of the two (depending on the requested address, and FIFO fill status).\r\n\r\nWe need to understand where exactly these X come from in this particular case.\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 535, "state": "closed", "title": "SimCtrlExtension: Add a default destructor", "body": "This base class needs a default destructor for potential future extensions."}
+{"org": "lowRISC", "repo": "ibex", "number": 534, "state": "closed", "title": "Inconsistency between Spike and OVPSIM", "body": "The post comparison results are different when ISS switched from Spike to OVPSIM for two particular cases:\r\n* riscv_unaligned_load_store_test\r\n* riscv_reset_test\r\n\r\n### Environment:\r\n```\r\novpsim build from commit: db82ac94ae9d9d2e1182c947424b78e340fd4dae\r\nspike build from commit: master\r\nvcs version: 2019.06-SP2\r\npython: 3.6\r\nibex: a28bcfa485e0cadd4ef14e57ee28873281a0ef84\r\n```\r\n\r\n### Issue:\r\n\r\nThe results of the `post_compare` step\r\n\r\nwith ISS = 'spike':\r\n* riscv_unaligned_load_store_test: Compare result[FAILED]: 84 matched, 18 mismatch\r\n* riscv_reset_test: Compare result[FAILED]: 0 matched, 22 mismatch\r\n\r\nwith ISS = 'ovpsim':\r\n* riscv_unaligned_load_store_test: Compare result[PASSED]: 13699 matched, 0 mismatch\r\n* riscv_reset_test: Compare result[PASSED]: 0 matched, 0 mismatch\r\n\r\nThe tests were run on the same set of asm_test files.\r\n\r\nThe result was persistent with various seeds.\r\n\r\n\r\n### Note:\r\n\r\nThe `riscv_unaligned_load_store_test` mismatch may related to issue: \r\nhttps://github.com/google/riscv-dv/issues/283#issuecomment-567284887\r\n@taoliug suggested \r\n> You can set unaligned load/store to F to see if it solves the problem.\r\n> https://github.com/google/riscv-dv/blob/master/target/rv32imc/riscvOVPsim.ic#L7\r\n\r\n### Stimulus:\r\nThis zip file includes the .bin, .S and .o files for both tests.\r\n[stimulus.zip](https://github.com/lowRISC/ibex/files/3990943/stimulus.zip)\r\n\r\n### Simulation results:\r\nThis zip file includes the .log and .csv file for spike, ovpsim and rtl simulation. All the simulations were run with stimulus provided above.\r\n[sim_results.zip](https://github.com/lowRISC/ibex/files/3990951/sim_results.zip)\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 532, "state": "closed", "title": "[make] Fix target reference", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 531, "state": "closed", "title": "[DV] Fix TB read responses", "body": "Currently, when the testbench returns a read response to the core, for either a load instruction or instruction fetch response, the testbench will perform a whole word read of the requested address, after word-alignment.\r\nHowever, for byte or halfword loads, this is not ideal, since it is possible that the extraneous bytes read by the testbench outside of the requested byte/halfword are not initialized in the testbench system memory.\r\nThis PR fixes this issue by having the dmem_intf_sequence only read bytes from the system memory that correspond to high bits in the `byte_enable` signal that the core outputs on LSU transactions to ensure that only valid byte addresses are accessed.\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 530, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@9ecee87", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 9ecee87bbc41650ca0f8846de9a277bec2783e18\r\n\r\n* fix mmu_stress_test generation failure (Udi Jonnalagadda)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 529, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@74b8cb6", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 74b8cb65838f575d6e59e1c80a145d305fbca381\r\n\r\n* fix ebreak generation in debug ROM (Udi Jonnalagadda)\r\n* enable nested traps (Udi Jonnalagadda)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 527, "state": "closed", "title": "Implement single-cycle multiplier", "body": "Currently ibex ships with two multiplier implementations, a fast one and a slow one. Both of them require multiple cycles. Implement an even faster multiplier within one cycle."}
+{"org": "lowRISC", "repo": "ibex", "number": 526, "state": "closed", "title": "[bitmanip] Implement Bit Counting (clz, ctz and pcnt) instructions", "body": "Implement the CLZ instruction of the bitmanip extension (count leading zeros). This is the first instruction to implement from bitmanip, it will therefore also require a bit of infrastructure work. See the documents linked in #89 for more information."}
+{"org": "lowRISC", "repo": "ibex", "number": 525, "state": "closed", "title": "[DV] fix incorrect irq_seq handle name", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 524, "state": "closed", "title": "[DV] Add test to assert interrupts during debug execution", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 521, "state": "closed", "title": "[DV] add support_unaligned_load_store setting", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 518, "state": "closed", "title": "[RTL] Only restore from mstack in nmi mode", "body": "Fixes #492\r\n\r\n@udinator could you run the tests you saw failing in #492 again on this?"}
+{"org": "lowRISC", "repo": "ibex", "number": 515, "state": "closed", "title": "[DV] Fix xRET wait checks", "body": "- update error messaging for handshake functions to make more clear\r\n- combine `wait (dut_vif.mret === 1'b1)` and `wait_dret(...)` into one task `wait_ret(...)` and update testbench accordingly\r\n- add privilege mode checking to testbench in tests that involve trapping between privilege modes\r\n- update irq/debug sequences to report if they have been started or not to prevent hanging when killing sequences at EOT\r\n- simplify enabling irq/debug sequences by turning on either `enable_irq_seq` or `enable_debug_seq` from the testlist and letting the UVM environment do the rest, instead of previous approach of enabling the particular sequence from the testbench\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 514, "state": "closed", "title": "Getting Timeout Error with spike while running random test generator..", "body": "Hi all,\r\n\r\nI am getting timeout errors with spike while executing the random test generator.\r\ncommand: python3 run.py --test riscv_csr_test --simulator questa\r\n\r\n\r\nPlease help me..\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 513, "state": "closed", "title": "[DV] update MISA csr yaml description", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 512, "state": "closed", "title": "[verilator] Clarify ELF BSS handling", "body": "Add a requirement for the software loaded by the simulator for zero-ing\r\nthe BSS section.\r\n\r\nFixes lowRISC/ibex#496"}
+{"org": "lowRISC", "repo": "ibex", "number": 508, "state": "closed", "title": "RTL simulation script upgrade", "body": "RTL simulation script was extended to support Cadence simulator."}
+{"org": "lowRISC", "repo": "ibex", "number": 507, "state": "closed", "title": "Pluseargs parsing fix", "body": "This commit fixes $value$plusargs sytem function error described in #497."}
+{"org": "lowRISC", "repo": "ibex", "number": 506, "state": "closed", "title": "[examples] Add fstream header", "body": "The fstream header is needed for `ofstream()` in ibex_simple_system."}
+{"org": "lowRISC", "repo": "ibex", "number": 504, "state": "closed", "title": "Add Synopsys VCS Support for Ibex Simple System", "body": "Add stimuli. Fix compile error for assignment from multiple blocks."}
+{"org": "lowRISC", "repo": "ibex", "number": 503, "state": "closed", "title": "UVM Modelsim compile problem: Could not link 'vsim_auto_compile.so'", "body": "I am trying to simulate testcase riscv_arithmetic_basic_test in uvm env in the path /opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm in modelsim 10.5b but I am getting this fatal error : Fatal: ** Error: (vsim-3828) Could not link 'vsim_auto_compile.so': cmd = '/home/sevyamm/intelFPGA/16.1/modelsim_ase/gcc-4.7.4-linux/bin/gcc -shared -fPIC -m32 -B/usr/lib32 -o \"/tmp/sevyamm@sevyamm-Lenovo-ideapad-320-15AST_dpi_14144/linuxpe_gcc-4.7.4/vsim_auto_compile.so\" \"/tmp/sevyamm@sevyamm-Lenovo-ideapad-320-15AST_dpi_14144/linuxpe_gcc-4.7.4/exportwrapper.o\" \r\nCan somebody suggest me how to remove this??\r\n\r\nThese are the commands I am using for simulating it : \r\n- vmap mtiUvm /home/sevyamm/intelFPGA/16.1/modelsim_ase/verilog_src/uvm-1.2\r\n- vlog -64 +incdir+/home/sevyamm/intelFPGA/16.1/modelsim_ase/verilog_src/uvm-1.2/src +incdir+/home/sevyamm/Desktop/opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm/riscv_dv_extension +incdir+/home/sevyamm/Desktop/opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm/common -printinfilenames -access=rwc -f /home/sevyamm/Desktop/opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm/ibex_dv.f -sv -mfcu +define+UVM_NO_DPI /home/sevyamm/Desktop/opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm/tb/core_ibex_tb_top.sv -l /home/sevyamm/Desktop/opentitan-master/hw/vendor/lowrisc_ibex/dv/uvm/out/instr_gen/compile.log\r\n- vsim -64 core_ibex_tb_top +UVM_TESTNAME=riscv_arithmetic_basic_test -sv_seed 1342"}
+{"org": "lowRISC", "repo": "ibex", "number": 502, "state": "closed", "title": "syn: Integrate with fusesoc", "body": "Instead of having a shell script, the yosys synthesis should be called as normal fusesoc target."}
+{"org": "lowRISC", "repo": "ibex", "number": 501, "state": "open", "title": "syn: Remove copy of prim_clock_gating.v and use shared version instead", "body": "Having multiple versions of that file in the tree confuses users to pick the wrong one, so the one in `syn` should go."}
+{"org": "lowRISC", "repo": "ibex", "number": 497, "state": "closed", "title": "Cadence simulator plusargs command line argument parsing error", "body": "Verification environment uses SystemVerilog line argument for getting signature address [(core_ibex_env_cfg.sv)](https://github.com/lowRISC/ibex/blob/ce7e38351e28bf54cbc7c2856ce6b65b9d2a3fbb/dv/uvm/env/core_ibex_env_cfg.sv#L30). Value is passed to environment at [(makefile)](https://github.com/lowRISC/ibex/blob/ce7e38351e28bf54cbc7c2856ce6b65b9d2a3fbb/dv/uvm/Makefile#L132) at run_sim step. The problem is Cadence simulator cannot recognize this argument as hexadecimal number:\r\n```\r\nvoid'($value$plusargs(\"signature_addr=%0h\", signature_addr));\r\n |\r\nncsim: *E,SYSFMT (ibex/dv/uvm/env/core_ibex_env_cfg.sv,30|24): $value$plusargs -- value found '0x8ffffffc' for plusarg 'signature_addr=' does not match specified format.\r\n```\r\nThis issue can be fixed with something like atohex() SystemVerilog function (this function should be supported by all simulators)."}
+{"org": "lowRISC", "repo": "ibex", "number": 496, "state": "closed", "title": "Verilator ELF loading: zero BSS segment", "body": "Currently, the ELF loader in verilator_sim_ctrl doesn't zero the BSS segment:\r\n\r\nhttps://github.com/lowRISC/ibex/blob/ce7e38351e28bf54cbc7c2856ce6b65b9d2a3fbb/dv/verilator/simutil_verilator/cpp/verilator_sim_ctrl.cc#L721\r\n\r\nMore discussion here: https://github.com/lowRISC/ibex/pull/411#issuecomment-555924017"}
+{"org": "lowRISC", "repo": "ibex", "number": 495, "state": "closed", "title": "New bit manipulate instruction request", "body": "We're interested in the following instructions. They're not currently in RISC-V ISA extension.\r\n\r\n**fls (find the largest bit set)**. eg 31 - clz\r\nbits (bit-set-by-position) and bitsi (immediate version)\r\nbitc (bit-clear-by-position) and bitci (immediate version)\r\n\r\nUse cases:\r\nfls(Find largest bit set; fls rd, rs). This and bitc are used in the inner loop to find-and-extract bits.\r\nEquivalent to: \r\nclz rd, rs\r\nxori rd, rd, 31\r\n\r\n**bits (bit-set-by-position) and bitsi (immediate version)**\r\nbits rd, rs1, rs2\r\nbitsi rd, rs, IMM\r\n\r\nSet bit by index. rd = rs1 | (1 << rs2)\r\nEquivalent to:\r\nli rs1, 1\r\nsll rs1, rs1, rs2\r\nor rd, rs1, rs2\r\n\r\nThe encoding for bitc and bits should be identical other than the value to place in bit position rs2. This may reduce gate count.\r\n\r\n**bitc (bit-clear-by-position) and bitci (immediate version)**\r\nbitc rd, rs1, rs2\r\nbitci rd, rs, IMM\r\n\r\nClear bit by index. rd = rs1 & ~(1 << rs2)\r\nGeneral case:\r\nli rs1, 1\r\nsll rs1, rs1, rs2\r\nxori rs1, rs1, -1\r\nand rd, rs1, rs2\r\n\r\nIf the immediately preceding instruction was fls rs2, rd, then we know the bit is set in the destination already:\r\nli rs1, 1\r\nsll rs1, rs1, rs2\r\nxori rd, rs1, -1\r\n\r\nAllowable in bitwise spec, which indicates it may be useful for lower-performance cores like ours which can't fuse macro ops"}
+{"org": "lowRISC", "repo": "ibex", "number": 493, "state": "closed", "title": "Update gitignore", "body": "Add more output files."}
+{"org": "lowRISC", "repo": "ibex", "number": 492, "state": "closed", "title": "MEPC written on `mret` instructions", "body": "Hi all,\r\nI noticed that on an `mret` instruction, `mepc` will get overwritten with the contents of `mstack_epc` as shown below:\r\n\r\nThis is causing some test failures, as this update is not reflected in the logs, resulting in a register write mismatch since the Ibex `mepc` now holds `0`, while the `mepc` in the ISS will still contain the correct value that was explicitly written at an earlier point in the simulation (`0x80000144`).\r\n`mepc` will still get written correctly whenever the core takes a trap, it is just this extra write that occurs on `mret` that modifies its state. According to the spec, `mepc` should never be written by the RTL apart from taking traps, so how does this align with the nonstandard `mstack` CSRs that Ibex implements?\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 491, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@d691906", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision d69190682078470bc6d5661d72f873ae9850ae53\r\n\r\n* enable CSR randomization only for csr instructions (google/riscv-\r\n dv#321) (udinator)\r\n* fix csr test script pathname (Udi Jonnalagadda)\r\n\r\nAddresses #485 \r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 489, "state": "closed", "title": "Can we run Random test generator with Model sim?", "body": "Hi all,\r\n\r\nI installed the ibex SV/UVM instruction generator for RISCV processor verification. \r\nI have done this:\r\n python3 run.py --test riscv_arithmetic_basic_test --simulator questa\r\nIt is showing an error message. please find the attachment.\r\n\r\n\r\nPlease help me.."}
+{"org": "lowRISC", "repo": "ibex", "number": 488, "state": "closed", "title": "[DV] streamline Makefile gen flow", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 487, "state": "closed", "title": "[DV] Update flow to match RISCV-DV changes", "body": "Signed-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 486, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@39ca859", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 39ca85903eea94350d3a610256307346da407e5b\r\n\r\n* Add directed stream to access higher privilege CSRs (google/riscv-\r\n dv#316) (udinator)\r\n* add config knob for mstatus.tw (Udi Jonnalagadda)\r\n* Fix ovpsim floating point instruction parsing issue (google/riscv-\r\n dv#313) (taoliug)\r\n* Fix SATP configure issue (google/riscv-dv#312) (taoliug)\r\n* Support import testlist (google/riscv-dv#311) (taoliug)\r\n* Add a rand address load/store test (google/riscv-dv#310) (taoliug)\r\n* Fix ovpsim log parsing issue (google/riscv-dv#309) (taoliug)\r\n* Add a generic approach to check command return value (google/riscv-\r\n dv#308) (taoliug)\r\n* Fix compile issue (google/riscv-dv#307) (taoliug)\r\n* Basic U-mode support (Udi Jonnalagadda)\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 485, "state": "closed", "title": "Regression testing failed", "body": "I've tried to run regression test but it has failed a few times. I debugged one of the fails and found differnce between iss_sim and rtl_sim program flows.\r\nSo, at asm program there is a jump to subroutine. Trace log of this jump looks the same for both iss and rtl simulations but return code differs.\r\n\r\nSubrotine call code at main program looks like this [(line 54)](https://github.com/lowRISC/ibex/files/3876255/riscv_illegal_instr_test_0_ASM.TXT):\r\n```\r\n ...\r\n j init_user_mode\r\n```\r\nAnd subroutine code is [(line 17 287)](https://github.com/lowRISC/ibex/files/3876255/riscv_illegal_instr_test_0_ASM.TXT):\r\n```\r\ninit_user_mode: \r\n ...\r\n mret\r\n```\r\nAccording to trace of ISS simulator it uses \"mret (0x30200073)\" [(line 145)](https://github.com/lowRISC/ibex/files/3876244/riscv_illegal_instr_test.0.log) command as the return instruction, but RTL uses \"jal (0800006f)\" [(line 69)](https://github.com/lowRISC/ibex/files/3876245/trace_core_00000000.lo) in the same case. So, they used different return codes which causes jumping to different addresses.\r\nAs I've seen ISS uses .o file as the source and rtl simulator .bin which can be a root of the problem, but both of them are generated by gen rule of makefile from the same source.\r\n\r\n[riscv_illegal_instr_test_0_ASM.TXT](https://github.com/lowRISC/ibex/files/3876255/riscv_illegal_instr_test_0_ASM.TXT)\r\n[riscv_illegal_instr_test.0.log](https://github.com/lowRISC/ibex/files/3876244/riscv_illegal_instr_test.0.log)\r\n[trace_core_00000000.log](https://github.com/lowRISC/ibex/files/3876245/trace_core_00000000.log)\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 484, "state": "closed", "title": "[ci] Add CS registers TB to CI", "body": "Build and run TB, checking for failures\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 483, "state": "closed", "title": "[DV] Test accesses to higher privileged CSRs", "body": "- Add test for accessing higher privilege mode CSRs from U-mode\r\n- Refactor illegal instruction checking logic to a separate task\r\n\r\nSigned-off-by: Udi "}
+{"org": "lowRISC", "repo": "ibex", "number": 482, "state": "closed", "title": "An higher prio interrupt routine is interrupted by lower prio IRQ", "body": "When executing a higher priority interrupt routine, it can be interrupted by a lower prio interrupt if MIE is set high and high prio IRQ source cleared. Is it an intended implementation? \r\n\r\nBelow is a screenshot where fast_irq_i[0] and fast_irq_i[1] occur simultaneously. First, fast_irq_i[1] is being served. But after I clear fast_irq_i[1] source & set MIE high, the routing is preempted by fast_irq_i[0] . Once fast_irq_i[0] routine is complete, the rest of fast_irq_i[1] is completed.\r\n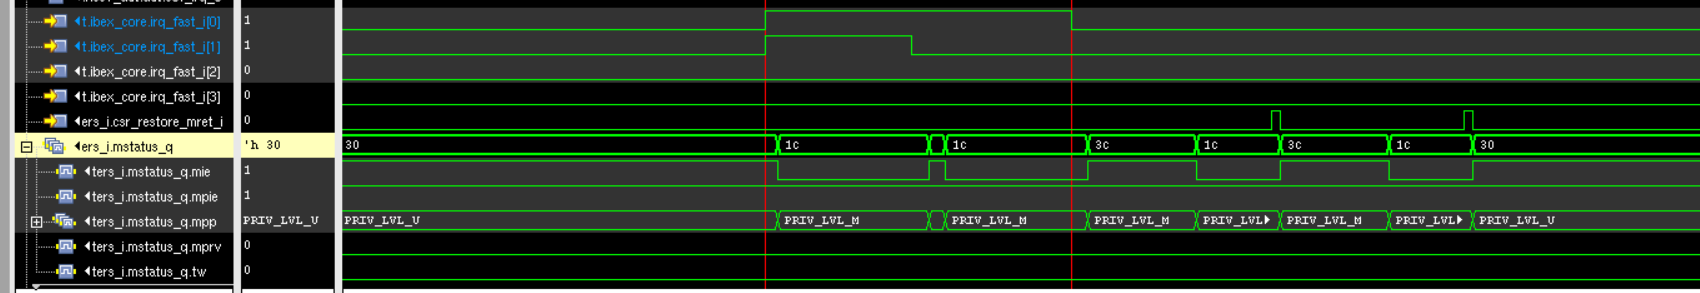\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 478, "state": "closed", "title": "[DV] Add exit check for setup call", "body": "Check the return value and exit program execution."}
+{"org": "lowRISC", "repo": "ibex", "number": 477, "state": "closed", "title": "Fix typo in comment", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 476, "state": "closed", "title": "[dv] Remove clock gating primitive in `dv/uvm/tb`", "body": "This commit removes a copy of the dummy clock gating primitive from\r\ntree previously used for UVM-based DV. There is another, identical copy\r\nof the same primitive in `shared/rtl` that can be used instead.\r\n\r\nThis resolves lowRISC/ibex#213.\r\n\r\nSigned-off-by: Pirmin Vogel "}
+{"org": "lowRISC", "repo": "ibex", "number": 474, "state": "closed", "title": "CS registers tb enhancements", "body": "All CSR addresses supported by the TB are now delared as an X\r\nmacro list. This list is then used to autogenerate the enum\r\ntype, string print helper and an array of all addresses.\r\n\r\nThe array of addresses can now be used by the randomize generator\r\nto turn an arbitrary integer index into an address. This removes\r\nthe restriction on only generating contiguous address ranges noted\r\nin #443.\r\n\r\nAdd missing signal csr_restore_dtret_i\r\n\r\nSigned-off-by: Tom Roberts "}
+{"org": "lowRISC", "repo": "ibex", "number": 473, "state": "closed", "title": "Cadence Genus doesn't remove performance counters with MHPMCounterNum = 0", "body": "It would be nice to add some ability mechanism to remove mphp registers(mhpmcounter_q) from the design via some parameter or defines. I just have synthesised the core with and without them, and can established that mhpm register occupy about 35% of the total area, but they can be optional for some tasks. "}
+{"org": "lowRISC", "repo": "ibex", "number": 469, "state": "closed", "title": "Failure with 4 nested interrupts", "body": "I'm trying to play with nested interrupts. So I made a basic simulation where 4 fast interrupts irq_fast_i[3:0] are generated in a row. \r\nUpon exit from the 4th (last) interrupt routine, the simulation crashes since PC gets mtvec value.\r\nBesides I noticed that MPP unexpectedly (in my opinion) gets PRIV_LVL_U value taken from mstack_q.mpp upon exit from 2nd interrupt. \r\n\r\n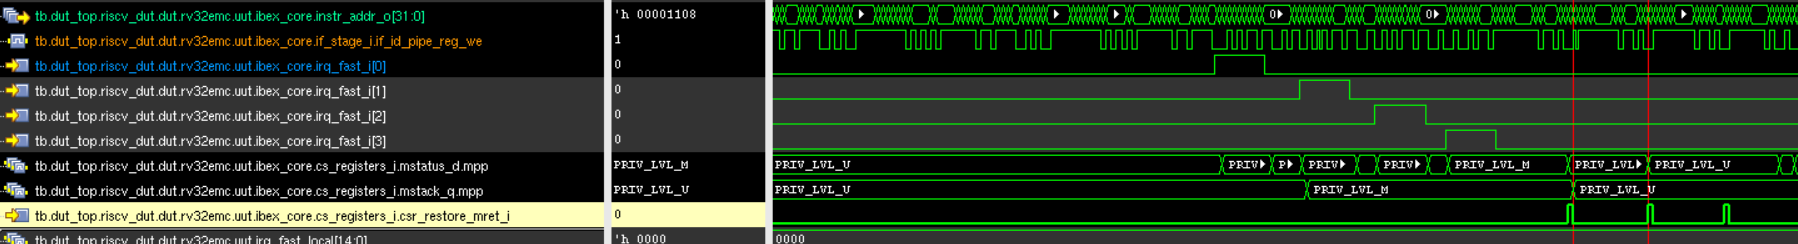\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 468, "state": "closed", "title": "Trace simulator control", "body": "Using the simple system example:\r\n```\r\n$ fusesoc --cores-root=. run --target=sim --setup --build lowrisc:ibex:ibex_simple_system\r\n$ build/lowrisc_ibex_ibex_simple_system_0/sim-verilator/Vibex_simple_system --raminit=examples/sw/simple_system/hello_test/hello_test.vmem\r\n```\r\nproduces the following trace\r\n```\r\n% tail -n 4 trace_core_00000000.log \r\n 1260 626 00100308 8082 c.jr x1 x1:0x001002b8\r\n 1262 627 001002b8 000202b7 lui x5,0x20 x5=0x00020000\r\n 1264 628 001002bc 00428293 addi x5,x5,4 x5:0x00020000 x5=0x00020004\r\n 1266 629 001002c0 4305 c.li x6,1 x6=0x00000001\r\n```\r\n\r\nFrom `crt0.S`\r\n```\r\n /* Halt simulation */ \r\n li x5, SIM_CTRL_BASE + SIM_CTRL_CTRL \r\n li x6, 1 \r\n sw x6, 0(x5)\r\n```\r\nwe see the last store instruction (which terminates the simulation via `simulator_ctrl.sv +73`) is not part of the trace.\r\nProbably not the highest priority to fix, but wanted to document what I saw."}
+{"org": "lowRISC", "repo": "ibex", "number": 467, "state": "closed", "title": "Optional U-Mode", "body": "Would it be feasible to make U-Mode enable a core parameter like PMP?\r\n\r\nI'm sure there are some use cases where it's not really needed, yet as small logic utilization as possible is required. Is the U-Mode so tightly integrated into the core that it cannot be easily separated as a parameter?"}
+{"org": "lowRISC", "repo": "ibex", "number": 466, "state": "closed", "title": "Fix formatting of table in simple system", "body": "Fixes #454"}
+{"org": "lowRISC", "repo": "ibex", "number": 465, "state": "closed", "title": "[rtl] Switch to M mode on debug entry", "body": "- Core should operate as if in M-mode while in debug mode\r\n- Previous priv level is restored from dcsr on DRET\r\n- Fixes #463"}
+{"org": "lowRISC", "repo": "ibex", "number": 464, "state": "closed", "title": "Update crt0 load instruction", "body": "And moved the gitignore from sw/led to sw so it applies to simple_system as well"}
+{"org": "lowRISC", "repo": "ibex", "number": 463, "state": "closed", "title": "Debug-mode privilege level", "body": "Hi all,\r\nI'm executing some tests after booting Ibex into User-Mode, and asserting debug stimulus, and I see the following:\r\n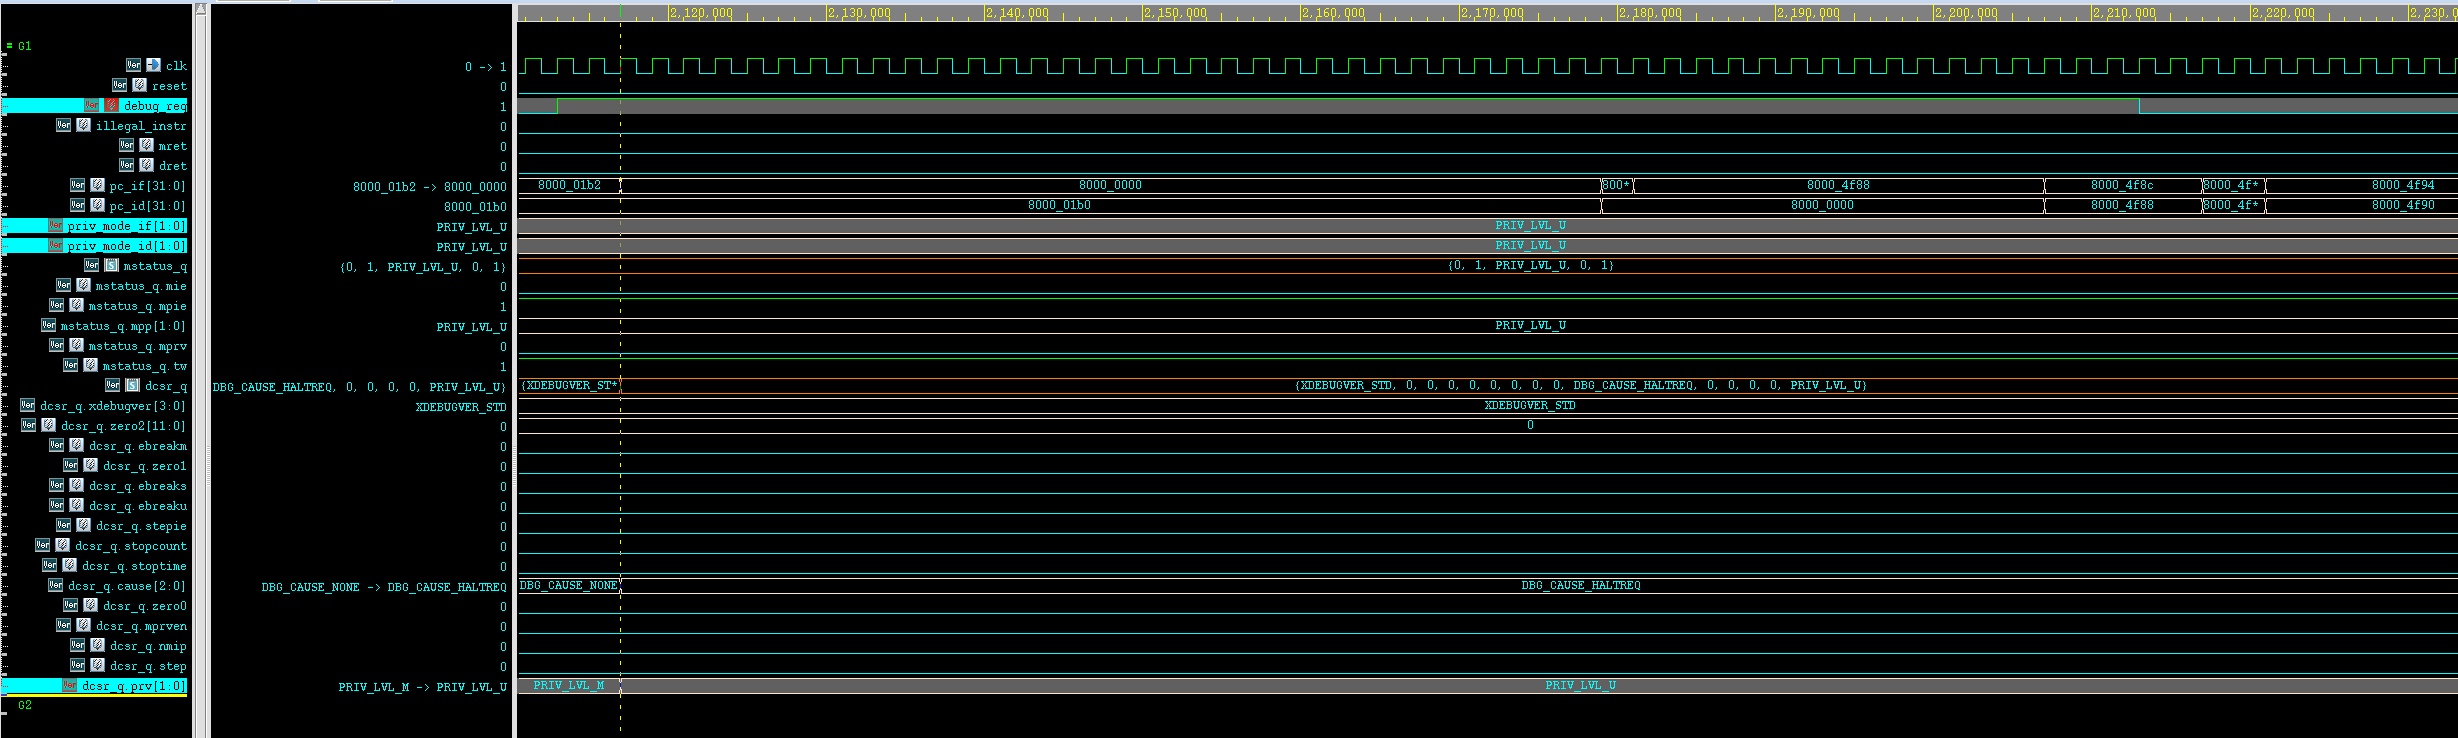\r\nIn this test, our debug ROM is located at `0x80004f88`.\r\nWe can see that the core's privilege level stays at `PRIV_LVL_U` even after the core has jumped to the debug ROM and `debug_req` has dropped, while the Debug-Mode Spec says that all operation in debug mode should be taken at machine mode. As a result of the current Ibex behavior, illegal instruction exceptions are thrown when we access D-mode CSRs inside of the debug ROM.\r\nHowever, `dcsr.prv` is being updated properly, and stores the value of `PRIV_LVL_M` after trapping to debug mode, it is just the current privilege mode that is being calculated incorrectly.\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 460, "state": "closed", "title": "[rtl/controller] Remove coverage holes", "body": "This PR contains two commits to remove coverage holes in the controller. The changes are non-functional."}
+{"org": "lowRISC", "repo": "ibex", "number": 459, "state": "closed", "title": "Add RV32Zicsr riscv-compliance target", "body": "Tests are moved in https://github.com/riscv/riscv-compliance/commit/df18fa8d95e78f2c54d7a5d59a8b94b3f19967ef from `rv32i` to `rv32Zicsr`.\r\nTarget needs to be added to azure."}
+{"org": "lowRISC", "repo": "ibex", "number": 457, "state": "closed", "title": "Arty shared", "body": "Use the shared folder to re-use code.\r\n\r\n@imphil does `shared/rtl/fpga/xilinx` make sense to you?"}
+{"org": "lowRISC", "repo": "ibex", "number": 455, "state": "closed", "title": "[funct_cov] Update Makefile options for coverage", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 454, "state": "closed", "title": "Simple system: Fix table at the end of the documentation", "body": "See the rendering of https://github.com/lowRISC/ibex/tree/master/examples/simple_system"}
+{"org": "lowRISC", "repo": "ibex", "number": 453, "state": "closed", "title": "[funct_cov] Update Ibex log parsing", "body": "- Update parsing of ibex tracer log to extract all register information (rs1/rs2/rd) if available\r\n- enable riscv_csr_test trace logs to get converted to CSV format for functional coverage\r\n\r\nNote: depends on https://github.com/google/riscv-dv/pull/291"}
+{"org": "lowRISC", "repo": "ibex", "number": 451, "state": "closed", "title": "Implement FENCE.I", "body": "We should add stimulation of fence.i to the DV and ensure this gets a decent testing. I have done some basic testing with simple system and it looks to work ok.\r\n\r\n(I'd be happy to look into the DV work but that won't happen til I return from Holiday)"}
+{"org": "lowRISC", "repo": "ibex", "number": 450, "state": "closed", "title": "Interrupt isn't taken in vicinity of a branch instruction", "body": "Below is a screenshot where a fast interrupt handler is mistakenly skipped. \r\nThe CPU jumps to IRQ vector at address 0x1040., there a jump instruction to address is 0x1084 is located. The jump isn't performed, instead main program is executed (addresses 0x00FC -> 0x0100 -> 0x0104 etc )\r\n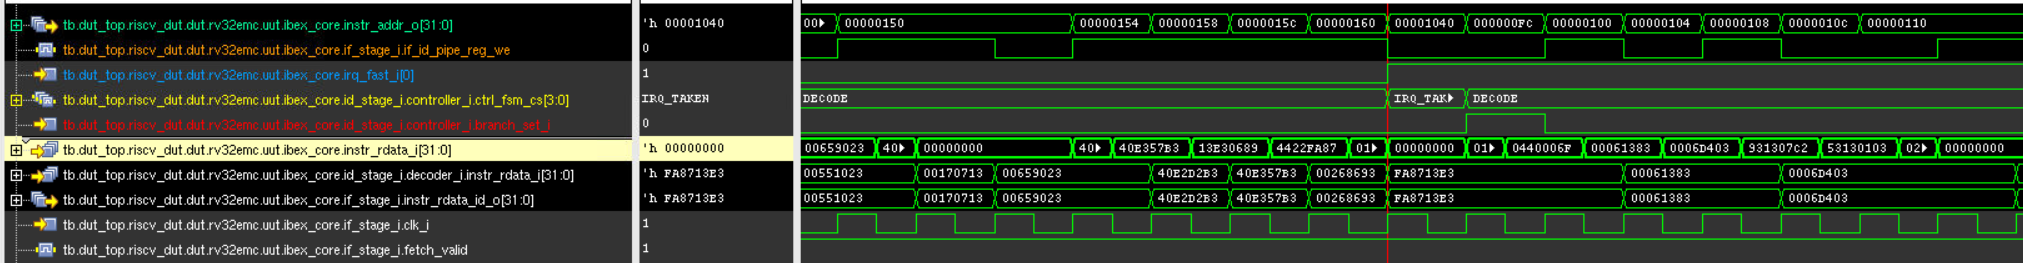\r\n\r\nHere below is another screenshot where the same interrupt occurs 1 clock cycle later. It can be seen a normal sequence of addresses, i.e. CPU jumps to address 0x1084 where the interrupt handler actually locates.\r\n\r\n\r\n\r\nI suspect the reason is due to vicinity of branch instruction (red signal branch_set_i).\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 448, "state": "closed", "title": "[DV] clean up stale TODOs", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 447, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@44bec76", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 44bec7695fd2399166e181fa84b66a608b5f745f\r\n\r\n* Re-enable custom OVPsim configuration files (google/riscv-dv#282)\r\n (udinator)"}
+{"org": "lowRISC", "repo": "ibex", "number": 446, "state": "closed", "title": "[DV/flow] Integrate with RISCV-DV", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 444, "state": "closed", "title": "Writing unaligned addresses to `dpc` CSR", "body": "Currently, writes to the `dpc` CSR are simply ignored if the address is unaligned. The debug spec does not specify what should happen if an unaligned address is written to `dpc`. In contrast, the privileged spec says that `xepc` can only hold aligned addresses.\r\n\r\nI suggest to align the behavior of these two registers, i.e., to make the LSB of `dpc` to be always 0 instead of ignoring writes with non-zero LSB completely."}
+{"org": "lowRISC", "repo": "ibex", "number": 443, "state": "closed", "title": "[dv] Extend registers testbench", "body": "This PR extends the registers testbench to also support performance counter CSRs.\r\n\r\nWhat is currently missing:\r\n- ~~Generate randomized transactions over the whole range of available CSRs (currently only contiguous ranges supported)~~ see #474 \r\n- ~~Add read-only/WARL registers~~ see below.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 442, "state": "closed", "title": "[rtl] Rework `core_busy` signals, remove feedback to clk", "body": "This commit reworks the generation of the `core_busy` signal used to control the main clock gate of the core. Without this commit, the controller generates a separate `first_fetch` signal only asserted in the FIRST_FETCH state that directly controls `core_busy` and thus the main clock gate. This is problematic as it introduces a feedback to from the controller state into the clock.\r\n\r\nThis commit removes the problematic signal and changes the generation of `ctrl_busy` in the FIRST_FETCH state of the controller. This signal is now used to control the main clock gate in all states (previously all except FIRST_FETCH) but it gets registered, thus it does not introduce the feedback into the clock.\r\n\r\nThis resolves lowRISC/ibex#211."}
+{"org": "lowRISC", "repo": "ibex", "number": 438, "state": "open", "title": "Modify/Extend Simple System to be a more generic base ", "body": "This PR https://github.com/lowRISC/ibex/pull/311 introduces Simple System. It allows you to build programs and easily run them on a basic Ibex system.\r\n\r\nIt shares many commonalities with the riscv-compliance system and the FPGA example. It should be possible to refactor these things so they are all working off the same base.\r\n\r\nIn addition it would be useful to add debugging support into Simple System to demonstrate how to setup a working debug environment. Though this may draw us away from it being a simple system so perhaps it would be a new example derived from Simple System."}
+{"org": "lowRISC", "repo": "ibex", "number": 436, "state": "closed", "title": "Makefile:133: recipe for target 'post_compare' failed!", "body": "configuration:\r\nisa: rv32imc\r\niss: riscv-ovpsim\r\nrun: make TEST=riscv_arithmetic_basic_test\r\ncompiler and simulation procedures seem no any problem, except log output of ovpsim_sim:\r\nfile: riscv_arithmetic_basic_test.0.log : empty\r\n\r\nfile: riscv_arithmetic_baisc_test.1~9.log: \r\nError (CM_NF) '../riscv-dv/target/rv32imc/riscvOVPsim.ic' not found\r\nFatal (FP_NVAR) No variant was specified. Suggest --variant . Use -showvariants to see a list.\r\nInfo Exiting"}
+{"org": "lowRISC", "repo": "ibex", "number": 435, "state": "closed", "title": "[DV] Assert interrupt during write to MSTATUS and MIE", "body": "Added two new tests to assert interrupts and debug mode requests while the core is handling a pipeline flush due to CSR write instructions dealing with xSTATUS and xIE.\r\nThis PR relies on the riscv-dv generator changes added in [this PR](https://github.com/google/riscv-dv/pull/273)."}
+{"org": "lowRISC", "repo": "ibex", "number": 434, "state": "closed", "title": "how to write interrupt handler", "body": "Question: \r\nI'm trying to write an interrupt handler. As far as I understand the handler should end with mret command. This command requires ra(x1) register to keep the return address. \r\nAt the same time subroutines in the main program code contain ret command which also uses ra register.\r\nSo if I explicitly affect ra in the interrupt handler, the interrupted subroutine will return to the wrong address. If I don't update ra in the interrupt handler explicitly by copying MEPC, the CPU doesn't jump to the address where it was just before the interrupt occurrence.\r\n\r\nProbably I miss smth. Please, advice.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 433, "state": "closed", "title": "Example files for the Nexys4DDR board.", "body": "As I was playing with the Nexys4DDR board, here are the example files.\r\nSmall difference on the reset signal compared to the Arty (as it doesn't have a ChipKit connection)."}
+{"org": "lowRISC", "repo": "ibex", "number": 432, "state": "closed", "title": "ALU: Dead enum values", "body": "Hi all,\r\nAs an extension to #420, there appear to be some more enum values that are never used in the core, namely `ALU_SLET` and `ALU_SLET`.\r\nI think these could be deleted as well since they appear to be dead code?\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 431, "state": "closed", "title": "Error synthesis in Vivado", "body": "Looks like my first PR regarding the error synthesis was ugly...\r\nThis one should be better now"}
+{"org": "lowRISC", "repo": "ibex", "number": 430, "state": "closed", "title": "Fixed a synthesis error with Vivado 2018.2", "body": "Following comments on issue #429 (synthesis error with Cadence Genus and Vivado 2018.2), the PR removes the string annotation for the multiplier. Synthesis is OK."}
+{"org": "lowRISC", "repo": "ibex", "number": 428, "state": "closed", "title": "RISC-V compliance mtvec alignment", "body": "Follow-up for PR #427 and in connection to #100 \r\n\r\nThe current RISC-V compliance test places a [trap handler](https://github.com/lowRISC/riscv-compliance/blob/master/riscv-test-suite/rv32i/src/I-EBREAK-01.S#L74) at non 256-byte aligned position and uses this as a target for [mtvec](https://github.com/lowRISC/riscv-compliance/blob/master/riscv-test-suite/rv32i/src/I-EBREAK-01.S#L47).\r\n\r\nIbex requires that the mtvec value is 256-byte aligned.\r\n\r\nRISC-V Privileged Spec:\r\n\r\n> If mtvec is writable, the set of values the register may hold can vary by implementation. The value in the BASE field must always be aligned on a 4-byte boundary, and the MODE setting may impose additional alignment constraints on the value in the BASE field. \r\n\r\n> An implementation may have different alignment constraints for different modes. In particular,\r\nMODE=Vectored may have stricter alignment constraints than MODE=Direct.\r\n\r\n> Allowing coarser alignments in Vectored mode enables vectoring to be implemented without a\r\nhardware adder circuit.\r\n\r\n@vogelpi mentioned in #427 that this should be fixed upstream.\r\nThe purpose of this issue is make the problem visible and to discuss the correct solution."}
+{"org": "lowRISC", "repo": "ibex", "number": 427, "state": "closed", "title": "Reduce mtvec alignment requirement", "body": "RISC-V Privileged Spec v1.11 allows BASE filed of mtvec to be 4-byte\r\naligned.\r\n\r\nUpdate the assignment and usage of mtvec to use 4-byte aligned\r\naddresses.\r\n\r\nThis fixes `I-EBREAK` and `I-ECALL` tests of RISC-V compliance failures\r\nreported in lowrisc/ibex#100."}
+{"org": "lowRISC", "repo": "ibex", "number": 426, "state": "closed", "title": "[DV] Increase number of illegal instructions generated", "body": "Additionally:\r\n1) Add configuration file for OVPsim, and update Makefile to pass correct config file into iss_sim target\r\n2) Additionally, changed default ISS to OVPsim, it has been fully configured for Ibex, and can handle `mie.mtie` being enabled without any weird side-effects."}
+{"org": "lowRISC", "repo": "ibex", "number": 424, "state": "closed", "title": "[rtl/alu] Remove unused comparison operations", "body": "These operations (ALU_GT, ALU_GTU, ALU_LE, ALU_LEU) are remnants of of the original OpenRISC design. RISC-V does not have these instructions and instead implements the operations by reversing operands for ALU_LT, ALU_LTU, ALU_GE, ALU_GEU.\r\n\r\nThis resolves lowRISC/ibex#420 reported by @udinator."}
+{"org": "lowRISC", "repo": "ibex", "number": 423, "state": "closed", "title": "Add slow multiplier test to CI", "body": "As mentioned in #412, now that we have possibility to choose between slow and fast multiplier in top level it would be nice to have a CI test for this configuration as well.\r\n\r\nMy question is if the entire test flow should be duplicated (so linter and compliance checks), or just some single step?"}
+{"org": "lowRISC", "repo": "ibex", "number": 422, "state": "closed", "title": "[CI] Add register testbench to CI", "body": "Once #298 lands we should add it to CI (with Verilator)."}
+{"org": "lowRISC", "repo": "ibex", "number": 421, "state": "closed", "title": "LSU: Remove/correct obsolete assertion", "body": "Inside `ibex_load_store_unit.sv`, we have an assertion checking that in the RVALID state, a grant can only be received while also getting the rvalid. This assertion has become obsolete in the process of adding PMP support. Currently, the RVALID state is only entered when a grant is no longer expected.\r\n\r\nThis assertion should be removed or corrected. "}
+{"org": "lowRISC", "repo": "ibex", "number": 420, "state": "closed", "title": "ALU: Remove dead code", "body": "Inside `ibex_pkg.sv` and `ibex_alu.sv`, there are a couple of unused ALU operations defined (ALU_GT, ALU_GTU, ALU_LE, ALU_LEU). These cannot be triggered as the decoder does not support them.\r\n\r\nThese operations are remnants of the original OpenRISC design. RISC-V does not have the corresponding instructions and instead implements the ops by reversing operands to (BLT, BLTU, BGE, BGEU, see p.23 of the RISC-V spec).\r\n\r\nI suggest to remove those fragements."}
+{"org": "lowRISC", "repo": "ibex", "number": 419, "state": "closed", "title": "ibex_core lint fail.", "body": "Hi,\r\n\r\nI'm trying to build ibex_core_tracing, got some error.\r\nI tried to find similar issue or goggled, but hard to find solution.\r\n\r\nOS : debian 4.9.0-9-amd64\r\nfusesoc : 1.9.3\r\nverilator : 4.020\r\ncommand : fusesoc --cores-root . run --target=lint lowrisc:ibex:ibex_core_tracing\r\n\r\n```\r\nINFO: Preparing lowrisc:ibex:ibex_core:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_tracer:0.1\r\nINFO: Preparing lowrisc:ibex:ibex_core_tracing:0.1\r\n\r\nverilator -f lowrisc_ibex_ibex_core_tracing_0.1.vc -Wall\r\n%Warning-UNUSED: ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_register_file_ff.sv:21: Signal is not used: 'test_en_i'\r\n : ... In instance ibex_core_tracing.u_ibex_core.id_stage_i.registers_i\r\n input logic test_en_i,\r\n ^~~~~~~~~\r\n ... Use \"/* verilator lint_off UNUSED */\" and lint_on around source to disable this message.\r\n%Warning-UNOPTFLAT: ../src/lowrisc_ibex_ibex_core_0.1/rtl/ibex_controller.sv:101: Signal unoptimizable: Feedback to clock or circular logic: 'ibex_core_tracing.u_ibex_core.id_stage_i.controller_i.ctrl_fsm_cs'\r\n ctrl_fsm_e ctrl_fsm_cs, ctrl_fsm_ns;\r\n ^~~~~~~~~~~\r\n%Error: Exiting due to 2 warning(s)\r\n%Error: Command Failed /usr/local/bin/verilator_bin -f lowrisc_ibex_ibex_core_tracing_0.1.vc -Wall\r\nMakefile:16: recipe for target 'Vibex_core_tracing.mk' failed\r\nmake: *** [Vibex_core_tracing.mk] Error 10\r\nTraceback (most recent call last):\r\n File \"/home/kwang/.local/bin/fusesoc\", line 11, in \r\n sys.exit(main())\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/fusesoc/main.py\", line 583, in main\r\n args.func(cm, args)\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/fusesoc/main.py\", line 268, in run\r\n flags, args.system_name, args.system, args.backendargs, args.build_root)\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/fusesoc/main.py\", line 357, in run_backend\r\n backend.build()\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/edalize/edatool.py\", line 117, in build\r\n self.build_main()\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/edalize/verilator.py\", line 166, in build_main\r\n self._run_tool('make', args)\r\n File \"/home/kwang/.local/lib/python2.7/site-packages/edalize/edatool.py\", line 293, in _run_tool\r\n except FileNotFoundError:\r\nNameError: global name 'FileNotFoundError' is not defined\r\n\r\n```\r\ncould you give some tips?\r\nthanks."}
+{"org": "lowRISC", "repo": "ibex", "number": 416, "state": "closed", "title": "[RTL/Tracer] Fix compressed jump RD write", "body": "Fixes #414."}
+{"org": "lowRISC", "repo": "ibex", "number": 415, "state": "closed", "title": "[DV] Enable timer interrupts", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 414, "state": "closed", "title": "[tracer] C.JALR does not display write to x1", "body": "Hi all,\r\n\r\nAs shown from this trace, even though `c.jalr` instruction will write `PC+2` to `x1`, this write is not reflected in the tracer log.\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 412, "state": "closed", "title": "[RTL] Add MultiplierImplementation parameter in top level", "body": "I thought that it would be nice to have this switch in top level, so that everything can be configured from here. Slow multiplication is already described in documentation, but there is no information how to enable it."}
+{"org": "lowRISC", "repo": "ibex", "number": 410, "state": "closed", "title": "[DV] Add interrupt wfi test to address coverage hole", "body": "- increase test timeout to 10M cycles\r\n- increase number of tests involving external stimulus"}
+{"org": "lowRISC", "repo": "ibex", "number": 409, "state": "closed", "title": "[DV] testplan documentation", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 408, "state": "closed", "title": "Tracer: Decode an all-zero instruction as INVALID", "body": "Fixes #396"}
+{"org": "lowRISC", "repo": "ibex", "number": 407, "state": "closed", "title": "Add Greg Chadwick to CREDITS.md", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 405, "state": "closed", "title": "[DV] Debug_ebreak test fix", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 404, "state": "closed", "title": "Add RV32IM test", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 402, "state": "closed", "title": "Docs: Make licensing docs more user-friendly", "body": "Currently we have a section \"Copyright\" in our docs [1]. This section is badly named, and not overly helpful to people unfamiliar with open source and the Apache license in particular. This PR rewords some of that content to make it more accessible for a broader audience.\n\nA second commit adds information about lowRISC offering commercial support for Ibex, which could be helpful information for some people looking at this page.\n\n\n[1] https://ibex-core.readthedocs.io/en/latest/copyright.html"}
+{"org": "lowRISC", "repo": "ibex", "number": 401, "state": "closed", "title": "[RTL] Fix single stepping on exceptions", "body": "When we single step over an instruction that causes an exception DPC\r\nshould be set to point to the exception handler (where we would have\r\ngone were we not single stepping).\r\n\r\nAs discussed on Zulip this looks to be the correct behaviour, see response to issue on riscv-debug-spec here https://github.com/riscv/riscv-debug-spec/issues/497"}
+{"org": "lowRISC", "repo": "ibex", "number": 400, "state": "closed", "title": "[DV] Fix bugs in mem_error test to circumvent test deadlock", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 398, "state": "closed", "title": "Debug fix", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 396, "state": "closed", "title": "[ibex_tracer] Ibex tracer improvements", "body": "This is an issue to collect points that could be improved or \"beautified\" in the instruction tracer. Please feel free to modify/add to this list.\r\n\r\n1) Improve printout alignment of the trace (see example below).\r\n2) Correctly handle invalid instructions (see example below).\r\n3) Add more information about exceptions.\r\n\r\nExample snippet where an all-zero instruction is interpreted as `c.addi4spn` instead of marking it as INVALID:\r\n```\r\n23688 11839 1a110354 00000013 addi x0,x0,0 x0:0x00000000 x0=0x00000000\r\n23696 11843 1a110358 7b302573 csrrs x10,0x7b3,x0 x0:0x00000000 x10=0x00000032\r\n23700 11845 1a11035c 00100073 ebreak \r\n23708 11849 1a110360 0000 c.addi4spn x0,x2,0 x0=0x00000000\r\n23726 11858 1a110808 04c0006f jal x0,1a110854 x0=0x00000000\r\n23736 11863 1a110854 7b351073 csrrw x0,0x7b3,x10 x10:0x00000032 x0=0x00000000\r\n23744 11867 1a110858 00000517 auipc x10,0x0 x10=0x1a110858\r\n23748 11869 1a11085c 00c55513 srli x10,x10,0xc x10:0x1a110858 x10=0x0001a110\r\n``` \r\n\r\nNote: there exist other opensource RISC-V cores that have a tracer (such as [Ariane](https://github.com/pulp-platform/ariane/blob/master/src/util/)). Maybe some synergy could be leveraged here and/or the format could be aligned...\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 395, "state": "closed", "title": "[DV] Let time-consuming checker tasks detect failures", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 394, "state": "closed", "title": "Is register CSR_MIE implemented ?", "body": "When accessing CSR_MIE register with the assembly code (rv32emc architecture)\r\n li t0, (0x00000001)<<11\r\n csrrs zero, mtvec, t0\r\nthe following simulation error message is received:\r\n\" Illegal instruction (core 0) at PC 0x00000090: 0x3042a073\"\r\nIn contrast the line csrrs zero, mtvec, t0 works well.\r\nSimulation shows the signal ibex_core.id_stage_i.illegal_csr_insn_i being high when error message occurs. Also inspection of the files ibex_cs_registers.sv and ibex_defines.sv doesn't show anything related to SCR_MIE.\r\nIs register CSR_MIE implemented in RTL?"}
+{"org": "lowRISC", "repo": "ibex", "number": 393, "state": "closed", "title": "ebreak instruction broken", "body": "The ebreak instruction is broken when executing in debug mode or when dcsr.ebreakm is set. The prevents the pulp riscv dbg module from working correctly as it extensively uses this instruction.\r\n\r\nThe root cause is the ID stage gets flushed as the controller transitions into DBG_TAKEN_ID but should probably remain valid and flush as part of the DBG_TAKEN_ID handling. Transitions into DBG_TAKEN_IF may have similar issues.\r\n\r\nI have a trial fix but more thought is required before I produce a PR."}
+{"org": "lowRISC", "repo": "ibex", "number": 392, "state": "closed", "title": "[DV] Add reset test", "body": "- Major changes to driver/monitor components throughout the testbench to allow for mid-test reset stimulus to be driven\r\n- Modifications to tb_top to move all clock and initial reset stimulus to `initial begin...end` blocks in the `clk_if`."}
+{"org": "lowRISC", "repo": "ibex", "number": 391, "state": "closed", "title": "Add support for FENCE.I instruction", "body": "As raised in https://github.com/lowRISC/ibex/issues/365 FENCE.I can be emitted by debuggers leading to an illegal instruction exception on Ibex as it doesn't support it.\r\n\r\nSupport should be fairly trivial (flush prefetch buffer and pipeline then continue)"}
+{"org": "lowRISC", "repo": "ibex", "number": 390, "state": "closed", "title": "[CI] Stop pinning an old attrs version", "body": "simplesat (required by fusesoc) was broken by an update to the attrs\r\nlibrary. Now simplesat 0.8.2 has been released which fixes the issue, we\r\ncan remove the explicit pinning of the old attrs version."}
+{"org": "lowRISC", "repo": "ibex", "number": 389, "state": "closed", "title": "Remove non-ASCII characters from .sv and .rst files", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 386, "state": "closed", "title": "Various lint improvements", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 384, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@ad6fe56", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 383, "state": "closed", "title": "[WIP] Allow setting RF implementation with FuseSoC use flag", "body": "**NOTE** This requires https://github.com/olofk/fusesoc/commit/0351dd09dfdd6a6a5e404d1375bf1fafd8b9652c which is not yet in a released FuseSoC version at this point\r\n\r\nFuseSoC has gained support for use flags. This patch adds support\r\nfor setting the Ibex RF implementation with the ibex_rf_latch use\r\nflag. Default is the FF implementation.\r\n\r\nExample: Run the verilator linter with the latch-based RF\r\nfusesoc run --target=lint --flag=ibex_rf_latch lowrisc:ibex:ibex_core"}
+{"org": "lowRISC", "repo": "ibex", "number": 382, "state": "closed", "title": "Add support for hardware breakpoints", "body": "It would be useful for Ibex to support hardware breakpoints (or triggers, as the RISC-V debug spec calls them). This would be done through at least the `tselect` and `tdataN` CSRs."}
+{"org": "lowRISC", "repo": "ibex", "number": 381, "state": "open", "title": "Add riscv compliance reference to doc", "body": "I did not find a reference in the online user manual to the `README.md` of the `riscv-compliance`.\r\n@imphil can you confirm this?"}
+{"org": "lowRISC", "repo": "ibex", "number": 380, "state": "closed", "title": "Update description for running RISC-V compliance", "body": "The RISC-V compliance test system requires an absolute path to the\r\nexecutable or one which starts at `riscv-test-suite/*`.\r\n\r\nI would be happy if someone could verify that a relative path starting in `$RISCV_COMPLIANCE_REPO_BASE` does not work."}
+{"org": "lowRISC", "repo": "ibex", "number": 379, "state": "closed", "title": "Remove reference to simulation", "body": "The testbench does not exist anymore. Was removed with #360 "}
+{"org": "lowRISC", "repo": "ibex", "number": 378, "state": "closed", "title": "[DV] Added unaligned memory error test", "body": "1) Enable unaligned memory ops in mem_error test\r\n2) Increase test iterations for some debug tests"}
+{"org": "lowRISC", "repo": "ibex", "number": 377, "state": "closed", "title": "[RTL LSU] Change unaligned error behaviour", "body": "- If an error is signalled in the first part of an unaligned\r\n transaction, the second part is issued anyway (to avoid a\r\n timing loop from data_err_i -> data_req_o)\r\n- Previously, the error was signalled and an exception was taken\r\n as soon as the first transaction completed. This commits makes\r\n the core wait until both transactions have completed.\r\n- This prevents strange behaviour caused by the lsu and controller\r\n being out of sync (fixes #374)."}
+{"org": "lowRISC", "repo": "ibex", "number": 376, "state": "closed", "title": "Bump minimum Verilator version", "body": "We currently don't document a specific version of Verilator. We use 4.016 in our CI at the moment, but the simulation should work with older versions at well. Instead of now documenting a arbitrary number, let's wait until we have a good reason for a bump.\r\n\r\nCurrently we have the following requirements:\r\n- at least 4.020: Remove workaround as discussed in #372\r\n\r\nExtend this issue over time, and then decide once we found a good version which is widely available to our users.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 375, "state": "closed", "title": "Tracer: Reference Verilator bug for miscompilation", "body": "This miscompilation is now reported and fixed, mention it in the code to\nrefer back to it when we can revert back to the old code (which will\ntake a couple months until we can require a newer Verilator version).\n\nFixes #372"}
+{"org": "lowRISC", "repo": "ibex", "number": 374, "state": "closed", "title": "DMEM fault during misaligned memory access", "body": "Hi all,\r\nWhen running this set of instructions:\r\n\r\nThe following waves were generated:\r\n\r\nThe `sw` instructions at `PC=0x800058d0` has a misaligned memory address, and is thus split into two internal memory transactions. In the waves, around 395,800,000ps corresponds to the memory response to the first of these two transactions, which is when the testbench randomly asserts a memory fault here. According to Ibex documentation for this situation, the second memory transaction should continue as normal, ignoring the response data, and then the core needs to also jump to the corresponding fault handler (located at `PC=0x80014000` in our case). The LSU's FSM transitions to it's error handling states from the misaligned transaction states, and the core jumps to `0x80014000` (which encodes the instruction `j 80014080`) directly after `0x800058d0`, but while executing this jump instruction, the core jumps to `0x8001e112` instead, throwing an illegal instruction exception, and then proceeds to wait for the `rvalid` corresponding to the second part of the original misaligned transaction. This occurs around 395,835,000ps, and after this, the core jumps back to the fault handler, and fully executes it. This intermediate PC of `0x8001e112` is calculated as the incorrect jump address from load address data that's already in the execution pipeline, and is muxed through due to `lsu_addr_incr_req_i` going high while waiting for the second half of the misaligned memory transaction to complete. Maybe a potential solution for this would be to only jump to the fault handler after the second part of the misaligned transactions has completed?\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 372, "state": "closed", "title": "Tracer: Debug miscompilation in decode_load_insn()", "body": "In https://github.com/lowRISC/ibex/blob/2acb497d22a5da877a9c4350ef5693d0c767cc61/rtl/ibex_tracer.sv#L584-L613 we switched from case to if statements to get around potentially wrong behavior in Verilator. Note that the `return` in the default statement hides that the default statement is always taken; the output without the return looks even more confusing.\r\n\r\nUpstream bug report at https://www.veripool.org/issues/1536-Verilator-Misoptimization-in-if-and-case-with-default-statement-inside-a-function"}
+{"org": "lowRISC", "repo": "ibex", "number": 371, "state": "closed", "title": "[DV] Top level toggle coverage", "body": "1) Enable toggle coverage of only top level I/O pins\r\n2) Tighten ibex log regex to exclude writes to `x0`"}
+{"org": "lowRISC", "repo": "ibex", "number": 370, "state": "closed", "title": "ebreak handling still assumes an M-mode only core", "body": "#343 added support for U-mode. One thing we missed was that the ebreak handling in ibex_controller.sv assumes the core is M-mode only. That is, it unconditionally checks dcsr.ebreakm when determining whether ebreak should enter debug mode, when it should check ebreakm/ebreaku depending on the current privilege level.\r\n\r\ncc @tomroberts-lowrisc @vogelpi"}
+{"org": "lowRISC", "repo": "ibex", "number": 369, "state": "closed", "title": "Add missing enum cast", "body": "Vivado doesn't compile the design without this cast."}
+{"org": "lowRISC", "repo": "ibex", "number": 368, "state": "closed", "title": "RISC-V Compliance test: Enable tracing", "body": "Use the tracing-enabled core wrapper when executing the RISC-V\ncompliance test suite to help with debugging it."}
+{"org": "lowRISC", "repo": "ibex", "number": 367, "state": "closed", "title": "Tracer: Fix default file name", "body": "We document the default file name to be trace_core_00000000.log, but\nactually used trace_core__00000000.log. Fix that."}
+{"org": "lowRISC", "repo": "ibex", "number": 366, "state": "closed", "title": "[DV] Update ibex log regex", "body": "Log parsing update to match the new modifications to the tracer.\r\nWill not merge until #360 is merged, to avoid breaking any current flows."}
+{"org": "lowRISC", "repo": "ibex", "number": 365, "state": "closed", "title": "mstatus.mie reset when hitting breakpoint", "body": "I'm currently evaluating PULPissimo platform with Ibex core and I encountered some strange behaviour with interrupts. It seems that after hitting breakpoint `mie` in `mstatus` register is reset to 0.\r\n\r\nHere is my setup:\r\n\r\n- PULPissimo with Ibex core and [pulp-platform/riscv-dbg](https://github.com/pulp-platform/riscv-dbg) as debug core,\r\n- ZedBoard (Xilinx Zynq, `master` version of all cores) and Terasic DE10-Nano (Altera Cyclone-V, with modifications to make the code compatible with Quartus),\r\n- Digilent HS2 JTAG programmer,\r\n- OpenOCD compiled basing on [instructions from PULPissimo](https://github.com/pulp-platform/pulpissimo/#gdb-and-openocd),\r\n- [pulp-platform/pulp-riscv-gnu-toolchain](https://github.com/pulp-platform/pulp-riscv-gnu-toolchain).\r\n\r\nOpenOCD config and log as well as gdb log (including issued commands) can be found [here](https://gist.github.com/MarekPikula/63bd5a35dcffa2361a1a7bc3de5642f9).\r\n\r\nCode:\r\n```c\r\n#include \r\n\r\nint main() {\r\n register int mstatus_mie = (1<<3); // mstatus.mie\r\n asm volatile (\"csrw 0x300, %0\" :: \"r\" (mstatus_mie) );\r\n\r\n uint32_t mstatus[3];\r\n asm volatile (\"csrr %0, 0x300\" : \"=r\" (mstatus[0]));\r\n asm volatile (\"nop\"); // First breakpoint\r\n\r\n asm volatile (\"csrr %0, 0x300\" : \"=r\" (mstatus[1]));\r\n asm volatile (\"nop\"); // Second breakpoint\r\n\r\n asm volatile (\"csrw 0x300, %0\" :: \"r\" (mstatus_mie) );\r\n asm volatile (\"csrr %0, 0x300\" : \"=r\" (mstatus[2]));\r\n asm volatile (\"nop\"); // Third breakpoint\r\n\r\n return 0;\r\n}\r\n```\r\n\r\nWhat the code does is set `mie` flag in `mstatus` register (0x300) and store it in `mstatus[0]`, then after hitting breakpoint read it to `mstatus[1]` and to confirm, `mstatus` register is written again and result stored in `mstatus[2]`.\r\n\r\nBasically after sending `x/3x mstatus` gdb returns: `0x00001808\t0x00001800\t0x00001808`, so in `mstatus[0]` and `mstatus[2]` `mie` flag is set, whereas in `mstatus[1]` it is not set, although, to my understanding, it should be recovered after going out of debug mode.\r\n\r\nIs it expected behaviour? If not what can I do to further test it?"}
+{"org": "lowRISC", "repo": "ibex", "number": 361, "state": "closed", "title": "Docs: Fix Sphinx warnings and errors", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 360, "state": "closed", "title": "New tracer", "body": "This PR is extending #280 to provide a Verilator-compatible tracer. In the process of doing the review in #280 I found various things which could be further simplified and took the opportunity to do that. Thanks @raulbehl for you starting point in #280, it's very much appreciated.\r\n\r\nThis PR contains a series of commits, the main one is rather large unfortunately. It's probably better not to look at the diff, but at the resulting code. From the main commit message:\r\n\r\n----\r\nThe ibex_tracer module implements an execution tracer, observing the\r\nexecution flow and writing a human-readable execution trace. The trace\r\ninformation is coming from the RVFI signals, as specified at\r\nhttps://github.com/SymbioticEDA/riscv-formal/blob/master/docs/rvfi.md.\r\n\r\nThe existing implementation was tailored for use in ModelSim and other\r\ncommercial simulators, and used SystemVerilog features which are not\r\nsupported in Verilator or Icarus Verilog, such as classes, queues and\r\nnon-standard format specifiers (e.g. the `-` specifier for right-aligned\r\noutput). Being unable to see an execution trace when using Verilator\r\nsignificantly reduced productivity and its usefulness.\r\n\r\nThis commit refactors the tracer to only use SystemVerilog constructs\r\nwhich are supported in Verilator. While doing so, multiple improvements\r\nwere made for correctness and style.\r\n\r\nMajor changes:\r\n\r\n- Improve compatibility with Verilator. Remove many non-synthesizable\r\n SystemVerilog constructs, such as classes and queues.\r\n Use casez instead of casex for better Verilator support (Verilator\r\n doesn't support X).\r\n- Make the decoded output of the tracer match objdump from binutils\r\n exactly. Doing so is beneficial for two reasons: we can easily\r\n cross-check the decoded output from the tracer against the disassembly\r\n produced by objdump (and we did that), and users don't need to get\r\n used to another slighly different disassembly format.\r\n- A plusarg \"+ibex_tracer_file_base=ibex_my_trace\" can be used to set a\r\n different basename for the trace log file.\r\n\r\nSmaller cleanups:\r\n\r\n- Remove decoding of reg-reg loads, which were leftover from a PULP\r\n extension.\r\n- Make better use of the data available on the RVFI. Pass all of RVFI\r\n to the tracer, and use the provided data instead of manually\r\n recreating it, e.g. to get register data or the jump target.\r\n- Rename all \"instr\" abbreviations to \"insn\". \"insn\" is what RVFI uses\r\n (and we cannot change that), so for consistency we now always use this\r\n abbreviation across the file.\r\n \r\nThe RISC-V compliance test suite for the RV32 I, M, and C extensions has\r\nbeen executed and traced. The disassembly of all traces have been\r\ncompared against traces produced by objdump to ensure identical output.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 358, "state": "closed", "title": "[DV]Add Makefile target for functional coverage", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 357, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@8e6fba0", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 8e6fba021d2dff44fee6b80777ac0b5ded0e488d\r\n\r\n* Signature_addr_reg constraint update (Udi)\r\n* Add a debug mode for functional coverage (google/riscv-dv#191)\r\n (taoliug)\r\n* Fix typo in README (google/riscv-dv#189) (taoliug)\r\n* Constrain scratch_reg (google/riscv-dv#188) (udinator)\r\n* Update README for the coverage flow (google/riscv-dv#187) (taoliug)\r\n* Add basic privileged CSR cover group (google/riscv-dv#186) (taoliug)\r\n* Fix cover point definition (google/riscv-dv#185) (taoliug)\r\n* Fix ovpsim log compare issue (google/riscv-dv#183) (udinator)"}
+{"org": "lowRISC", "repo": "ibex", "number": 356, "state": "closed", "title": "[rtl/ibex_core] Added missing parameter assignment", "body": "Added missing parameter assignment for PMPEnable of ibex_cs_registers."}
+{"org": "lowRISC", "repo": "ibex", "number": 354, "state": "closed", "title": "[DV] Refactor debug_stress and instr_fault stimulus to avoid race conditions with EOT checks", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 353, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@d341944", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision d3419444ca2fdb499a204587b2d36c6f5c1e0c44\r\n\r\n* Update README (Udi)\r\n* Add knob to enable full CSR randomization, fix mstatus.spp (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 351, "state": "closed", "title": "Tighten debug stimulus assertion", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 350, "state": "closed", "title": "[CI] Add Docker testing environment", "body": "Fixes #341.\r\n\r\nFollows tests in `azure-pipelines.yml`."}
+{"org": "lowRISC", "repo": "ibex", "number": 349, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@e3e1e30", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision e3e1e308cfc3d718aeb94bb3463371979d9a31ae\r\n\r\n* Disable full trace in the run script (google/riscv-dv#180) (taoliug)\r\n* Fix spike logging issue (google/riscv-dv#179) (taoliug)\r\n* Add functional coverage for HINT instructions (google/riscv-dv#177)\r\n (taoliug)\r\n* Add functional coverage for various hazard conditions (google/riscv-\r\n dv#176) (taoliug)"}
+{"org": "lowRISC", "repo": "ibex", "number": 348, "state": "closed", "title": "RVFI Interface - load/store memory faults", "body": "Hi all,\r\nQuick question regarding the RVFI, in particular [this section](https://github.com/SymbioticEDA/riscv-formal/blob/master/docs/rvfi.md#memory-access) regarding its set of memory access signals. The description for this whole set of signals specify that they should indicate only valid data, when applicable, but when I monitor these signals in Ibex after injecting a load or store error into the memory response, I see that these buses will still contain the calculated memory address and read/write data and corresponding mask, even though the assertion of the error signal should invalidate the transaction.\r\nI propose a modification where on invalid memory transactions (due to memory faults), the relevant R/W memory address/data signals are driven to 0. This would be similar to Ibex's RVFI implementation of `rd_wdata` and `rd_addr`, which are driven to 0 if `regfile_we` is not high for a given transaction. \r\nAny thoughts or suggestions would be welcome!\r\nBest,\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 347, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@4450592", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 44505927a70a6234b996d15f2e51bd1e2632b68e\r\n\r\n* Dump performance counters to testbench at EOT (Udi)\r\n* Fix a constraint issue (google/riscv-dv#174) (taoliug)\r\n* Allow split a long test to small batches (google/riscv-dv#173)\r\n (taoliug)\r\n* Fix ius compile problem (google/riscv-dv#172) (taoliug)\r\n* Add basic functional coverage for RV64IMC (google/riscv-dv#171)\r\n (taoliug)\r\n* Initial prototype of functional coverage (google/riscv-dv#169)\r\n (taoliug)"}
+{"org": "lowRISC", "repo": "ibex", "number": 346, "state": "closed", "title": "[DV] Fix implemented_csr[] compile issue", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 344, "state": "closed", "title": "[DV] Fix memory error test logic", "body": "- Updated the logic for memory fault checking test\r\n- Added virtual RVFI interface, TODO item to add some RVFI register checks to this test, waiting for #332 "}
+{"org": "lowRISC", "repo": "ibex", "number": 343, "state": "closed", "title": "[Priv modes] Add support for U-Mode", "body": "- General changes to suport U-mode (fixes #88)\r\n- Update documentation (also fixes #306)\r\n- Add priv mode flops to CSRs module\r\n- Propagate correct priv mode to PMP module\r\n- Fix various address matching bugs in PMP module\r\n- Implement CSR priv-mode permission checking\r\n- Implement illegal U-mode instruction checking\r\n- Add extra mstatus bits for U-mode (MPRV and TW)"}
+{"org": "lowRISC", "repo": "ibex", "number": 341, "state": "closed", "title": "Local CI tests", "body": "What do you think about making a local CI test solution based on Docker container? Currently that's how I'm testing my changes before commiting. I have simple Dockerfile doing pretty much all the initialisation part from `azure-pipelines.yml` and then I'm executing next commands by hand.\r\n\r\nWould anyone be interested in PR with this? I could polish the Dockerfile and write simple script executing all the tests."}
+{"org": "lowRISC", "repo": "ibex", "number": 340, "state": "closed", "title": "Instruction fetch error execution", "body": "Hi all,\r\n\r\n\r\nAbove is a snippet of disassembled code I was running on Ibex, and the associated section in the core tracer. At `PC=0x8000087c`, there should be a `nop` instruction, but Ibex shows execution of `lui x19, 0xabd6c000` at this PC.\r\n\r\nAt the location in the waves where the cursor is, the active `instr_grant` and `instr_rvalid` are responding to the `request` corresponding to the address `0x8000087c`. At the same time, the testbench randomly asserts an `instr_error` during the instruction fetch response, and randomizes the returned `instr_rdata`, as the request has returned with an error response. The random data here happens to be the value `0xabd6c9b7`, which Ibex decodes as the same exact `lui` instruction from above. We should expect that this should not be executed then, since an error was returned to the core, but we can see that at time 4,113,000ns, Ibex raises the register file `we_a_i` write enable signal, and writes the data `0xabd6c000` to register `0x13`, effectively completing execution of this random instruction data even though there was an instruction fetch error associated with this response. Immediately after completing execution of the randomly generated data at `PC=0x8000087c`, the core jumps to the instruction fetch exception handler at `PC=80014000`, and runs the handler code.\r\nThis issue only exists for the instruction fetch interface; for similar situations involving load/store errors that the testbench generates, Ibex will not commit load data to the regfile, or write store data to our memory model, and will only run the faulty memory instruction to completion once it has finished executing the associated exception handler code."}
+{"org": "lowRISC", "repo": "ibex", "number": 339, "state": "closed", "title": "Tracing: Wrap fatal error message with `$fatal()`", "body": "The syntax of this statement is not correct without the `$fatal()` SV construct. This causes errors in some tools even if the error condition is not met."}
+{"org": "lowRISC", "repo": "ibex", "number": 337, "state": "closed", "title": "[DV] Shorten length of interrupt tests to prevent timeouts", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 336, "state": "closed", "title": "[RTL] Quartus compatibility", "body": "I am working on porting PULPissimo project to support Altera/Intel Quartus and thus Intel FPGAs. Besides issues stated in #117 I had some weird problems with core not willing to enter debug mode. As it turns out Quartus isn't interpreting SystemVerilog in the same way as Vivado does (I'm currently documenting all the stuff I've stumbled upon [here](https://github.com/MarekPikula/quartus-sv-gotchas)) and makes some assumptions regarding `case` statement, which are not necessarily true.\r\n\r\nIn this commit I propose some changes, which result in correct RTL for Quartus (didn't test it in Vivado yet, but I guess it should work just fine) and IMHO make the code more readable in some places.\r\n\r\nIt's definitely not to be merged since I'd need to make some correct indentation and some cosmetic changes for a final version. I just wanted to make changes only in the places, which have indeed been changed, so that the diff is more readable. Purpose of this PR is to open discussion on some specific places in code, which don't synthesize correctly with Quartus.\r\n\r\nHere's the list of changes with explanations:\r\n\r\n## ibex_cs_registers.sv\r\n\r\nHere is the place where Quartus just cut entire `default` section (line 319 in upstream), leaving `illegal_csr` high for some reason. I presume that it's caused by some partial cases being handled before (like `CSR_MCOUNTINHIBIT`, `CSR_MCYCLE`, …).\r\n\r\n### CSR read logic \r\nSince we don't use `unique case inside` as pointed out in [style guides](https://github.com/lowRISC/style-guides) (this construct isn't supported in Quartus either way) I propose to use `casez` with wildcarded `CSR_OFF_MCOUNTER_SETUP`, `CSR_OFF_MCOUNTER` and `CSR_OFF_MCOUNTERH` with internal `unique case` for distinguishing between subaddresses in the same address range. This results in less code and IMHO more readable code, as a reader now clearly sees that these subaddresses are indded in this address range and that not all subaddresses are illegal as code suggests.\r\n\r\n### CSR write logic\r\n\r\nSimilar thing is done for write section and I'd have suggestion to change assignment for `illegal_csr_write` from global assign without much meaning to an assignment inside this case statement for particular cases and some additional ones, which are not handled by global assign.\r\n\r\nAnother thing, which reduces clutter is making `if (csr_we_int == 1'b1)` condition outside case statement. That's a minor change not particularly connected with topic of this PR, but I'd say it makes the code more readable.\r\n\r\n### Use of constant expression in case statement\r\n\r\nAs stated [here](https://github.com/MarekPikula/quartus-sv-gotchas/blob/master/Intel%20Quartus%20SystemVerilog%20gotchas.md#1252-constant-expression-in-case-statement) it simply doesn't synthesize correctly. For example for the code starting at line 499 in upstream the synthesizer basically replaced this case statement with `exception_pc = pc_if_i;` totally ignoring the second case. Correct me if I'm wrong, but I think that syntax in my patch is equivalent to constant expression case.\r\n\r\n## ibex_id_stage.sv and ibex_multdiv_fast.sv \r\n\r\nThe only problem was constant expression case."}
+{"org": "lowRISC", "repo": "ibex", "number": 335, "state": "closed", "title": "[RTL] Flop exc_req in controller to ease timing", "body": "Fixes #305\r\n\r\n@udinator would you be able to run some tests on this change? I've done some basic tests to ensure exceptions continue to function but if you had something more in-depth to try out that would be useful."}
+{"org": "lowRISC", "repo": "ibex", "number": 334, "state": "closed", "title": "[DV] Drive external stimulus to 0 after reset", "body": "Addresses #301."}
+{"org": "lowRISC", "repo": "ibex", "number": 333, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@80d4294", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 80d429475138b4b94d863030246a06980c89889d\r\n\r\n* Fix mstatus randomization issue (google/riscv-dv#168) (taoliug)\r\n* Lower the percentage of JAL instruction (google/riscv-dv#167)\r\n (taoliug)\r\n* Add an option to run a directed assembly test with ISS\r\n (google/riscv-dv#166) (taoliug)\r\n* Add memory fault handlers (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 332, "state": "closed", "title": "[Prefetch buffer] - various bug fixes", "body": "- Fix incorrect address output to mepc on interrupt (fixes #320)\r\n- Fix instruction address changing before grant (fixes #296)\r\n- Remove excess address flops in fetch_fifo\r\n- Remove restriction on outstanding requests"}
+{"org": "lowRISC", "repo": "ibex", "number": 331, "state": "closed", "title": "[Doc] Add more pipeline details", "body": "Still need to add a bit more detail on how the long division algorithm works but not yet sure if it's latency is fixed or if it has an early out (looking at the state machine looks like there is a data dependent way for it to finish early).\r\n\r\nI'd suggest looking at the actual rendered docs. You just need to checkout my pipeline_docs branch and do a 'make html' in the doc/ directory. You may need a 'make clean' beforehand as I've seen it fail to correctly rebuild in some cases."}
+{"org": "lowRISC", "repo": "ibex", "number": 330, "state": "closed", "title": "Add memory error testing", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 328, "state": "closed", "title": "[DV] Add dsim support", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 326, "state": "closed", "title": "Lint: Fix parameter width", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 325, "state": "closed", "title": "Compliance test suite: Prefer D over I accesses", "body": "Give higher priority to data accesses from the CPU to improve\r\nperformance. This is the recommended setup for Ibex."}
+{"org": "lowRISC", "repo": "ibex", "number": 324, "state": "closed", "title": "[DV] Add interrupt testing, and update some debug test checks", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 323, "state": "closed", "title": "Integrate with the new riscv-dv user extension flow", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 322, "state": "closed", "title": "Compressed tracer load/store issue", "body": "Hi @raulbehl,\r\nI'm seeing some weird behavior with the tracer (from #262) involving long runs of compressed `lw` or `sw` instructions, below is the disassembled instruction sequence that is getting executed:\r\n\r\nAnd, below is what Ibex tracer is printing out for the exact same sequence:\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 321, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@0d2b5b7", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 0d2b5b7b8b1cdbce74d9e123a427052b12accd7b\r\n\r\n* Add user extension support (google/riscv-dv#163) (taoliug)\r\n* Update README (google/riscv-dv#162) (taoliug)\r\n* Fix compilation issue (google/riscv-dv#161) (taoliug)\r\n* Fix compilation issue (google/riscv-dv#160) (taoliug)\r\n* Adding dsim support (google/riscv-dv#159) (taoliug)\r\n* Fix RV64A typo (google/riscv-dv#158) (taoliug)"}
+{"org": "lowRISC", "repo": "ibex", "number": 320, "state": "closed", "title": "Incorrect `mepc` value after irq is taken", "body": "Hi all,\r\nDuring a test, this segment of code is running on the core:\r\n\r\nAt `PC=0x80000276` (a `nop` instruction), our testbench asserts a software interrupt, as shown from the waves below:\r\n\r\nHowever, we see that `mepc_q` gets set to `0x80000274` after this interrupt is detected and handling begins, meaning that after the interrupt handler has ended, the core will jump back to this address, but as you can see from the code snippet, this is a misaligned address, so Ibex immediately takes an illegal instruction exception, and fails the test. This address comes from the `exception_pc`, which is muxed to the value of `pc_if_i`, which for some reason is set to this misaligned address, and is less than the `pc_id_i`."}
+{"org": "lowRISC", "repo": "ibex", "number": 317, "state": "closed", "title": "Remove dependency on DPI calls from Verilator SimCtrl", "body": "Verilator SimCtrl currently will not link correctly unless an external function \"simutil_verilator_memload\" is defined, and a SystemVerilog module containing at least one DPI call is included in the file list.\r\n\r\nSuggestion - split all the memory loading functionality into a separate class/file which can be left out if not needed."}
+{"org": "lowRISC", "repo": "ibex", "number": 316, "state": "closed", "title": "[DV] Fix latch in simple bus", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 313, "state": "closed", "title": "Fix regression failure", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 312, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@c98d89c", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision c98d89cdff7b56d9911904e05e6b46e005233280\r\n\r\n* Interrupt test integration (Udi)\r\n* Update README for illegal/hint instruction (google/riscv-dv#155)\r\n (taoliug)\r\n* Refactor illegal/hint instruction generation (google/riscv-dv#154)\r\n (taoliug)\r\n* Skip x0 in GPR save/restore (google/riscv-dv#153) (taoliug)\r\n* Move user_define.h to the beginning of the program (google/riscv-\r\n dv#151) (taoliug)\r\n* Add user_define.h (google/riscv-dv#149) (taoliug)\r\n* Move instr_bin to a separate section (google/riscv-dv#148) (taoliug)\r\n* Remove temp files (google/riscv-dv#145) (taoliug)\r\n* Move dv_defines.svh outside the package (google/riscv-dv#144)\r\n (taoliug)\r\n* Fix typo (google/riscv-dv#141) (taoliug)\r\n* Refactored loop instruction stream, reduce global reserved registers\r\n (google/riscv-dv#139) (taoliug)\r\n* Remove obsolete sample program (google/riscv-dv#138) (taoliug)\r\n* Update readme (google/riscv-dv#137) (taoliug)\r\n* Skip kernel instruction/data pages when not needed (google/riscv-\r\n dv#136) (taoliug)\r\n* Re-organize data page generation (google/riscv-dv#135) (taoliug)\r\n* Re-organize text and data section (google/riscv-dv#134) (taoliug)\r\n* Refine the bare program mode (google/riscv-dv#133) (taoliug)\r\n* Add a bare program mode (google/riscv-dv#130) (taoliug)\r\n* Allow running riscv-dv from other directories (google/riscv-dv#128)\r\n (taoliug)\r\n* Fix trace compare issue (google/riscv-dv#123) (taoliug)\r\n* Optimize for constraint solving performance (google/riscv-dv#122)\r\n (taoliug)\r\n* Avoid ISS simulation timeout (google/riscv-dv#121) (taoliug)\r\n* Optimize irun randomization performance (google/riscv-dv#120)\r\n (taoliug)\r\n* fix ius compile/simulation warnings (Tao Liu)\r\n* Fix ius compilation failure (Tao Liu)\r\n* Fix google/riscv-dv#109 ius constraint solver failure (Tao Liu)\r\n* Add ebreak sequence generation and cmdline options (Udi)\r\n* Added dret instruction to random generation (Udi)\r\n* Tighten up regex in spike log tracer. (Dave Estes)\r\n* Fix generation of debug handshake (Udi)\r\n* Fix wfi generation, add indent to core_initialization handshake\r\n (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 311, "state": "closed", "title": "Simple system", "body": "Opening this PR now so I can get some feedback. Currently missing documentation (beyond a few comments) which I intend to write as part of the PR but want to avoid re-writing it if there's lot of stuff to change.\r\n\r\nIt should sit on top of my pcount stuff so that's also dragged into this PR, will rebase this on top of ibex once that is merged in."}
+{"org": "lowRISC", "repo": "ibex", "number": 310, "state": "closed", "title": "Basic memory transaction latency", "body": "During basic memory transaction Load-Store Unit expects signals data_gnt_i and data_rvalid_i to become active one after another (see Figure 3 at https://ibex-core.readthedocs.io/en/latest/load_store_unit.html). This introduces one additional cycle of access latency.\r\n\r\nFor better system bus performance it's interesting to allow both data_gnt_i and data_rvalid_i become active simultaneously. I tried such scenario. It doesn't work due to Load-Store Unit FSM architecture.\r\nIs there a chance to fix that?\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 309, "state": "open", "title": "Create page tracking tape out information (and maybe comparison?)", "body": "It would be awesome if you had a \"information from tape outs\" type page in the documentation somewhere. I would like to see it have the following information;\r\n\r\n - [ ] What was taped out\r\n - [ ] Who it was taped out with (IE Foundry, Node, PDK, Process, etc)\r\n - [ ] What type of tape out it was, test chip, production run, etc....\r\n - [ ] What tools were used\r\n - [ ] What was the resulting gate count\r\n - [ ] What was the resulting silicon area usage (mm x mm)\r\n - [ ] Some performance / energy specs.\r\n\r\nThe idea is to quickly get an idea for;\r\n - [ ] How frequently the core is being taped out.\r\n - [ ] What the most popular way to tape out the IC is (who is being used, what node, etc)\r\n - [ ] Ballpark around expected size and performance\r\n\r\nThere is some great information in the \"Slow and Steady Wins the Race? A Comparison of\r\nUltra-Low-Power RISC-V Cores for Internet-of-Things Applications\" paper you link too. However, it would be good to have a quick summary to look at.\r\n\r\nFYI The information from that paper says;\r\n> Zero-riscy is 2.2× smaller than Riscy and provides a 2× energy boost for mixed control/arithmetic code with limited DSP. Micro-riscy is 1.6× smaller than Zero-riscy (∼11.6 kgates in UMC 65nm), has a power envelope of just 100μW at 160MHz and it is 1.4× more energy efficient than Zero-riscy on pure control code.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 307, "state": "closed", "title": "Document debug CSRs", "body": "Document dscratch0, dscratch1 and dpc CSRs in the CSR documentation, and link them from the debug documentation page."}
+{"org": "lowRISC", "repo": "ibex", "number": 306, "state": "closed", "title": "Documentation: PMP documentation table rendering is broken", "body": "This table isn't being rendered correctly:\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 305, "state": "closed", "title": "Potential timing issues around pc_set", "body": "The pc_set signal factors in both exceptions that have just occurred and branch conditions and directly feeds into the top-level instr_addr_o output (and associated signals). This is a long path making the instruction memory interface outputs late.\r\n\r\nThe paper 'Slow and Steady Wins the Race? A Comparison of Ultra-Low-Power RISC-V Cores for Internet-of-Things Applications' (https://www.researchgate.net/profile/Francesco_Conti4/publication/321121782_Slow_and_steady_wins_the_race_A_comparison_of_ultra-low-power_RISC-V_cores_for_Internet-of-Things_applications/links/5a37aa3ea6fdccdd41fc99e1/Slow-and-steady-wins-the-race-A-comparison-of-ultra-low-power-RISC-V-cores-for-Internet-of-Things-applications.pdf) which looked at zero-riscy highlighted this path as the worst in their test system.\r\n\r\nThe simple fix (stall and set the pc cycle after branch decision/exception) adds a cycle latency to any branch. A simple branch predictor may be able to reduce the impact of this."}
+{"org": "lowRISC", "repo": "ibex", "number": 304, "state": "closed", "title": "C/C++ Lint: Document its use and enforce it", "body": "#303 added a clang-format configuration to this repository to lint C/C++ code. We should \r\n- Document our expectations on how developers run it, and possibly provide helper scripts for that.\r\n- Run clang-format in CI on the patch."}
+{"org": "lowRISC", "repo": "ibex", "number": 303, "state": "closed", "title": "Add clang-format configuration for C/C++ files", "body": "We have more and more C/C++ code in this repository. Add a clang-format configuration following the standard lowRISC coding style to help developers format their code consistently."}
+{"org": "lowRISC", "repo": "ibex", "number": 302, "state": "closed", "title": "Controller: fix `nmi_mode` default assignment", "body": "Without this commit, the `nmi_mode` register is continuously cleared and set again, and the core can never handle the NMI.\r\n\r\nThis resolves lowRISC/ibex#300 reported by @udinator."}
+{"org": "lowRISC", "repo": "ibex", "number": 301, "state": "closed", "title": "Core_sleep_o issue", "body": "Hi,\r\nI was running a `wfi` test, expecting the new `core_sleep_o` signal (#284) to be asserted after the `wfi` started being executed, but instead it looks like this signal remains at `1'b0` for the entire test, and switches to `1'bX` at some points as well, as shown in the waveform below:\r\n\r\nAdditionally, there may be an issue with `clock_en`, as it is `1'b1` through the entire simulation, but changes to `1'bX` after a `wfi` is executing."}
+{"org": "lowRISC", "repo": "ibex", "number": 300, "state": "closed", "title": "Non-maskable interrupt handling", "body": "Hi all,\r\nIn testing Ibex's interrupt interface, I ran into the following situation:\r\n\r\nI drive `irq_nm_i`, signaling a non-maskable interrupt to Ibex. Since Ibex treats interrupts as level sensitive, and relies on handler routines to deassert the interrupt lines, I treat non-maskable interrupts the same way, and leave it driven to `1'b1` until the handler code is completed. However, Ibex, after jumping into the `DECODE` state from `IRQ_TAKEN` upon detection of the `irq_nm`, seems to keep detecting that `irq_nm` is high, and then infinitely loops between the `DECODE` and `IRQ_TAKEN` states, causing the simulation to time out. Since according to #199 as well as the docs this seems to be incorrect behavior for `irq_nm`, would it be possible to clarify what expected behavior for non-maskable interrupt should be? "}
+{"org": "lowRISC", "repo": "ibex", "number": 299, "state": "closed", "title": "Add performance counter utils for verilator sims", "body": "These aren't used anywhere yet but have been tested with some verilator stuff I have locally.\r\n\r\nThey could live under dv/verilator/simutil_verilator but there's no reason it couldn't be used independently of that so put it under it's own directory.\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 298, "state": "closed", "title": "[DV] Add registers testbench", "body": "- Sample C++ unit testbench for system registers module\r\n- Only tests a few PMP registers at the moment"}
+{"org": "lowRISC", "repo": "ibex", "number": 297, "state": "closed", "title": "riscv-compliance test system: Fix arbitration error in bus", "body": "@GregAC mentioned that this code\r\n\r\nhttps://github.com/lowRISC/ibex/blob/ac22439374a0bafd6fc2f9d38aefc02e44fa2abb/dv/riscv_compliance/rtl/bus.sv#L57-L64\r\n\r\ndoesn't work as expected in Verilator and gives out grants to two hosts at the same time. \r\n\r\n@GregAC can you\r\n- Double-check what the standard and other tools say should be the right behavior?\r\n- If this happens to be a bug in Verilator, file a bug report.\r\n- And possibly try to find a workaround?"}
+{"org": "lowRISC", "repo": "ibex", "number": 296, "state": "closed", "title": "Instruction address changes before a request/grant handshake", "body": "The instruction interface of Ibex allows to change the address while asserting request and waiting for a grant. This behavior is inherited from RI5CY. If I remember correctly, the primary reason for having this in RI5CY is that in multi-core configurations (PULP) with a shared instruction cache, it allows to reduce contention on the cache and leads to notable performance gains. This can also be beneficial for performance in Ibex (e.g. in case the core takes a branch while the instruction interface is still waiting for the grant of a previous request) but has over and over again confused people.\r\n\r\nThere were several GitHub issues where we needed to explain this to users, but the problem was usually something else. However, we never had an issue to discuss if we want to change this behavior or keep it.\r\n\r\nI think we should remove it. Ibex is a different core that does not target multi-core configs with shared I-caches, so the actual performance benefit is probably relatively low. Instead, it is confusing and complicates translation into popular protocols such as AXI/AHB (it is however legal for TileLink interconnects) as mentioned in pulp-platform/riscv#128.\r\n\r\nWDYT?\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 293, "state": "closed", "title": "[I-side] - Fix issues found in tracing example", "body": "- Fixes #288\r\n- Add missing grant qualification to stop spurious address updates\r\n- Make RTL robust to spurious rvalid signalling"}
+{"org": "lowRISC", "repo": "ibex", "number": 291, "state": "closed", "title": "Instruction set extensions M and C may be swapped", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 290, "state": "closed", "title": "Incorrect irq_fast ID assignment", "body": "According to the documentation, Ibex should assign all of the fast interrupts `irq_fast_i[14:0]` an ID from 16 to 30, so that `irq_fast_i[0]` has an ID of 16, `irq_fast_i[1]` has an ID of 17, and so on. In the [Ibex CSR register file](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_cs_registers.sv#L572), the entire 15 bit array is output to the [Ibex controller module](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_controller.sv#L165), where `mfip_id` is assigned based on on the value of `irq_fast_i[14:0]`. However these assigned IDs are between 0 and 14. Later on in the controller, `exc_cause_o` is [assigned](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_controller.sv#L363) by appending 1'b1 to `mfip_id`. This is sent to the [Ibex IF stage](https://github.com/lowRISC/ibex/blob/master/rtl/ibex_if_stage.sv#L109), where the 5 bit `irq_id`, which in this case is the ID assigned earlier in the controller, is multiplied by `0x4` and added to the address held in `mtvec` to get the trap address. However, the ID's of all fast interrupts are still from 0 to 14, which seems incorrect according to the RISC-V Privileged Spec Ch. 3.1.16. This means that there are now conflicts with all other interrupts that have ID's between 0 and 14, so Ibex will now jump to the wrong vectored address for all fast interrupts that are sent to the core. I think the `irq_fast` ID assignments in the CSR file should be from between 16 to 30 to fix this issue and comply with the spec."}
+{"org": "lowRISC", "repo": "ibex", "number": 289, "state": "closed", "title": "Fix syntax error", "body": "Fix a syntax error introduced by #284, addresses the first part of #287 "}
+{"org": "lowRISC", "repo": "ibex", "number": 288, "state": "closed", "title": "Ibex tracing example needs update following the changes in prefetch buffer", "body": "The recent changes to I-side logic and prefetch buffer has changed how ibex asserts `instr_req_o`. Due to this the current example in the TB doesn't produce the intended results. The delays in the TB would need to be adjusted as per the new logic.\r\n\r\nFYI: Here are the contents of the `trace_core_00000000.log`\r\n```\r\n Time Cycles PC Instr Mnemonic\r\n 240 8 00000080 00008106 c.mv x2, x1 x2=0x00000000 x1:0x00000000\r\n 250 9 00000082 00008186 c.mv x3, x1 x3=0x00000000 x1:0x00000000\r\n 290 13 00000090 00400113 addi x2, x0, 4 x2=0x00000004\r\n 310 15 00000094 ff810113 addi x2, x2, -8 x2=0xfffffffc x2:0x00000004\r\n 340 18 00000098 4000006f jal x0, 1024\r\n 390 23 00000498 039597b3 mulh x15, x11, x25 x15=0x00000000 x25:0x00000000 x11:0x00000000\r\n 400 24 0000049c 13410d13 addi x26, x2, 308 x26=0x00000130 x2:0xfffffffc\r\n 410 25 000004a0 e1070713 addi x14, x14, -496 x14=0xfffffe10 x14:0x00000000\r\n 420 26 000004a4 fff7c793 xori x15, x15, -1 x15=0xffffffff x15:0x00000000\r\n```\r\nThe trace ends abruptly at `420ns` (since now the timing between `instr_req_o`, `instr_gnt_i` & `instr_valid_i` isn't in-sync anymore).\r\n\r\nAlso, it would be nice if we could come up with a new naming scheme for the dumped filename? The current one has way too many zeros getting appended!"}
+{"org": "lowRISC", "repo": "ibex", "number": 287, "state": "closed", "title": "Compile issues while running ibex-tracer example", "body": "Hi, \r\n\r\nIbex top is broken due to the changes in the following commits:\r\n\r\nbec84ca2b1\r\nMissing a `,` after the port connection: https://github.com/lowRISC/ibex/blob/60de915d6b85b61a4981263c7a7fa8fa922d3f4d/rtl/ibex_core_tracing.sv#L151\r\n\r\nand \r\n\r\n16177fe8db\r\n`NUM_REQS` is not defined: \r\nhttps://github.com/lowRISC/ibex/blob/60de915d6b85b61a4981263c7a7fa8fa922d3f4d/rtl/ibex_fetch_fifo.sv#L222\r\n\r\nI am surprised to see how CI failed to catch these. The second one probably makes sense since the verilator compilation wouldn't see the assertions due to a guarding `ifndef VERILATOR`. But the first one should have been caught! "}
+{"org": "lowRISC", "repo": "ibex", "number": 285, "state": "closed", "title": "Dcsr.xdebugver reset value", "body": "Hi all,\r\nI noticed that in the CSR register module, `dcsr.xdebugver` is set to `XDEBUGVER_NO` upon reset, but after reset is over and an explicit write to `dcsr` occurs, the `xdebugver` field will then be permanently set to the value of `XDEBUGVER_STD` for the duration of the simulation. This seems to contradict with the behavior of the `dcsr.prv` field, which is set to `PRV_LVL_M` at reset, as well as whenever a write occurs outside of reset. Why does this separate reset behavior for `xdebugver` occur, instead of setting it to `XDEBUGVER_STD` from reset onwards especially since this field is read-only and stays as a constant?\r\nThank you!\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 284, "state": "closed", "title": "Add core_sleep_o to ibex interface (fixes #258)", "body": "Signals the core is totally idle (WFI with no outstanding memory\r\ntransactions)."}
+{"org": "lowRISC", "repo": "ibex", "number": 282, "state": "closed", "title": "[RTL] Fix I-side timing loop", "body": "- See issue #265 (partially fixes)\r\n- Remove path from instr_rvalid_i to instr_req_o\r\n- Prefetch buffer unit can now issue up to two outstanding requests\r\n- Structure moved from state machine to request queue\r\n- Change fetch fifo to use an unaligned flag rather than updating\r\n the address each time"}
+{"org": "lowRISC", "repo": "ibex", "number": 281, "state": "closed", "title": "Added dret and ebreak tests", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 280, "state": "closed", "title": "Add verilator support to Ibex tracer", "body": "- Removed the tracer class in the ibex_tracer file and implemented class methods and properties as functions and global variables\r\n- Updated the class new method with init function which implements the same functionality\r\n- Updated usage of queues to systemverilog arrays of structs\r\n- Updated $fwrite function to use verilator friendly string formatting\r\n- Added verilator top-tb which performs the same sequence of instructions as the system-verilog top tracing TB\r\n- Updated top_tracing_sim.core file to support verilator as well"}
+{"org": "lowRISC", "repo": "ibex", "number": 279, "state": "closed", "title": "Replace cluster_id/core_id with hart_id (Fixes #29)", "body": "Uncertain if we actually want a HartIDWidth parameter or just hard-code it to 32 bit."}
+{"org": "lowRISC", "repo": "ibex", "number": 278, "state": "open", "title": "Implement time CSR", "body": "We have `mtime` implemented. When implementing U mode (#88) we also need to implement `time`.\r\n\r\nTo simplify the implementation we can implement it via software trap handler, and document how such a trap handler should look like."}
+{"org": "lowRISC", "repo": "ibex", "number": 277, "state": "closed", "title": "CSR: Access checks on Debug CSRs", "body": " - The RISC-V Debug Spec v.0.13.2 (p.41) mandates that the core\r\n debug CSRs dcsr, dpc, dscratch0 and dscratch1 must not be\r\n accessible if not in debug mode. Fixes #275"}
+{"org": "lowRISC", "repo": "ibex", "number": 275, "state": "closed", "title": "Accessing debug CSRs while not in debug mode", "body": "The RISC-V Debug Spec v.0.13.2 (p.41) mandates that the core debug CSRs `dcsr`, `dpc`, `dscratch0` and `dscratch1` must not be accessible if not in debug mode. Currently, Ibex always allows accesses to these. This should be changed.\r\n\r\nSee also pulp-platform/riscv#136.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 274, "state": "closed", "title": "Assertion needs to be disabled while reset is asserted", "body": "There are a few assertions in ibex_load_store_unit which are not disabled while reset is asserted. This could cause some false firing if some signals are x when reset is asserted.\r\n\r\ne.g. ibex_load_store_unit.sv:457\r\n\r\n```\r\n assert property (\r\n @(posedge clk) (CS == IDLE) |-> (data_rvalid_i == 1'b0) );\r\n\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 273, "state": "closed", "title": "Update comments in latch-based register file", "body": "This commit updates the comments inside the latch-based register file. Some of them were outdated or just wrong."}
+{"org": "lowRISC", "repo": "ibex", "number": 272, "state": "closed", "title": "Fix behavior of DRET executed outside debug mode", "body": "Executing a DRET instruction outside of debug mode now causes an illegal instruction exception as mandated by the Debug Spec v0.13.2 p.41.\r\n\r\nThis resolves lowRISC/ibex#270."}
+{"org": "lowRISC", "repo": "ibex", "number": 271, "state": "closed", "title": "Update ibex_register_file_latch.sv", "body": "Fix latch to transparent on low"}
+{"org": "lowRISC", "repo": "ibex", "number": 270, "state": "closed", "title": "DRET treated as normal instruction in M-mode", "body": "\r\nWhile executing this code in M-mode and with no external debug/irq stimulus applied, the log shows ibex executing a dret and then jumping to `PC=0x00000000`, and the instruction at this address raises an illegal instruction exception, causing a jump to our vectored trap handler at `0x8001c000`.\r\n\r\nIn the waveform, we see that ibex recognizes the `dret` instruction, raising `dret_insn_dec`, but then when the core jumps to `FLUSH` state it executes the instruction as normal, and sets the next pc to `PC_DRET`, the value stored in the `dpc` CSR, or `0x00000000`. However according to the debug spec, executing `dret` while not in Debug Mode should cause an illegal instruction exception (Debug Spec, chapter 4.6), which does not seem to be the case in this situation."}
+{"org": "lowRISC", "repo": "ibex", "number": 268, "state": "closed", "title": "Update interrupt mode, add debug mode WFI test, update EOT mechanism", "body": "- Expanded dut_if to monitor other system instructions (ebreak/dret/mret/wfi)\r\n- Added debug_wfi test, and instantiated new debug/irq sequences to be used in directed test cases, allow test to have fine grain control over their send_req() task\r\n- Added testlist option to switch between this fine grain sequence or the original stress stimulus sequence\r\n- Slight modifications to sim.py to scan the ibex_report_server output before performing sim log comparisons to determine whether this comparison is at all necessary"}
+{"org": "lowRISC", "repo": "ibex", "number": 267, "state": "closed", "title": "Lint: Update Verilator waiver file", "body": "PR #236 broke the Verilator lint since lines changed. Fix that."}
+{"org": "lowRISC", "repo": "ibex", "number": 265, "state": "closed", "title": "Combinational paths between RVALID_I/ERR_I and REQ_O", "body": "Description: Combinational paths exist from data_rvalid_i and data_err_i to data_req_o and from instr_rvalid_i to instr_req_o. Such paths can potentially limit the achievable performance in systems that do not pipeline these signals as they would introduce a path from a slave to the master (i.e. Ibex) and then back to the slave. For details see the attached pdf.\r\n\r\nGit tag: 242147239551be9fb8523fbc6f26f22b898d8d93 (august 26 2019)\r\n\r\n[IBEX0.pdf](https://github.com/lowRISC/ibex/files/3546206/IBEX0.pdf)\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 264, "state": "closed", "title": "Integrate risc-v stream generator handshake into Ibex sim flow", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 263, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@faddfa4", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision faddfa49f456f3f8ef8c4231865994b7b13aa96d\r\n\r\n* Obsolete test clean up (Tao Liu)\r\n* Remove the old flow (Tao Liu)\r\n* minor fix, update README for A extension support (Tao Liu)\r\n* Add basic atomic instruction test (Tao Liu)\r\n* Add RV32A/RV64A instructions (google/riscv-dv#95) (Tao Liu)\r\n* Fix the missing GPR save operations for exception handling (Tao Liu)\r\n* Generate handshake sequence to communicate with testbench (Udi)\r\n* Fix compare error (Tao Liu)\r\n* Fix compare error (Tao Liu)\r\n* Initial signature enum for handshake protocol (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 261, "state": "closed", "title": "[ibex tracer] enhancement request - runtime knob to disable tracer", "body": "At chip level DV, we \"stub\" the ibex cpu by forcing its clk_i to 0 and taking control of the TL interface by overdriving it with our TL transactor. The advantage of doing that is choosing to 'stub' the cpu becomes a runtime config knob / setting as opposed to being a build time, which reduces overhead in terms of requiring additional parallel builds. \r\n\r\nIn chip level dv tests where the ibex core is stubbed, the ibex tracer still appears to be running. I would like to request that it be enhanced through a runtime plusarg setting (call it \"enable_ibex_tracer\" or something similar), that is set to 1 by default. Users can override it via plusarg to set it to 0. If set to 0, then the tracer should stay dormant (and it should not even create the log file). \r\n\r\nThanks\r\nSri"}
+{"org": "lowRISC", "repo": "ibex", "number": 260, "state": "closed", "title": "Correct a typo in doc/verification.rst", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 258, "state": "closed", "title": "Signal “core idle” to users outside of the core", "body": "We need to add a top-level signal indicating that the core is in WFI and completely idle.\r\n\r\nIt's a good indication for the power manager to know that the core is completely quiescent, and it is safe to switch off power without leaving a hanging transaction on the bus. The outside hardware world needs some kind of indication that upon WFI ibex is truly idle, and not for example secretly doing prefetches. "}
+{"org": "lowRISC", "repo": "ibex", "number": 254, "state": "closed", "title": "Update google_riscv-dv to 73274f2", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 73274f227000f1316cb201a8503aad437e427948\r\n\r\n* Merge pull request #88 from google/dev (taoliug)\r\n* Fix spike log processing issue (Tao Liu)\r\n* Merge pull request #87 from google/dev (udinator)\r\n* Add vectored interrupt support (Tao Liu)\r\n* Merge pull request #85 from udinator/debug (udinator)\r\n* Add debug sub-programs, and extra options to generator (Udi)\r\n* Merge pull request #84 from imphil/fix-apache-urls (taoliug)\r\n* Fix license URLs in comments (Philipp Wagner)"}
+{"org": "lowRISC", "repo": "ibex", "number": 253, "state": "closed", "title": "Consolidate some debug generation options, and make the signature_add…", "body": "…r handshake optional"}
+{"org": "lowRISC", "repo": "ibex", "number": 252, "state": "closed", "title": "[RTL] - Add PMP module", "body": "- Instantiate generic PMP module\r\n- Wire up I-side and D-side PMP faults"}
+{"org": "lowRISC", "repo": "ibex", "number": 249, "state": "closed", "title": "`ram_1p.sv`: Fix `rvalid_o` generation", "body": "This signal must also be set in case of write transactions as it is a request valid and not a read valid."}
+{"org": "lowRISC", "repo": "ibex", "number": 248, "state": "closed", "title": "Remove unused signal data_reg_offset", "body": "This removes an unused which was hardwired to ```2'b0``` in the decoder and was passed through to the LSU.\r\nThis addresses https://github.com/lowRISC/ibex/issues/229"}
+{"org": "lowRISC", "repo": "ibex", "number": 247, "state": "closed", "title": "CI: Use Azure Pipelines to run lint and some DV", "body": "This sets up Azure Pipelines to run the following two tasks:\r\n\r\n- Run Verilator lint on the SystemVerilog code.\r\n- Run the RISC-V compliance test suite for RV32IMC"}
+{"org": "lowRISC", "repo": "ibex", "number": 246, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@7cce16c", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 7cce16c0a212c8713a82516fbf8f2570d3dc4505\r\n\r\n* Update spike log processing script to include full trace information\r\n (Tao Liu)\r\n* Add new tests (Tao Liu)\r\n* Add basic debug test functionality (Udi)\r\n* fix spelling error, fix output directory arg (Udi)\r\n* Add shorten option (dang hai)\r\n* Support SAIL-RISCV ISSi, update README (Tao Liu)\r\n* Fix CSR map copy issue (Tao Liu)"}
+{"org": "lowRISC", "repo": "ibex", "number": 244, "state": "closed", "title": "Rework CSR-related pipeline flushes", "body": "This commit clarifies why CSR-related pipeline flushes are needed (e.g. when enabling interrupts), only introduces them when doing the critical modifications (write/set bits in `mstatus` and `mie` CSRs\r\nfor enabling interrupts, reads and clears are uncritical for these CSRs), and makes sure the controller is actually able to start handling interrupts while doing a CSR-related pipeline flush.\r\n\r\nThis resolves lowrisc/ibex#6."}
+{"org": "lowRISC", "repo": "ibex", "number": 243, "state": "closed", "title": "Add basic debug test and modify sim flow", "body": "- Modified sim.py to correctly process any sim_opts and compare_opts passed specified in the testlist\r\n- Removed shared utility functions from sim.py (duplicates of functions in lib.py)\r\n- Changed location of vseq.stop() call in testbench to prevent debug or interrupt signal assertions after ecall has been detected\r\n\r\nReferences #205 "}
+{"org": "lowRISC", "repo": "ibex", "number": 242, "state": "closed", "title": "[DV] Enable unaligned load/store test", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 241, "state": "closed", "title": "Update google_riscv-dv to 63fa0ca", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 63fa0ca922ecf10f3cd733d15a0a79a7937a591e\r\n\r\n* Merge pull request #74 from google/dev (taoliug)\r\n* Add gcc compile options, fix unaligned load/store (Tao Liu)\r\n* Merge pull request #72 from google/dev (taoliug)\r\n* Properly disable branch instruction in push/pop stack operations\r\n (Tao Liu)"}
+{"org": "lowRISC", "repo": "ibex", "number": 240, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@07599f6", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 07599f689a385794cb73932922008bdbe8131d82\r\n\r\n* Fix introduced TypeError in run.py (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 239, "state": "closed", "title": "Mhartid illegal instruction exception", "body": "Hi,\r\nJust a quick question about the mhartid csr in the Ibex core. The RISC-V Privileged Spec says that mhartid should be a read-only CSR, and I noticed that Ibex will throw an illegal instruction exception if any write to mhartid is encountered. However, with the misa csr, which is hardwired to its reset value, Ibex will just ignore any writes to that address if it encounters any, instead of throwing any exceptions.\r\nAs a result, I was wondering if this difference in behavior was intended, since both CSRs are intended to be read-only?"}
+{"org": "lowRISC", "repo": "ibex", "number": 238, "state": "open", "title": "DV: Test performance counters", "body": "We have recently reworked the performance counters to be compliant to the RISC-V spec. The documentation is here: https://ibex-core.readthedocs.io/en/latest/performance_counters.html\r\n\r\nAre the performance counters already covered by existing DV? Otherwise this is the issue to track progress towards that :-)\r\n\r\n> estimate 4"}
+{"org": "lowRISC", "repo": "ibex", "number": 236, "state": "closed", "title": "Update to the license headers", "body": "These changes have been approved by Luca and Frank. Review is needed for style and other non-content topics."}
+{"org": "lowRISC", "repo": "ibex", "number": 234, "state": "closed", "title": "Update google_riscv-dv to google/riscv-dv@e905e9f", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision e905e9f134e0b7cf7da491218d1a30c75ce8649a\r\n\r\n* add pass_val and fail_val into csr test flow for EOT correctness\r\n checking (Udi)\r\n* Support unaligned load/store (Tao Liu)\r\n* refactored test generation logic (Udi)\r\n* refactored test generation logic (Udi)\r\n* Give error when mutually exclusive between -co, and -so argument\r\n (dang hai)\r\n* documentation, and small fixes (Udi)\r\n* no_iss bug (Udi)\r\n* no_iss/no_post_compare optional, CSR read_only is now only specified\r\n at field level granularity (Udi)\r\n* made no_iss optional (Udi)\r\n* rm print (Udi)\r\n* setup_logging call (Udi)\r\n* undo overriding --verbose in run.py, comment cleanup in csr gen\r\n script (Udi)\r\n* missed verbose arguments (Udi)\r\n* verbose arg (Udi)\r\n* updated csr description, integrated csr test into flow (Udi)\r\n* updated csr description, integrated csr test into flow (Udi)\r\n* Enhance verbose information by logging instead of using print (dang\r\n hai)\r\n* Report date time for output directory (dang hai)\r\n* Add main entry point for run.py (dang hai)\r\n* Separate command line parser by function (dang hai)\r\n* Skip generating S/U mode program for machine mode test (Tao Liu)\r\n* minor update to README.md (Tao Liu)\r\n* Update the README.md to match command reference from --help (Tao\r\n Liu)\r\n* Ignore untrack file from python script (dang hai)\r\n* Make questa work for new YAML based regression flow (dang hai)\r\n* Fix typo in README (Tao Liu)\r\n* Fix README google/riscv-dv#54 (Tao Liu)\r\n* changed formatting of generator option table (Udi)"}
+{"org": "lowRISC", "repo": "ibex", "number": 233, "state": "closed", "title": "Update ibex simulation flow", "body": "Integrated ibex simulation flow with `riscv-dv` privileged CSR test\r\n- Added options for CSR test generation script to `Makefile`\r\n- Added `csr_description.yaml`, containing YAML descriptions of all implemented CSRs, as per `docs/cs_registers.rst` for use in privileged CSR testing\r\n- Modified license of `testlist.yaml` to match standard Ibex licenses\r\n- Modified `sim.py` to deal with the optional `no_post_compare` license\r\n- Updated `ibex_log_to_trace_csv.py` to add functionality to parse UVM sim logs for the new report messages"}
+{"org": "lowRISC", "repo": "ibex", "number": 231, "state": "closed", "title": "Added CSR testing integration with simulation flow, and added general EOT uvm_report_server reporting", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 230, "state": "closed", "title": "Fix broken links in the verification doc", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 229, "state": "closed", "title": "Unused signal in decoder: data_reg_offset_o", "body": "Hi,\r\nI was looking through the ibex_decoder and found the signal ```data_reg_offset_o```, and I couldn't find anywhere where it is set apart from on the line\r\nhttps://github.com/lowRISC/ibex/blob/19ffe9ac1db96dcdfb18c5fe0b3b2cf382cc179b/rtl/ibex_decoder.sv#L193\r\nIs there a reason for this signal to exist?\r\n\r\nThanks,\r\nIvan"}
+{"org": "lowRISC", "repo": "ibex", "number": 228, "state": "closed", "title": "DV: Test writable mtvec", "body": "With #118 landed mtvec is now writable. We need DV to test this, and to ensure that the documented constraints (256B-aligned, only vectorized) are obeyed when reading the value back."}
+{"org": "lowRISC", "repo": "ibex", "number": 226, "state": "closed", "title": "Make BASE field of `mtvec` CSR writeable", "body": "This commit makes the BASE field of the `mtvec` CSR writable to\r\nallow changing the trap-vector base address at runtime without\r\nchanging the boot address input. Similar to the boot address,\r\nthe trap-vector base address must always be aligned to 256 bytes.\r\nAt bootup, the trap-vector base address is initialized to the boot\r\naddress.\r\n\r\nMost of this work has been done by @ivanmgribeiro.\r\nThis commit resolves lowrisc/ibex#118.\r\n\r\nThis supersedes PR #193 ."}
+{"org": "lowRISC", "repo": "ibex", "number": 225, "state": "closed", "title": "Fix linting warning", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 221, "state": "closed", "title": "Document register map of compliance test system", "body": null}
+{"org": "lowRISC", "repo": "ibex", "number": 220, "state": "closed", "title": "Make ibex_tracer Verilator-compatible", "body": "It should be possible to use a coding style for the tracer which works in Verilator, making this helpful tool available there as well."}
+{"org": "lowRISC", "repo": "ibex", "number": 219, "state": "open", "title": "Provide software using PMP", "body": "We need software (and possibly a modified simulation setup) to exercise PMPs in our tests. Needed to start development on #8."}
+{"org": "lowRISC", "repo": "ibex", "number": 218, "state": "open", "title": "Provide software exercising U-Mode", "body": "We need test software which exercises U mode to help with development of it in #88."}
+{"org": "lowRISC", "repo": "ibex", "number": 217, "state": "closed", "title": "enabling Tracer in verilator", "body": "@imphil referring to #99 \r\nGreat progress, I have managed to reproduce your results, and have all but 4 RV32I tests passing (as expected)\r\n\r\n**Q1. Is it possible to enable instruction tracing, register dumping, memory Load/Store from the simulation run ?**\r\n\r\nI will attempt to (manually) merge your code changes into my sandbox\r\nLooking at your changes, I see the following\r\n\r\nChanges to link.ld, my plan is to have a local linker script for ibex, and to have an additional section for the traphandlers, in order to define the correct memory region.\r\n\r\nIn RVTEST_CODE_BEGIN, I note you have removed the line\r\n\r\n> 110: .align 6\r\n\r\n**Q2. can you explain why this was removed ?**\r\n\r\nAlso I note you have commented out the code initialising the (non-existant) Supervisor registers.\r\nI had already handled this differently by indicating the the framework whether Supervisor or User modes were present, so I think I can fix this is a way that does not affect the other architectures\r\n\r\n**Q3. Finally, do you have a memory map of the RTL platform you have created ?**\r\nI will bear this in mind when creating the linker script.\r\n\r\nThx\r\nLee"}
+{"org": "lowRISC", "repo": "ibex", "number": 216, "state": "closed", "title": "instr_multicycle_done is not asserted, continuous register writes", "body": "While executing the code shown below:\r\n\r\nWe see this incorrect behavior in the core:\r\n\r\n\r\nAs shown, the `addi` instruction at PC `0x80000088` appears to correctly load register `x13` with the value `0xa5a5a5a5`, but at the very next instruction (PC: `0x8000008c`), we can see from the trace log that `x13` now has the value `0xa5a5de17`. \r\n\r\n\r\nFrom the waveform, `rf_reg[13]` is written correctly by the `addi` after adding the immediate value `0x5a5` (`alu_operand_b_i`), and becomes `0xa5a5a5a5`. After this, the testbench does not assert the `instr_gnt_i` for a number of cycles, leading the core to stay in the DECODE phase while waiting for the next instruction fetch. However, we see that `rf_reg[13]` keeps getting written with the incremented values of `alu_result` in every consecutive cycle that the core waits, as `instr_multicycle_done_q` in the ID stage does not go high after the `addi` finishes. This keeps `regfile_we` at 1, causing the continuous writes."}
+{"org": "lowRISC", "repo": "ibex", "number": 215, "state": "closed", "title": "Fix waveform/coverage dump mode", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 214, "state": "closed", "title": "RISC-V Compliance: Use unmodified upstream version", "body": "Currently, Ibex requires a modified version of riscv-compliance (living at https://github.com/imphil/riscv-compliance/tree/ibex), since the upstream version makes some assumptions which don't hold for our design, and which are not mandated by the spec (so we're conformant).\r\n\r\nThese issues need to be sorted our by the compliance working group. Once that has happened, we should switch the documentation in https://github.com/lowRISC/ibex/blob/master/dv/riscv_compliance/README.md to recommend using an unmodified upstream version of riscv-compliance.\r\n\r\nSee #99 and #209 for more discussion on the current implementation and status."}
+{"org": "lowRISC", "repo": "ibex", "number": 213, "state": "closed", "title": "prim_clock_gating.sv: Consolidate various in-tree example versions ", "body": "We currently have multiple versions of prim_clock_gating.sv in our tree, two pure verilog ones, and one Xilinx-specific one. Figure out where to place this IP so that it can be shared."}
+{"org": "lowRISC", "repo": "ibex", "number": 212, "state": "closed", "title": "UNOPTFLAT in ibex_core.cs_registers_i.mie_q", "body": "Investigate where this Verilator warning comes from, and decide if we want to fix it."}
+{"org": "lowRISC", "repo": "ibex", "number": 211, "state": "closed", "title": "UNOPTFLAT in ibex_core.id_stage_i.controller_i.ctrl_fsm_cs", "body": "Investigate where this loop comes from and if we can/should eliminate it."}
+{"org": "lowRISC", "repo": "ibex", "number": 210, "state": "closed", "title": "Fixed broken URL in readme.", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 209, "state": "closed", "title": "Provide simulation to run RISC-V Compliance test", "body": "This adds a Verilator simulation of Ibex for use in RISC-V Compliance\r\nTesting. In addition to ibex itself, the simulation contains a RAM and\r\na memory-mapped helper module for the test software to interact with the\r\noutside world. The test framework uses this to dump a \"test signature\",\r\nwhich is written to a certain part of the memory, and to end the\r\nsimulation. (In the future, this could be extended to include printf()\r\nlike functionality.)\r\n\r\nFixes https://github.com/lowRISC/ibex/issues/99\r\n\r\nNote that this requires changes to the compliance test suite itself, please see #99 for more discussion."}
+{"org": "lowRISC", "repo": "ibex", "number": 205, "state": "closed", "title": "Verify debug interface", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 203, "state": "closed", "title": "Update google_riscv-dv to a07e0a7", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision a07e0a726edf0230314c08d31546eecbed23054b\r\n\r\n* Merge pull request #53 from google/flow (taoliug)\r\n* Update README file for the new flow (Tao Liu)\r\n* Merge pull request #52 from google/flow (taoliug)\r\n* Add timeout mechanism to the flow (Tao Liu)\r\n* Merge pull request #51 from google/flow (taoliug)\r\n* Simulation flow update (Tao Liu)\r\n* Merge pull request #50 from udinator/master (taoliug)\r\n* added license for csr_template.yaml (Udi)\r\n* Merge pull request #49 from google/dev (taoliug)\r\n* Update log process script (Tao Liu)\r\n* Merge pull request #48 from google/dev (taoliug)\r\n* Fix illegal instruction issue (Tao Liu)\r\n* Merge pull request #47 from google/dev (taoliug)\r\n* Refactor the simulation flow (Tao Liu)\r\n* Merge pull request #45 from danghai/master (taoliug)\r\n* Add .gitignore to remove untracked files (danghai)\r\n* Fix warning from Questa optmize (danghai)\r\n* Add optimize log file for Questa simulator (danghai)\r\n* New YAML based simulation flow (Tao Liu)\r\n* Merge pull request #40 from scottj97/typos-redone (taoliug)\r\n* Fix typos in comments (Scott Johnson)\r\n* Fix typos/grammar in README (Scott Johnson)\r\n* Merge pull request #43 from udinator/master (taoliug)\r\n* use hex format in YAML description (Udi)\r\n* CSR test description (Udi)\r\n* removed run script (Udi)\r\n* Modified CSR test generation code to adhere to style guidelines.\r\n (Udi)\r\n* Merge pull request #41 from vandanaprabhu/questa (taoliug)\r\n* CSR Generation Script and YAML template (Udi)\r\n* Prevent Xcelium from attempting to run a simulation during the\r\n compile step (Scott Johnson)\r\n* Document support for Questa (Scott Johnson)\r\n* Fix simulation-time warnings from Mentor Questa (Scott Johnson)\r\n* Fix compile warnings from Mentor Questa (Scott Johnson)\r\n* Fix warning from Questa compiler (Scott Johnson)\r\n* Fix warning from Questa compiler (Scott Johnson)\r\n* Adding support for using the Questa simulator (Vandana Prabhu)\r\n* Pass proper seed to Cadence Xcelium simulator (Scott Johnson)\r\n* Convert compile commands to functions instead of variables (Scott\r\n Johnson)"}
+{"org": "lowRISC", "repo": "ibex", "number": 200, "state": "closed", "title": "Document specifications we aim to support", "body": "Fixes #124"}
+{"org": "lowRISC", "repo": "ibex", "number": 199, "state": "closed", "title": "interrupt detection", "body": "From the below waveform, our interrupt testbench model pulses interrupts for just one cycle. When ibex is in the SLEEP state and a nonmaskable interrupt is pulsed for one cycle (irq_nm_i), ibex immediately wakes up and jumps to FIRST_FETCH state and starts executing code as normal, but doesn't do any handling of the interrupt, even though it is non-maskable [RISC-V Privileged Spec, section 3.3.4]. Note that handle_irq is is only high for the duration of this interrupt, for one cycle.\r\n\r\n\r\n\r\nHowever, in the second waveform below, we have a software interrupt pulsed for one cycle directly after a non maskable interrupt, which is also pulsed just for one cycle. Because these interrupts are back to back, the handle_irq wire is high for two cycles, causing ibex to move to IRQ_TAKEN state, from which it jumps to interrupt handler code elsewhere in the program. However, since the irq_software signal was high while in the IRQ_TAKEN state, ibex only registers the software interrupt by setting exc_cause_o to EXC_CAUSE_IRQ_SOFTWARE_M, and thus appears to ignore that there was a non-maskable interrupt just one cycle before.\r\n\r\n\r\n\r\nAs a result, it would seem that we have to hold interrupts high for two or more cycles for ibex to properly detect and handle any interrupts. However ibex will wake up out of SLEEP state after detecting irq_nm_i pulsed for only one cycle, and will not handle this interrupt. Can you help clarify what is considered correct interrupt detection behavior in these situations?"}
+{"org": "lowRISC", "repo": "ibex", "number": 198, "state": "closed", "title": "No trap on misaligned jump", "body": "Ibex doesn't seem to be trapping when a jump or branch instruction tries to jump to a location that isn't 2-byte aligned (LSB is 1)."}
+{"org": "lowRISC", "repo": "ibex", "number": 197, "state": "closed", "title": "Ibex tracer - compressed instructions", "body": "Hi,\r\nWould it be possible to have the Ibex tracer indicate that an instruction is compressed, and if so, log the compressed instruction name? This would bring the log file closer in similarity to Spike log files, and would make debugging regression failures a bit easier to do.\r\nNot sure if this complies with RVFI spec though.\r\nThanks!\r\nUdi"}
+{"org": "lowRISC", "repo": "ibex", "number": 195, "state": "closed", "title": "Wrong encoding of EXC_CAUSE_ILLEGAL_INSN", "body": "This issue seems to be introduced in this commit\r\nhttps://github.com/lowRISC/ibex/commit/c2fffe04406287bc7e1be3962999f0f6b44ebe87#diff-ef03dc5b772f9745e0a161472ea79c60R190\r\n\r\nEXC_CAUSE_ILLEGAL_INSN should be 2 according to RISC-V privileged mode spec"}
+{"org": "lowRISC", "repo": "ibex", "number": 194, "state": "closed", "title": "src_files.yml: correct path of source files", "body": "This PR contains a single commit to update the path of source files in the `src_files.yml` file used in the PULP world."}
+{"org": "lowRISC", "repo": "ibex", "number": 193, "state": "closed", "title": "Change mtvec implementation and boot address", "body": "This PR aims to change the implementation of the mtvec CSR in order to allow it to be written to and read from by software.\r\nThis also allows for the boot address to be set to the input boot address instead of adding an offset to it, and it no longer needs to be 256-byte aligned"}
+{"org": "lowRISC", "repo": "ibex", "number": 191, "state": "closed", "title": "RVFI: re-add accidentally removed `rvfi_intr` signal", "body": "This PR re-adds the signal `rvfi_intr` part of the RVFI after it got accidentally removed in PR #188.\r\n\r\nThis signal is now set during the first instruction after the PC has been set to enter a trap handler."}
+{"org": "lowRISC", "repo": "ibex", "number": 189, "state": "closed", "title": "Update TB for the new interrupt interface", "body": "Update TB for the new interrupt interface, fix issue #187"}
+{"org": "lowRISC", "repo": "ibex", "number": 188, "state": "closed", "title": "Adapt interrupt interface for Arty example, tracer and TB", "body": "This PR also adapts the interrupt interface in the Arty example, the tracer and the tracer TB.\r\n\r\nA follow-up PR will contain the required changes for the UVM infrastructure.\r\n\r\nThis PR is related to #187 ."}
+{"org": "lowRISC", "repo": "ibex", "number": 187, "state": "closed", "title": "Tracer compile issue: irq_ack_o ", "body": "Looks like this port is removed recently, but still connected to the tracer.\r\n\r\n/usr/local/google/home/taliu/ibex_dbg/ibex/rtl/ibex_core.sv, 645\r\n Identifier 'irq_ack_o' has not been declared yet. If this error is not \r\n expected, please check if you have set `default_nettype to none.\r\n\r\nhttps://github.com/lowRISC/ibex/blob/master/rtl/ibex_core.sv#L645"}
+{"org": "lowRISC", "repo": "ibex", "number": 186, "state": "closed", "title": "Avoid linting errors", "body": "This PR contains a single commit removing a couple of linting errors in the decoder."}
+{"org": "lowRISC", "repo": "ibex", "number": 185, "state": "closed", "title": "Cleanup CSRs", "body": "This PR contains two cleanup commits affecting the CSRs:\r\n1. Remove define for `mstatus` CSR by bit index parameters in `ibex_pkg.sv`.\r\n2. Remove `csr_restore_dret_id_o` signal. This signal was used to restore the `mstatus` CSR when exiting debug mode. This is not needed as the `mstatus` CSR is not modified when entering debug mode.\r\n "}
+{"org": "lowRISC", "repo": "ibex", "number": 183, "state": "closed", "title": "Exceptions : load/store access fault", "body": "In the documentation:-\r\nibex can trigger an exception due to the following exception causes:\r\n- Load access fault\r\n- Store access fault\r\n\r\nCould you give an example of how either of these exceptions could be raised ?\r\n\r\nMy understanding is that these exceptions would be generated either from a Virtual Memory Fault, or a PMP Fault, neither of these units are present in ibex\r\n\r\nThx\r\nLee"}
+{"org": "lowRISC", "repo": "ibex", "number": 181, "state": "closed", "title": "Compile issue while running ibex_core_tracer example", "body": "Hi, \r\n\r\nI am running into compile issues while trying to run the `ibex_core_tracer` example using `fusesoc`. I guess the issue is in the way `timescale` value is specified on the command-line. \r\n\r\nUpdating the timescale option from `timescale=1ns/1ns` to `timescale 1ns/1ns` should fix it. "}
+{"org": "lowRISC", "repo": "ibex", "number": 180, "state": "closed", "title": "Update google_riscv-dv to 112dcc2", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 112dcc2e669f124dfe48c35a09477603c3ccb180\r\n\r\n* Merge pull request #39 from google/dev (taoliug)\r\n* CSR instruction update (Tao Liu)"}
+{"org": "lowRISC", "repo": "ibex", "number": 179, "state": "closed", "title": "[DV] Fix compile issue caused by design changes", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 177, "state": "closed", "title": "Rename cores for fusesoc, mainly tracer", "body": "Painful, but needed for symmetry and to reduce confusion: rename the cores in the fusesoc core files.\r\n\r\nThis PR requires RVFI to be defined globally if the ibex_core_tracing.sv is used to avoid potential design bugs caused by differing tool behavior. It's better to be explicit here.\r\n\r\nIf RVFI is not set and the ibex_core_tracing.sv file is used a compile error will be thrown as the file includes invalid syntax. I'm not yet sure that this is the right way to go, but it seems that there's no universally understood way to convince a Verilog parser to issue a compile-time fatal error."}
+{"org": "lowRISC", "repo": "ibex", "number": 176, "state": "closed", "title": "Decoder: remove reg-reg load, make LWU illegal", "body": "The custom reg-reg instruction was added in the original design but is\r\nno longer needed. This commit removes it. Also, load instructions with\r\n`instr[14:12] == 3'b110` are now decoded as illegal.\r\n\r\nThis resolves #25."}
+{"org": "lowRISC", "repo": "ibex", "number": 174, "state": "closed", "title": "Rename packages", "body": "Rename _defines.sv to _pkg.sv. Patch best viewed without whitespace changes."}
+{"org": "lowRISC", "repo": "ibex", "number": 173, "state": "closed", "title": "Rename ibex_tracer_defines to ibex_tracer_pkg", "body": "ibex_tracer_defines.sv is actually a package and doesn't contain defines (any more). Rename this file to reflect this reality."}
+{"org": "lowRISC", "repo": "ibex", "number": 172, "state": "closed", "title": "Decoder: avoid setting PC upon illegal JALR instructions", "body": "Without this commit, the PC is still set to a possible wrong jump target on illegal JALR instructions ultimately causing the wrong PC being saved to `mepc` during the illegal instruction exception.\r\n\r\nThis bug has been reported by @taoliug. This commit resolves #170."}
+{"org": "lowRISC", "repo": "ibex", "number": 171, "state": "closed", "title": "Remove unneeded tracer define", "body": "The tracer defines are not used by ibex on its own."}
+{"org": "lowRISC", "repo": "ibex", "number": 170, "state": "closed", "title": "MEPC is not updated with correct value for illegal JALR instruction", "body": "spike log\r\n\r\n```\r\ncore 0: 0xffffffff8000f720 (0x65d42c67) unknown\r\ncore 0: exception trap_illegal_instruction, epc 0xffffffff8000f720\r\ncore 0: tval 0x0000000000000000\r\ncore 0: 0x000000008001d000 (0x00007119) addi sp, sp, -128\r\n\r\n```\r\n0x65d42c67 is detected as illegal instruction by ibex correctly. However, seems like the core still executed the JALR instruction which causes the PC changed to some unexpected value(0x65a) and get saved to MEPC eventually.\r\n\r\nibex log:\r\n```\r\n 34443000 17123 8000f720 65d42c67 INVALID \r\n 34465000 17134 0000065a xxxxxxxx lui xx, 0xxxxxx000 \r\n```\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 169, "state": "closed", "title": "ID/EX stage: do not write to register file upon load errors", "body": "This commit fixes the write back FSM to not store values returned from\r\nmemory to the register file when the LSU is reporting a load error.\r\n\r\nThis bug was reported by @ivanmgribeiro. This commit resolves #162."}
+{"org": "lowRISC", "repo": "ibex", "number": 168, "state": "closed", "title": "Check behavior of exceptions and special instructions related to debug mode", "body": "Currently, exceptions and special instructions are handled independent of whether the core is in debug mode or not. This is not correct for a couple of cases. For example, the Debug Spec v0.13.2 states on p.39 that while in debug mode:\r\n- ~~WFI acts as a NOP. Currently the core just goes to sleep anyway.~~\r\n- Exceptions do not update any registers such as `mcause`, `mepc`, `mtval`, `dpc` and `mstatus`. Currently, exception handling does not depend on debug mode.\r\n\r\n~~Similarly, the DRET instruction must lead to an illegal instruction exception when the core is not in debug mode (p.41). Currently, DRET always restores the PC in dpc even if the core is not in debug mode, thus silently messing up the processor state.~~\r\n\r\n "}
+{"org": "lowRISC", "repo": "ibex", "number": 167, "state": "closed", "title": "Controller: save next PC to dpc CSR upon a halt request", "body": "This commit changes the controller to save the PC of the next\r\ninstruction to the dpc CSR when entering debug mode upon a halt\r\nrequest instead of the PC of the current instruction (only valid\r\nfor EBREAK instructions).\r\n\r\nThis bug was reported by @taoliug. This resolves #164."}
+{"org": "lowRISC", "repo": "ibex", "number": 166, "state": "closed", "title": "Decoder: fix signaling and detection of illegal instructions", "body": "This commit fixes two bugs in the decoder:\r\n\r\n1. For illegal branch condition selections, the illegal instruction\r\ncondition must be signaled as long as the instruction is being executed\r\nand not just during the first cycle, as the controller cannot interrupt\r\nmulticycle instructions.\r\n\r\n2. Illegal instructions should also be signaled when `instr[28]` is set\r\nfor register-register ALU operations. Previously, these were not\r\nsignaled as the original design used `instr[28]` to encode custom bit-\r\nmanipulation instructions.\r\n\r\nThese bugs were discovered by @taoliug. This resolves issue #163."}
+{"org": "lowRISC", "repo": "ibex", "number": 164, "state": "closed", "title": "Debug request causes the same instruction to be executed twice", "body": "In this test, debug_req is asserted while the core is executing instruction at PC 0x8000056a. dpc is saved to the current PC value rather than the next instruction. As a result, the instruction at 0x8000056a is executed again after exiting from debug mode(dret). \r\n\r\nibex log\r\n```\r\n 8487000 4145 8000056a 00cf9f93 slli x31, x31, 0xc x31=0x55508000 x31:0x9d655508\r\n 8595000 4199 80000040 3780e06f jal x0, 58232 \r\n 8639000 4221 8000e3b8 7b200073 dret \r\n 8683000 4243 8000056a 00cf9f93 slli x31, x31, 0xc x31=0x08000000 x31:0x55508000\r\n```\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 163, "state": "closed", "title": "7d10b363 is not decoded as illegal instruction", "body": "Based on the RISC-V instruction encoding, 7d10b363 doesn't map to any legal instruction. The trace log shows the instruction as INVALID. However, the id_stage doesn't assert the illegal_insn signal, and the core continues executing the instructions without jump to exception handling routine. Looks like the core can only detect illegal compressed instructions and illegal CSR instructions.\r\n\r\nSpike log\r\n\r\n```\r\ncore 0: 0xffffffff8000faaa (0x7d10b363) unknown\r\ncore 0: exception trap_illegal_instruction, epc 0xffffffff8000faaa\r\ncore 0: tval 0x0000000000000000\r\ncore 0: 0x000000008001d000 (0x00007119) addi sp, sp, -128\r\n```\r\n\r\nibex log\r\n```\r\n 22039000 10921 8000faa8 40b6d693 srai x13, x13, 0x40b x13=0x00000000 x13:0x00000000\r\n 22041000 10922 8000faaa 7d10b363 INVALID \r\n 22047000 10925 8000faae 001d0d13 addi x26, x26, 1 x26=0x5fab433a x26:0x5fab4339\r\n\r\n```"}
+{"org": "lowRISC", "repo": "ibex", "number": 162, "state": "closed", "title": "Load instructions that cause an error still write to registers", "body": "Hi,\r\nThere seems to be a bug in Ibex when performing a read from memory which returns an error.\r\n\r\nI would expect that when the memory slave sets data_err high, the core would not write the data that was read in into a register, but it appears to still be written to the register regardless.\r\n\r\nWhat i observe is that the data is still written into the register.\r\n\r\nI'm using the following instructions:\r\n```\r\naddi r2, r0, 1\r\nlw r2, r2[2]\r\naddi r3, r2, 1\r\n```\r\nWhen using the load word instruction, the register is overwritten with 0x0, but when using load halfword or load byte, it seems to actually read what is returned by memory and store it in the register.\r\n\r\nMy memory slave is configured such that accesses outside of the range 0x80000000 - 0x80007fff will set data_err high.\r\n\r\nI've performed a fix that seemed to work locally by changing the line\r\nhttps://github.com/lowRISC/ibex/blob/b7ef64b62da74afe52bb40165e17a7e87539d47a/rtl/ibex_id_stage.sv#L283\r\nto\r\n```\r\nassign regfile_we = (illegal_csr_insn_i || !instr_executing || lsu_load_err_i) ? 1'b0 :\r\n```\r\n\r\nThis fix seems to work with other failing loads as well, but I'm not sure that it conforms to your style guide or whether it should be done here or at some other point in the code."}
+{"org": "lowRISC", "repo": "ibex", "number": 161, "state": "closed", "title": "Remove linting errors for RVFI-related signals", "body": "`illegal_insn_id` and `id_out_valid` are only used if the RVFI is enabled. This PR removes linting errors happening when the RVFI is disabled."}
+{"org": "lowRISC", "repo": "ibex", "number": 160, "state": "closed", "title": "debug mode related TB updates", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 159, "state": "closed", "title": "Update google_riscv-dv to 2e5a401", "body": "Update code from upstream repository https://github.com/google/riscv-\r\ndv to revision 2e5a40145a367ac3b04f78fee02c5011022719fd\r\n\r\n* Merge pull request #36 from google/dev (taoliug)\r\n* Add basic debug mode support (Tao Liu)"}
+{"org": "lowRISC", "repo": "ibex", "number": 158, "state": "closed", "title": "[DV] fix debug_seq runtime options, update trace processing script", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 155, "state": "closed", "title": "Tracer based on RVFI", "body": "This PR changes how RVFI signals are generated (https://github.com/lowRISC/ibex/issues/151, fixes https://github.com/lowRISC/ibex/issues/147).\r\nIt also forwards the uncompressed instruction to the tracer (https://github.com/lowRISC/ibex/issues/154).\r\n\r\nAs those commits are all closely coupled I think it is easier to do it in one PR.\r\n@taoliug could you please test this before it is merged? "}
+{"org": "lowRISC", "repo": "ibex", "number": 154, "state": "closed", "title": "Tracer support for compressed instructions", "body": "The tracer reuses the RVFI signals. `rvfi_insn` holds the current instruction, but for the RISC-V formal verification this needs to be the instruction which is inserted into the core.\r\nFor compressed instructions the core will decode those to uncompressed instruction, which are then used internally.\r\n\r\nThe tracer currently prints `INVALID` for compressed instructions (https://github.com/lowRISC/ibex/issues/147#issuecomment-511083710) as it has no support for compressed instructions. \r\n\r\nFor the tracer we can either add an additional output signal with the uncompressed instruction or add support in the tracer for decoding compressed instructions.\r\n@imphil do you have an opinion here?"}
+{"org": "lowRISC", "repo": "ibex", "number": 153, "state": "closed", "title": "dpc is not updated properly if debug_req_i is a one cycle pulse", "body": "As you can see from below waveform, debug_req_i is modeled as a pulse interrupt which is only asserted for one cycle. ibex can enter debug mode and start fetching instructions from DmHaltAddr. However, dpc is not updated properly (keep at default value 0). I cannot find in the RISC-V debug spec that whether the halt request should be a level or pulse signal, can you help to clarify? \r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 151, "state": "closed", "title": "Rework RVFI to align with decoder", "body": "As reported in https://github.com/lowRISC/ibex/issues/147 the tracer, which is based on the RVFI signals is not working correct. This is because `rvfi_valid` signal depends on the state of the decoder (retired instruction). The current implementation looked for changes in the program counter in order to be only valid if the new program counter is actually used. With https://github.com/lowRISC/ibex/pull/150 it should now be possible to change this implementation so that a retired instruction can be marked as valid without waiting for the next instruction."}
+{"org": "lowRISC", "repo": "ibex", "number": 150, "state": "closed", "title": "Generate `instr_ret/compressed` inside ID stage", "body": "This commit moves the generation of these signals into the ID stage to generate it with more accurate timing. More precisely, an instruction is now considered as retired once it has been completely executed and not once the next instruction is pushed into the IF-ID pipeline register.\r\n\r\nAlso, it no longer depends on whether the instruction was valid or illegal. For RVFI and the tracer, also illegal instructions must be considered."}
+{"org": "lowRISC", "repo": "ibex", "number": 149, "state": "closed", "title": "Rework interrupts, add `mip` & `mie` CSRs, add non-maskable interrupt", "body": "This PR adds the `mip` and `mie` CSRs and adds three new interrupt input signals: external (connects to a PLIC), software interrupts (connects to a memory-mapped register) and timer (connects to a timer module). In addition, it removes the legacy internal interrupt controller and instead adds 15 fast interrupt lines connected to the `mip` CSR and controlled through the `mie` CSR. Together with a memory-mapped software interrupt register and timer module (both not part of Ibex), these changes allow to implement what others refer to as core-local interrupt block (CLINT).\r\n\r\nAlso, this PR adds one non-maskeable interrupt (NMI) and a three more CSRs to allow for nested interrupts and recoverable NMIs. This extension is not part of the RISCV standard. But might be added in the future: https://github.com/riscv/riscv-isa-manual/issues/261\r\n\r\nFinally, this PR also updates the documentation accordingly."}
+{"org": "lowRISC", "repo": "ibex", "number": 148, "state": "closed", "title": "[DV] Change TB to use ibex_core_tracer as DUT", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 147, "state": "closed", "title": "New tracer doesn't work as expected", "body": "I am running regression with new tracer with RVFI interface, seems to me the generated trace is not as expected. Looks like the logic used to generate rvfi_valid_int is one cycle off. The decoded instruction is not captured properly.\r\n\r\n\r\n\r\nRelated code:\r\nhttps://github.com/lowRISC/ibex/blob/master/rtl/ibex_core.sv#L667"}
+{"org": "lowRISC", "repo": "ibex", "number": 145, "state": "closed", "title": "Change return to exit in sim script (fixes #137)", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 144, "state": "closed", "title": "Enable data byte access for Arty example", "body": "The current Arty example only allows word access to the data memory.\r\nThis can be improved by allowing byte access.\r\nSee https://github.com/lowRISC/ibex/pull/78#discussion_r298485379 and https://github.com/lowRISC/ibex/pull/78/files#diff-7d58ac393f600bdb2679c4bd1143adb4R66 for the relevant points."}
+{"org": "lowRISC", "repo": "ibex", "number": 143, "state": "closed", "title": "[tlul] reduce sync fifo usage in blocks that do not require them", "body": "the current fabric path to memory does not really need outstanding capacity in the fifos, especially if memory accesses always complete in a single cycle.\r\n\r\nwe should update the sockets to reflect this.\r\n\r\n@eunchan, i'll assign this to both of us, and whoever manages to get to it first can just do it :)\r\nI imagine we both have a few things piled up anyways...\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 141, "state": "closed", "title": "Document DV flow", "body": "Document how to use the DV contained in this repository. The documentation should go into the `doc` folder."}
+{"org": "lowRISC", "repo": "ibex", "number": 140, "state": "closed", "title": "Simulation fail because of asm_file", "body": "In the sim bash script, it reads asm_test file,\r\nbut there is no such file\r\n\r\nCan someone help to get that file?\r\n\r\nI also tried to use iss_sim to generate the bin file, but still no success(("}
+{"org": "lowRISC", "repo": "ibex", "number": 139, "state": "closed", "title": "Update opcode enum", "body": "Rename fence and sort"}
+{"org": "lowRISC", "repo": "ibex", "number": 138, "state": "closed", "title": "Opcode name fence", "body": "While working on https://github.com/lowRISC/ibex/issues/134 I just saw that we now have \r\nhttps://github.com/lowRISC/ibex/blob/b203a0f7c70be7c7dbdbb8d6abb97671323e2023/rtl/ibex_defines.sv#L33\r\nas opposed to `OPCODE_MISC_MEM`. I understand that we only have `FENCE` and not `FENCE.I` so this is the only time the opcode is used. Just want to check if we want to keep `OPCODE_FENCE`?"}
+{"org": "lowRISC", "repo": "ibex", "number": 137, "state": "closed", "title": "iss_sim contains return statement, that should rename to exit", "body": "When running iss_sim, it gives this warning:\r\n\r\n./iss_sim: line 84: return: can only `return' from a function or sourced script\r\n\r\nAnd this is failing lines;\r\n *)\r\n echo \"unknown option $1\"\r\n return\r\n\r\nI think return should be replaced with exit"}
+{"org": "lowRISC", "repo": "ibex", "number": 136, "state": "closed", "title": "Illegal JALR instruction is executed unexpectedly", "body": "Here's the related instruction trace.\r\n\r\n97598000 48700 8000f7e0 34391c67 INVALID \r\n97638000 48720 00002dac f2051ae3 bne x10, x0, -204 x10:00001900\r\n\r\n0x34391c67 is decoded as illegal instruction correctly, as it's a JALR instruction with bit[14:12] != 0. However, looks like ibex doesn't jump to the boot address correctly to do the trap handling. Instead, the JALR instruction is executed and an instruction from 0x2adc is fetched unexpectedly. \r\n\r\nWaveform snapshot:\r\n\r\n\r\nplease let me know if more information is needed to debug this issue"}
+{"org": "lowRISC", "repo": "ibex", "number": 135, "state": "closed", "title": "Add #!/usr/bin/env bash for the sim script", "body": "Fix issue #133"}
+{"org": "lowRISC", "repo": "ibex", "number": 134, "state": "closed", "title": "FENCE instruction is shown as INVALID in the trace log", "body": "I think right now ibex is handling FENCE as NOP correctly, however, it's shown as INVALID in the trace log. This could be confusing when debug with the trace log\r\n\r\n 14678000 7240 80000cfe 0ff0000f INVALID \r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 133, "state": "closed", "title": "Add bin/bash in sim file", "body": "Please add #!/bin/bash in sim file, this will allow to run ./sim without makefile"}
+{"org": "lowRISC", "repo": "ibex", "number": 130, "state": "closed", "title": "Problem when the value of opcode FSM is OPCODE_JALR", "body": "Hello,\r\n\r\nWith the new file ibex_decoder.sv (5093e0a), when the opcode FSM = OPCODE_JALR, the pc_mux_o FSM stays at PC_BOOT value. Normally, the pc_mux_o FSM must toogle to PC_JUMP value.\r\nI created a zip file containing:\r\n ibex_28may19.log : result from the ibex_tracer module. No problem \r\n ibex_last_version.log : result from the ibex_tracer module : problem line 43 (jalr)\r\n waves_AES_CBC_old.wlf : waveform (modelsim) : pc_mux_o signal : PC_JUMP -> PC_BOOT -> PC_JUMP -> PC_BOOT \r\n waves_AES_CBC_new.wlf : waveform (modelsim) : problem (pc_mux_o : PCPC_JUMP -> PC_BOOT) \r\n ibex_new_jalr.png printscreen of waveform (version with _**problem)**_\r\n ibex_old_jalr.png printscreen of waveform (correct version)\r\n\r\nSolution : In ibex_decoder.sv, after the line 239, add the following line:\r\n **_jump_set_o = 1'b1;_**\r\n\r\nRemark: During compilation of ibex_decoder.sv file with modelsim, I obtain the following error:\r\n **_Error (suppressible): (vlog-12003) /cad/projects/eSecure/jlm4/design/digital/modules/esecure_cpu/macro/IP_ibex/sources/hdl/ibex_decoder.sv(623): Variable 'illegal_insn_o' written by continuous and procedural assignments. See /cad/projects/eSecure/jlm4/design/digital/modules/esecure_cpu/macro/IP_ibex/sources/hdl/ibex_decoder.sv(554)._** \r\n\r\nSolution : At line 553 : change the **_illegal_insn_o_** signal by **_illegal_insn_**.\r\n\r\nDespite the addition of the line **_jump_set_o = 1'b1;_** , my simulation still has errors.\r\nI'm debugging this new problem.\r\n\r\nBest regards,\r\n\r\nJean-Louis\r\n[problem_ibex_jalr.zip](https://github.com/lowRISC/ibex/files/3377638/problem_ibex_jalr.zip)\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 128, "state": "closed", "title": "Improve documentation for misa and mtvec CSRs", "body": "misa is WARL, but hard-wired. mtvec is WARL rather than read-only (but is also hard wired). The patches in this PR adjust the documentation to reflect this."}
+{"org": "lowRISC", "repo": "ibex", "number": 124, "state": "closed", "title": "User/Priv spec", "body": "I see that the current code conforms to PRIV 1.11, But I cannot find anywhere which indicates the USER level, I would presume 2.3, but I guess it could be 2.2. In which case where should I look I cannot find it in the docs\r\nThx\r\nLee"}
+{"org": "lowRISC", "repo": "ibex", "number": 123, "state": "closed", "title": "misa register", "body": "Looking at the documentation here\r\nhttps://ibex-core.readthedocs.io/en/latest/cs_registers.html\r\n\r\nI cannot see a description of the MISA register regarding the enabling/disabling of MISA[C]\r\nAssuming I have a core configured as RV32IMC\r\nin lowRISC, is it possible to disable compressed instructions at runtime by setting MISA[C]=0\r\n\r\nThx\r\nLee\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 122, "state": "closed", "title": "Fix LSU + lint errors", "body": "I prepared this PR to get urgent stuff fixed before the bigger changes for the controller and interrupts/exceptions.\r\n\r\nThis PR contains two commits:\r\n- The first one is a cleanup of the LSU that also fixes a critical error. Previously, misaligned loads/stores were broken as the byte enable generation and read data alignment for the second transaction part were not working. These operations rely on the updated input address having the same alignment as the original address, whereas the LSU provided the aligned output address to the AGU.\r\n- The second one fixes recently introduced linting errors.\r\n\r\nTested using Verilator and Vivado."}
+{"org": "lowRISC", "repo": "ibex", "number": 121, "state": "closed", "title": "Addr && be not stable during read req", "body": "I'm seeing data_addr_o and data_be_o change, while data_req_o is high, and data_gnt_i has not been received.\r\nIs it possible I'm misreading the spec? (or that there are illegal things I might have in the environment which could cause this?)\r\nThank you.\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 120, "state": "closed", "title": "Cleanup ID stage and decoder", "body": "This PR contains a major cleanup of the ID stage and the decoder. Control logic (e.g. for stalls) that depends not on the decoder exclusively, is moved out of the decoder. Similarly, logic inside the ID stage that is strictly related to instruction decoding (immediate & register file address generation and checking) is moved into the decoder. \r\n\r\nAs a result, the ID stage now instantiates the modules of the controller, decoder and registers, and contains the the main muxes, the write-back (WB) FSM to handle multicycle instructions and minimal glue logic, only.\r\nThis will ease future work on any of these parts. \r\n\r\nFinally, the WB FSM inside the ID stage is cleaned up to remove circular dependencies between FSM and decoder. This resolves #103 ."}
+{"org": "lowRISC", "repo": "ibex", "number": 118, "state": "closed", "title": "Writable mtvec", "body": "`mtvec` is currently read-only and hardwired to the boot address. We need it writable."}
+{"org": "lowRISC", "repo": "ibex", "number": 117, "state": "closed", "title": "Support for Intel/Altera Quartus Lite/Standard (not Pro)", "body": "for (genvar ..) generate_statement() is not supported in Quartus\r\n\r\nit likes \r\n\r\ngenerate\r\ngenvar g;\r\nfor(g ...) generate_statement() \r\nendgenerate\r\n\r\nThe suggestion is made to add ifdef QUARTUS around the four places that you do this"}
+{"org": "lowRISC", "repo": "ibex", "number": 112, "state": "closed", "title": "ibex compilation issue: is_compressed_i ", "body": "I am getting this error while compiling ibex with VCS, PTAL. Looks like the port is renamed.\r\n\r\nError-[XMRE] Cross-module reference resolution error\r\n/usr/local/google/home/taliu/ibex/ibex/rtl/ibex_core.sv, 766\r\n Error found while trying to resolve cross-module reference.\r\n token 'is_compressed_i'. Originating module 'ibex_core'.\r\n Source info: .compressed_i (id_stage_i.is_compressed_i)\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 109, "state": "closed", "title": "Add error response to instruction interface", "body": "Unlike the data interface, the instruction interface does not have an error response to signal errors on the instruction interface to the core and raise an exception. This feature should be added and the core should raise an instruction access fault (Exception ID 1)."}
+{"org": "lowRISC", "repo": "ibex", "number": 108, "state": "closed", "title": "Interrupt context saving not working", "body": "\r\nThe problem is not systematic.\r\nThe problem is detected by comparing the files generated by the tracer.sv module, for the zero_riscy and the Ibex.\r\nA small modification (around the is_decoding_o signal)of ibex_controller.sv module permits to avoid the problem (but this modification is not safe to 100 %; The problem must be present in Debug mode : not tested).\r\nlist of file:\r\nzero_riscy_VS_ibex_problem.log : comparaison, line by line of trace_core.log (generated by trace.sv)\r\nmodifications_ibex_controller.log : modification that improves the behavior of Ibex during an interruption\r\nibex_writing_during_an_interruption.png : waveforms to show the problem\r\nzero_riscy_writing_during_an_interruption.pgn : waveforms of zero_riscy (no problem)\r\n[zero_riscy_VS_ibex_problem.log](https://github.com/lowRISC/ibex/files/3320582/zero_riscy_VS_ibex_problem.log)\r\n[modifications_ibex_controller.log](https://github.com/lowRISC/ibex/files/3320584/modifications_ibex_controller.log)\r\n\r\n\r\n\r\n \r\n\r\n\r\n\r\n[modifications_ibex_controller.log](https://github.com/lowRISC/ibex/files/3344870/modifications_ibex_controller.log)\r\n[zero_riscy_VS_ibex_problem.log](https://github.com/lowRISC/ibex/files/3344871/zero_riscy_VS_ibex_problem.log)\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 105, "state": "closed", "title": "Instructions accessing x16-x31 should be considered illegal for RV32E", "body": "The specification doesn't require that all unused instruction encodings generate illegal instruction traps. However, we prefer to do so for Ibex as this increases the chances of catching errors early and provides some forward-compatibility for trap+emulate of future standard or non-standard extensions.\r\n\r\nRight now, an illegal instruction exception won't be signalled on an RV32E system for instructions accessing x16-x31. There is some relevant commented out logic in ibex_id_stage.sv: https://github.com/lowRISC/ibex/blob/90796e3800207c67f5f0349b2216ef8bdf623ab2/rtl/ibex_id_stage.sv#L274-L278 Logic may also be needed in ibex_compressed_decoder.sv for the CI and CSS formats (ultimately, after #104 we need to ensure the mcause holds the compressed version of the instruction)."}
+{"org": "lowRISC", "repo": "ibex", "number": 104, "state": "closed", "title": "Spec compliant trap handling", "body": "This PR mainly modifies the trap handling infrastructure to comply with the RISC-V privileged spec, draft versions 1.11. To this end, additional CSRs were added.\r\n\r\nAll exceptions now jump to the base address of the trap-vector table. Interrupts are handled in vectored mode and jump to the base address + 4*irq_id. The exception cause is stored in `mcause` and `mtval` has been added to hold additional information (illegal instruction for illegal instruction exception, address of faulting transaction part for LSU errors).\r\n\r\nTo implement these changes the AGU mux for misaligned loads/stores has been reworked.\r\nIn addition, the `mscratch` CSR has been implemented.\r\n\r\nThis PR resolves: #97 and #70.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 103, "state": "closed", "title": "Diagnose/remove combinatorial loop", "body": "Verilator reports this loop:\r\n\r\n```\r\n%Warning-UNOPTFLAT: ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_core.sv:129: Signal unoptimizable: Feedback to clock or circular logic: ibex_core.is_decoding\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_core.sv:129: Example path: ibex_core.is_decoding\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_controller.sv:527: Example path: ASSIGNW\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_id_stage.sv:158: Example path: ibex_core.id_stage_i.deassert_we\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_decoder.sv:550: Example path: ASSIGNW\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_id_stage.sv:174: Example path: ibex_core.id_stage_i.jump_in_id\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_id_stage.sv:602: Example path: ALWAYS\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_id_stage.sv:172: Example path: ibex_core.id_stage_i.jump_set\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_controller.sv:151: Example path: ALWAYS\r\n ../src/lowrisc_ibex_ibex_0.1/rtl/ibex_core.sv:129: Example path: ibex_core.is_decoding\r\n```\r\n\r\nWe need to diagnose this loop in more detail, and hopefully remove it. Otherwise add an explanation and a lint waiver.\r\n\r\n(My gut feeling is that we need to apply deassert_we later to signals that need it.)"}
+{"org": "lowRISC", "repo": "ibex", "number": 102, "state": "closed", "title": "Setup Verilator lint and waivers", "body": "Setup Verilator lint and waivers\r\n\r\nThis adds Verilator lint support to our fusesoc core file. A waiver file\r\nis created to waive all well-understood lint warnings. The UNOPTFLAT\r\nwarnings are not well understood at the moment, they are waived for now\r\nand further discussion is expected to happen in a GH issue (referenced\r\nin the waiver).\r\n\r\nRun with\r\n\r\n```\r\nfusesoc --cores-root . run --target=lint lowrisc:ibex:ibex_core\r\n```\r\n\r\nThe waiver file support requires edalize >= 0.1.5."}
+{"org": "lowRISC", "repo": "ibex", "number": 99, "state": "closed", "title": "Run RISC-V Compliance tests through Verilator", "body": "Provide a Verilator model of Ibex to serve as target for the RISC-V compliance test suite, and add required tooling and documentation for it. (https://github.com/riscv/riscv-compliance/tree/master/doc#the-target-environment) \r\n\r\nInspiration can be taken from RI5CY (https://github.com/pulp-platform/riscv/tree/master/tb/core)."}
+{"org": "lowRISC", "repo": "ibex", "number": 97, "state": "closed", "title": "Implement the mscratch CSR", "body": "The title says it all."}
+{"org": "lowRISC", "repo": "ibex", "number": 95, "state": "closed", "title": "Clarify usage and requirements of register file versions", "body": "This PR aim at avoiding future confusion and wrong selection of register file implementations (latch- or flip-flop-based) as for example documented in #75 . It does so by\r\n\r\n- renaming the register file `ibex_register_file.sv` to `ibex_register_file_latch.sv`\r\n- clarifying the application scenarios and requirement of the two register files in source code and documentation\r\n- preventing the simulation of the latch-based register file using Verilator\r\n- adapting the clock gating primitive provided as part of the DV infrastructure to be compatible with the latch-based register file\r\n\r\nThis resolves #93."}
+{"org": "lowRISC", "repo": "ibex", "number": 93, "state": "closed", "title": "Clock gate for latch-based register file ", "body": "The clock gate currently provided in `dv/uvm/tb/prim_clock_gating.sv` is not compatible with the latch-based register file. Usage of this clock gate leads to wrong behavior in simulation as reported in #75. \r\n\r\nFor commercial, event-based simulators a clock-gate using a latch for the enable signal can be used. For Verilator, a different workaround is needed.\r\n\r\nAlso, the requirements on the clock gate must be documented accordingly.\r\n\r\nMoreover, we should rename the two register files to `register_file_ff.sv` and `register_file_latch.sv` to avoid people accidentally taking the wrong register file and running into the same problem again.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 92, "state": "closed", "title": "Expand word widths to keep Verilator lint checks happy", "body": "Verilator bombs out by default unless all the widths match (and -Wno-width is not specified). This patch expands widths where necessary to overcome this problem. However it may not be the most elegant solution.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 91, "state": "closed", "title": "We need to document working versions of CAD tools", "body": "The Google UVM framework requires either VCS or incisive.\r\nI have found that vcs-mx/N-2017.12-SP1 works but that vcs-2016.06-sp1 does not.\r\n\r\nWe should record these experiences in some sort of compatibility table.\r\n\r\nThe failing version crashes out, with a fatal error.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 90, "state": "closed", "title": "Implement sleep with wfi instruction", "body": "We currently implement the WFI instruction as NOP. This implementation is correct, but we should think about putting the core to sleep instead to save power."}
+{"org": "lowRISC", "repo": "ibex", "number": 89, "state": "closed", "title": "[tracking] Implement bit manipulation (B) RISC-V ISA extension", "body": "The bit manipulation (bitmanip) extension is currently being specified. Bit manipulation is a common task in many scenarios where Ibex could be used.\r\n\r\nThe bitmanip extension adds many new instructions to Ibex, not all of them have a straightforward implementation. Please have a look at the implementation plan and the implementation tracking sheet for an overview \r\n\r\n* [Draft standard](https://github.com/riscv/riscv-bitmanip/blob/master/bitmanip-draft.pdf)\r\n* [Implementation plan](https://docs.google.com/document/d/1HS6tLeCac1MJPdrhnzD1k7PBBLxwb66W2R26moWZmok/edit)\r\n* [Implementation tracking sheet](https://docs.google.com/spreadsheets/d/1XzAnCXw4GVD8dAEqZTnDEFYrvZ7v0_8zb27CVaWIfvQ/edit)\r\n\r\n**All implementations of individual instructions are tracked in separate issues.**\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 88, "state": "closed", "title": "Add support for User (U) mode", "body": "Currently, Ibex is M-mode only. For some usage scenarios, support for U mode would be beneficial.\r\n\r\nSubtasks:\r\n- Evaluate the implementation effort for this change. As a starting point, we can look at RI5CY (https://github.com/pulp-platform/riscv) \r\n- Check overhead of this extension.\r\n- Decide on configurability: should this feature be always-on, or configurable via a parameter? (Depends much on the area overhead.)\r\n- Ensure that we have DV for this.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 87, "state": "open", "title": "Test trap precision", "body": "Add DV to ensure that traps are as precise as we expect them to be. This requires the expectations to be documented first in #86."}
+{"org": "lowRISC", "repo": "ibex", "number": 85, "state": "closed", "title": "Disable performance counters by default", "body": "Performance counters are an optional feature. Disable them by default to\navoid users having them enabled unknowingly and paying the (rather\nlarge) area price for it."}
+{"org": "lowRISC", "repo": "ibex", "number": 84, "state": "closed", "title": "Make sure CSR set/clear/write op only change the CSR during one cycle", "body": "Without this change, the core can continue to write CSRs for multiple clock cycles when being stalled. This can corrupt CSR (e.g. performance counters)."}
+{"org": "lowRISC", "repo": "ibex", "number": 80, "state": "closed", "title": "Number of performance counters", "body": "the parameter MHPMCounterNum does not seem to influence the number of performance counters. I synthesized the core once with MHPMCounterNum=1 and then with MHPMCounterNum=8 and it results in almost exactly the same area.\r\n\r\nby looking at the code I also don't see how this parameter is changing the number of physically present counters/flipflops. I'm pretty sure there are 32 64b registers and 32 64b adders no matter what the parameters are.\r\n\r\nI think MHPMCounterWidth has the same problem. it probably only counts to the desired width, but the registers [63:MHPMCounteWidth] cannot be optimized away.\r\n\r\nthe problem with the width can be easily fixed by changing:\r\n```\r\ncsr_rdata_int = mhpmcounter_q[mhpmcounter_idx][63:32];\r\n```\r\nto\r\n```\r\ncsr_rdata_int[MHPMCounterWidth-1:0] = mhpmcounter_q[mhpmcounter_idx][MHPMCounterWidth-1:32];\r\ncsr_rdata_int[32-1:MHPMCounterWidth-32] = '0;\r\n```\r\n\r\nif mhpmcounter_q[63:MHPMCounterWidth] is never accessed, the synthesizer can optimize it away. otherwise these registers are there but cannot really be used."}
+{"org": "lowRISC", "repo": "ibex", "number": 75, "state": "closed", "title": "Unaligned instruction fetch and data addresses", "body": "Hi, \r\nI've got an issue while trying to execute a code compiled by *riscv64-unknown-elf-gcc-8.2.0-2019.02.0-x86_64-linux-centos6* (from https://www.sifive.com/boards/) on the *ibex* core.\r\n\r\nListing:\r\n> 25e:\t028b2783 \tlw\ta5,40(s6)\r\n\r\nMessage:\r\n> 316725ns: Illegal instruction (core 0) at PC 0x0000025e: 0x028b028b\r\n\r\nCould you please suggest what might be wrong here.\r\nThanks.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 74, "state": "closed", "title": "Fix linting errors", "body": "This PR fixes 3 linting errors.\r\n\r\nBoth Verilator and Vivado builds successfully tested."}
+{"org": "lowRISC", "repo": "ibex", "number": 72, "state": "closed", "title": "Reference integration for FPGA", "body": "Goal: Provide a minimal, but fully working example of how to use Ibex on a well-known FPGA board.\r\n\r\nTarget board: One of the well-known Xilinx 7-series boards, Nexys or Arty*.\r\n\r\nThis will require:\r\n- A toplevel\r\n- Additional hardware blocks\r\n - A RAM\r\n - A prim_clock_gating implementation\r\n - A trivial GPIO IP would be nice which maps some bus reads/writes to LEDs/Switches.\r\n- A board-dependent constraints file (xdc)\r\n- Build system support (a fusesoc core file)\r\n- Documentation and code to run a minimal hello world (including linker file, crt)\r\n\r\nI'm not sure about where to put these things into the repository, I'd most likely go for a top-level directory like `examples/fpga/nexyvideo` and `examples/sw/hello_world`."}
+{"org": "lowRISC", "repo": "ibex", "number": 70, "state": "closed", "title": "Implement trap handling according to latest RISC-V spec", "body": "Hi guys (@vogelpi , @imphil )\r\n\r\naccording to the Priv ISA Spec of RISC-V 1.10, you should handle the exceptions by always jumping to mtvec rather than vectoring them as it was in the past\r\n\r\nLook at the section\r\n3.1.12 Machine Trap-Vector Base-Address Register (mtvec)\r\nof this document please: https://riscv.org/specifications/privileged-isa/\r\n\r\nI have already done it in RISCY.\r\nSo now in the controller everytime you get an exception you set exc_pc_mux_o to exceptions:\r\nhttps://github.com/pulp-platform/riscv/blob/master/rtl/riscv_controller.sv#L731\r\n\r\nand in the IF stage you always jump to the same address regardless the exception cause:\r\nhttps://github.com/pulp-platform/riscv/blob/master/rtl/riscv_if_stage.sv#L141\r\n\r\n\r\n\r\n\r\n\r\n\r\n\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 64, "state": "open", "title": "Evaluate the feasibility of parameterising ibex by XLEN", "body": "It could be interesting to support RV64I as well as RV32I (imagine small helper cores, with access to the same address space as a larger 64-bit application cores). Before leaping into doing this, someone needs to do the ground work to see how disruptive it might be, so we can evaluate the potential maintenance / readability costs vs the benefits of supporting an RV64I configuration."}
+{"org": "lowRISC", "repo": "ibex", "number": 62, "state": "closed", "title": "Switch ibex_tracer to use RVFI", "body": "Currently ibex_tracer is instantiated within the ibex_core.sv file depending on a define. It would be cleaner if we do the following:\r\n\r\n- Modify ibex_tracer.sv take the RVFI signals as input. Requires #61 to be merged first.\r\n- Remove the instantiation of ibex_tracer from ibex_core.sv\r\n- Show people how to instantiate ibex_core and ibex_tracer in their top-level design; either in documentation, or by creating ibex_core_tracing.sv which instantiates ibex_core and ibex_tracer and passes through all signals except for the tracing ones."}
+{"org": "lowRISC", "repo": "ibex", "number": 54, "state": "closed", "title": "Fix decoding of C.LI, C.LUI, C.SRLI, C.SRAI, C.SSLI", "body": "Hints encoded in these compressed instructions must decode into hints\r\nin the corresponding base instructions. This resolves #51."}
+{"org": "lowRISC", "repo": "ibex", "number": 53, "state": "closed", "title": "Perf counters & CSRs", "body": "This PR brings several changes related to CSRs and performance counters that bring the CSRs closer to the specs. The most important changes are:\r\n\r\n- Fixes to the clear operation and and documentation: resolves #16 , #15 \r\n- Replace legacy/custom performance counters by standard compliant ones, resolves #27 \r\n- Add access checks for CSR operations and cause illegal instruction exceptions on violations\r\n- Modify illegal clear and set CSR ops to be read-only as mandated by the specs \r\n- Update outdated documentation on CSRs and performance counters\r\n\r\nThe changes have been successfully tested using Verilator and Xilinx Vivado."}
+{"org": "lowRISC", "repo": "ibex", "number": 52, "state": "closed", "title": "Add riscv-dv vendor in script and patches", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 51, "state": "closed", "title": "HINT instruction decoding issue - 0x7065", "body": "Based on the spec, it should be decoded as HINT instruction (C.LUI, rd == 0), but it's decoded as illegal instruction by design incorrectly.\r\nhttps://github.com/lowRISC/ibex/blob/master/rtl/ibex_compressed_decoder.sv#L105\r\n\r\n```\r\n 3'b011: begin\r\n // c.lui -> lui rd, imm\r\n instr_o = {{15 {instr_i[12]}}, instr_i[6:2], instr_i[11:7], {OPCODE_LUI}};\r\n\r\n if (instr_i[11:7] == 5'h02) begin\r\n // c.addi16sp -> addi x2, x2, nzimm\r\n instr_o = {{3 {instr_i[12]}}, instr_i[4:3], instr_i[5], instr_i[2],\r\n instr_i[6], 4'b0, 5'h02, 3'b000, 5'h02, {OPCODE_OPIMM}};\r\n end else if (instr_i[11:7] == 5'b0) begin // this is INCORRECT\r\n illegal_instr_o = 1'b1;\r\n end\r\n\r\n if ({instr_i[12], instr_i[6:2]} == 6'b0) illegal_instr_o = 1'b1;\r\n end\r\n```\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 50, "state": "closed", "title": "Fix non-unique case bug in tracer.", "body": "The `nop` instruction ( `32'h00_00_00_13` ) cannot be distinguished from masked `addi` ( `17'b?, 3'b000, 5'b?, 7'h13` ) in `unique casex` statement. The other way around is not a problem, as `addi` cannot have both registers as 0x0. \r\nThis can be also fixed by replacing `unique casex` with `priority casex`. However, in my opinion, it is not a good solution as it may hide future bugs like this."}
+{"org": "lowRISC", "repo": "ibex", "number": 49, "state": "closed", "title": "Code cleanup", "body": "This PR implements three main changes:\r\n- Enforce line wrapping after 100 characters. This is required by our style guide and avoids lint warnings.\r\n- Simplify default assignments of `'X` and `'0` to enum types.\r\n- Make state signal names for the prefetch buffer FSM lowercase.\r\n\r\nSuccessfully tested in Verilator and Vivado. "}
+{"org": "lowRISC", "repo": "ibex", "number": 48, "state": "closed", "title": "Compressed hints", "body": "Fix handling of HINTs in compressed instructions. \r\n\r\nFixes #46 (and a bit more)\r\n\r\n\r\n@taoliug can you re-test with these modifications?\r\n@asb does my reading of the spec sound about right?"}
+{"org": "lowRISC", "repo": "ibex", "number": 47, "state": "closed", "title": "Code cleanup", "body": "This PR contains:\r\n- a cosmetic fix to the documentation (exceptions were not ordered correctly)\r\n- fixes to the tracer (switch from unsigned to logic for instruction mask parameters, replace non-unique `case` by `unique case` + `default`)\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 46, "state": "closed", "title": "Decode HINT as NOP", "body": "The core fetched an compressed instruction like below.\r\n\r\nFrom a downstream bug report:\r\n\r\ncore 0: 0xffffffff8000f2ec (0x00009056) add zero, zero, s5\r\n\r\n0x9056 is correctly decoded as HINT instruction by spike, but ibex decode it as illegal C.EBREAK instruction:\r\n\r\nhttps://github.com/lowRISC/stwg-base/blob/master/hw/vendor/lowrisc_ibex/rtl/ibex_compressed_decoder.sv#L215\r\n\r\n```\r\n if (instr_i[11:7] == 5'b0) begin\r\n // c.ebreak -> ebreak\r\n instr_o = {32'h00_10_00_73};\r\n if (instr_i[6:2] != 5'b0) illegal_instr_o = 1'b1;\r\n```\r\n\r\nThis code first checks if instr[11:7] is zero to determine if it's c.ebreak instruction, then check instr[6:2] to see if it's illegal. However, when instr[6:2] == 0 and instr_i[11:7] != 0, it should be treated as HINT instruction rather than illegal instruction."}
+{"org": "lowRISC", "repo": "ibex", "number": 45, "state": "closed", "title": "Code cleanup", "body": "This PR implements a couple of changes (to list the most important ones):\r\n- Add capability to detect and react on load/store errors\r\n- Add missing `default` in `unique case`, progagate `'X' in FSM states\r\n- Replace non-unique `case` constructs by `unique case` -> resolves #43 \r\n- Remove unnessary `{}` to avoid linting errors\r\n- Update doc to add `data_err_i` and LSU exceptions -> resolves #44 \r\n\r\nThe changes are tested in simulation using Verilator. The FPGA bitstream build is completing without errors."}
+{"org": "lowRISC", "repo": "ibex", "number": 44, "state": "closed", "title": "Missing description of input signal from documentation.", "body": "Hi,\r\nDescription of input \"data_err_i\" of the data memory interface is missing from documentation. This signal is currently used only for an assertion. Since it is a top level input, I believe it would be better for the user to read about it in the documentation instead of figuring it out from the RTL.\r\n\r\nBest,\r\nIoannis"}
+{"org": "lowRISC", "repo": "ibex", "number": 43, "state": "closed", "title": "Replace non-unique `case` constructs by `unique case`", "body": " There are still many non-unique `case` constructs in the ibex code base that should be replaced by `unique case` constructs with a proper `default` as required by our coding guidelines.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 41, "state": "closed", "title": "Switch back to upstream Sphinx package", "body": "Once a Sphinx release with sphinx-doc/sphinx#6364 is out we need to switch back to it, we're currently using a fork to fix a bug.\r\n\r\nhttps://github.com/lowRISC/ibex/blob/62185d054ef937d5ceb74c85797245f481016fb3/doc/requirements.txt#L2"}
+{"org": "lowRISC", "repo": "ibex", "number": 40, "state": "closed", "title": "Fix synthesis ikarageo", "body": "Replaces #38 as the other one seemed to be messed up by GitHub"}
+{"org": "lowRISC", "repo": "ibex", "number": 39, "state": "closed", "title": "Code cleanup", "body": "This PR contains a couple of fixes related to linting errors. First of all, the width of literals later cast to enums is specified. Second, before doing a part select, signed signals are converted to unsigned signals. Also, this PR clarifies that some MSBs in the ALU and the multiplier can safely be ignored (some linting tools also produce errors because of these MSBs being ignored).\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 38, "state": "closed", "title": "Fix unsynthesizable construct and missing signal for tracer", "body": "- Synthesis tools throw warnings with system task $stop. \r\n- Functionality of tracer broke after commit 53f2fb935030eee131e4d927f6890295f86344ac"}
+{"org": "lowRISC", "repo": "ibex", "number": 37, "state": "closed", "title": "Temporarily switch to custom sphinx", "body": "Using figures in admonitions did not work so far. A patch was created\r\nand merge is pending. As long as it is not merged, use custom sphinx.\r\n\r\nFixes #24"}
+{"org": "lowRISC", "repo": "ibex", "number": 36, "state": "closed", "title": "Fix wavedrom versions", "body": "Ensure to pickup the correct versions for wavedrom."}
+{"org": "lowRISC", "repo": "ibex", "number": 35, "state": "closed", "title": "Fix missing enum casts", "body": "This PR fixes to remaining issues related to the recent introduction of enum types for previously hard-coded parameters:\r\n\r\n1. Before assigning literals to enum types, Vivado expects an explicit type cast and otherwise throws an error. (#33)\r\n2. There were instances of `csr_op` signals in `id_stage` which still were using the previous logic types leading to illegal signal assignments (#34).\r\n\r\nThe changes have been tested using Verilator and Vivado (synthesis and implementation ran through without issues)."}
+{"org": "lowRISC", "repo": "ibex", "number": 34, "state": "closed", "title": "Illegal assignment of logic variable to enum type port", "body": "Hi there,\r\nThe following illegal assignment is found:\r\nhttps://github.com/lowRISC/ibex/blob/93b0b77f2717a69f87608929f7cde9d5268ca2e8/rtl/ibex_core.sv#L482\r\n\r\nChanging the csr_op to enum type should be combined with a change in csr_op_ex as well as the relevant signals in \"ibex_id_stage.sv\".\r\n\r\nBest,\r\nIoannis"}
+{"org": "lowRISC", "repo": "ibex", "number": 33, "state": "closed", "title": "Enum assignment cast", "body": "In the following lines the enum types are assigned with a value without an explicit cast\r\nhttps://github.com/lowRISC/ibex/blob/93b0b77f2717a69f87608929f7cde9d5268ca2e8/rtl/ibex_controller.sv#L159\r\n\r\nhttps://github.com/lowRISC/ibex/blob/93b0b77f2717a69f87608929f7cde9d5268ca2e8/rtl/ibex_controller.sv#L162"}
+{"org": "lowRISC", "repo": "ibex", "number": 32, "state": "closed", "title": "Code cleanup", "body": "This pull request aligns the coding style of ibex to our guidelines: all I/Os use _i/_o suffices, configurable parameters use UpperCamelCase, and the types of all parameters are specified.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 31, "state": "closed", "title": "Code cleanup, addresses #150 in stwg-base", "body": "This pull request addresses most of the points discussed in #150 in stwg-base and should fix most of the linting errors in ibex. Remaining linting errors related to the load/store unit and bus exceptions will be addressed separately.\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 30, "state": "closed", "title": "Cleanup: Remove REG_* defines from ibex_id_stage", "body": "Can we get rid of those defines and replace them by parameters or structs?"}
+{"org": "lowRISC", "repo": "ibex", "number": 29, "state": "closed", "title": "Replace core_id and cluster_id parameters in favour of a single hartid parameter", "body": "Ibex should allow system integrators to directly specify the hartid using whatever scheme makes most sense for their design. Currently core_id and cluster_id must be specified - this makes sense for the PULP use case, but will require some gymnastics for users who have a different hartid generation scheme.\r\n\r\n[EDIT: \"gymnastics\" is hyperbolic given they're just concatenated - but you get my point. An integrator may also want a hartid that is greater than 10 bits in length]"}
+{"org": "lowRISC", "repo": "ibex", "number": 28, "state": "closed", "title": "Code cleanup", "body": "Some more cleanup"}
+{"org": "lowRISC", "repo": "ibex", "number": 27, "state": "closed", "title": "Standard-compliant performance counters", "body": "We need to look into performance counters and see how we can implement them in a standard-compliant way (or ensure that we document where we have good reasons to deviate).\r\n\r\nWhile at it, check #17, #16 and #15 to see if they are valid and fix/close as needed."}
+{"org": "lowRISC", "repo": "ibex", "number": 26, "state": "closed", "title": "Some more ibex cleanup", "body": "Switch from parameters to enums where possible, and remove unused ones."}
+{"org": "lowRISC", "repo": "ibex", "number": 25, "state": "closed", "title": "Remove reg-reg loads", "body": "reg-reg load (i.e., offset taken from a register and not from an immediate) should not be part of the Ibex ISA.\r\n\r\nThe code at line 261 here:\r\nhttps://github.com/lowRISC/ibex/blob/master/rtl/ibex_decoder.sv\r\n\r\nis a piece of code coming from RISCY and it should be removed."}
+{"org": "lowRISC", "repo": "ibex", "number": 24, "state": "closed", "title": "Fix PDF documentation build", "body": "```cmd\r\n$ LANG=C make latexpdf\r\nRunning Sphinx v2.0.1\r\nbuilding [mo]: targets for 0 po files that are out of date\r\nbuilding [latex]: all documents\r\nupdating environment: 12 added, 0 changed, 0 removed\r\nreading sources... [100%] register_file \r\nlooking for now-outdated files... none found\r\npickling environment... done\r\nchecking consistency... done\r\nprocessing ibex.tex... index introduction integration instruction_fetch load_store_unit register_file cs_registers interrupts performance_counters exception_interrupts debug copyright \r\nresolving references...\r\ndone\r\nwriting... failed\r\n\r\nException occurred:\r\n File \"/home/philipp/src/ibex/doc/venv/lib64/python3.7/site-packages/cairosvg/parser.py\", line 414, in __init__\r\n 'No tag with id=\"{}\" found.'.format(element_id))\r\nTypeError: No tag with id=\"vvv-2-2\" found.\r\nThe full traceback has been saved in /tmp/sphinx-err-u9zes32v.log, if you want to report the issue to the developers.\r\nPlease also report this if it was a user error, so that a better error message can be provided next time.\r\nA bug report can be filed in the tracker at . Thanks!\r\nmake: *** [Makefile:20: latexpdf] Error 1\r\n```\r\n\r\n\r\nThe SVG image in question actually is generated through wavedrom, as this part of the stacktrace shows:\r\n\r\n```\r\n File \"/home/philipp/src/ibex/doc/venv/lib64/python3.7/site-packages/sphinxcontrib/wavedrom.py\", line 187, in visit_wavedrom\r\n imgname = render_wavedrom(self, node, outpath, bname, format)\r\n File \"/home/philipp/src/ibex/doc/venv/lib64/python3.7/site-packages/sphinxcontrib/wavedrom.py\", line 162, in render_wavedrom\r\n cairosvg.svg2pdf(svgout.tostring(), write_to=fpath)\r\n```\r\n\r\nThe SVG (which is then converted to PDF and causes the error) contains a couple of tags with `xlink:href=\"#vvv-2-2\"` statements, but no tag with the `id=\"vvv-2-2\"` attribute. So the error message of cairosvg is correct, and something is wrong in the generation of the wavedrom SVG (for reference: the same problem happens with `vvv-2`, but `vvv-3` is handled correctly in the SVG)\r\n\r\nThe following wavedrom source code is trying to be rendered. It's in [doc/instruction_fetch.rst](https://github.com/lowRISC/ibex/blob/master/doc/instruction_fetch.rst):\r\n\r\n```\r\n{\"signal\":\r\n [\r\n {\"name\": \"clk\", \"wave\": \"p......\"},\r\n {\"name\": \"data_addr_o\", \"wave\": \"x===xxx\", \"data\": [\"Address\", \"Address\", \"Address\"]},\r\n {\"name\": \"data_req_o\", \"wave\": \"01..0..\"},\r\n {\"name\": \"data_gnt_i\", \"wave\": \"0..10..\"},\r\n {\"name\": \"data_rvalid_i\", \"wave\": \"0....10\"},\r\n {\"name\": \"data_rdata_i\", \"wave\": \"xxxxx=x\", \"data\": [\"RData\"]}\r\n ],\r\n \"config\": { \"hscale\": 2 }\r\n}\r\n```\r\n\r\nSo we have:\r\n\r\n1. A bug: wavedrom should not generate invalid SVG.\r\n2. More to investigate: is the wavedrom source actually wrong, or is the conversion wrong?\r\n3. More error reporting would be helpful, getting the file which causes the error required adding print statements across the sources."}
+{"org": "lowRISC", "repo": "ibex", "number": 23, "state": "closed", "title": "Add documentation link to the README.md", "body": ""}
+{"org": "lowRISC", "repo": "ibex", "number": 20, "state": "closed", "title": "Prefetcher busy_o", "body": "Two asserts that check that busy_o in the prefetch_buffer can change its state are failing. The assert that checks that once busy_o is low it can go high in future is failing in two clock cycles; this one I'm more inclined to say it can be a setup issue, as I'm still not fully familiar with the design; the interfaces are not fully specified either so difficult to say. However, the assert that says once you're busy you should become not busy eventually is also failing at 6 clock cycles suggesting it is possible to put the prefetcher in the busy state forever. "}
+{"org": "lowRISC", "repo": "ibex", "number": 16, "state": "closed", "title": "Bit clear operation (`csrrc` and `csrrci` ops) wrong for performance counter registers", "body": "Looking at RTL, clear operations are implemented bad. Applies to all CSRs related to performance counters (PCMR, PCER, PCCRx).\r\n\r\nBelow is the sample code for PCMR, but the same pattern applies to the other CSRs. Rather than inverting the register value, do invert the mask (i.e. `csr_wdata_i`).\r\n\r\nhttps://github.com/pulp-platform/zero-riscy/blob/b1b89f55fb1dbbf6f35ac5f92c5c1d12b2f41d45/zeroriscy_cs_registers.sv#L431"}
+{"org": "lowRISC", "repo": "ibex", "number": 15, "state": "closed", "title": "PCMR bits swapped in documentation", "body": "Looking at the RTL code, the function of Global Enable and Saturation is swapped in the documentation. Saturation is really controlled by bit 1 and enable by bit 0.\r\n\r\nPlease indicate which one is correct. RTL or doc?\r\n\r\nhttps://github.com/pulp-platform/zero-riscy/blob/c6eeb34f57ff1cec354a74e025b889c26138146b/doc/performance_counters.rst#L16-L26\r\n\r\nhttps://github.com/pulp-platform/zero-riscy/blob/b1b89f55fb1dbbf6f35ac5f92c5c1d12b2f41d45/zeroriscy_cs_registers.sv#L401-L406\r\n"}
+{"org": "lowRISC", "repo": "ibex", "number": 11, "state": "closed", "title": "Doc: Inline documentation of waveforms", "body": "So far I used wavedrom for rendering, but that required external\r\ntooling. After patching the extension, sphinx can now render inline\r\nwaveforms!"}
+{"org": "lowRISC", "repo": "ibex", "number": 6, "state": "closed", "title": "why mstatus accessed by CSR instruction will flush prefetch fifo", "body": " Please refer the line 306 in “zeroriscy_controller.sv”, what purpose is for the csr_status_i (mstatus accessed by CSR instruction) will enter the FLUSH state?\r\n\r\n else if (~branch_set_i & ~jump_set_i & (mret_insn_i | ecall_insn_i | pipe_flush_i | ebrk_insn_i | illegal_insn_i | csr_status_i))\r\n begin\r\n ctrl_fsm_ns = FLUSH;\r\n halt_if_o = 1'b1;\r\n halt_id_o = 1'b1;\r\n end"}