
instruction stringlengths 15 30k |
|---|
The question is actually about _Simplified_ DES (rather than _Simple_ DES as stated), which is an extremely simplified mock-up of [_Single_ DES][1].
From reading the definition of S-DES in the [reference][2] used in the question, we get that:
>The S-boxes operate as follows. The first and fourth input bits are trea... |
Skein uses an additional compression function call to finalize the output, even when the output isn't larger than the native output size.
The Skein paper says:
> Due to Skein’s output transformation, it remains an open problem how to create collisions or second preimages for the Skein hash function, even if one c... |
Why does Skein use an output transform, but other similar hashes don't? |
According to [the original paper][1], Lamport one-time signature scheme uses two one-way functions: $F$ and $G$. The former one, $F$, is used to create a public key by hashing elements of the private key (and also for hashing signature elements when verifying it); the latter, $G$, is used to hash a message when signing... |
According to [the original paper][1], Lamport one-time signature scheme uses two one-way functions: $F$ and $G$. The former one, $F$, is used to create a public key by hashing elements of the private key (and also for hashing signature elements when verifying it); the latter, $G$, is used to hash a message when signing... |
According to [the original paper][1], Lamport one-time signature scheme uses two one-way functions: $F$ and $G$. The former one, $F$, is used to create a public key by hashing elements of the private key (and also for hashing signature elements when verifying it); the latter, $G$, is used to hash a message when signing... |
SHA-1 processes data by 512-bit blocks (64 bytes). For a given input message _m_, it first appends some bits (at least 65, at most 576) so that the total length is a multiple of 512. Let's call _p_ the added bits (that's the _padding_). The padding bits depend only on the _length_ of _m_ (these bits include an encoding... |
I have been trying to understand exactly how a length extension attack works on SHA1. I'll detail below what I've understood so far, so that I can convey my understanding of the same and hopefully get advice on where I'm going wrong.
Lets assume that for a message "m", a secret "s" is appended to it and the SHA1 has... |
The question is actually about _Simplified_ DES (rather than _Simple_ DES as stated), which is an extremely simplified mock-up of [_Single_ DES][1].
From reading the definition of S-DES in the [reference][2] used in the question, we get that:
>The S-boxes operate as follows. The first and fourth input bits are trea... |
Call your original ($k$-to-$3k$ bit) PRG $G$ and your construction $G'$.
Let $\mathcal{U}_t$ denote the uniform distribution on $\{0,1\}^t$. Then $G'$ is a PRG as long as the distributions $\mathcal{U}_{3k}$ and $G'(\mathcal{U}_{2k})$ are indistinguishable with effort polynomial in $k$; see [this reference][1].
D... |
With Steganography, we take a short message, and embed that into a much larger signal, with the goal being that someone seeing the larger signal cannot tell that there's the embedded message. Now, this larger signal (which might be JPEG, a handwritten message, or in your case, interpacket delays) has a natural distrib... |
With Steganography, we take a short message, and embed that into a much larger signal, with the goal being that someone seeing the larger signal cannot tell that there's the embedded message. Now, this larger signal (which might be JPEG, a handwritten message, or in your case, interpacket delays) has a natural distrib... |
Assume Alice and Bob communicate over an insecure channel using one-time perfectly-secret encryption together with one-time secure message authentication code. Say Eve has the ability to eavesdrop and to inject messages into this insecure channel, but not to block or delay messages (i.e. Eve can mostly only replay auth... |
Assume Alice and Bob communicate over an insecure channel using one-time perfectly-secret encryption together with one-time secure message authentication code. Say Eve has the ability to eavesdrop and to inject messages into this insecure channel, but not to block or delay messages (i.e. Eve can mostly only replay auth... |
I need to encrypt relatively short strings (generally less than 100 characters). If possible, I want to avoid leaking the length of these strings. How can I do that?
The thing that came to my mind is to pad the text to 1 KiB with random data, separating the content from the padding with a 0x00 byte. Is this a good i... |
I'm doing some exercises before my exam, and I stuck with the task number 4. from this file: www.cs.umd.edu/~jkatz/crypto/f10/hw1.pdf . Could you help me with this?
When using the one-time pad encryption scheme, it can occur that $k=0^l$ and then the ciphertext is equal to the plaintext! It has been suggested to imp... |
Suppose I have an algorithm that relies on multiple iterations of a hash function like SHA1 to slow down an attacker trying to bruteforce a hash.
digest[0] = hash(password + salt)
for i in 1..r:
digest[i] = hash(digest[i-1] + password)
The final `digest[r]` is then used as the hash. How does t... |
Is it possible to parallelize a hashing function to crack an iteratively hashed password? |
In few words:
1. OTP has perfect secrecy;
2. For a cipher to have perfect secrecy, it is required that $|K|=|M|$.
Let $K=M=C=\{0,1\}^n$ be the set of keys, messages and ciphertexts. If you apply the "improvement", ie, if you remove $0^n$ from the keyspace, then you've created a cipher that cannot show perfect ... |
If two parties want to communicate with securely using OTP , how is the key ( that is lengthy as plain text) shared with other party for decryption ?
|
All the know problems have been solved and currently there is, at least, one practical and secure Mental Poker protocol.
Check:
METHOD AND APPARATUS FOR EFFICIENT AND SECURE CREATING, TRANSFERRING, AND REVEALING OF MESSAGES OVER A NETWORK
Application number: 13/086,208
Publication number: US 2011/0202766 A1
... |
All the know problems have been solved and currently there is, at least, one practical and secure Mental Poker protocol.
Check this patent application:
* [METHOD AND APPARATUS FOR EFFICIENT AND SECURE CREATING, TRANSFERRING, AND REVEALING OF MESSAGES OVER A NETWORK][1]
* Application number: 13/086,208
* Public... |
How is it possible to parallelize a hashing function to crack an iteratively hashed password? |
In few words:
1. OTP has perfect secrecy;
2. For a cipher to have perfect secrecy, it is required that $|K|=|M|$.
Let $K=M=C=\{0,1\}^n$ be the set of keys, messages and ciphertexts. If you apply the "improvement", ie, if you remove $0^n$ from the keyspace, then you've created a cipher that cannot show perfect ... |
In my notes, there are 2 definitions of perfect security:
Enc(M; K) = E = E1,E2...Em where Ei = Xi ⊕ Ki
Dec(E; K) = E1 ⊕ K1, E2 ⊕ K2,..., Em ⊕ Km
See here (sorry it would not let me post images since I am new): http://i45.tinypic.com/29nxyqo.png
I have two questions:
1. Could someone clarify the definition... |
The question to answer is "Is N the product of P*Q?" I believe that the easiest way to understand Shor is to imagine two sine waves, one length P and one length Q. Assuming that P and Q are co-prime, then the question above can also be answered "At what point does the harmony of P overlapped with Q repeat itself?" And ... |
I came across this little HRNG widget and was really intrigued as I have been looking for a decent but afordable source for truly random bits to use in a one-time pad.
<www.entropykey.co.uk>[Link to HRNG thingy][1]
[1]: http://www.entropykey.co.uk/ "Link to HRNG thingy"
The question is, would a HRNG like t... |
> If M0, and M1 are any 2 m-bit messages, how is it possible that their encryption be equal b?
The definition does not say that their encryption is equal *b*. It says that the function *f* outputs *b*. This function is often called *distinguisher* (or attacker) and he should not be able to distinguish which message ... |
In few words:
1. OTP has perfect secrecy;
2. For a cipher to have perfect secrecy, it is required that $|K| \ge|M|$.
Let $K=M=C=\{0,1\}^n$ be the set of keys, messages and ciphertexts. If you apply the "improvement", ie, if you remove $0^n$ from the keyspace, then you've created a cipher that cannot show perfe... |
In my notes, there are 2 definitions of perfect security:
$\mathrm{Enc} \left ( M, K \right ) = E = E_1, E_2 \dots E_m ~ $ where $~ E_i = X_i \oplus K_i$
$\mathrm{Dec} \left ( E, K \right ) = E_1 \oplus K_1, E_2 \oplus K_2, \dots, E_m \oplus K_m$
See here (sorry it would not let me post images since I am new):... |
What's the main differemce betweem Pohlig-Hellman and RSA? |
Why is QKD usually associated with OTP ?
QKD is about key distribution, where as OTP is about using key as long as message to get perfect secrecy, can any one explain how they are related ?
|
What's the main difference between Pohlig-Hellman and RSA? |
All the know problems have been solved and currently there is, at least, one practical and secure Mental Poker protocol.
Check this patent application:
* [METHOD AND APPARATUS FOR EFFICIENT AND SECURE CREATING, TRANSFERRING, AND REVEALING OF MESSAGES OVER A NETWORK][1]
* Application number: 13/086,208
* Public... |
In my notes, there are 2 definitions of perfect security:
![enter image description here][1]
$\mathrm{Enc} \left ( M, K \right ) = E = E_1, E_2 \dots E_m ~ $ where $~ E_i = X_i \oplus K_i$
$\mathrm{Dec} \left ( E, K \right ) = E_1 \oplus K_1, E_2 \oplus K_2, \dots, E_m \oplus K_m$
I have two questions:
... |
I came across [this little HRNG widget][1] and was really intrigued as I have been looking for a decent but afordable source for truly random bits to use in a one-time pad.
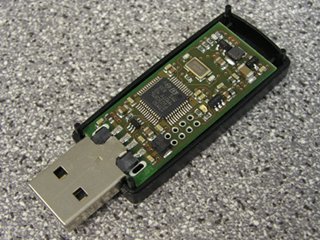
[1]: http://www.entropykey.co.uk/ "Link to HRNG thingy"
The questio... |
In my notes, there are 2 definitions of perfect security:
> 1. "For $M \in \{0,1\}^m$, define the distribution $D_M$ on strings as follows: to choose a random member of $D_M$, choose a random $K \in \{0,1\}^n$ and output $Enc(M,K)$. Then $Enc,Dec$ is _perfectly secure_ if $D_M$ is exactly the same for every $M$. T... |
Both Pohlig-Hellman and RSA perform encryption and decryption by exponentiation modulo some integer ($p$ prime for PH, $n$ composite for RSA). They both use a key $e$ as the exponent to encrypt a message. They both use the inverse element of key $e$ to decrypt. In both, the encryption key $e$ can be a randomly chosen i... |
Why AES based encryption is not recommended for encrypting images with high redundancy in their content? for example, the encryption of an image which shows a bird in the blue sky. Most of the pixels are blue in that case. |
What do you mean "AES is not recommended for highly-redundant images"?
Perhaps you're referring to "ECB mode is not recommended for highly-redundant images" (and yes, AES can be used for ECB mode).
Yes, AES in ECB mode is not recommended for highly-redundant images, because it doesn't disguise when two 128 bit pl... |
I have this situation, where, in a game, people send messages to each other (game moves etc...) These messages need to be encrypted, and should only be readable by the destination person. I am using RSA for this, but, recently I got a doubt. Is it possible that, if the message is one of n possible messages, can somebod... |
Suppose tha i want to verify the correctness of the following equation:
$q_1(s)*P_1(s)+q_2(s)*P_2(s)+\ldots+q_n(s)*P_n(s) = 1$ where each $P_i(s)=\prod_{x \in S}{(x+s)}$ for some secret s that the proover which is the extended euclidean algorithm. The prover wants to compute these $q_i(s)$ and he sends me back $g^{q_i... |
How can i use bilinear maps to verify the correctness of extended euclidean algorithm? |
Suppose tha i want to verify the correctness of the following equation:
$q_1(s)*P_1(s)+q_2(s)*P_2(s)+\ldots+q_n(s)*P_n(s) = 1$ where each $P_i(s)=\prod_{x \in S}{(x+s)}$ for some secret s that the proover which is the extended euclidean algorithm. The prover wants to compute these $q_i(s)$ and he sends me back $g^{q_i... |
sufficient randomness
---------------------
[The Whirlygig RNG][1] --
and some other similar [low-cost hardware random number generators][2] --
have published schematics.
Yes, such a hardware random-number generator
gives more than sufficient randomness to produce one-time pads.
It seems quite possible that ... |
sufficient randomness
---------------------
[The Whirlygig RNG][1] --
and some other similar low-cost hardware random number generators [a][2] [b][3] --
have published schematics.
Yes, such a hardware random-number generator
gives more than sufficient randomness to produce one-time pads.
It seems quite possi... |
One way to share a OTP key is to separately send several different independently-generated OTP keys, each one in its own [tamper-evident package][1] (often more than one layer).
When Bob receives the package, if the seal shows the package hasn't been opened in transit, then therefore no one has opened the package an... |
I found responses provided by [Stephen Harris][1] and [PBKDF2 Answers](http://crypto.stackexchange.com/a/3498/2693) very useful. I just wanted to add my two cents on authenticated encryption and verification of the ciphertext without actually decrypting it.
In [PBKDF2 Answers' response][2] computing HMAC prior to ... |
If Alice encrypts two messages *a* and *b*, such that *x*=E(*a*), *y*=E(*b*). Can Alice prove (without revealing *a*, *b* or the private key) that *a* = *b*?
Obviously the proof must not be too long and it should be practical to compute and verify (either interactively or non-interactively).
This is possible for ... |
Is there a public key semantically secure cryptosystem for which one can prove in zero knowledge the equivalence of two plaintexts? |
If your motivation is to rely on a DPA protected implementation of a block cipher, why don't you use one of the many hash function constructions based on a block cipher (think of Davies-Meyer for instance)?
Then, from an efficiency point of view, your proposal is going to be at least $n$ times slower than any other ... |
If Alice encrypts two messages *a* and *b*, such that *x*=E(*a*), *y*=E(*b*). Can Alice prove (without revealing *a*, *b* or the private key) that *a* = *b*?
Obviously the proof must not be too long and it should be practical to compute and verify (either interactively or non-interactively).
This is possible for ... |
If Alice encrypts two messages $a$ and $b$, such that $x=E(a)$, $y=E(b)$. Can Alice prove (without revealing $a$, $b$ or the private key) that $a = b$?
Obviously the proof must not be too long and it should be practical to compute and verify (either interactively or non-interactively).
This is possible for the Po... |
It seems to me that anything that was sufficiently good as a KDF would work just fine as a password hash, though the reverse might not be true. Are there considerations specific to password-hashing that don't apply to KDFs? |
What's the difference between a Key Derivation Function and a Password-Hash? |
It seems to me that anything that was sufficiently good as a KDF would work just fine as a password hash, though the reverse might not be true. Are there considerations specific to password-hashing that don't apply to KDFs?
To clarify: This is about key-stretching KDFs. Not the kind for diversifying keys (eg. HKDF... |
I'm doing some exercises before my exam, and I am stuck with task number 4 in this file: http://www.cs.umd.edu/~jkatz/crypto/f10/hw1.pdf
Could you help me with this task?
> When using the one-time pad encryption scheme, it can occur that $k=0^l$ and then the ciphertext is equal to the plaintext! It has been sugge... |
If your motivation is to rely on a DPA protected implementation of a block cipher, why don't you use one of the many hash function constructions based on a block cipher (think of Davies-Meyer for instance)?
Then, from an efficiency point of view, your proposal is going to be at least $n$ times slower than any other ... |
If your motivation is to rely on a DPA protected implementation of a block cipher, why don't you use one of the many hash function constructions based on a block cipher (think of Davies-Meyer for instance with say Rijndael at 256-bit plaintext)?
Alternatively, the issue of using small input size compression function ... |
I've been reading [Introduction to Modern Cryptography][1] by Katz and Lindell as an introduction to cryptography. The book seems to use the term 'simulator' when it talks about a game like, for instance, how it defines CPA-security as an interaction between an algorithm and a simulator.
Having looked at some crypto... |
I hope somebody can help me understand the design criterias for AES. Therefore, I would be really thankful if somebody could explain "non-linearity" in this context.
A criteria for the s-box in AES is non-linearity, where the maximum input-output correlation amplitude must be as small as possible. Why is a look-up t... |
I need to implement an AES encryption for firmware distribution system.
I have a bootloader that can decrypt various AES variants (ECB,CBC,CTR).
When I approached this I found few issues that aren't clear to me.
1. First, there's the IV vector, which is strange to me.
This vector has to be known to the encrypto... |
for example if the entropy of a password is 30 bits, then what is the entropy of the password when you hash it with MD5?
Thanks! :) |
What happens to the entropy of a password when you hash it? |
If Alice encrypts two messages $a$ and $b$, such that $x=E(a)$, $y=E(b)$. Can Alice prove (without revealing $a$, $b$ or the private key) that $a = b$?
Obviously the proof must not be too long and it should be practical to compute and verify (either interactively or non-interactively).
This is possible for the Po... |
Still 30 bits.
A hash function does not add entropy. It could change the entropy rate though. For example if you had 30 bits of entropy in a 64 bit password and hashed it to a 128 bit digest, the rate has gone down ($\frac{30}{64}\approx 0.47$, but $\frac{30}{128}\approx 0.23$). On the other hand, if the password is... |
For example, if the entropy of a password is 30 bits, what is the entropy of the password when you hash it with MD5? |
I'm reading [a paper][1] about finding collisions for the MD5 hash algorithm involving the concept of [tunnels][2].
But I couldn't understand about the difference between point of verification and point of choice. Aren't they the same?
[1]: http://www.di.ens.fr/~leurent/files/APOP_FSE07.pdf "a paper"
[2]: ... |
This wording is creeping everywhere ([e.g. there][1]): "I encrypt with the private key" and even sometimes, "I decrypt with the public key." Does it make any sense?
[1]: http://crypto.stackexchange.com/questions/4020 |
How do I encrypt with the private key? |
Asymmetric encryption and signing are entirely distinct concepts. The security and construction requirements are completly different. (Encryption for instance, needs to be an injection, whereas signatures need to be surjections. As a further hint of how they are intrinsically different, note that it lasted quite a bit ... |
Asymmetric encryption and signing are entirely distinct concepts. The security and construction requirements are completly different. (Encryption for instance, needs to be an injection, whereas signatures need to be surjections. As a further hint of how they are intrinsically different, note that it lasted quite a bit ... |
Title says all; Is it safe to hold key file's hash (MD5 or SHA1) in application (hard-coded)?
Thanks |
I have the following password in this fixed order, which starts with a fixed value of 111, followed by 2 random lower case letters and then lastly a random digit.
"111""2 Random lowercase letters""random digit"
**Is my below calculation correct?**
fixed value 111 -> log2(1) = 0 bits
2 random lowercase lette... |
I have the following password with a prescribed format: it starts with a fixed value of 111, followed by 2 random lower case letters and then lastly a random digit:
"111""2 Random lowercase letters""random digit"
**Is my below calculation correct?**
fixed value 111 -> log2(1) = 0 bits
2 random lowercase let... |
Let's say I have a message, a Private Key and a Public Key
Normally if you want to see if the message is *unaltered* and is *from the sender* you would have the message part + signed part, which you can verify using the senders Public key.
This will lead to some extra data, which I want to work around
[ messa... |
Let's say I have a message, a Private Key and a Public Key.
Normally if you want to see if the message is *unaltered* and is *from the sender* you would have the message part + signature part, which you can verify using the senders Public key.
This will lead to some extra data, which I want to work around
[ me... |
Can I save space for short messages by using encryption with private key instead of a signature? |
In general, no.
First, with an arbitrary public key scheme, the public and private keys might have quite different formats, and there might be no such thing like "encryption with a private key".
For example, with (generic) ElGamal, the public key is a member of the group, the private key is a natural number used ... |
Read a post on [Schneiers blog][1] ([and again 2011][2]) about increasing the number of rounds for AES from to "*AES-128 at 16 rounds, AES-192 at 20 rounds, and AES-256 at 28 rounds*" to raise the security. However, I did wonder where these figures came from. According to Schneier "*hey're off the top of my head, and c... |
If you "decrypt with a public key" then it is not "encrypted" in the usual sense, since the public key is _public_: anybody can use the public key, and, therefore, the message cannot be considered confidential in any way.
For the message confidentiality to be preserved, the decryption operation must be available onl... |
The only threats against MD5 are security, afaik it's mostly about its collision resistance (and some specific cases of preimage).
If you rite that app is "non-security-sensitive", maybe you should not care about those threats and gain from speed?
For some applications collisions are acceptable when happen very r... |
We have a server, which sends encrypted content to a flash client encoded as AES128 or RC4 over an insecure HTTP channel. The encryption key is negotiated using Diffie Hellman.
The problem:
- Diffie Hellman can be MITM-ed.
- flash client can be easily reversed (can be obfuscated though), so if I use a hardcoded ... |
A lot depends on your threat model, your system setup, etc. Do you require mutual authentication? Are connections secured with SSL or a similar protocol?
For passwords [scrypt][1] or [bcrypt][2] would be the way to go. They are better than just a simple salt + password setup. [It has been recommended][3] by someone ... |
In a security context course, we need to reproduce the old DES hashing scheme in the crypt program, on an old unix system.
I am actually reading the crypt page on wikipedia:
> The traditional implementation uses a modified form of the DES
> algorithm. The user's password is truncated to eight characters, and
> ... |
We have a server, which sends content encrypted with AES128 or RC4 to a flash client over an insecure HTTP channel. The encryption key is negotiated using Diffie Hellman.
The problem:
- Diffie Hellman can be MITM-ed.
- flash client can be easily reversed (can be obfuscated though), so if I use a hardcoded key, i... |
Are there any stream ciphers (or a deterministic random number generators, that should work as well I guess?) that cannot be parralellized?
So for example if I seed it with a specific value, and then "run" it for a year, generating more and more bits, and finally get a bitstream off it, then that bitstream will be imp... |
Are there secure stream ciphers that cannot be parralellized? |
Have a look at the corresponding [paper][1].
The key is a 128-bit string K. The round keys for round $r=1,...,8$ are derived as follows:
- take the version of $K$ cyclically rotated to the left $25\cdot r$ times;
- split the string obtained into eight substrings a call them $Z_1^{(r)}$, ..., $Z_8^{(r)}$.
Th... |
Are there any stream ciphers (or a deterministic random number generators, that should work as well I guess?) that cannot be parallelized?
So for example if I seed it with a specific value, and then "run" it for a year, generating more and more bits, and finally get a bitstream off it, then that bitstream will be impo... |
Are there secure stream ciphers that cannot be parallelized? |
Have a look at the corresponding [paper][1].
The key is a 128-bit string $K$. The round keys for round $r=1,...,8$ are derived as follows:
- take the version of $K$ cyclically rotated to the left $25\cdot r$ times;
- split the string obtained into eight substrings and call them $Z_1^{(r)}$, ..., $Z_8^{(r)}$.
... |
I know a plaintext - ciphertext couple of length 6 for a hill cipher where its key is a [3x3] matrix.
Based on what I've read and learned, to attack and crack keys of [n x n], if we know a plaintext - ciphertext duo of length $n^2$ then we have our set of n equations with n variables, and this is generally solvable.... |
Proving knowledge of a preimage of a hash without disclosing it? |
The [**Hill cipher**](http://en.wikipedia.org/wiki/Hill_cipher) is a historic polygraphic substitution cipher invented by Lester S. Hill in 1929.
It was the first substitution cipher to allow operations on groups of more than three plaintext characters at a time.
The Hill cipher is based on linear algebra, specific... |
Most of the current key exchange techniques are based on public-key cryptography. Are there any key exchange/establishment techniques based on symmetric-key cryptography too ?
In my setup primary assumption is both communicating parties can have pre-shared key and further they need to exchange messages to derive a ... |
With any convergent encryption algorithm E, it's easy for Alice to prove -- without revealing(*) a, b or the private key -- that a == b.
In order for the data deduplication feature to work, convergent algorithms are specifically designed such that
when Alice encrypts two messages a and b, such that x=E(a), y=E(b),
... |
Addition modulo $2^{16}$ just means, add the two numbers as you normally would, and subtract $2^{16}$ from the result until the sum is less than $2^{16}$. So suppose you wanted to add, say, 51995 and 29291 modulo $2^{16}$:
51995 + 29291 = 81286
Subtract 2^16 = 65536, you get 81286 - 65536 = 15750
... |
Subsets and Splits
No community queries yet
The top public SQL queries from the community will appear here once available.